
 Do Son
A new, deeply stealthy formjacking malware is targeting WooCommerce, secretly stealing customer payment data from legitimate checkout processes.
Malware

Malicious npm packages have been silently destroying files and corrupting data in React, Vue.js, and Vite projects for over two years.

Deceptive VS Code extensions like 'solaibot' are stealing crypto wallet credentials, disabling Defender, and deploying persistent spyware on Windows.

The notorious Genesis Market is back! A new campaign deploys a malicious browser extension via Lumma Stealer to covertly harvest user data.
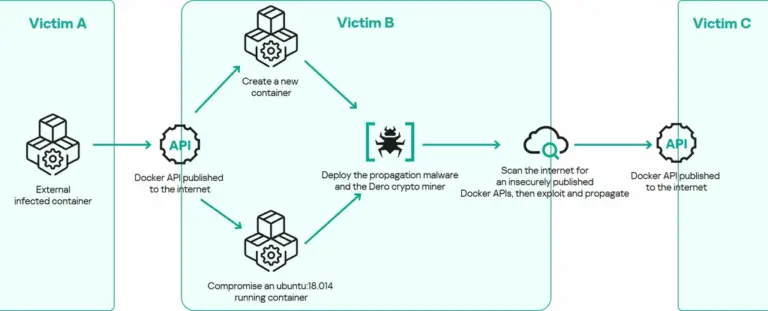
A new self-replicating Dero cryptominer is infecting exposed Docker containers, spreading as a worm without needing a C2 server.


A joint advisory warns that Russia's APT28 (Fancy Bear) is actively targeting logistics and tech companies supporting Ukraine with espionage and data exfiltration.

Beware fake Kling AI sites! A new campaign uses deceptive filenames to trick users into downloading infostealers, stealing crypto and browser data.

A malicious plugin is putting chatbot privacy at risk, silently stealing user messages. Is your Koishi bot compromised?

A technical analysis of the More_Eggs malware, detailing its use of ieuinit.exe abuse, DLL side-loading, and polymorphic JavaScript.

In-depth analysis of DBatLoader malware: Learn how it uses DLL side-loading, anti-detection techniques, and delivers SnakeKeylogger.

In-depth analysis of Skitnet malware: Rust, Nim, and DNS abuse. Discover how this sophisticated threat evades detection.

A trojanized KeePass installer is spreading malware! Learn how this sophisticated attack steals credentials and deploys Cobalt Strike.

RVTools briefly hijacked in a Bumblebee malware supply chain attack. Learn how attackers used a trusted tool to deliver post-exploitation payloads.

Remcos RAT campaign evades antivirus using PowerShell-based in-memory execution. Steals data, bypasses UAC, and avoids detection with stealthy tactics.

Malware found in Procolored printer software includes backdoor XRed and new clipbanker virus SnipVex. Users urged to reformat infected systems.

Zscaler reveals TransferLoader: a stealthy malware using IPFS and obfuscation to drop ransomware and backdoors. A new threat in the wild since 2025.

DarkCloud Stealer resurfaces in 2025 with AutoIt scripting and multi-stage obfuscation, targeting sensitive browser, email, and FTP credentials.

Attackers used Google Calendar invites and Unicode PUAs to deliver obfuscated malware via NPM. Aikido uncovers this novel supply chain attack.

A malicious PyPI package named 'solana-token' targeted Solana developers to steal code and secrets. Learn how it worked and how to stay safe.

Chihuahua Stealer uses stealthy PowerShell loaders, CNG AES-GCM encryption, and .NET memory injection to exfiltrate browser and crypto wallet data.

Earth Ammit’s VENOM and TIDRONE campaigns target Taiwan and South Korea’s drone, military, and satellite sectors via stealthy supply chain attacks.