
 Do Son
Swan Vector cyber-espionage campaign uses sophisticated malware to target institutions in Japan and Taiwan. Learn how they evade detection and steal data
Malware

Horabot malware targets Latin America with fake invoices, hijacking Outlook to spread phishing emails and steal data via stealthy scripting.

New report details APT37's "ToyBox Story" campaign, using spear phishing and cloud services to deploy RoKRAT malware. Fileless attacks and stealthy tactics revealed.

Attackers exploit fake AI video tools to deploy Noodlophile Stealer and XWorm, stealing credentials and data via Telegram bots.

New lightweight PupkinStealer malware silently steals browser data, messaging sessions, and desktop files, sending it all via Telegram.

Beware! Cybercriminals are using fake CAPTCHA pages to trick you into running commands that install the dangerous Lumma Stealer malware.

Sophisticated malware hides inside image files within .NET apps to secretly infect systems, targeting finance in Türkiye and logistics in Asia.

OtterCookie malware by North Korea-linked WaterPlum group evolves to target Chrome, MetaMask, and system files on both Windows and macOS platforms.

Warning! Malicious npm packages pumptoolforvolumeandcomment & debugdogs steal crypto keys and trading data, sending it via Telegram. Stay safe!

New email campaign uses tricky tactics and legitimate services to deliver the RATty Trojan in Spain, Italy, and Portugal. Stay alert for invoice scams!

Watch out! Sophisticated Facebook ads lure crypto users to download malware via fake platforms and celebrity endorsements. Bitdefender warns of data theft.

Urgent warning! Malicious npm packages disguised as Cursor AI tools are stealing credentials and installing backdoors on macOS. Protect your code!

CVE-2025-31324 in SAP NetWeaver lets attackers upload web shells, enabling full remote code execution and system compromise—no login required.

Atomic Stealer malware is targeting macOS users, disguised as a cracked Evernote download, stealing passwords and data.

RedisRaider malware exploits misconfigured Redis servers to deploy cryptominers via cron jobs, evading detection with obfuscation and anti-forensics.

Netskope Labs details a complex infection chain used by the DOGE Big Balls Ransomware, involving PowerShell scripts, exploits, and lateral movement tactics.
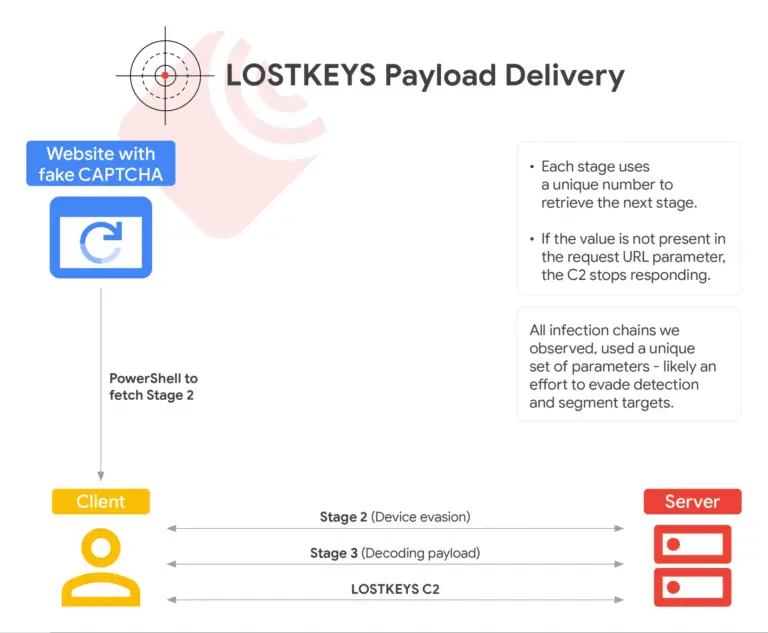
Google's GTIG reveals LOSTKEYS malware, a new tool by Russian actor COLDRIVER, targeting NATO advisors and Ukraine via fake CAPTCHAs.

Agenda ransomware (Qilin) is back, now using the advanced NETXLOADER and SmokeLoader to enhance infiltration and evade detection. Targets global sectors.
A sophisticated phishing campaign, possibly by APT36, spoofs Indian government sites and uses ClickFix tactics to target Windows and Linux users.

Aikido discovers a Remote Access Trojan (RAT) hidden in rand-user-agent, a popular npm package with 45,000 weekly downloads.

Unit 42 uncovers a sophisticated Lampion malware campaign using ClickFix social engineering tactics to target government and financial sectors in Portugal.

A zero-day privilege escalation vulnerability (CVE-2025-29824) in Microsoft CLFS was exploited by Balloonfly (Play ransomware) before the official patch.