
 Do Son
HarfangLab analysis details Gamaredon's PteroLNK malware, revealing its stealthy tactics and infrastructure used for espionage.
Malware

Prodaft analysis reveals Gorilla, a new Android malware evolving to steal data and potentially conduct espionage.

Sekoia TDR reveals Interlock ransomware's evolving tactics, including ClickFix social engineering, to evade detection and steal data.
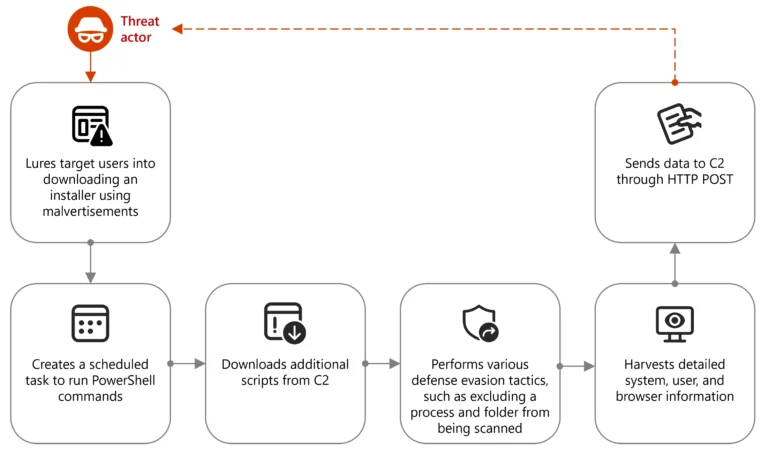
Threat actors abuse Node.js in malvertising campaigns to steal data and deliver malware via fake crypto installers and stealthy PowerShell scripts.

New attack campaign uses Microsoft Teams phishing and a novel TypeLib COM hijacking technique for persistence, targeting finance sector.

APT29, a Russia-linked group, targets European diplomats with phishing emails disguised as wine tasting invitations, deploying GRAPELOADER malware

LummaStealer evolves into a sophisticated Malware-as-a-Service, using stealth and advanced techniques to steal data.

CrazyHunter ransomware group targets Taiwan's critical infrastructure with sophisticated attacks, using BYOVD techniques and open-source tools.

Discover Waiting Thread Hijacking, a novel process injection technique that bypasses EDR systems. Learn how it stealthily executes code in remote processes.
A new campaign by Chinese threat actor UNC5174 uses the VShell RAT. Sysdig TRT reports on the group's shift to open-source tools and evasion tactics.

Kandji's research uncovers PasivRobber, a sophisticated macOS malware suite targeting user data. Learn about its deceptive tactics and capabilities.

A malicious npm package, disguised as an Advcash integration, contains a reverse shell that triggers after successful payments, granting attackers server access.

CloudSEK's report reveals how fake PDF converters use social engineering to spread malware. Learn how these malicious sites deceive users and steal data

Trend Micro uncovers BPFDoor backdoor used in cyberespionage across Asia and the Middle East, attributing it to the Red Menshen APT group

NVISO's report details BRICKSTORM, a China-linked backdoor targeting European industries, using sophisticated techniques to evade detection

Learn about ResolverRAT, a new remote access trojan using advanced evasion to avoid detection. This malware employs sophisticated techniques.

Sucuri discovered a credit card skimming attack using a fake font domain to steal credit card data from a WordPress website.
The NCSC reveals DAMASCENED PEACOCK, a sophisticated malware targeting the UK MOD, using spear-phishing, code signing, and COM Hijacking.

North Korean threat group Slow Pisces targets crypto developers with fake job offers and malicious coding challenges. Learn how they steal millions

A fake npm package named pdf-to-office has been discovered injecting malicious code into Atomic and Exodus crypto wallets, redirecting funds and stealing data

TROX Stealer exploits urgency via phishing emails to deliver obfuscated MaaS malware that steals credit cards, browser data, and crypto wallets

FortiGuard Labs discovers malicious NPM packages targeting PayPal users. Attackers use deceptive tactics to steal usernames, paths, and hostnames