
 Do Son
ViperSoftX malware is being used by Arabic-speaking attackers to target South Korea, according to ASEC. This malware uses PowerShell and spreads through torrents, delivering PureCrypter and Quasar RAT
Malware

BI.ZONE Threat Intelligence reports Sapphire Werewolf using updated Amethyst stealer malware to target energy companies, employing advanced evasion techniques.Sources and related content

A new report reveals Russia-linked Shuckworm's evolved cyber campaign targeting a military mission in Ukraine, featuring sophisticated malware and stealthy tactics.

A Silent Push report details the evolving tactics of the Scattered Spider hacker collective, including new phishing kits, the Spectre RAT, and targeting of major brands in 2025.

The NCSC UK warns of BADBAZAAR and MOONSHINE spyware targeting Uyghur, Tibetan, and Taiwanese individuals. These sophisticated trojans collect sensitive data via fake apps. Learn how to protect your devices.

A new "Pick Your Poison" phishing campaign tricks users into choosing between having their credentials stolen or infecting their systems with malware. Cofense analysis reveals how this double-edged attack uses files.fm to deliver malicious payloads.

Microsoft reports active exploitation of a Windows CLFS zero-day (CVE-2025-29824) to escalate privileges and deploy ransomware. Learn about the attacks, the threat actors involved, and how to mitigate the risk.
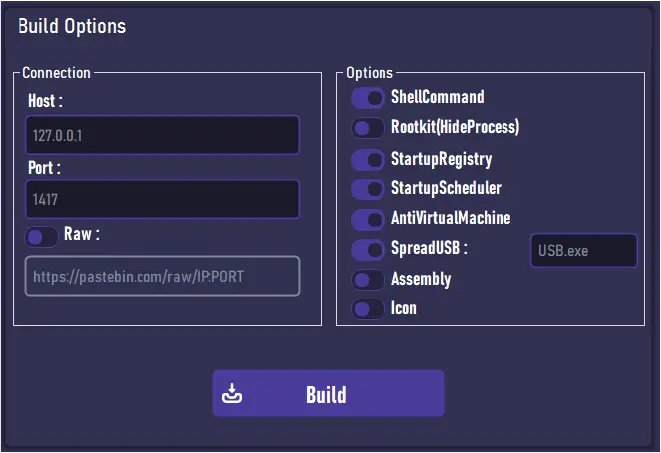
CYFIRMA researchers discovered Neptune RAT, an advanced Remote Access Trojan targeting Windows. Learn about its destructive features, evasion techniques, and distribution methods.

Vidar Stealer malware is distributed by masquerading as BGInfo.exe, exploiting expired signatures and file discrepancies to evade detection

Attackers are using SourceForge to distribute malware, including a ClipBanker Trojan and a cryptocurrency miner, disguised as a Microsoft Office enhancement suite.

The Grandoreiro banking trojan is being spread through phishing campaigns. Learn about the attack methods and how to stay safe.

Ten popular Visual Studio Code extensions were found secretly installing XMRig miners, exploiting users’ CPUs for unauthorized cryptomining.

Explore the evolving threat of ransomware 2025 and learn about new tactics, targeted industries, and defense strategies.

Stay informed about the security risks of TVT NVMS9000. Learn about a major vulnerability that exposes DVRs to cyber attacks.

Uncover the details of the Lazarus Group malicious campaign targeting the npm ecosystem with advanced malware techniques.

Uncover the LegionLoader Campaign's deceptive tactics. Learn how fake CAPTCHAs and CloudFlare Turnstile are used in malware distribution.
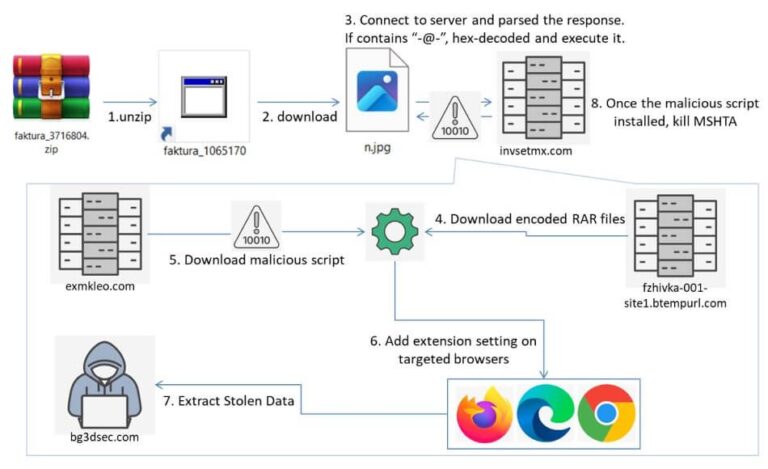
Discover the dangers of RolandSkimmer and how it exploits browser vulnerabilities through deceptive ZIP files and extensions.

Discover the rise of carding attacks with the malicious Python package disgrasya targeting WooCommerce stores with automated scripts.

Explore the dangers of Tropidoor malware and how deceptive emails can lead to cyber threats. Stay informed and protected.

Explore the dangers of Outlaw Linux malware, a persistent coinminer that combines automated execution with manual oversight.

Uncover the threat posed by the TookPS downloader, a malware strain exploiting popular software and fraudulent websites.

Learn about the Qilin ransomware attack that compromised an MSP and affected numerous customers through a phishing campaign.