
 Do Son
A new Android malware disguised as "PM KISAN YOJNA" is stealing sensitive data using multi-stage droppers and evasion tactics. Beware of fake updates!
Malware

LayerX found "sleeper agent" Chrome extensions, installed on 1.5M devices, disguised as audio tools but capable of remote command execution and data theft.

A sophisticated "ClickFix" phishing campaign uses fake Booking.com CAPTCHAs to deliver RATs and info stealers to the hotel and travel industry.

ViperSoftX, a stealthy malware, is actively spreading via fake software to steal cryptocurrency and enable remote control, affecting users globally.

A new AMOS macOS stealer variant is using typo-squatted Spectrum domains in a clever cross-platform social engineering campaign. Stay vigilant!
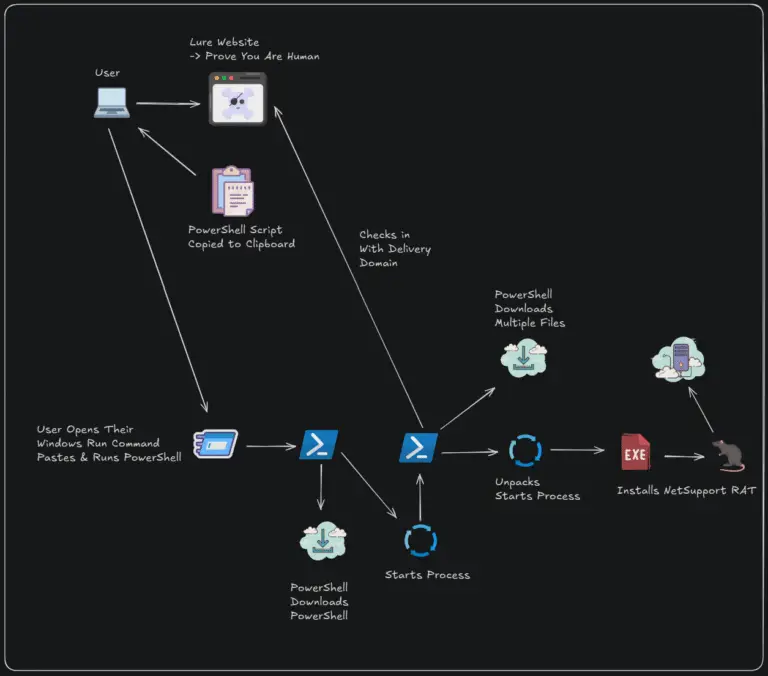
A new campaign uses fake DocuSign & Gitcodes pages to trick users into manually installing NetSupport RAT, gaining remote control.

K7 Labs details an evolved PowerShell malware, ViperSoftX 2025, featuring enhanced modularity, stealth, and persistence for advanced attacks.

Crocodilus, a rapidly evolving Android banking trojan, now targets global users, stealing crypto seed phrases and bypassing defenses.

Socket uncovers malicious RubyGems impersonating Fastlane plugins, stealing sensitive CI/CD data by rerouting Telegram API calls. Beware of fastlane-plugin-telegram-proxy!

Sysdig uncovers a campaign exploiting misconfigured Open WebUI instances to deploy AI-assisted cryptominers and infostealers, showcasing new threat vectors.

Wordfence uncovers a sophisticated WordPress malware disguised as a legitimate plugin, stealing admin credentials & enabling remote code execution.

Socket discovers 4 malicious npm packages designed to drain crypto wallets on BSC & Ethereum, downloaded over 2,100 times.

A U.S. jury ordered NSO Group to pay Meta's WhatsApp $167M in damages for its 2019 Pegasus spyware attack on 1,400+ users.

Wiz uncovers JINX-0132, a cryptojacking campaign exploiting misconfigured Nomad, Consul, Docker, and Gitea in DevOps environments to mine Monero.

A new npm supply chain attack, "xlsx-to-json-lh," uses typosquatting to enable remote code execution, silently awaiting a "kill switch" to delete project directories.

Learn how interactive sandboxes like ANY.RUN can detect and analyze Microsoft 365 phishing attacks in real-time, preventing silent breaches and data exfiltration.

A new ransomware strain, Lyrix, targets Windows systems with strong encryption, anti-analysis, and data destruction techniques. Learn how to protect your data.

A sophisticated PyPI supply chain attack, "cappership," steals Solana private keys by monkey-patching, leveraging transitive dependencies and blockchain exfiltration.

Darktrace uncovers PumaBot, a stealthy Linux botnet using Go binaries, SSH brute-force, and rootkits to compromise IoT devices, aiming for persistent, undetected access.
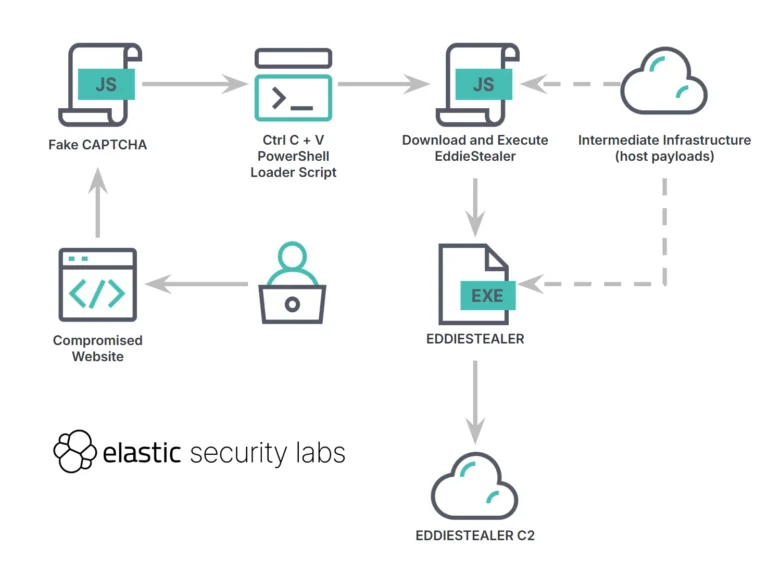
EDDIESTEALER, a new Rust-based infostealer, targets Windows systems via fake CAPTCHAs, stealing crypto wallets, browser data, and credentials with advanced stealth.

AyySSHush is a new stealthy botnet backdooring ASUS routers via SSH keys, abusing legitimate features to persist across firmware updates and targeting residential networks globally.

Threat actors are exploiting AI hype with fake software installers, delivering CyberLock ransomware, Lucky_Gh0$t, and the destructive Numero malware.