
 Do Son
Unauthenticated remote attackers can crash Cisco ISE via RADIUS, enabled by default. CVE-2025-20152 fix released—patch now to prevent DoS.
Vulnerability

Grafana rushed an emergency patch for CVE-2025-4123, a high-severity XSS flaw that was made public. Upgrade now to prevent unauthorized access.

GitLab released urgent updates (18.0.1+) fixing high-severity flaws, including a DoS vulnerability (CVE-2025-0993) and a 2FA bypass (CVE-2024-12093).
NIST introduces the Likely Exploited Vulnerability (LEV) metric, a new way to estimate which CVEs have likely been exploited in the wild.

Critical vulnerabilities (CVSS 9.8) in the Langroid Python framework allow remote code execution in LLM applications. Update to version 0.53.15 now!

Learn about critical vulnerabilities in LLM-powered Browse agents like Browser Use, allowing domain bypass and prompt injection for data theft.

AutomationDirect's MB-Gateway has a critical (CVSS 10) flaw allowing unauthenticated remote access and RCE. Hardware limits prevent a software fix; replacement is recommended.

A high-severity path traversal flaw in setuptools can allow RCE, exposing millions of Python users. Update to 78.1.1 now.

A high-severity BIND DNS server vulnerability allows remote attackers to crash servers using malformed TSIG signatures. Urgent update advised.

A reflected XSS flaw in GlobalProtect (CVE-2025-0133) allows malicious JavaScript execution. PoC exploit code is available. Update your PAN-OS.
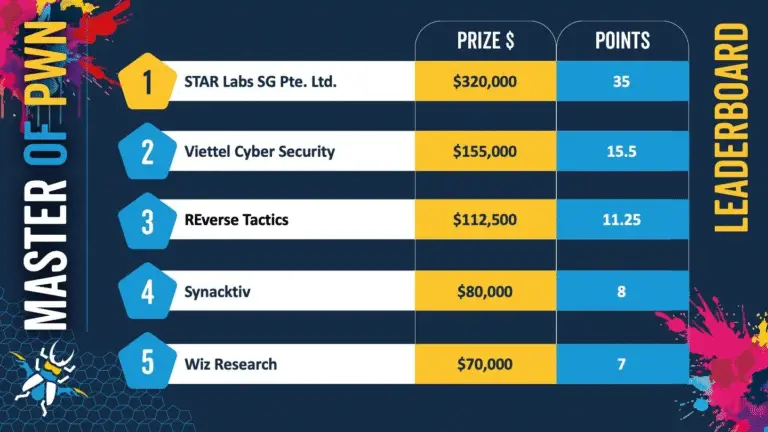
Pwn2Own Berlin saw VMware ESXi and Windows 11 compromised, along with Firefox. Researchers earned over $1M for 30+ zero-day exploits.

Lexmark CVE-2025-1127 flaw allows remote code execution via embedded web server. Affects many printer models—patch firmware to version .240.206+ now.

Critical CVSS 9.8 flaw in vLLM allows remote code execution via PyNcclPipe. Patch to 0.8.5 now to protect your AI infrastructure.

A critical containerd flaw (CVE-2025-47290) allows malicious container images to hijack the host filesystem. Update to version 2.1.1 now.
CISA warns of critical CVSS 9.8 flaws in Vertiv Liebert devices allowing RCE and auth bypass—patch now to protect OT environments.

A critical vulnerability (CVE-2025-40634) in TP-Link Archer AX50 routers allows remote code execution as root. A public PoC increases the risk.

CVE-2025-22157 is a CVSS 7.2 Jira vulnerability allowing privilege escalation. Update Jira Data Center now to prevent unauthorized access.

A critical DNSdist vulnerability allows unauthenticated attackers to launch DoS attacks, disrupting DNS operations. Update now to secure your system.

A critical flaw in Broadcom's Automic Automation Agent for Unix exposes systems to privilege escalation. Check your version and update to stay secure.

A critical OpenPGP.js flaw (CVE-2025-47934) allows attackers to spoof message signatures and manipulate content. Update to fix this risk.

Broadcom addresses four new vulnerabilities in VMware ESXi, vCenter, Workstation, and Fusion, ranging from command execution to XSS. Update now.

Learn about new vulnerabilities in VMware Cloud Foundation that could lead to unauthorized access, info disclosure, and unapproved actions.