Skip to content
October 30, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
  • Home
  • News
  • Cyber Security
  • Don’t Click! Fake Chat Used in Meta Business Account Phishing
  • Cyber Security

Don’t Click! Fake Chat Used in Meta Business Account Phishing

Do Son March 24, 2025 3 minutes read
0
Layoff Phishing Scam Remcos RAT Malware Aruba Phishing, Phishing-as-a-Service PyPI, phishing CVE-2024-25608 PyPI Phishing, Credential Theft
Add Daily CyberSecurity as a preferred source on Google

“What if you received an email stating, ‘YOUR ADS ARE TEMPORARILY SUSPENDED’? The urgency of the email instantly grabs your attention… hoping to get it fixed promptly.”

In the digital world of likes, follows, and ad conversions, a single email can unravel your entire marketing infrastructure. That’s exactly what a sophisticated phishing campaign discovered by the Cofense Phishing Defense Center (PDC) is exploiting — with fake Meta emails, deceptive chatbots, and even counterfeit support agents.
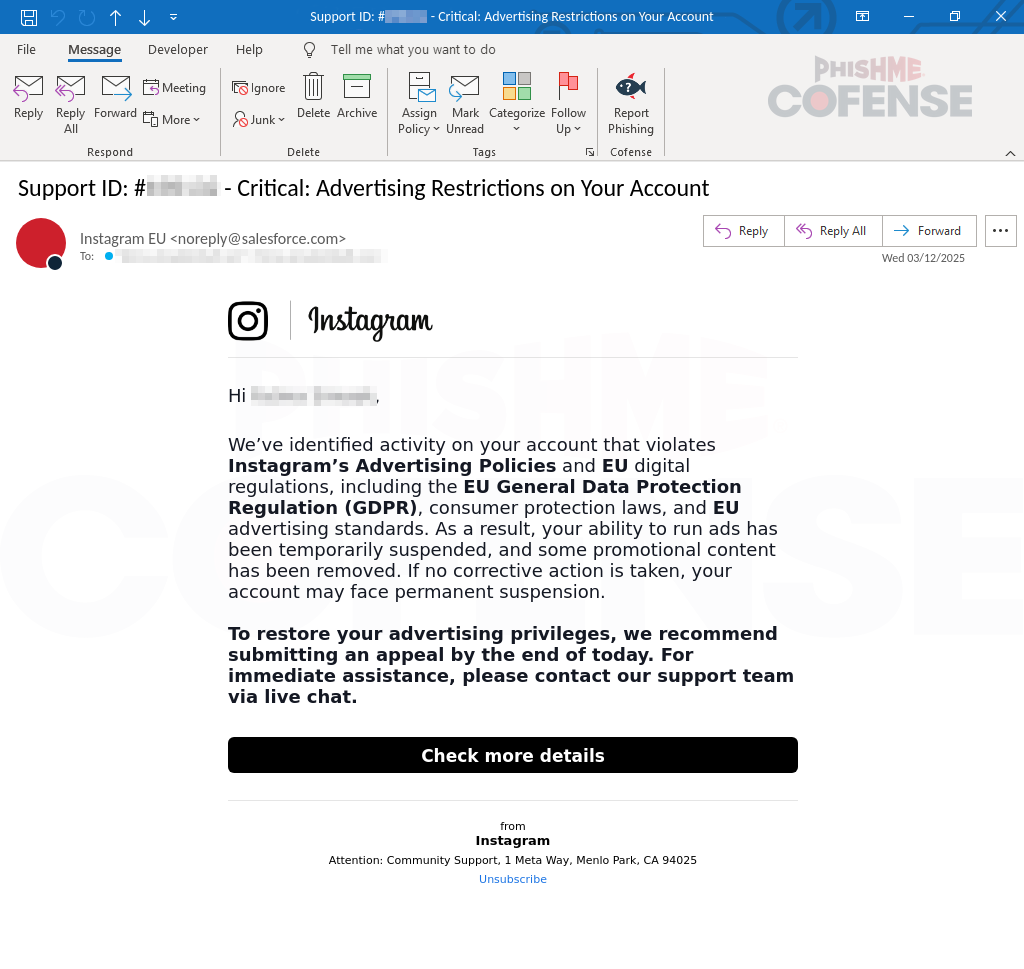
Malicious Email | Image: Cofense 

The campaign begins with an urgent email disguised as a Meta/Instagram alert, complete with subject lines like:

“Support ID: #xxxx – Critical Advertising Restrictions on Your Account”​

This phishing email plays on fear — warning that ad accounts have violated EU GDPR or Meta’s ad policies. Victims are encouraged to click a “Check More Details” button, which leads to a legitimate-looking fake Meta page.

But there’s a clue: the sender address isn’t official — it’s noreply@salesforce[.]com, not a Meta-owned domain.

Once on the fake landing page (businesshelp-manager[.]com), victims see a warning that their account may face termination. From there, they’re guided toward a “Request Review” option.

“Comparing this to a legitimate Meta Business page, most people will think there isn’t anything out of the ordinary.”
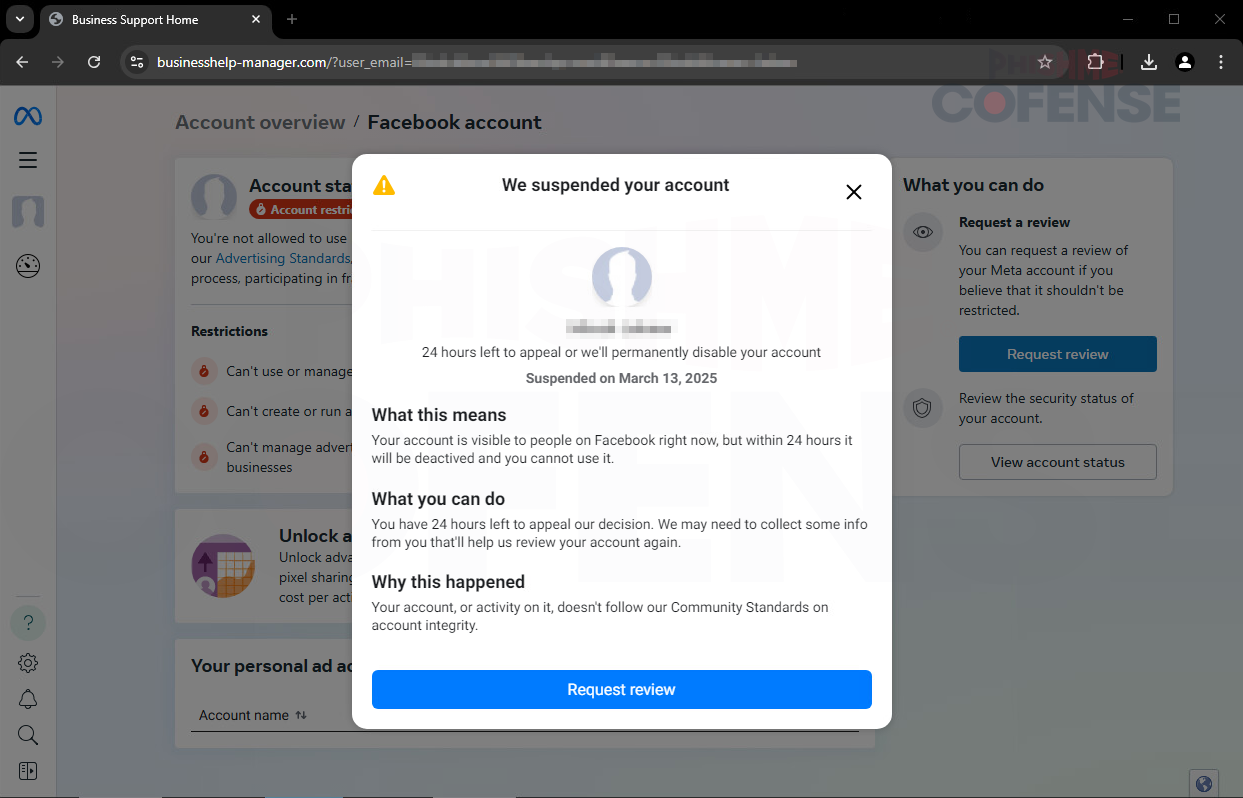
Meta Business Account Phishing
Initial Infection URL Landing Page | Image: Cofense 

Victims are asked to chat with a support chatbot — seemingly helpful, but 100% malicious. The chatbot requests:

  • Business name

  • Screenshots of Facebook Business settings

  • Contact number

  • Personal profile information

“The attacker even asks for screenshots… perhaps as a way of screening victims.”

Eventually, the victim is told to run a “System Check” — a euphemism for giving the attacker Two-Factor Authentication (2FA) access via their own Authenticator app.

“The attacker aims to hijack Business Meta accounts by registering themselves as a ‘Secure Login’ via the Authenticator App feature of Meta.”​

If users don’t fall for the chatbot, the attacker has a Plan B — a DIY-style “setup guide” that leads victims to the same endpoint: handing over control.

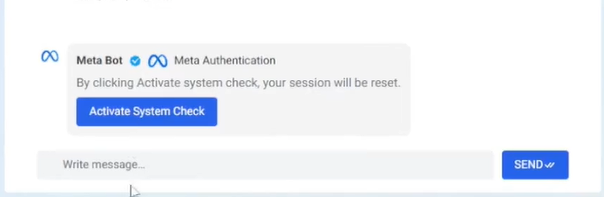
The attack culminates with a password prompt after clicking “Activate System Check.”

“The page reloads and asks the user to enter their Facebook password.”​

Redacted screenshot of phishing login page with “Activate System Check” button and password field. | Image: Cofense 

Once entered, the attacker can:

  • Bypass email recovery
  • Lock the real user out
  • Run ads from the compromised business page
  • Steal audience data, post scams, or worse

“The inclusion of live agent support adds an additional layer of deception, making users believe they are interacting with Meta’s official support team.”​

Phishing isn’t just about shady links anymore. Today’s attackers are brand impersonation experts, crafting convincing experiences across email, web, and support.

Stay alert. Stay skeptical. And always double-check before you click.

Related Posts:

  • Cybercriminals Escalate Attacks with Sophisticated HR-themed Phishing Scam
  • Meta’s AI Push: From Llama to Chatbot, Subscription Model Coming
  • Phishing Campaign Bypasses MFA to Target Meta Business Accounts, Putting Millions at Risk
  • Amazon Prime Phishing Scam Steals Login, Payment Info
  • Copilot Phishing: New Scam Targets Microsoft Users

Related coverage

  • “CL Suite” Deception: Malicious Chrome Extension Steals 2FA Secrets and Meta Business Data
  • Hadooken & K4Spreader Malware: 8220 Gang’s Latest Cloud Hijacking Tools
  • Torrent of Threats: China-Nexus APT UAT-9244 Hijacks South American Telecoms with PeerTime Backdoor
  • Cloudflare WARP Abused to Hijack Cloud Services, Cado Security Report Reveals
  • Unmasking ELECTRUM: Cyber Predators of the Ukrainian Grid
  • TIDRONE: The Unseen Cyberespionage Threat Targeting Taiwan’s Military and Satellite Industries
Track all actively exploited CVEs →

Support Our Threat Intelligence

Find our threat intelligence and malware analysis helpful? Support our work today and unlock a 100% ad-free reading experience!

Buy Me a Coffee Logo Buy Me a Coffee
Select your plan
Free Pro Team

Hover over a plan to see its benefits.

Get Zero-Hour Vulnerability Alerts

Critical CVEs, CVSS scores, and PoC updates — straight to your inbox every week.

We respect your inbox. Unsubscribe anytime.

SHARE
Share on FacebookShare on XShare on LinkedInShare on TelegramShare on BlueskyShare on Mastodon
Written by
@DdoS · Security Researcher

Do Son

Do Son is the Founder and Editor of SecurityOnline.info. Working in cybersecurity since 2013, he reports on vulnerabilities, malware, and emerging threats, providing timely analysis to help organizations and individuals stay ahead of evolving risks.

Tags: Meta Business Account Phishing

Leave a Reply Cancel reply

You must be logged in to post a comment.

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-118527CVSS 4.3
    Use of predictable filenames in Ivanti Connect Secure before versions 25.1.1.3 and 22.8R2.6 allows a remote authenticated attacker...
    Admin intel📅 Updated: Oct 30, 2026
  • CVE-2026-118539
    This module enables you to sell goods and services to customers through an included shopping cart and checkout...
    Admin intel📅 Updated: Oct 29, 2026
  • CVE-2022-31034CVSS 8.3
    Impact All versions of Argo CD starting with v0.11.0 are vulnerable to a variety of attacks when an...
    Watchtower Verified📅 Updated: Oct 29, 2026
  • CVE-2026-112353CVSS 6.2
    GFI KerioConnect (Kerio Connect) before 10.0.8 Patch 2 contains a stored cross-site scripting vulnerability in the Webmail component...
    Watchtower Verified📅 Updated: Oct 29, 2026
  • CVE-2026-116779CVSS 9.8
    Summary `sofia_presence_handle_sip_i_message()` splits the To user of an inbound SIP MESSAGE on `+` and treats the left half...
    Admin intel📅 Updated: Oct 29, 2026
  • CVE-2026-97229CVSS 10.0
    GitLab has remediated an issue that, under certain conditions, could have allowed an unauthenticated user to execute arbitrary...
    CISA KEV📅 Added to KEV: Oct 29, 2026
  • CVE-2026-76418CVSS 8.6
    A vulnerability in the Remote Access SSL VPN service of Cisco Secure Firewall Adaptive Security Appliance (ASA) Software...
    CISA KEV📅 Added to KEV: Oct 29, 2026
  • CVE-2026-116690CVSS 7.5
    MLflow is an open source AI engineering platform for agents, large language models, and machine learning models. From...
    Admin intel📅 Updated: Oct 28, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2023-22793CVSS 9.3
    A vulnerability allowing an unauthenticated attacker to perform remote code execution (RCE) on servers running the Veeam Virtualization...
    📅 Updated: Oct 29, 2026
  • CVE-2026-61707CVSS 9.0
    SOCFortress CoPilot focuses on providing a single pane of glass for all your security operations needs. Prior to...
    📅 Updated: Oct 29, 2026
  • CVE-2026-61645CVSS 9.1
    Docat is a tool for hosting versioned static documentation. In the affected implementation, an arbitrary file upload vulnerability...
    📅 Updated: Oct 29, 2026
  • CVE-2026-31158CVSS 9.8
    SQL Injection vulnerability in CRM SOFTTRADE Infotech (aka softtradeindia) 1.0 allows a remote attacker to execute arbitrary code...
    📅 Updated: Oct 29, 2026
  • CVE-2026-107032CVSS 9.1
    Insecure permissions in Bulk Share : Location Sender v2.1.0 (versionCode 5) allows unauthorized attackers to invoke an exported...
    📅 Updated: Oct 29, 2026
  • CVE-2024-8517CVSS 9.8
    SPIP before 4.3.2, 4.2.16, and 4.1.18 is vulnerable to a command injection issue. A remote and unauthenticated attacker...
    📅 Updated: Oct 29, 2026
  • CVE-2026-82854CVSS 9.3
    Nodemailer before 8.0.4 is vulnerable to SMTP command injection through the unsanitized envelope.size parameter. When an application passes...
    📅 Updated: Oct 29, 2026
  • CVE-2026-81694CVSS 9.3
    openssl-encrypt (pip package, versions
    📅 Updated: Oct 29, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.