Skip to content
October 28, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
  • Home
  • News
  • Data Leak
  • Hackers sell US military drone documents for $150
  • Data Leak

Hackers sell US military drone documents for $150

Do Son July 13, 2018 2 minutes read
US military drone documents
Add Daily CyberSecurity as a preferred source on Google
The MQ-9 drone (codename: Reaper) is a highly lethal new crewless combat aircraft capable of performing intelligence, surveillance, and reconnaissance (ISR) missions. In March 2007, the US Air Force formed the Reaper UAV Attack Squadron, the 42nd Air Attack Aircraft Squadron at Crich Air Force Base, Nevada, and set up a particular Reaper UAV Working Group. Research tactics, train crews, and conduct practice drills.
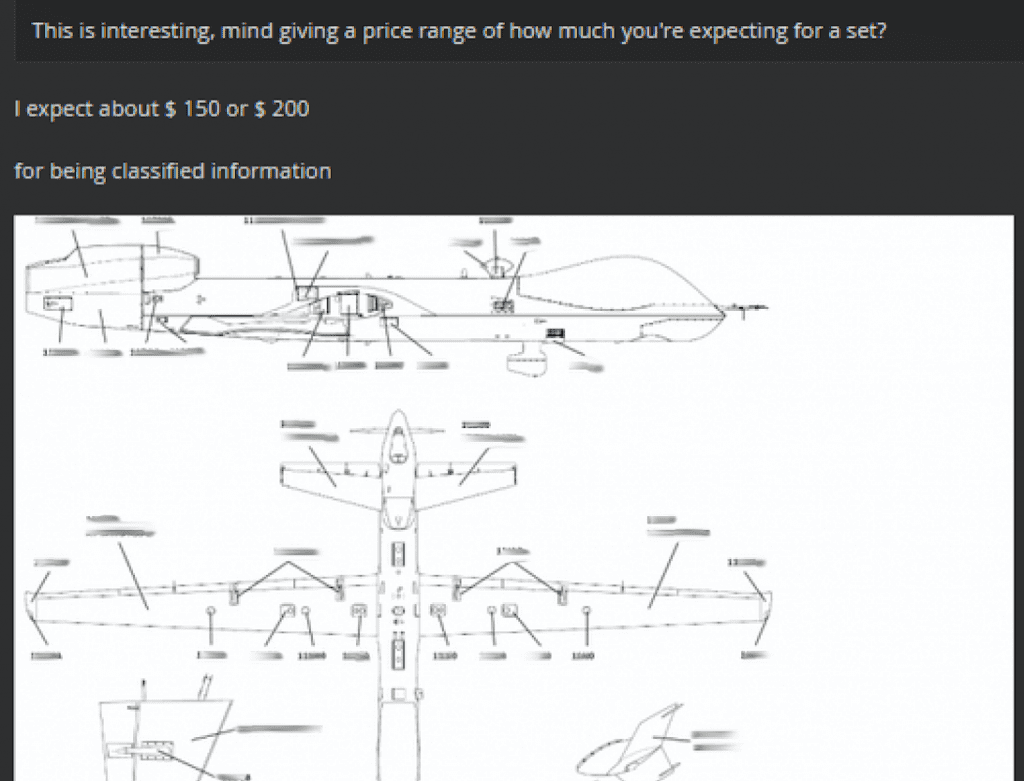
According to several media reports, the threat intelligence company Recorded Future recently discovered that a group of hackers is selling sensitive military documents in the dark market trading market, including the maintenance manual and pilot list of the MQ-9 Reaper drone.
It is also worth mentioning that the military documents being sold are not limited to the information related to the MQ-9 Reaper drone. Other materials include the description of improvised explosive devices. Various training manuals for the bombs, M1 Abrams tank operation manual, crew training and survival manual, and documentation detailing tank tactics.
The US-based Recorded Future said that for these online sales files, hackers are relatively inexpensive, ranging from $150 to $200.
Image: recordedfuture
Recorded Future also said it had contacted hackers online. According to hackers, they obtained these files by exploiting vulnerabilities that publicly disclosed in the Netgear router in 2016.
Hackers use the Shodan search engine to discover those vulnerable Netgear routers online and then exploit them to exploit them. Hackers say these routers are still using known default FTP passwords, which makes it easy to log in, and some of them are in military facilities.
Based on some information posted by hackers on the Internet and conversations with them, Recorded Future was finally able to determine that the attacked military Netgear router located at Crich Air Force Base, Nevada. After obtaining some necessary access rights through the router, he successfully got the maintenance manual and pilot list of the MQ-9 Reaper drone.
The MQ-9 Reaper is considered one of the most advanced drones in the world and is widely used by the US Air Force, Navy, Central Intelligence Agency, Customs and Border Protection, NASA, and other countries. use.
For other military documents, the hackers did not disclose where they specifically stole, but Recorded Future, based on some information they posted, believed that the source of the materials was likely to be the Pentagon or some US Army officials.

Related coverage

  • Allianz Life Suffers Data Breach: 1.4 Million Customers’ PII Compromised via Cloud CRM Social Engineering Attack
  • Sourcenext Data Breach Exposes 22.5M User Records
  • Spy Games or Glitch? The Truth Behind Venezuela’s BGP Leak
  • 20,000+ Ubiquiti Devices Exposed: Amplification Attacks & Data Leaks
  • ShinyHunters Syndicate Alleges Major FBI Network Compromise
  • Claude AI Shared Chats Surfaced in Google Over a Config Error
Track all actively exploited CVEs →

Support Our Threat Intelligence

Find our threat intelligence and malware analysis helpful? Support our work today and unlock a 100% ad-free reading experience!

Buy Me a Coffee Logo Buy Me a Coffee
Select your plan
Free Pro Team

Hover over a plan to see its benefits.

Get Zero-Hour Vulnerability Alerts

Critical CVEs, CVSS scores, and PoC updates — straight to your inbox every week.

We respect your inbox. Unsubscribe anytime.

SHARE
Share on FacebookShare on XShare on LinkedInShare on TelegramShare on BlueskyShare on Mastodon
Written by
@DdoS · Security Researcher

Do Son

Do Son is the Founder and Editor of SecurityOnline.info. Working in cybersecurity since 2013, he reports on vulnerabilities, malware, and emerging threats, providing timely analysis to help organizations and individuals stay ahead of evolving risks.

Tags: US military drone documents

Search

Translation

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2020-13125CVSS 7.2
    An issue was discovered in the "Ultimate Addons for Elementor" plugin before 1.24.2 for WordPress, as exploited in...
    Watchtower Verified📅 Updated: Oct 28, 2026
  • CVE-2020-13126CVSS 9.9
    An issue was discovered in the Elementor Pro plugin before 2.9.4 for WordPress, as exploited in the wild...
    Watchtower Verified📅 Updated: Oct 28, 2026
  • CVE-2019-20180CVSS 8.0
    The TablePress plugin for WordPress is vulnerable to CSV Injection in versions up to and including 1.14 via...
    Watchtower Verified📅 Updated: Oct 28, 2026
  • CVE-2012-20005CVSS 5.1
    SocialFit plugin for WordPress through 1.2.2 contains a reflected cross-site scripting vulnerability that allows unauthenticated attackers to inject...
    Watchtower Verified📅 Updated: Oct 28, 2026
  • CVE-2016-20101CVSS 9.2
    Issuu Panel plugin for WordPress before 1.6.6 contains a PHP file inclusion vulnerability that allows unauthenticated attackers to...
    Watchtower Verified📅 Updated: Oct 28, 2026
  • CVE-2016-20097CVSS 8.7
    Weaver (Fanwei) E-cology 8.0 contains a SQL injection vulnerability in the SignatureDownLoad servlet that allows unauthenticated remote attackers...
    Watchtower Verified📅 Updated: Oct 28, 2026
  • CVE-2026-102785CVSS 10.0
    Joomla Extension - yootheme.com - Unauthenticated remote code execution in YOOtheme Pro 5.0.0-5.0.52 - YOOtheme Pro’s publicly accessible...
    Admin intel📅 Updated: Oct 27, 2026
  • CVE-2026-48356CVSS 9.3
    Adobe Commerce is affected by an Unrestricted Upload of File with Dangerous Type vulnerability that could result in...
    CISA KEV📅 Added to KEV: Oct 27, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-110879CVSS 9.8
    jackson-databind validates the outer class of a class-name type ID but accepts attacker-selected classes inside its generic arguments,...
    📅 Updated: Oct 28, 2026
  • CVE-2026-58256CVSS 9.1
    GRR is a resource management and reservation application. Prior to the advisory-reported fixed version 4.5.0, an administrator can...
    📅 Updated: Oct 27, 2026
  • CVE-2024-51092CVSS 9.1
    LibreNMS before 24.10.0 allows a remote attacker to execute arbitrary code via OS command injection involving AboutController.php's index(),...
    📅 Updated: Oct 27, 2026
  • CVE-2026-91656CVSS 9.1
    Vulnerability in Oracle Essbase (component: Federated Partitions). The supported version that is affected is 21.8.3.0.0. Easily exploitable vulnerability...
    📅 Updated: Oct 27, 2026
  • CVE-2026-71195CVSS 9.9
    In OpenStack Manila before 23.0.1, multiple Manila API operations on public shares do not verify that the caller...
    📅 Updated: Oct 27, 2026
  • CVE-2026-114108CVSS 9.3
    HKUDS Vibe-Trading from 0.1.0 before 0.1.7 contains a missing authentication vulnerability that allows unauthenticated attackers to access the...
    📅 Updated: Oct 27, 2026
  • CVE-2026-114053CVSS 9.2
    vLLM from 0.7.3 before 0.31.0 forwards the request-supplied mm_processor_kwargs.code_revision to Transformers AutoProcessor.from_pretrained, letting clients select which revision of...
    📅 Updated: Oct 27, 2026
  • CVE-2026-116692CVSS 9.8
    MLflow is an open source AI engineering platform for agents, large language models, and machine learning models. From...
    📅 Updated: Oct 27, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.