Skip to content
October 13, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
  • Home
  • News
  • Malware
  • Hackers are spreading FELIXROOT backdoors through Microsoft Office vulnerabilities
  • Malware

Hackers are spreading FELIXROOT backdoors through Microsoft Office vulnerabilities

Do Son July 30, 2018 2 minutes read
FELIXROOT backdoors
Add Daily CyberSecurity as a preferred source on Google

The latest report from FireEye security companies shows that hackers are inserting backdoors into victims through security vulnerabilities in older versions of Microsoft Office. The above vulnerability Microsoft has been fixed in the second half of last year, so users weren’t affected by the vulnerability after installing the latest update.

FELIXROOT backdoor program:

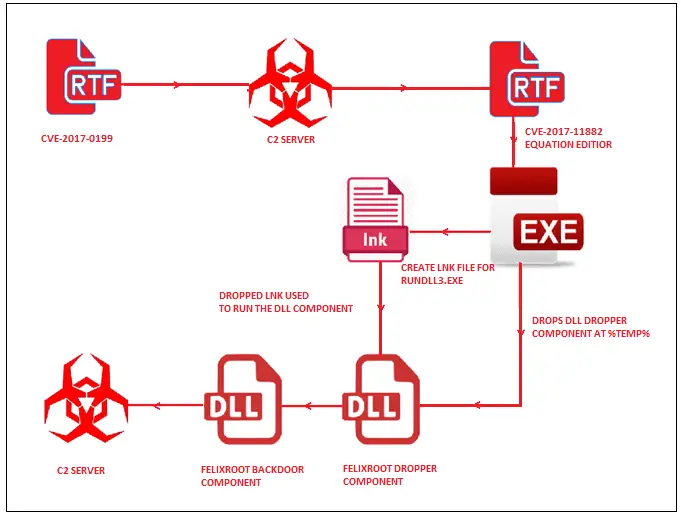
This attack was initiated by phishing emails carrying RTF files containing malicious code. Once opened, the exploits can be exploited to exploit the vulnerability.

The hacker claimed in the phishing email that this is a document about the environmental protection seminar, so the unknown user would be induced to download and open the RTF document.

After opening, the malicious code starts running and contacts the remote control server to get the instructions. The system process runs a backdoor named FELIXRROOT.

After the backdoor program loaded successfully, it can start collecting private information on the victim’s computer, then package and compress it and upload it to the remote C&C server for saving.


Self-cleaning after the collection is completed prevents the discovery:

For espionage, the backdoor program only collects information and does not cause any damage to the computer, so it does not want to be discovered after the purpose of receiving.

Therefore, after collecting the information, the backdoor program stops executing the action and then starts to clean up the data, and deletes all the traces of its documents and its self and destroys itself.

Currently, the security company has not completed tracking of the backdoor program, so it is not clear which interest-related hacking gangs the backdoor program may involve.

Routine safety reminder time:

Most attacks against Microsoft Office rely on vulnerabilities and documents that carry malicious code and induce users to open to load other malware.

Keeping Microsoft Office updates is the best solution for users, and continuing updates can block security vulnerabilities that have already been discovered.

Besides, do not open any documents of unknown origin. In most cases, the attachment documents sent by non-contacts are not advertisements and contain malicious code.

Source, Image: FireEye

Related coverage

  • EastWind Campaign: New CloudSorcerer Attacks Target Russian Gov Using APT31 and APT27 Tactics
  • Kaspersky has been uncovers Slingshot campaign targets Africa and the Middle East since 2012
  • Cryptojacking Campaign Exploits Atlassian Confluence CVE-2023-22527 Vulnerability
  • New Ransomware Tactics & Tools: An In-Depth Analysis of Emerging Threats
  • Manic Android Malware Steals Data Without Active Internet
  • Credit Card Skimmer and Backdoor Found Lurking on WordPress E-commerce Site
Track all actively exploited CVEs →

Support Our Threat Intelligence

Find our threat intelligence and malware analysis helpful? Support our work today and unlock a 100% ad-free reading experience!

Buy Me a Coffee Logo Buy Me a Coffee
Select your plan
Free Pro Team

Hover over a plan to see its benefits.

Get Zero-Hour Vulnerability Alerts

Critical CVEs, CVSS scores, and PoC updates — straight to your inbox every week.

We respect your inbox. Unsubscribe anytime.

SHARE
Share on FacebookShare on XShare on LinkedInShare on TelegramShare on BlueskyShare on Mastodon
Written by
@DdoS · Security Researcher

Do Son

Do Son is the Founder and Editor of SecurityOnline.info. Working in cybersecurity since 2013, he reports on vulnerabilities, malware, and emerging threats, providing timely analysis to help organizations and individuals stay ahead of evolving risks.

Tags: FELIXROOT backdoors

Search

Translation

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-102255CVSS 10.0
    A Pre-authentication SSRF vulnerability exists in the SMA1000 Appliance Work Place interface due to an unintended alternate access...
    Admin intel📅 Updated: Oct 9, 2026
  • CVE-2026-105133CVSS 6.9
    A vulnerability was detected in Ahsay AhsayCBS up to 10.3.2. This affects the function checkSysPwd of the file...
    Admin intel📅 Updated: Oct 9, 2026
  • CVE-2023-22894CVSS 4.9
    Strapi through 4.5.5 allows attackers (with access to the admin panel) to discover sensitive user details by exploiting...
    CISA KEV📅 Added to KEV: Oct 8, 2026
  • CVE-2016-3081CVSS 8.1
    Apache Struts 2.3.19 to 2.3.20.2, 2.3.21 to 2.3.24.1, and 2.3.25 to 2.3.28, when Dynamic Method Invocation is enabled,...
    CISA KEV📅 Added to KEV: Oct 8, 2026
  • CVE-2015-3306CVSS 10.0
    The mod_copy module in ProFTPD 1.3.5 allows remote attackers to read and write to arbitrary files via the...
    CISA KEV📅 Added to KEV: Oct 8, 2026
  • CVE-2015-5477CVSS 7.5
    named in ISC BIND 9.x before 9.9.7-P2 and 9.10.x before 9.10.2-P3 allows remote attackers to cause a denial...
    CISA KEV📅 Added to KEV: Oct 8, 2026
  • CVE-2021-3199CVSS 9.8
    Directory traversal with remote code execution can occur in /upload in ONLYOFFICE Document Server before 5.6.3, when JWT...
    CISA KEV📅 Added to KEV: Oct 8, 2026
  • CVE-2026-94504CVSS 7.2
    Ninja Forms 3.15.3 stores an anonymous non-RTE textarea value and renders it without safe HTML encoding in the...
    Admin intel📅 Updated: Oct 7, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2025-65570CVSS 9.8
    A type confusion in jsish 2.0 allows incorrect control flow during execution of the OP_NEXT opcode. When an...
    📅 Updated: Oct 13, 2026
  • CVE-2025-68929CVSS 9.0
    Frappe is a full-stack web application framework. Prior to versions 14.99.6 and 15.88.1, an authenticated user with specific...
    📅 Updated: Oct 13, 2026
  • CVE-2025-68860CVSS 9.8
    Authentication Bypass Using an Alternate Path or Channel vulnerability in Mobile Builder Mobile builder mobile-builder allows Authentication Abuse.This...
    📅 Updated: Oct 13, 2026
  • CVE-2025-51677CVSS 9.1
    An issue was discovered in openRISC OR1200 commit 83ac6b. An output mismatch between the RTL and the netlist...
    📅 Updated: Oct 13, 2026
  • CVE-2025-50329CVSS 9.8
    An issue in ConeXware, Inc Power Archiver v.22.00.11 and before allows a remote attacker to escalate privileges and...
    📅 Updated: Oct 13, 2026
  • CVE-2025-65340CVSS 9.8
    kishan0725 Hospital Management System 4.0 is vulnerable to SQL Injection in /betweendates-detailsreports.php.
    📅 Updated: Oct 13, 2026
  • CVE-2025-29296CVSS 9.8
    H3C Magic BE18000 V200R007, H3C NX400 V100R015, H3C Magic NX30 Pro V100R0011, H3C Magic R3010 V100R009, H3C Magic...
    📅 Updated: Oct 13, 2026
  • CVE-2026-74043CVSS 9.0
    Summary The `@expose_resources` framework upload helpers `upload_list_file`, `upload_rule_file`, and `upload_decoder_file` build their destination path from a caller-supplied `filename`...
    📅 Updated: Oct 13, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.