Skip to content
November 4, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
  • Home
  • News
  • Technology
  • Let’s Encrypt introduced ACME v2 protocol and wildcard support for testing
  • Technology

Let’s Encrypt introduced ACME v2 protocol and wildcard support for testing

Do Son January 9, 2018 3 minutes read
ACME v2 protocol

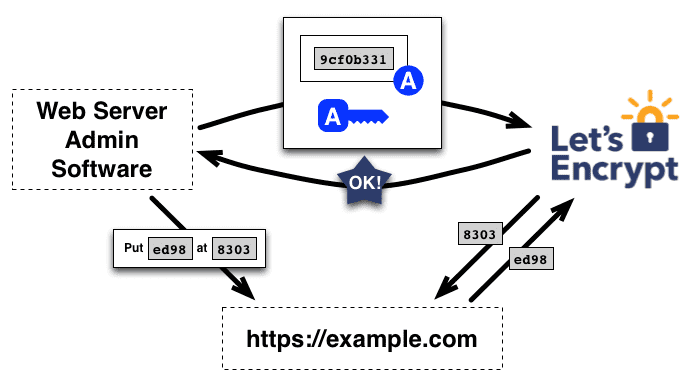
Let’s Encrypt, the free digital certification authority released the ACME v2 protocol API endpoint and officially announced the start of testing the ACME V2 API interface that supports the issue of wildcard digital certificates.

You can start testing your client for ACME v2 support using the following directory URL:

https://acme-staging-v02.api.letsencrypt.org/directory

Note that because the temporary environment root certificate does not exist in the browser/client truststore, the endpoint is not suitable for use in a production environment. The v2 API endpoints ready for production will be released on February 27.

ACME V2 is not a backward compatible version, so ACME v1 clients, which are used by almost all today, will not work with ACME v2 endpoints. Existing clients need to change their code and use the new version to support ACME v2.

Image: letsencrypt

ACME v2 vs ACME v1

There are a number of differences between the ACME v2 and v1 APIs, notable changes:

  1. Authorization/issuance process has changed
  2. JWS request authorization to change
  3. The “resource” field of the JWS request body is replaced by the new JWS request header “url”
  4. Directory endpoint/resource rename

The new version began to provide wildcard certificate issued:

In July 2017, Let’s Encrypt announced that it will provide wildcard certificates by the beginning of 2018 and is currently testing wildcard certificates in the first week of 2018.

At present, the V2 API interface is under test. Developers can apply for a wildcard certificate through the API interface. However, the API interface is still in the testing phase, so there may be some problems.

Ordinary users can wait and see first wait until formally launched. Interested developers now may want to download and test the new API interface to experience it.

The new version of the API interface, see: https://community.letsencrypt.org/t/staging-endpoint-for-acme-v2/49605

Wildcard certificate explanation:

Domain Name Certificate Similar to the concept of pan-domain DNS resolution, a wildcard certificate issued by a primary domain name can be used in all sub-domains.

Wildcard certificate advantages:

Domain name wildcard certificate is the biggest characteristic of the application can be deployed in the use of sub-domain names, so for sub-domain names, there is no need to re-apply for a new certificate. The price, the wildcard domain name certificate is usually several times higher than the single domain name certificate, but the main reason for the high price of nature is the use of convenience.

Reference: letsencrypt

Add Daily CyberSecurity as a preferred source on Google

Related coverage

  • Google Integrates Nano Banana AI Editor into Search, NotebookLM, and Photos to Deepen Ecosystem AI
  • OpenAI to Retain Non-Profit Structure, Focus on Societal Impact
  • OpenAI Slashes o3 Model API Prices by 80%: Output Cost Drops to Just $8/Million Tokens!
  • Facebook F8 2018 officially opened the registration
  • Google Lens is expanding to more Android devices
  • The Open Web Is in “Rapid Decline,” Google Admits in Court
Track all actively exploited CVEs →

Support Our Threat Intelligence

Find our tech and OS security coverage helpful? Support our work today and unlock a 100% ad-free reading experience!

Buy Me a Coffee Logo Buy Me a Coffee
Select your plan
Free Pro Team

Hover over a plan to see its benefits.

Get Zero-Hour Vulnerability Alerts

Critical CVEs, CVSS scores, and PoC updates — straight to your inbox every week.

We respect your inbox. Unsubscribe anytime.

SHARE
Share on FacebookShare on XShare on LinkedInShare on TelegramShare on BlueskyShare on Mastodon
Written by
@DdoS · Security Researcher

Do Son

Do Son is the Founder and Editor of SecurityOnline.info. Working in cybersecurity since 2013, he reports on vulnerabilities, malware, and emerging threats, providing timely analysis to help organizations and individuals stay ahead of evolving risks.

Tags: ACME v2 protocol

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
  • CVE-2023-54413CVSS 6.1
    The WPML plugin for WordPress is vulnerable to Reflected Cross-Site Scripting via the wp_lang parameter in versions up...
    Watchtower Verified📅 Updated: Nov 4, 2026
  • CVE-2026-81648CVSS 10.0
    The CryptoPayment Gateway WordPress plugin from 1.2.1 to 1.2.2 does not apply an authorization check on one of...
    Admin intel📅 Updated: Nov 3, 2026
  • CVE-2026-119977CVSS 8.1
    WordPress Core is vulnerable to Remote Code Execution in versions 4.7 through 7.1.3. This is due to predictable,...
    CISA KEV📅 Added to KEV: Nov 3, 2026
  • CVE-2026-58115CVSS 10.0
    A vulnerability has been identified in SIMATIC IoT2050 Advanced (6ES7647-0BA00-1YA2) (All versions < V4.3.4.1 running Industrial OS with...
    Admin intel📅 Updated: Nov 2, 2026
  • CVE-2026-20051CVSS 7.4
    A vulnerability with the Ethernet VPN (EVPN) Layer 2 ingress packet processing of Cisco Nexus 3600 Platform Switches...
    Watchtower Verified📅 Updated: Nov 1, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-114425CVSS 9.2
    SEPPmail Secure Email Gateway before 15.1.1 trusts a file path supplied in externally provided Large File Transfer attachment...
    📅 Updated: Nov 4, 2026
  • CVE-2026-114424CVSS 9.2
    SEPPmail Secure Email Gateway before 15.1.1 can evaluate attacker-influenced replacement text as Perl code in sender or recipient...
    📅 Updated: Nov 4, 2026
  • CVE-2026-28336CVSS 9.9
    SolarWinds Dameware was found to be affected by a command injection vulnerability that could lead to the compromise...
    📅 Updated: Nov 4, 2026
  • CVE-2026-13594CVSS 9.1
    Zoho Corporation's ManageEngine Log360 and EventLog Analyzer versions 13062 and below are vulnerable to an issue that could...
    📅 Updated: Nov 4, 2026
  • CVE-2026-13214CVSS 9.8
    The OCPP 1.6 client in subsys/net/lib/ocpp/ocpp_j.c contains a stack buffer overflow in parse_getconfig_msg(). When handling a GetConfiguration request...
    📅 Updated: Nov 4, 2026
  • CVE-2026-121246CVSS 9.6
    Use after free in WebGL in Google Chrome on on Android prior to 157.0.8103.38 allowed a remote attacker...
    📅 Updated: Nov 4, 2026
  • CVE-2026-121247CVSS 9.6
    Buffer overflow in Dawn in Google Chrome on on Android prior to 157.0.8103.38 allowed a remote attacker to...
    📅 Updated: Nov 4, 2026
  • CVE-2026-121185CVSS 9.6
    Use after free in PictureInPicture in Google Chrome prior to 157.0.8103.38 allowed a remote attacker leveraging social engineering...
    📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.