Skip to content
November 3, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
Weekly Threat Intelligence: May 25 to May 31, 2026 Weekly Threat Intelligence Active Vulnerability Report
  • Weekly Recap

Weekly Threat Intelligence: May 25 to May 31, 2026

Do Son June 1, 2026 0

Read our weekly threat intelligence briefing. Our active vulnerability report reveals new zero-day exploits and CISA KEV additions for May 2026.

Notepad++ Exploit Code and Flaws Publicly Disclosed Notepad++ exploit code arbitrary code execution
  • Vulnerability Report

Notepad++ Exploit Code and Flaws Publicly Disclosed

Do Son June 1, 2026 0

Learn about the new Notepad++ security flaws. Public Notepad++ exploit code triggers arbitrary code execution. Update to version v8.9.6.1 now.
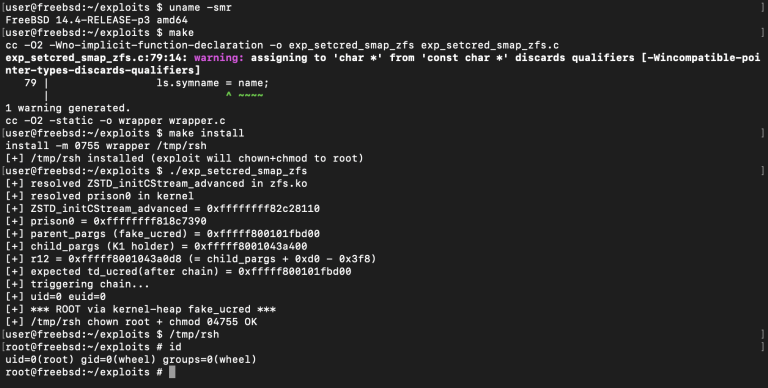
Critical FreeBSD Kernel Buffer Overflow Disclosed: Public Details & PoC Out FreeBSD kernel buffer overflow public exploit code released
  • Vulnerability

Critical FreeBSD Kernel Buffer Overflow Disclosed: Public Details & PoC Out

Do Son June 1, 2026 0

A critical FreeBSD kernel buffer overflow vulnerability is exposed. Learn more about this threat now that public exploit code released.

Critical Eppendorf Bioreactor Security Flaw Disclosed Eppendorf bioreactor security flaw hard-coded VNC password
  • Vulnerability Report

Critical Eppendorf Bioreactor Security Flaw Disclosed

Do Son June 1, 2026 0

A critical Eppendorf bioreactor security flaw exposes systems via a hard-coded VNC password. Learn how to secure your BioFlo 320 device.

Critical MCP Toolbox Vulnerability Exposes Enterprise Databases MCP Toolbox vulnerability session hijacking
  • Vulnerability Report

Critical MCP Toolbox Vulnerability Exposes Enterprise Databases

Do Son May 31, 2026 0

A critical MCP Toolbox vulnerability exposes enterprise databases. Learn how this security flaw allows session hijacking and how to fix it.
Comet Backup Server Flaw Exposes Remote Customer Data Comet Backup RCE vulnerability CVE-2026-32999 patch Comet Backup IDOR Cross-Tenant Takeover
  • Vulnerability Report

Comet Backup Server Flaw Exposes Remote Customer Data

Do Son May 31, 2026 0

A critical Comet Backup RCE vulnerability has been found. Learn about the CVE-2026-32999 patch released to secure backup servers and user data.

FIFA Website Spoofing Scams: FBI Issues Major World Cup Warning FIFA website spoofing scams FBI World Cup alert Pig Butchering Scam Jingliang Su Sentencing Meta China Scam Ads, Zuckerberg Revenue Conflict Trading Bot Scam BEC Scam Rental Payment Fraud
  • Cybercriminals

FIFA Website Spoofing Scams: FBI Issues Major World Cup Warning

Do Son May 31, 2026 0

Bad actors are running FIFA website spoofing scams. Read the latest FBI World Cup alert to stay safe from fake ticket sites and data theft.

SolyxImmortal Info Stealer Exploits Systems via Discord SolyxImmortal info stealer Discord webhooks
  • Malware

SolyxImmortal Info Stealer Exploits Systems via Discord

Do Son May 31, 2026 0

The SolyxImmortal info stealer targets user data. Learn how this Python malware steals passwords and abuses Discord webhooks to exfiltrate files.

Inside a Massive Elderly Lottery Fraud Scam Elderly lottery fraud scam DOJ wire fraud conspiracy ALPHV BlackCat, Insider Threat Nefilim ransomware Artem Stryzhak guilty plea, Volodymyr Tymoshchuk $11M reward CoinDCX, Employee Arrest Operation PowerOFF Cybercrime, Self-Promotion Hacking
  • Cybercriminals

Inside a Massive Elderly Lottery Fraud Scam

Do Son May 31, 2026 0

A massive elderly lottery fraud scam broker receives a prison sentence for a DOJ wire fraud conspiracy that targeted millions.

Football Fan Scams Surge Ahead of World Cup 2026 TASPEN, mobile malware North Korean IT Worker Fraud
  • Cybercriminals

Football Fan Scams Surge Ahead of World Cup 2026

Do Son May 31, 2026 0

Cybercriminals are ramping up football fan scams and World Cup 2026 fraud. Protect yourself from fake merchandise, phishing, and lottery traps today.
Apache Ignite Vulnerability Fixes Critical Security Loophole Apache Ignite vulnerability arbitrary file read
  • Vulnerability Report

Apache Ignite Vulnerability Fixes Critical Security Loophole

Do Son May 30, 2026 0

A newly fixed Apache Ignite vulnerability allows arbitrary file read attacks via path traversal. Learn how to secure your database immediately.

Abusive Bulletproof Hosting Networks Fuel Global Phishing Campaigns abusive bulletproof hosting networks malicious JavaScript payloads
  • Cybercriminals

Abusive Bulletproof Hosting Networks Fuel Global Phishing Campaigns

Do Son May 30, 2026 0

Intrinsec uncovers how abusive bulletproof hosting networks host dangerous malware infrastructure distributing malicious JavaScript payloads.
WebSphere Remote Code Execution Defended with New IBM Security Fixes IBM WebSphere execution flaws WebSphere security bulletin patches request smuggling patch WebSphere remote code execution Langflow OSS vulnerability remote code execution patch
  • Vulnerability Report

WebSphere Remote Code Execution Defended with New IBM Security Fixes

Do Son May 30, 2026 0

IBM released a critical WebSphere remote code execution update. Apply the request smuggling patch immediately to protect your server environment.

Massive npm Dependency Confusion Attack Infiltrates Corporate Ecosystems npm dependency confusion attack malicious packages discovered
  • Malware

Massive npm Dependency Confusion Attack Infiltrates Corporate Ecosystems

Do Son May 30, 2026 0

Microsoft uncovers a massive npm dependency confusion attack targeting enterprise infrastructure. Learn how these malicious packages discovered run code.
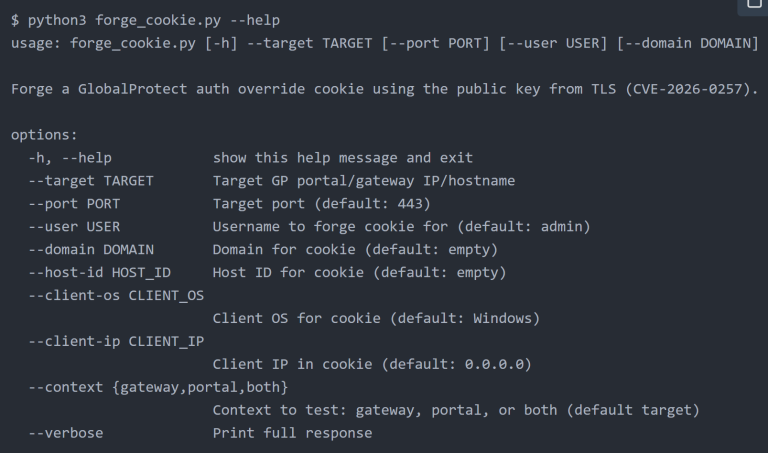
PAN-OS Authentication Bypass Flaw Exploited in the Wild PAN-OS authentication bypass flaw exploited in the wild
  • Vulnerability Report

PAN-OS Authentication Bypass Flaw Exploited in the Wild

Do Son May 30, 2026 0

The PAN-OS authentication bypass flaw is actively exploited in the wild. Learn how to secure your GlobalProtect VPN gateways today.

Romanian Hacker Sentenced to Prison Following Government Cyberattacks Romanian hacker sentenced identity theft conviction Pig-Butchering Crackdown Operation Level Up Oleksandr Didenko North Korean IT Workers Coinbase TaskUs insider breach, Hyderabad police Coinbase arrest Scattered Spider, Cybercrime Scattered Spider group
  • Cybercriminals

Romanian Hacker Sentenced to Prison Following Government Cyberattacks

Do Son May 29, 2026 0

A Romanian hacker sentenced to prison following an identity theft conviction and selling access to a US government network infrastructure.

Architectural Serenity: Microsoft Redefines Copilot with a Monochromatic Corporate Aesthetic Copilot Microsoft 365 redesign
  • Technology

Architectural Serenity: Microsoft Redefines Copilot with a Monochromatic Corporate Aesthetic

Do Son May 29, 2026 0

Microsoft rolls out a major Copilot Microsoft 365 redesign. Discover the clean, monochromatic workspace, unified sidebar layout, and dynamic prompt surface.

PureLogs Info Stealer Campaign Exploits Trusted Windows Process PureLogs info stealer campaign
  • Malware

PureLogs Info Stealer Campaign Exploits Trusted Windows Process

Do Son May 29, 2026 0

FortiGuard Labs exposes a highly evasive PureLogs info stealer campaign utilizing process hollowing and fileless execution.

Rising Chinese PhaaS Ecosystem Bypasses Modern Security Controls Chinese PhaaS ecosystem
  • Cybercriminals

Rising Chinese PhaaS Ecosystem Bypasses Modern Security Controls

Do Son May 29, 2026 0

Discover how the Chinese PhaaS ecosystem uses real-time interception and AI automation to bypass MFA and exploit digital wallets.

China-Based Red Lamassu Targets Telecoms Across Asia Red Lamassu threat actor
  • Cybercriminals

China-Based Red Lamassu Targets Telecoms Across Asia

Do Son May 29, 2026 0

Learn how the Red Lamassu threat actor targets telecom networks with the newly discovered JFMBackdoor malware framework.

Advanced Lazarus Memory-Only Toolset Deeply Analyzed by Fox-IT Lazarus memory-only toolset
  • Malware

Advanced Lazarus Memory-Only Toolset Deeply Analyzed by Fox-IT

Do Son May 29, 2026 0

Fox-IT uncovers a sophisticated Lazarus memory-only toolset used to compromise financial firms via an evasive three-stage malware pipeline.
Oracle Releases Massive May 2026 Critical Security Patch Update PeopleSoft RCE security bug, unauthenticated HTTP exploit, CVE-2026-35273 Oracle security patch updates critical software vulnerabilities
  • Vulnerability Report

Oracle Releases Massive May 2026 Critical Security Patch Update

Do Son May 29, 2026 0

Stay secure with the latest Oracle security patch updates. Learn how these fixes address critical software vulnerabilities across multiple enterprise platforms.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-81648CVSS 10.0
    The CryptoPayment Gateway WordPress plugin from 1.2.1 to 1.2.2 does not apply an authorization check on one of...
    Admin intel📅 Updated: Nov 3, 2026
  • CVE-2026-58115CVSS 10.0
    A vulnerability has been identified in SIMATIC IoT2050 Advanced (6ES7647-0BA00-1YA2) (All versions < V4.3.4.1 running Industrial OS with...
    Admin intel📅 Updated: Nov 2, 2026
  • CVE-2026-20051CVSS 7.4
    A vulnerability with the Ethernet VPN (EVPN) Layer 2 ingress packet processing of Cisco Nexus 3600 Platform Switches...
    Watchtower Verified📅 Updated: Nov 1, 2026
  • CVE-2026-20118CVSS 6.8
    A vulnerability in the handling of an Egress Packet Network Interface (EPNI) Aligner interrupt in Cisco IOS XR...
    Watchtower Verified📅 Updated: Nov 1, 2026
  • CVE-2010-20125CVSS 8.7
    DedeCMS before 5.7 contains a file inclusion vulnerability in plus/carbuyaction.php that allows remote unauthenticated attackers to control the...
    Watchtower Verified📅 Updated: Oct 30, 2026
  • CVE-2015-20130CVSS 5.1
    Netsweeper before 4.0.11 and 4.1.0 before 4.1.5 contains a reflected cross-site scripting vulnerability in webadmin/reporter/view_server_log.php that allows remote...
    Watchtower Verified📅 Updated: Oct 30, 2026
  • CVE-2026-111357CVSS 7.0
    Ivanti Connect Secure 22.8R2.4 mishandles the manner in which the dsinvoked broker trusts DSCache configuration data, leading to...
    CISA KEV📅 Added to KEV: Oct 30, 2026
  • CVE-2026-118527CVSS 4.3
    Use of predictable filenames in Ivanti Connect Secure before versions 25.1.1.3 and 22.8R2.6 allows a remote authenticated attacker...
    CISA KEV📅 Added to KEV: Oct 30, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-81648CVSS 10.0
    The CryptoPayment Gateway WordPress plugin from 1.2.1 to 1.2.2 does not apply an authorization check on one of...
    Admin intel📅 Updated: Nov 3, 2026
  • CVE-2026-94290CVSS 9.1
    SUSE Rancher Fleet clusters reference a kubeconfig secret that the controller uses to install and manage a Fleet...
    📅 Updated: Nov 3, 2026
  • CVE-2026-88811CVSS 9.1
    Missing filtering in the SUSE Rancher Manager meta proxy could cause passed in rancher credentials to be leaked to...
    📅 Updated: Nov 3, 2026
  • CVE-2026-120534CVSS 9.8
    The Advanced Custom Fields: Extended PRO plugin for WordPress is vulnerable to Limited Code Injection in all versions...
    📅 Updated: Nov 3, 2026
  • CVE-2026-120518CVSS 9.1
    The BuddyPress XProfile Image Field plugin for WordPress is vulnerable to arbitrary file deletion in all versions up...
    📅 Updated: Nov 3, 2026
  • CVE-2026-116606CVSS 9.3
    An authentication bypass in Barracuda Email Security Gateway versions earlier than 9.4.0.030 allows an unauthenticated remote attacker to...
    📅 Updated: Nov 3, 2026
  • CVE-2026-105606CVSS 9.5
    Joomla Extension - joomlaboat.com - Unauthenticated arbitrary file upload in Custom Tables < 3.7.8 - An unauthenticated attacker...
    📅 Updated: Nov 3, 2026
  • CVE-2026-105604CVSS 9.3
    Joomla Extension - dj-extensions.com - Unauthenticated SQL injection in DJ-Classifieds < 3.11.3 - The Joomla extension DJ-Classifieds is...
    📅 Updated: Nov 3, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.