
 Do Son
Critical: Cemu 2.6 Linux binaries were backdoored via a developer's stolen GitHub token. If you downloaded Cemu for Linux between May 6–12, audit your system now.
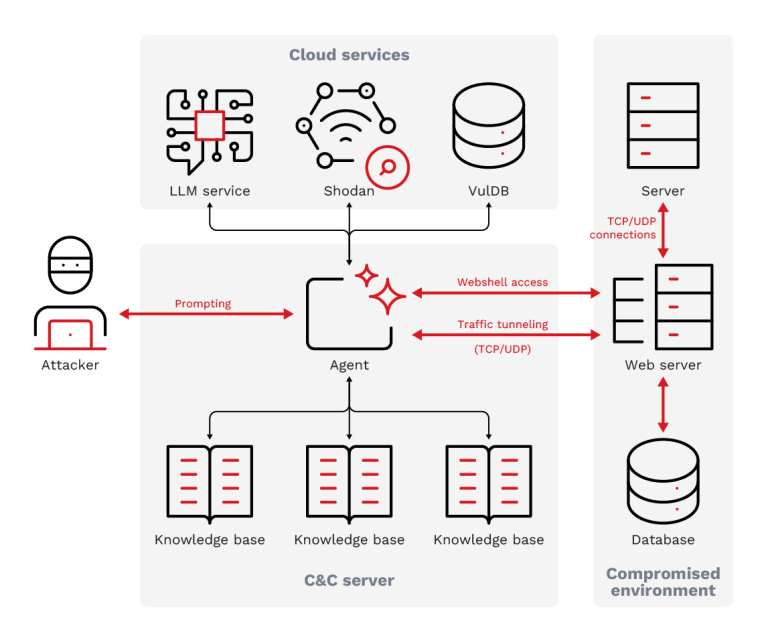
TrendAI exposes SHADOW-AETHER: threat groups using agentic AI to "vibe code" custom backdoors and automate intrusions across government and financial sectors.

Gen Digital exposes a JDownloader site breach (May 6-7, 2026). Attackers used WDAC policies to kill antivirus and r77 rootkits for total system invisibility.

GemStuffer exploits RubyGems as an illicit data transport to scrape UK council portals. Discover how this supply chain attack bypasses standard defenses.

Urgent: Public PoC for Apache CVE-2026-23918. A critical double-free in mod_http2 enables unauthenticated DoS and RCE. Update to Apache 2.4.67 immediately.
Urgent: Public PoC exploit code released for YellowKey (BitLocker bypass) and GreenPlasma (SYSTEM elevation). Windows 11 and Server 2025 are at high risk.

Critical Siemens Alert: 9.3 severity XSS flaws hit SIMATIC S7 PLCs. Attackers can hijack sessions via web interfaces. Update to V3.1.6 or follow mitigations.
Critical Alert: CVE-2026-25244 (CVSS 9.8) in WebdriverIO allows RCE via unsanitized git branch names. Secure your CI/CD pipeline and update to 9.24.0 now.

Microsoft’s May 2026 update fixes 137 vulnerabilities, including 30 Critical RCE and EoP flaws. Prioritize patches for Netlogon, Office, and M365 Copilot now.
Critical Alert: CVE-2026-43898 (CVSS 10) in SandboxJS allows a total sandbox escape and RCE. Update to version 0.9.6 immediately to secure your host.
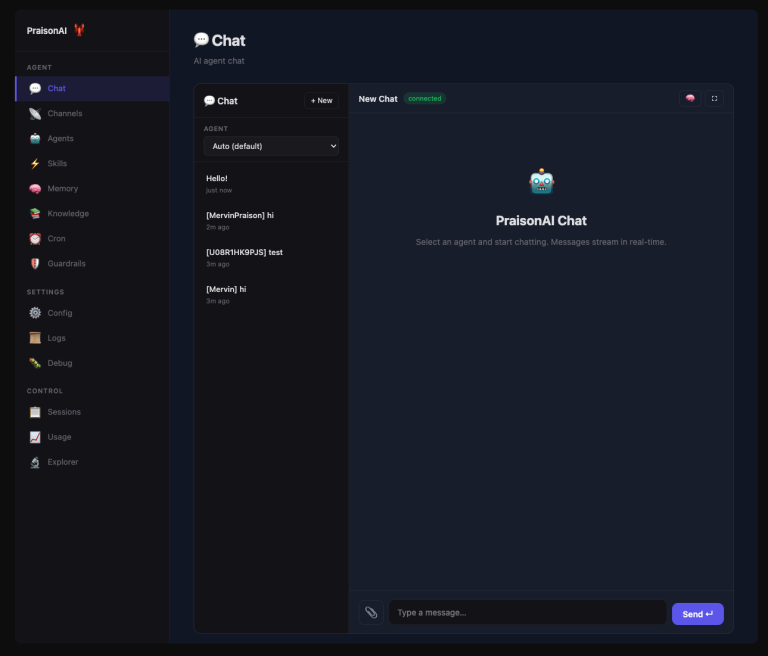
Sysdig warns: PraisonAI (CVE-2026-44338) exploited in under 4 hours. Attackers bypassed auth to hijack agents and drain API quotas. Update to 4.6.34 now!
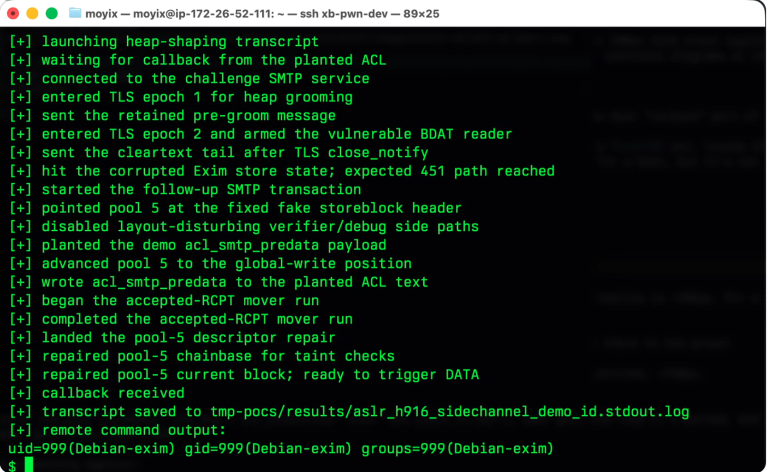
Urgent: Exim fixes a 9.8 severity RCE (CVE-2026-45185) affecting GnuTLS builds. A single-byte heap corruption allows for server takeover. Update to 4.99.3 now!

Urgent: Fortinet warns of 9.1 severity flaws in FortiSandbox (CVE-2026-26083) and FortiAuthenticator (CVE-2026-44277). Patch now to prevent unauthorized RCE.

Urgent: dnsmasq patches 6 critical flaws (CVE-2026-2291+) enabling DNS poisoning and root access. Update your router firmware to version 2.92rel2 now!
Urgent: Casdoor IAM platform hit by critical file write flaw (CVE-2026-44213). Attackers can bypass sandboxes to overwrite databases and gain host access.

Urgent: Siemens patches a 9.3 severity Path Traversal (CVE-2026-41551) in ROS#. Attackers can read/write arbitrary files on robotics systems. Update to V2.2.2!
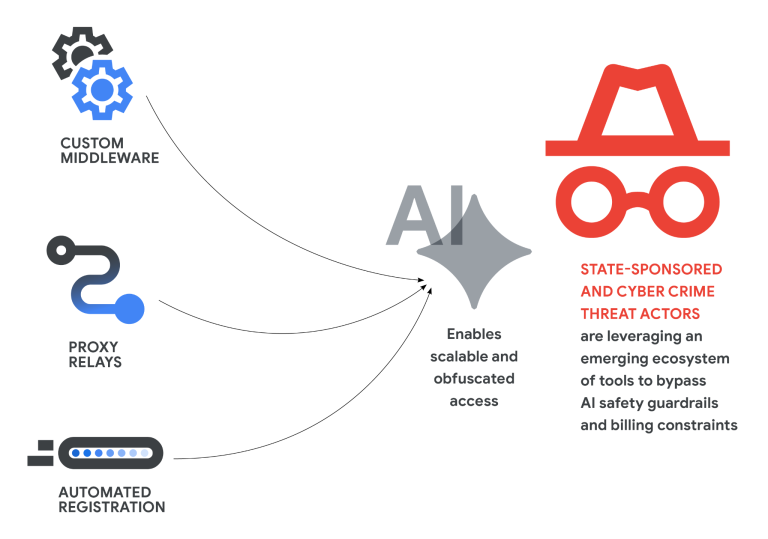
Google GTIG confirms the first AI-built zero-day exploit used in the wild. Discover how AI is industrializing cyber warfare and how Big Sleep is fighting back.
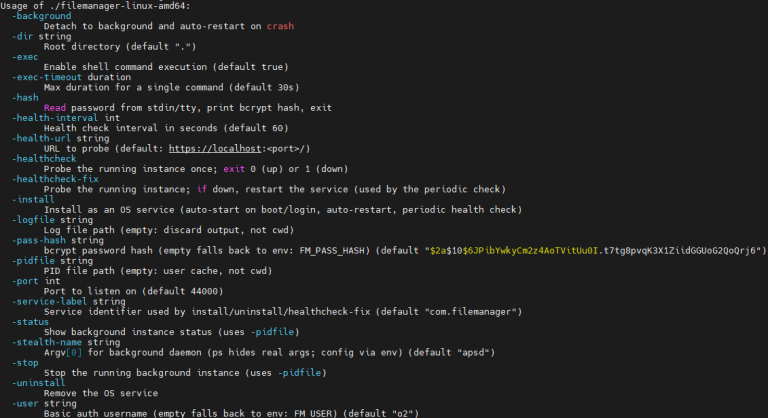
Urgent: cPanel & WHM hit by global 9.8 CVSS auth bypass. Over 2,000 IPs are actively hijacking servers for data theft and ransomware. Patch immediately!
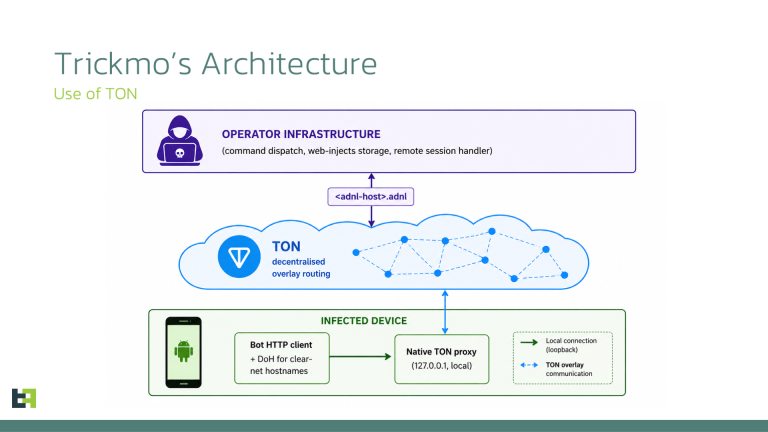
ThreatFabric uncovers TrickMo Variant C, a new Android banking trojan using the decentralized TON network to evade detection and turn phones into proxies.
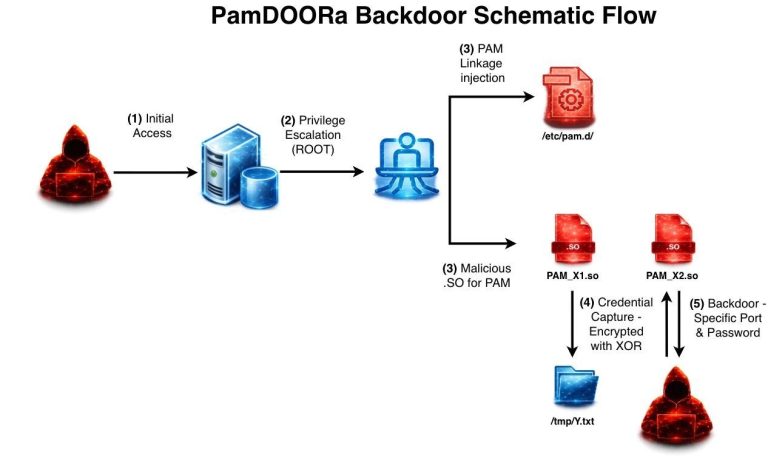
Flare unmasks PamDOORa: a $1,600 Linux backdoor that hijacks the PAM stack to harvest credentials and manipulate authentication logs to evade detection.

Urgent: Dell patches a 9.8 severity credential flaw (CVE-2026-40636) in ECS and ObjectScale. Secure your enterprise storage by upgrading to version 4.3.0.0.
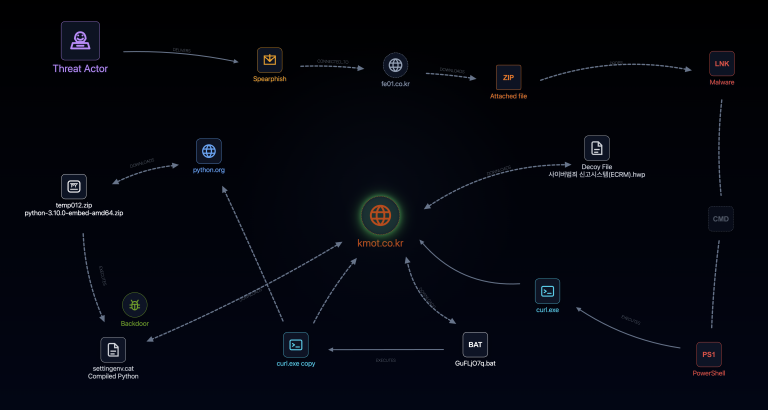
Genians unmasks an APT37 campaign using environment variable tricks and compiled Python malware to bypass EDR. Protect your network from these stealthy lures.