Skip to content
November 3, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
Exploited in the Wild: Critical OWA Spoofing Flaw (CVE-2026-42897) Hits On-Premises Exchange Servers Outlook Web Access Exploit CVE-2026-42897 Exchange Server
  • Vulnerability Report

Exploited in the Wild: Critical OWA Spoofing Flaw (CVE-2026-42897) Hits On-Premises Exchange Servers
Do Son May 15, 2026 0

CVE-2026-42897 exploited in the wild. A 8.1 CVSS OWA flaw allows RCE via malicious emails. Verify your Exchange Emergency Mitigation (EM) status now!

79 Security Holes Sealed: Google Issues Urgent Chrome Update to Fix 14 “Critical” Vulnerabilities Chrome Security Update May 2026 Chrome Critical Vulnerabilities Fix
  • Vulnerability Report

79 Security Holes Sealed: Google Issues Urgent Chrome Update to Fix 14 “Critical” Vulnerabilities

Do Son May 15, 2026 0

Google Chrome patches 79 vulnerabilities, including 14 "Critical" RCE threats. Update to version 148.0.7778.167 now to protect your data and browser.

Exploited in the Wild: Maximum CVSS 10 SD-WAN Flaw (CVE-2026-20182) Grants Admin Control Cisco SD-WAN Exploited CVE-2026-20182 CVSS 10
  • Vulnerability Report

Exploited in the Wild: Maximum CVSS 10 SD-WAN Flaw (CVE-2026-20182) Grants Admin Control

Do Son May 15, 2026 0

Cisco Catalyst SD-WAN CVE-2026-20182 (CVSS 10) exploited in the wild. Attackers bypassing auth to seize admin control. Upgrade your network fabric now!

Nginx Releases Critical Update: Six Vulnerabilities Patched in New Stable Version NGINX JavaScript Module Vulnerability CVE-2026-8711 NGINX 1.30.1 Security Update CVE-2026-42945 RCE NGINX Vulnerability CVE-2026-1642 NGINX Github - CVE-2025-23419
  • Vulnerability Report

Nginx Releases Critical Update: Six Vulnerabilities Patched in New Stable Version

Do Son May 14, 2026 0

NGINX 1.30.1 fixes a 9.2 CVSS RCE flaw (CVE-2026-42945) and five other critical vulnerabilities. Protect your web infrastructure and update immediately!

Critical IKEv2 Buffer Overflow and CAS Bypass Hit Palo Alto PAN-OS PAN-OS IKEv2 Buffer Overflow CVE-2026-0263 Palo Alto Cortex XDR Privilege Escalation Palo Alto Networks Vulnerability CVE-2026-0229 PAN-OS Vulnerability CVE-2026-0227 CVE-2024-5914 - Palo Alto Networks - CVE-2025-0108 & CVE-2025-0110
  • Vulnerability Report

Critical IKEv2 Buffer Overflow and CAS Bypass Hit Palo Alto PAN-OS

Do Son May 14, 2026 0

Palo Alto Networks patches CVE-2026-0263 and CVE-2026-0265. Fixes for IKEv2 RCE and CAS bypass are now available. Update your PAN-OS firewalls immediately!

Googlebook Debuts with AluminumOS and Surprising x86 Intel Support Googlebook AluminumOS laptop
  • Technology

Googlebook Debuts with AluminumOS and Surprising x86 Intel Support

Do Son May 14, 2026 0

Google unveils the Googlebook series powered by AluminumOS. Discover how Intel's x86 architecture is bringing native Android apps to a powerful new desktop.

Update Alert: Windows 11 KB5089549 Triggers Widespread Network Degradation and Installation Failures Windows 11 app updates Windows Insider preview build, Calculator app update, built-in Windows apps Windows 11 KB5089549 network lag Windows 11 Home to Pro Education upgrade Windows 11 Start menu update Windows 11 update KB5079391 Windows 11 KB5085516 OOB update Windows 11 C drive permission error Windows 11 C drive access denied Windows native NVMe driver UEFI Secure Boot certificate rotation Windows 11 printer driver policy Windows 11 printer driver deprecation Windows 11 Build 26300 Sysmon Windows 11 Storage settings restriction Windows 11 Build 26300.7674, Windows Insider channel migration 2026 Windows 11 Update Fix KB5073455 shutdown bug, Secure Launch restart loop Windows 11 File Explorer search performance, Search Indexer RAM usage fix Windows 11 Gaming PC Specs, NVMe DirectStorage Windows 10 End of Support Windows 11 Slow Adoption Windows 11 Crash Loop KB5062553 Bug Update and Shut Down, KB5067036 Windows authentication, Kerberos bug Windows 11 fix, localhost bug Windows 11 Update Restart, Update and Shut Down Windows SMBv1 Windows 11 Arm, Easy Anti-Cheat Windows 11 error, Pluton Windows 11 24H2, Easy Anti-Cheat Windows Firewall Bug, Microsoft Update Error Windows 11, JScript9Legacy Windows Activation, TSforge Windows 11 Update, Firewall Error Windows 11 25H2, Annual Update Windows Resiliency Initiative, Kernel Security Windows 11 Upgrade, ESU Program Windows 11 Recall, Data Export Windows 11 Easy Anti-Cheat Windows 11 Update, Cumulative Update Windows Update, ACPI.sys Windows Updates, Enterprise Software Windows 11 Start Data Encryption Standard Printing Problems Windows 11 updates Estimated installation time Smart App Control, Windows 11 security
  • Windows

Update Alert: Windows 11 KB5089549 Triggers Widespread Network Degradation and Installation Failures

Do Son May 14, 2026 0

Windows 11 KB5089549 is causing severe network lag and boot-loop installation failures. Learn why IT admins say the latency persists even after uninstallation.

Weaponized JPEG Payload Deploys Trojanized ScreenConnect for Covert Espionage axios Supply Chain Attack WAVESHAPER.V2 SnappyBee Malware Salt Typhoon Stately Taurus ScoringMathTea RAT, Lazarus Reflective DLL
  • Cybercriminals

Weaponized JPEG Payload Deploys Trojanized ScreenConnect for Covert Espionage

Do Son May 14, 2026 0

CYFIRMA warns of Operation SilentCanvas: A weaponized JPEG delivers trojanized ScreenConnect, bypassing AMSI and UAC for full-system surveillance. Stay alert!

Exploited in the Wild: Critical 9.8 CVSS RCE Hits Canon GUARDIANWALL MailSuite GUARDIANWALL MailSuite Exploit CVE-2026-32661 FileZen Vulnerability CVE-2026-25108 Ivanti EPMM Vulnerability Dormant Backdoor Fortinet Authentication Bypass CVE-2026-24858 VMware vCenter Server Flaw CVE-2025-21590
  • Vulnerability Report

Exploited in the Wild: Critical 9.8 CVSS RCE Hits Canon GUARDIANWALL MailSuite

Do Son May 14, 2026 0

CVE-2026-32661 exploited in the wild. A 9.8 CVSS flaw in GUARDIANWALL MailSuite allows unauthenticated RCE. Apply Canon's official patches immediately.

200K Sites at Risk: 9.8 CVSS RCE via Burst Statistics Auth Bypass Exploited in the Wild Burst Statistics Authentication Bypass CVE-2026-8181 Exploit
  • Vulnerability Report

200K Sites at Risk: 9.8 CVSS RCE via Burst Statistics Auth Bypass Exploited in the Wild

Do Son May 14, 2026 0

200,000+ sites hit by CVE-2026-8181. A 9.8 CVSS Burst Statistics flaw allows RCE via auth bypass. 5,000+ attacks blocked. Update to 3.4.2 immediately!

Architectural Breach: AMD Zen 2 Flaw Allows Higher-Privilege Instruction Corruption AMD Zen 2 Vulnerability CVE-2025-54518 AMD EPYC processors vulnerability - CVE-2023-31315
  • Vulnerability Report

Architectural Breach: AMD Zen 2 Flaw Allows Higher-Privilege Instruction Corruption

Do Son May 14, 2026 0

Urgent: AMD Zen 2 processors (Ryzen/EPYC) hit by CVE-2025-54518. Hardware flaw allows instruction corruption and privilege escalation. Update your BIOS now!

GitLab Critical Patch: High-Severity XSS and Unauthenticated DoS Flaws Hit Self-Managed Instances GitLab security updates, GitLab patch release, CVE-2026-6552, CVE-2026-10087, CVE-2026-7250 GitLab Security Update May 2026 GitLab XSS and DoS Vulnerabilities GitLab Security Session Hijacking GitLab Security Update, CI/CD Vulnerability GitLab DoS, Security Update bypassing SAML - CVE-2024-8312 and CVE-2024-6826
  • Vulnerability Report

GitLab Critical Patch: High-Severity XSS and Unauthenticated DoS Flaws Hit Self-Managed Instances

Do Son May 14, 2026 0

GitLab patches high-severity XSS (8.7 CVSS) and unauthenticated DoS flaws in versions 18.11.3, 18.10.6, and 18.9.7. Secure your DevOps pipeline now!

Critical 9.6 Severity Ivanti Xtraction Flaw Exposes Sensitive Data Ivanti EPMM security updates Ivanti ITSM vulnerability authenticated privilege escalation Ivanti Xtraction vulnerability CVE-2026-8043 Ivanti EPM RCE, SQL Injection Ivanti EPM, remote code execution CVE-2024-50330 - CVE-2025-0282 and CVE-2025-0283
  • Vulnerability Report

Critical 9.6 Severity Ivanti Xtraction Flaw Exposes Sensitive Data

Do Son May 14, 2026 0

Ivanti issues an urgent patch for CVE-2026-8043, a critical 9.6 CVSS flaw in Xtraction allowing attackers to read files and write malicious HTML. Update now!

Critical MongoDB Flaw CVE-2026-8053 Paves the Way for Server Takeover MongoDB Vulnerability CVE-2026-25611 MongoDB zlib vulnerability, CVE-2025-14847 MongoDB Vulnerabilities, Data Access CVE-2024-6376 CVE-2025-0755
  • Vulnerability Report

Critical MongoDB Flaw CVE-2026-8053 Paves the Way for Server Takeover

Do Son May 14, 2026 0

Urgent: A memory corruption flaw in MongoDB time-series collections (CVE-2026-8053) enables server takeover. Patch to versions 8.3.2, 8.0.23, or 7.0.34 now.

OPNsense Critical Root RCE (CVE-2026-44194 & CVE-2026-45158) Details and PoC Disclosed OPNsense RCE Vulnerability CVE-2026-44194 PoC
  • Vulnerability Report

OPNsense Critical Root RCE (CVE-2026-44194 & CVE-2026-45158) Details and PoC Disclosed

Do Son May 14, 2026 0

Urgent: Public PoC for OPNsense CVE-2026-44194 and CVE-2026-45158. Critical flaws allow root command execution via DHCP and User sync. Update to 26.1.8 now!

Urgent Update: Composer Vulnerability Leaks GitHub Secrets in Plaintext Logs (CVE-2026-45793) CVE-2026-40176, CVE-2026-40261 Composer GitHub Token Leak CVE-2026-45793
  • Vulnerability Report

Urgent Update: Composer Vulnerability Leaks GitHub Secrets in Plaintext Logs (CVE-2026-45793)

Do Son May 14, 2026 0

Composer CVE-2026-45793 leaks GitHub tokens into CI/CD logs due to a validation error. Update to version 2.9.8 now and audit your GitHub Action logs.

Critical 18-Year-Old NGINX RCE (CVE-2026-42945) and GitHub PoC Disclosed NGINX RCE Vulnerability CVE-2026-42945 PoC
  • Vulnerability Report

Critical 18-Year-Old NGINX RCE (CVE-2026-42945) and GitHub PoC Disclosed

Do Son May 14, 2026 0

Public PoC for NGINX CVE-2026-42945. An 18-year-old RCE flaw in the rewrite module enables server takeover. Update to NGINX 1.31.0 or 1.30.1 immediately.

Fragnesia Universal Linux Root LPE Details and One-Line PoC Disclosed Fragnesia Linux Exploit Universal LPE PoC
  • Linux
  • Vulnerability Report

Fragnesia Universal Linux Root LPE Details and One-Line PoC Disclosed

Do Son May 13, 2026 0

Public PoC for Fragnesia. This universal Linux LPE exploit allows unprivileged users to seize root via the page cache. Patch your kernel immediately!

What Controlled Unclassified Information Means for Your Business Operations busi
  • Technique

What Controlled Unclassified Information Means for Your Business Operations

Do Son May 13, 2026 0
One of the most common sources of confusion among defense contractors preparing for CMMC certification is also...
Read More Read more about What Controlled Unclassified Information Means for Your Business Operations
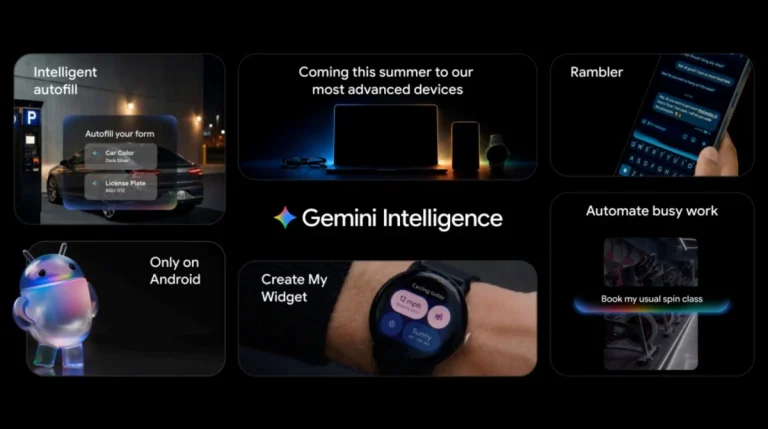
Chrome for Android Gains Gemini 3.1, Nano Banana Image Synthesis, and “Auto Browse” Powers Chrome Gemini 3.1 Android update
  • Technology

Chrome for Android Gains Gemini 3.1, Nano Banana Image Synthesis, and “Auto Browse” Powers

Do Son May 13, 2026 0

Google transforms Chrome into an "Intelligent Browsing Companion" with Gemini 3.1. Explore Auto Browse, real-time image synthesis, and AI webpage deconstruction.

Android 17 Adds Native AirDrop Support and “Zero-Friction” iOS Migration Android 17 AirDrop support
  • Android

Android 17 Adds Native AirDrop Support and “Zero-Friction” iOS Migration

Do Son May 13, 2026 0

Google I/O 2026 bombshell: Android 17's Quick Share adds native AirDrop support and a "one-tap" iOS migration tool. See the new Noto 3D emojis and Pause Point.

The “Unbreakable” OS: Android 17 Unveils AI-Powered Fraud Defense and Thief-Proof Biometrics Android 17 security features
  • Android

The “Unbreakable” OS: Android 17 Unveils AI-Powered Fraud Defense and Thief-Proof Biometrics

Do Son May 13, 2026 0

Google’s 2026 Android roadmap turns AI into a "Live Threat Detection" sentinel. Explore Android 17’s new anti-theft biometrics and banking fraud intercepts.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-81648CVSS 10.0
    The CryptoPayment Gateway WordPress plugin from 1.2.1 to 1.2.2 does not apply an authorization check on one of...
    Admin intel📅 Updated: Nov 3, 2026
  • CVE-2026-58115CVSS 10.0
    A vulnerability has been identified in SIMATIC IoT2050 Advanced (6ES7647-0BA00-1YA2) (All versions < V4.3.4.1 running Industrial OS with...
    Admin intel📅 Updated: Nov 2, 2026
  • CVE-2026-20051CVSS 7.4
    A vulnerability with the Ethernet VPN (EVPN) Layer 2 ingress packet processing of Cisco Nexus 3600 Platform Switches...
    Watchtower Verified📅 Updated: Nov 1, 2026
  • CVE-2026-20118CVSS 6.8
    A vulnerability in the handling of an Egress Packet Network Interface (EPNI) Aligner interrupt in Cisco IOS XR...
    Watchtower Verified📅 Updated: Nov 1, 2026
  • CVE-2010-20125CVSS 8.7
    DedeCMS before 5.7 contains a file inclusion vulnerability in plus/carbuyaction.php that allows remote unauthenticated attackers to control the...
    Watchtower Verified📅 Updated: Oct 30, 2026
  • CVE-2015-20130CVSS 5.1
    Netsweeper before 4.0.11 and 4.1.0 before 4.1.5 contains a reflected cross-site scripting vulnerability in webadmin/reporter/view_server_log.php that allows remote...
    Watchtower Verified📅 Updated: Oct 30, 2026
  • CVE-2026-111357CVSS 7.0
    Ivanti Connect Secure 22.8R2.4 mishandles the manner in which the dsinvoked broker trusts DSCache configuration data, leading to...
    CISA KEV📅 Added to KEV: Oct 30, 2026
  • CVE-2026-118527CVSS 4.3
    Use of predictable filenames in Ivanti Connect Secure before versions 25.1.1.3 and 22.8R2.6 allows a remote authenticated attacker...
    CISA KEV📅 Added to KEV: Oct 30, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-77876CVSS 9.3
    Control Web Panel (CWP) before webpanel_version 1.16 contains an OS command injection vulnerability in the protected_directory user panel...
    📅 Updated: Nov 3, 2026
  • CVE-2026-73696CVSS 9.3
    Control Web Panel (CWP) before webpanel_version 1.12 contains an execution after redirect vulnerability in the user panel authentication...
    📅 Updated: Nov 3, 2026
  • CVE-2026-58256CVSS 9.1
    GRR is a resource management and reservation application. Prior to the advisory-reported fixed version 4.5.0, an administrator can...
    📅 Updated: Nov 3, 2026
  • CVE-2026-115904CVSS 9.6
    Topluyo is a social networking platform. A vulnerability exists in Topluyo Desktop for Linux prior to version 2026.9.2410...
    📅 Updated: Nov 3, 2026
  • CVE-2026-118375CVSS 9.2
    llama.cpp b8841 before b11865 contains an out-of-bounds write vulnerability in the ggml-rpc RDMA transport rdma_recv() function that allows...
    📅 Updated: Nov 3, 2026
  • CVE-2026-54749CVSS 9.4
    Summary Three custom API-Platform controllers under `src/CoreBundle/Controller/Api/` perform privileged mutations but enforce only a global platform role (`ROLE_TEACHER`)...
    📅 Updated: Nov 3, 2026
  • CVE-2026-89292CVSS 9.2
    In Eclipse Mnestix Browser versions 1.6.0 up until but excluding 2.3.0 it was possible for an unauthenticated attacker...
    📅 Updated: Nov 3, 2026
  • CVE-2026-121022CVSS 9.2
    Use of Default Password (CWE-1393) in the web client in AxxonSoft Axxon One before 3.0.0 on Windows and...
    📅 Updated: Nov 3, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.