Skip to content
November 3, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
OpenAI Debuts “Finances” Feature to Turn ChatGPT into Your Personal Wealth Manager ChatGPT Finances Plaid feature
  • Technology

OpenAI Debuts “Finances” Feature to Turn ChatGPT into Your Personal Wealth Manager

Do Son May 18, 2026 0

OpenAI launches Finances for ChatGPT Pro! Integrated with Plaid, the AI securely reads your real-time bank and investment data for custom wealth advice.

Critical RCE Flaw in Apache Flink (CVE-2026-35194) Threatens TaskManagers CVE-2020-17519 Apache Flink Vulnerability CVE-2026-35194 RCE
  • Vulnerability Report

Critical RCE Flaw in Apache Flink (CVE-2026-35194) Threatens TaskManagers

Do Son May 18, 2026 0

Critical CVE-2026-35194 flaw in Apache Flink allows RCE via SQL injection on TaskManagers. Upgrade your clusters immediately to secure your data!
Critical Strapi Flaws Enable Unauthenticated Admin Takeover and Server RCE Strapi CMS Vulnerabilities CVE-2026-27886 Admin Takeover
  • Vulnerability Report

Critical Strapi Flaws Enable Unauthenticated Admin Takeover and Server RCE

Do Son May 18, 2026 0

Two critical flaws in Strapi CMS (CVE-2026-27886 & CVE-2026-22599) allow unauthenticated admin takeover and SQL injection. Update your nodes now!
The CVE Watchtower: Weekly Threat Intelligence Briefing (May 11 – May 17, 2026) 6
  • Weekly Recap

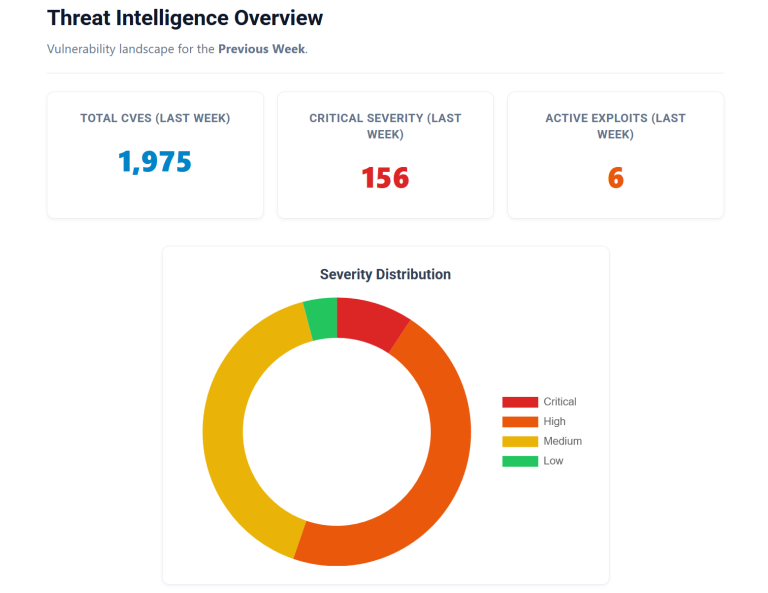
The CVE Watchtower: Weekly Threat Intelligence Briefing (May 11 – May 17, 2026)

Do Son May 18, 2026 0

Cisco SD-WAN (CVE-2026-20182) and Exchange Server (CVE-2026-42897) are actively exploited in the wild! Discover the top threats you must patch now.

Three Critical 9.4 CVSS Flaws Expose n8n Automation Nodes to Full RCE n8n Node RCE Vulnerabilities CVE-2026-44791 Prototype Pollution n8n RCE Vulnerabilities CVE-2026-27497 CVE-2026-25053 n8n RCE Vulnerability CVE-2026-21877 n8n RCE, CVE-2025-68613 n8n Git RCE, core.hooksPath Exploit
  • Vulnerability Report

Three Critical 9.4 CVSS Flaws Expose n8n Automation Nodes to Full RCE

Do Son May 18, 2026 0

n8n fixes three critical 9.4 CVSS flaws (CVE-2026-44790/91/89). Authenticated users can break sandboxes for local file read and server-level RCE. Patch now!

No Encryption Needed: New “GhostLock” Technique Weaponizes Windows SMB to Freeze Enterprise Files GhostLock Ransomware Evasion SMB File Share Lockout
  • Vulnerability Report

No Encryption Needed: New “GhostLock” Technique Weaponizes Windows SMB to Freeze Enterprise Files

Do Son May 18, 2026 0

The GhostLock whitepaper exposes a critical blind spot in ransomware defense. Low-privilege users can freeze SMB shares with zero data encryption.

MiniPlasma Zero-Day: PoC Exploit Code and Vulnerability Details Publicly Disclosed for Windows 11 MiniPlasma exploit Windows privilege escalation
  • Vulnerability Report

MiniPlasma Zero-Day: PoC Exploit Code and Vulnerability Details Publicly Disclosed for Windows 11

Do Son May 18, 2026 0

Details and PoC code for the "MiniPlasma" zero-day exploit are now public. See how a 6-year-old flaw grants SYSTEM access on fully patched Windows 11.
CVSS 10 Alert: Quest KACE SMA Auth Bypass Exploited to Hijack Managed Endpoints Quest KACE SMA Vulnerability CVE-2025-32975 Exploit
  • Vulnerability Report

CVSS 10 Alert: Quest KACE SMA Auth Bypass Exploited to Hijack Managed Endpoints

Do Son May 16, 2026 0

Quest KACE SMA CVE-2025-32975 (CVSS 10) exploited in the wild. Attackers bypass auth to seize admin control. Patch to version 14.1.101 or 14.0.341 now!

RaccoonLine Publishes 2026 Report on Global VPN Blocking and DPI Enforcement pr-13-internet-freedom-index_177884562602hq9EpivU
  • Press Release

RaccoonLine Publishes 2026 Report on Global VPN Blocking and DPI Enforcement

cybernewswire May 15, 2026 0
Rome, Italy, 15th May 2026, CyberNewswire
Read More Read more about RaccoonLine Publishes 2026 Report on Global VPN Blocking and DPI Enforcement
Paper Werewolf Unleashed: Custom Stealers and AI-Assisted Loaders Target Global Industrial Hubs Paper Werewolf Espionage PaperGrabber Malware
  • Malware

Paper Werewolf Unleashed: Custom Stealers and AI-Assisted Loaders Target Global Industrial Hubs

Do Son May 15, 2026 0

Paper Werewolf APT targets industrial sectors with PaperGrabber stealer and EchoGather RAT. Learn to detect their AI-assisted loaders and custom tools.

Stealth & Automation: Seedworm’s 2026 Global Campaign Hijacks Security Software to Deploy ChromElevator Seedworm Espionage Campaign 2026 ChromElevator Stealer DLL Sideloading SIM Swapping Crypto Theft Lazarus Comebacker, Aerospace Espionage Delete PlugX Malware
  • Cyber Security

Stealth & Automation: Seedworm’s 2026 Global Campaign Hijacks Security Software to Deploy ChromElevator

Do Son May 15, 2026 0

Iranian group Seedworm infiltrates global firms using automated Node.js scripts and DLL sideloading via trusted binaries. Protect your credentials now!

Root Access Race: TOCTOU Vulnerability (CVE-2026-41702) Hits VMware Fusion VMware Fusion Privilege Escalation CVE-2026-41702 TOCTOU VMware Vulnerabilities, Broadcom Security CVE-2024-38814 - VMware HCX CVE-2025-22224, CVE-2025-22225, and CVE-2025-22226
  • Vulnerability Report

Root Access Race: TOCTOU Vulnerability (CVE-2026-41702) Hits VMware Fusion

Do Son May 15, 2026 0

VMware Fusion CVE-2026-41702 allows local users to gain root access via a TOCTOU race condition. Secure your host and update to 26H1 immediately!

OpenAI Forces Code Signing Certificate Rotation After TanStack Supply Chain Breach OpenAI confidential IPO filing OpenAI code signing certificate rotation AI private equity joint ventures OpenAI Axios Supply Chain Attack OpenAI Promptfoo acquisition OpenAI military resignation ChatGPT Plus military fraud OpenAI smart speaker Jony Ive OpenAI Frontier platform ChatGPT AI age prediction 2026, OpenAI Persona age verification Sarah Friar OpenAI infrastructure, AI Scaling Law revenue OpenAI Gumdrop AI pen, Jony Ive OpenAI hardware 2027 OpenAI New CRO, Denise Dresser Monetization Strategy OpenAI Competitive Pressure Gemini 3 Overtake OpenAI Infrastructure, AI Closed Loop Economy
  • Data Leak

OpenAI Forces Code Signing Certificate Rotation After TanStack Supply Chain Breach

Do Son May 15, 2026 0

OpenAI rotates code signing certificates following the TanStack npm breach. macOS users must update ChatGPT and Codex manually before June 12, 2026.
Desktop Power, Mobile Control: OpenAI Brings Remote Codex Management to the ChatGPT App OpenAI legacy model deprecation OpenAI Codex mobile integration
  • Technology

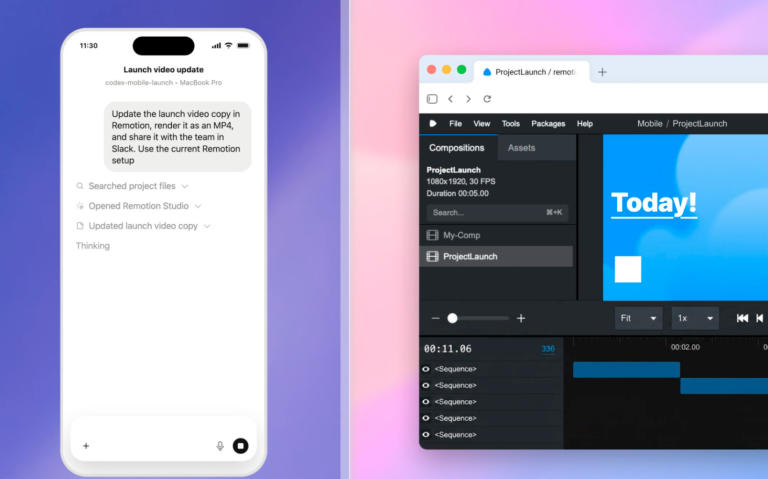
Desktop Power, Mobile Control: OpenAI Brings Remote Codex Management to the ChatGPT App

Do Son May 15, 2026 0

OpenAI integrates Codex into the ChatGPT app! Monitor tasks, approve code, and manage remote macOS environments from your phone with encrypted secure relays.
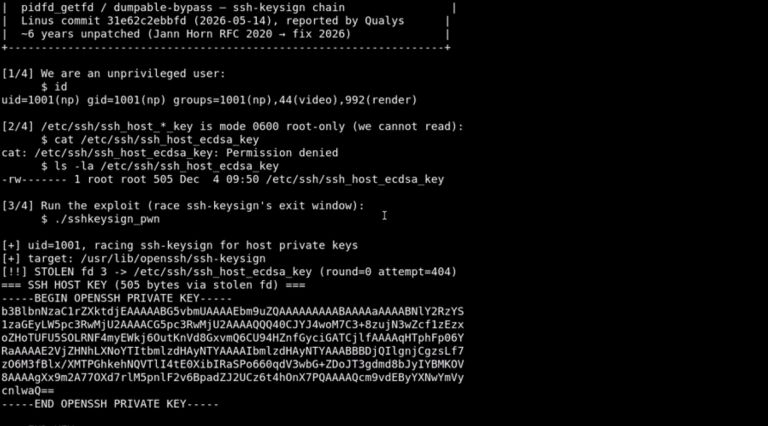
PoC Released: Critical Linux Kernel ptrace Flaw Publicly Disclosed—Unprivileged Root File Access Possible key
  • Linux
  • Vulnerability Report

PoC Released: Critical Linux Kernel ptrace Flaw Publicly Disclosed—Unprivileged Root File Access Possible

Do Son May 15, 2026 0

Technical details and PoC exploits disclosed for Linux Kernel ptrace flaw. Unprivileged users can steal root file descriptors. Patch to May 14 release!

Apple Joins Google to Fight EU Mandate on Deep AI System Access Apple Google EU alliance DMA European Commission Breach Trivy Supply Chain Attack Europa.eu Breach EU Cloud Infrastructure EU Cyber Sanctions State-Sponsored Hacking EU 2040 Emissions Target, Europe Climate Leadership AWS Azure DMA Cloud Gatekeeper DSA violation, illegal content Apple DMA Delay, iPhone Mirroring EU EU Age Verification, Google Play Integrity Corning Antitrust, EU Competition Apple EU Digital Markets Act App Store commission European Union cyberattacks - InvestAI EU Targets Musk’s X Digital Markets Act, EU fines
  • Technology

Apple Joins Google to Fight EU Mandate on Deep AI System Access

Do Son May 15, 2026 0

Apple and Google form a rare alliance to block an EU mandate. Discover why Apple is fighting to stop third-party AI from accessing Android’s core architecture.

cPanel & WHM Patch 5 High-Severity Flaws, Including 8.6 Severity File Read and SQLi cPanel WHM Vulnerabilities 2026 CVE-2026-29205 Arbitrary File Read cPanel Security Vulnerability Perl Injection Exploit cPanel Authentication WHM Security cPanel Privilege Escalation, Directory Traversal LPE
  • Vulnerability Report

cPanel & WHM Patch 5 High-Severity Flaws, Including 8.6 Severity File Read and SQLi

Do Son May 15, 2026 0

cPanel & WHM fix 5 critical vulnerabilities (CVE-2026-29205). Fixes for arbitrary file read, SQLi, and privilege escalation are now live. Update now!

No Password Required: 9.8 Severity ELECOM Router Flaws Allow Total Network Takeover ELECOM Router Vulnerability CVE-2026-42062 Command Injection
  • Vulnerability Report

No Password Required: 9.8 Severity ELECOM Router Flaws Allow Total Network Takeover

Do Son May 15, 2026 0

ELECOM routers hit by critical 9.8 CVSS flaws (CVE-2026-42062). Unauthenticated attackers can execute OS commands and bypass auth. Update firmware now!

Cisco SD-WAN Manager XXE Flaw Grants Unauthenticated Access to Private Files Cisco SD-WAN Manager Vulnerability CVE-2026-20224 XXE
  • Vulnerability Report

Cisco SD-WAN Manager XXE Flaw Grants Unauthenticated Access to Private Files

Do Son May 15, 2026 0

Cisco fixes a critical 8.6 CVSS XXE flaw (CVE-2026-20224) in Catalyst SD-WAN Manager. Unauthenticated attackers can read arbitrary files. Patch now!

Critical 9.2 CVSS RCE Found in Amazon Redshift JDBC Driver Amazon Redshift JDBC Driver RCE CVE-2026-8178 AWS Bahrain fire 2026 AWS UAE data center fire Amazon North Korean hacker keystroke latency, Arizona laptop farm infiltration
  • Vulnerability Report

Critical 9.2 CVSS RCE Found in Amazon Redshift JDBC Driver

Do Son May 15, 2026 0

CVE-2026-8178 in Amazon Redshift JDBC Driver allows RCE via unsafe class loading. Protect your data warehouse and update to version 2.2.2 now!

Critical 9.4 CVSS pgAdmin 4 Flaws Enable Full OS Command Execution pgAdmin 4 Vulnerabilities CVE-2026-7813 Authorization Bypass pgAdmin RCE, BOM Bypass Flaw
  • Vulnerability Report

Critical 9.4 CVSS pgAdmin 4 Flaws Enable Full OS Command Execution

Do Son May 15, 2026 0

pgAdmin 4 v9.15 fixes a 9.4 CVSS auth bypass and multiple RCE flaws. Attackers can execute OS commands via SQL tools. Upgrade your pgAdmin server now!

Kubernetes Alert: 9.4 Severity RCE in CloudNativePG Enables PostgreSQL Superuser Takeover CloudNativePG RCE Vulnerability CVE-2026-44477
  • Vulnerability Report

Kubernetes Alert: 9.4 Severity RCE in CloudNativePG Enables PostgreSQL Superuser Takeover

Do Son May 15, 2026 0

CVE-2026-44477 in CloudNativePG allows low-privilege users to gain root-level RCE via metrics exporters. Update to version 1.29.1 or 1.28.3 now!

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-81648CVSS 10.0
    The CryptoPayment Gateway WordPress plugin from 1.2.1 to 1.2.2 does not apply an authorization check on one of...
    Admin intel📅 Updated: Nov 3, 2026
  • CVE-2026-58115CVSS 10.0
    A vulnerability has been identified in SIMATIC IoT2050 Advanced (6ES7647-0BA00-1YA2) (All versions < V4.3.4.1 running Industrial OS with...
    Admin intel📅 Updated: Nov 2, 2026
  • CVE-2026-20051CVSS 7.4
    A vulnerability with the Ethernet VPN (EVPN) Layer 2 ingress packet processing of Cisco Nexus 3600 Platform Switches...
    Watchtower Verified📅 Updated: Nov 1, 2026
  • CVE-2026-20118CVSS 6.8
    A vulnerability in the handling of an Egress Packet Network Interface (EPNI) Aligner interrupt in Cisco IOS XR...
    Watchtower Verified📅 Updated: Nov 1, 2026
  • CVE-2010-20125CVSS 8.7
    DedeCMS before 5.7 contains a file inclusion vulnerability in plus/carbuyaction.php that allows remote unauthenticated attackers to control the...
    Watchtower Verified📅 Updated: Oct 30, 2026
  • CVE-2015-20130CVSS 5.1
    Netsweeper before 4.0.11 and 4.1.0 before 4.1.5 contains a reflected cross-site scripting vulnerability in webadmin/reporter/view_server_log.php that allows remote...
    Watchtower Verified📅 Updated: Oct 30, 2026
  • CVE-2026-111357CVSS 7.0
    Ivanti Connect Secure 22.8R2.4 mishandles the manner in which the dsinvoked broker trusts DSCache configuration data, leading to...
    CISA KEV📅 Added to KEV: Oct 30, 2026
  • CVE-2026-118527CVSS 4.3
    Use of predictable filenames in Ivanti Connect Secure before versions 25.1.1.3 and 22.8R2.6 allows a remote authenticated attacker...
    CISA KEV📅 Added to KEV: Oct 30, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-77876CVSS 9.3
    Control Web Panel (CWP) before webpanel_version 1.16 contains an OS command injection vulnerability in the protected_directory user panel...
    📅 Updated: Nov 3, 2026
  • CVE-2026-73696CVSS 9.3
    Control Web Panel (CWP) before webpanel_version 1.12 contains an execution after redirect vulnerability in the user panel authentication...
    📅 Updated: Nov 3, 2026
  • CVE-2026-58256CVSS 9.1
    GRR is a resource management and reservation application. Prior to the advisory-reported fixed version 4.5.0, an administrator can...
    📅 Updated: Nov 3, 2026
  • CVE-2026-115904CVSS 9.6
    Topluyo is a social networking platform. A vulnerability exists in Topluyo Desktop for Linux prior to version 2026.9.2410...
    📅 Updated: Nov 3, 2026
  • CVE-2026-118375CVSS 9.2
    llama.cpp b8841 before b11865 contains an out-of-bounds write vulnerability in the ggml-rpc RDMA transport rdma_recv() function that allows...
    📅 Updated: Nov 3, 2026
  • CVE-2026-54749CVSS 9.4
    Summary Three custom API-Platform controllers under `src/CoreBundle/Controller/Api/` perform privileged mutations but enforce only a global platform role (`ROLE_TEACHER`)...
    📅 Updated: Nov 3, 2026
  • CVE-2026-89292CVSS 9.2
    In Eclipse Mnestix Browser versions 1.6.0 up until but excluding 2.3.0 it was possible for an unauthenticated attacker...
    📅 Updated: Nov 3, 2026
  • CVE-2026-121022CVSS 9.2
    Use of Default Password (CWE-1393) in the web client in AxxonSoft Axxon One before 3.0.0 on Windows and...
    📅 Updated: Nov 3, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.