Skip to content
November 3, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
Iranian APT MuddyWater Masquerades as Chaos Ransomware in Elaborate False Flag MuddyWater APT Ransomware False Flag
  • Cyber Security

Iranian APT MuddyWater Masquerades as Chaos Ransomware in Elaborate False Flag

Do Son May 11, 2026 0

Rapid7 unmasks Iranian APT MuddyWater using a Chaos ransomware "false flag" to hide state-sponsored espionage. See how they bypassed MFA via MS Teams.
Fileless Python Malware Uses Humanitarian Lures to Deploy Full-Spectrum Surveillance Python Cyberespionage Fileless Malware
  • Malware

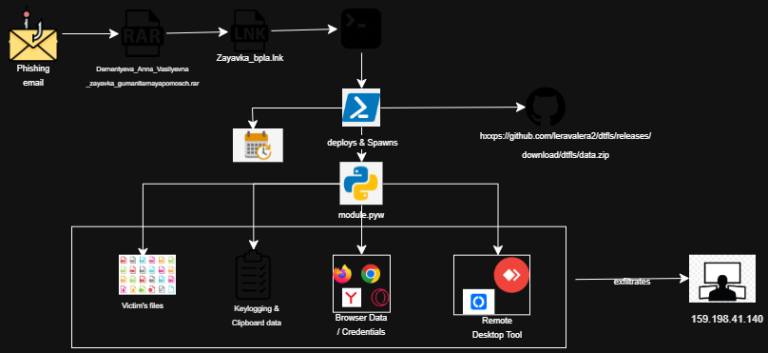
Fileless Python Malware Uses Humanitarian Lures to Deploy Full-Spectrum Surveillance

Do Son May 11, 2026 0

CRIL exposes a cyberespionage campaign using fake humanitarian aid forms to deploy fileless Python malware via GitHub for full-spectrum surveillance.
The CVE Watchtower: Weekly Threat Intelligence Briefing (May 4 – May 10, 2026) Weekly vulnerability digest May 2026
  • Weekly Recap

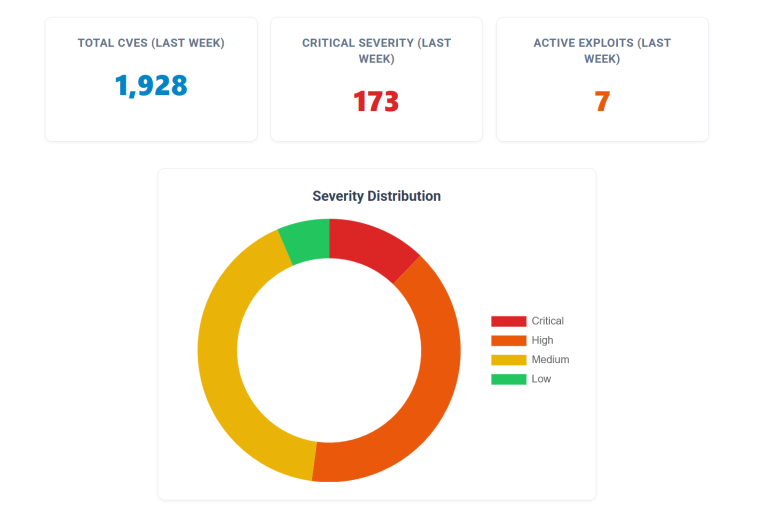
The CVE Watchtower: Weekly Threat Intelligence Briefing (May 4 – May 10, 2026)

Do Son May 11, 2026 0

Weekly Security Digest: 1,928 new vulnerabilities hit the wire. From Palo Alto firewalls to LiteLLM AI gateways, here is how to prioritize your defense.

Quantum-Ready and AI-Driven: How RHEL 10.2 and 9.8 are Redefining Enterprise Linux Security Red Hat Enterprise Linux 10.2 release
  • Linux

Quantum-Ready and AI-Driven: How RHEL 10.2 and 9.8 are Redefining Enterprise Linux Security

Do Son May 11, 2026 0

Red Hat RHEL 10.2 & 9.8 arrive with NIST Post-Quantum Cryptography, AI-driven Ansible upgrades, and MCP servers for natural language system governance.

Beyond Text: How Google Gemini’s New Multimodal RAG Turns Images and PDFs into Actionable Intelligence Google Gemini API file search
  • Technology

Beyond Text: How Google Gemini’s New Multimodal RAG Turns Images and PDFs into Actionable Intelligence

Do Son May 11, 2026 0

Google Gemini API expands file search with Multimodal RAG. Featuring image-text retrieval, custom metadata, and page-level citations for enterprise AI.

Optimization or Artifice? The Truth Behind the Windows 11 “Low Latency Profile” and CPU Speed Bursts Windows 11 Low Latency Profile Windows 11 Build 26300.8289 update
  • Windows

Optimization or Artifice? The Truth Behind the Windows 11 “Low Latency Profile” and CPU Speed Bursts
Do Son May 11, 2026 0

Microsoft is testing a "Low Latency Profile" to fix Windows 11 UI lag with 3-second CPU bursts. Is it lazy engineering or a sophisticated industry standard?

Patch Now: Apache CloudStack Plugs Proxmox and KVM Exploits in New LTS Release CloudStack VM Hijacking Apache CloudStack Security Update CVE-2024-42062 and CVE-2024-42222 - Apache CloudStack
  • Vulnerability Report

Patch Now: Apache CloudStack Plugs Proxmox and KVM Exploits in New LTS Release

Do Son May 11, 2026 0

Urgent: Apache CloudStack patches critical flaws (CVE-2026-25199, CVE-2026-25077) enabling VM hijacking and KVM host RCE. Secure your cloud environment now.

Root Access at Risk: Perl Injection and Symlink Flaws Hit cPanel & WHM cPanel WHM Vulnerabilities 2026 CVE-2026-29205 Arbitrary File Read cPanel Security Vulnerability Perl Injection Exploit cPanel Authentication WHM Security cPanel Privilege Escalation, Directory Traversal LPE
  • Vulnerability Report

Root Access at Risk: Perl Injection and Symlink Flaws Hit cPanel & WHM

Do Son May 11, 2026 0

Update cPanel immediately! High-severity vulnerabilities (CVSS 8.8) allow Perl injection and privilege escalation. Protect your hosting environment now.

The Q1 2026 Exploit Surge: AI Discovers the Flaws, APTs Reap the Rewards shell-quote command injection AI-Driven Vulnerabilities Q1 2026 Cyber Threats vm2 Sandbox Escape Node.js RCE upKeeper Privilege Escalation CVE-2026-2449 Pharos Controls Vulnerability Root Access Exploit Cybersecurity Vulnerability Roundup CVSS 10.0 Flaws Shadow Archives CVE-2026-0866 MS-Agent Prompt Injection CVE-2026-2256 basic-ftp Path Traversal CVE-2026-27699 telnetd Root Vulnerability CVE-1999-0073 Regression USR-W610 Vulnerabilities End-of-Life IoT Security IceWarp Security Update IceWarp Vulnerabilities Airleader Master Vulnerability CVE-2026-1358 ZLAN5143D Vulnerability CISA ICS Advisory Acronis Cyber Protect Vulnerability CVE-2025-30411 WAGO 852 Vulnerability OT Network Security SandboxJS Vulnerability Sandbox Escape (CVSS 10.0) Kubernetes Local Path Provisioner CVE-2025-62878 CISA Unresponsive Vendors Avation & RISS Vulnerabilities KiloView Vulnerability CVE-2026-1453 OpenClaw RCE vulnerability Johnson Controls Vulnerability CVE-2025-26385 SandboxJS Vulnerability CVE-2026-23830 ibaPDA Vulnerability CVE-2025-14988 Protobuf Vulnerability CVE-2026-0994 AVEVA Process Optimization Vulnerability CVE-2025-61937 ConnectWise PSA Vulnerability CVE-2026-0695 Aruba VIA Vulnerability CVE-2025-37186 aiohttp v3.13.3, Denial of Service (DoS) SmarterMail RCE, CVE-2025-52691 Airoha RACE, Headphone Jacking HPE OneView RCE CVE-2025-37164 FreePBX Auth Bypass, PBX Takeover ScreenConnect Config Flaw, Untrusted Extensions Ruby SAML Auth Bypass, XML Parser Differential Devolutions SQL Injection, Password Manager Flaw Vivotek Unauthenticated RCE, EOL IP Camera Flaw Lynx+ Critical Flaw, Unauthenticated Reset Firebox Default Credentials, CVE-2025-59396 Veeder-Root RCE, Critical ATG Flaw ArcGIS Server SQLi Watchdoc RCE, CVE-2025-58384 Delta DIALink Daikin Security Gateway, authentication bypass Frostbyte10, industrial controller security SunPower, vulnerability Ubiquiti UniFi Connect, EV Station Vulnerabilities Adobe Experience Manager, RCE Vulnerability UniFi Access, Command Injection LDAPNightmare - CVE-2025-1316
  • Vulnerability Report

The Q1 2026 Exploit Surge: AI Discovers the Flaws, APTs Reap the Rewards

Do Son May 11, 2026 0

Kaspersky reports a record surge in CVEs for Q1 2026. Discover how AI-driven exploits, authentication bypasses, and new C2 trends are reshaping cyber defense.
Zero-Click Shell: Public Exploit and PoC Disclosed for Android’s Critical ADB Auth Bypass (CVE-2026-0073) Android ADB Auth Bypass CVE-2026-0073 PoC
  • Vulnerability Report

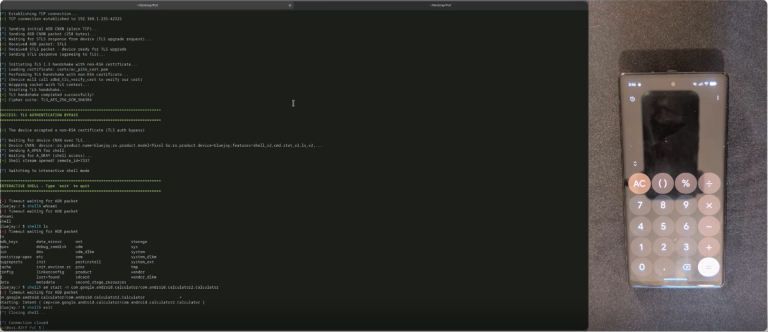
Zero-Click Shell: Public Exploit and PoC Disclosed for Android’s Critical ADB Auth Bypass (CVE-2026-0073)

Do Son May 11, 2026 0

BARGHEST reveals CVE-2026-0073: a zero-click Android ADB bypass over Wi-Fi. Public PoC and exploit details are now live. Secure your mobile device today!
Data Destruction and Memory Poisoning: Spring AI Vulnerabilities Threaten LLM Integrity Spring AI Vulnerability LLM Memory Poisoning Spring AI Vulnerability Vector Store Injection
  • Vulnerability Report

Data Destruction and Memory Poisoning: Spring AI Vulnerabilities Threaten LLM Integrity

Do Son May 11, 2026 0

Protect your AI apps. Spring AI issues urgent patches for three critical vulnerabilities causing data destruction, memory poisoning, and user data leaks.

Zero Installation, Total Compromise: Critical Grav CMS Exploit Chain Grants Unauthenticated RCE Grav CMS Vulnerability CVE-2026-42613
  • Vulnerability Report

Zero Installation, Total Compromise: Critical Grav CMS Exploit Chain Grants Unauthenticated RCE

Do Son May 10, 2026 0

Protect your Grav CMS deployments. Attackers are chaining CVE-2026-42613 and CVE-2026-42607 to achieve unauthenticated remote code execution. Patch today!

Let’s Encrypt Slashes Certificate Lifespans and Sunsets mTLS on May 13 Merkle Tree Certificates Let's Encrypt 45-Day Certificates ACME Profile Updates 2026 Let’s Encrypt Generation Y, 45-Day TLS Certificates Let's Encrypt, IP Certificates Certificate Revocation Lists
  • Technology

Let’s Encrypt Slashes Certificate Lifespans and Sunsets mTLS on May 13

Do Son May 9, 2026 0

May 13 Deadline: Let’s Encrypt launches 45-day certs, freezes mTLS, and moves to Gen Y intermediates. Is your automation ready for the triple-threat update?

Trust Hijacked: Official JDownloader Website Breached to Distribute Malicious Installers JDownloader Breach Supply Chain Attack
  • Malware

Trust Hijacked: Official JDownloader Website Breached to Distribute Malicious Installers

Do Son May 9, 2026 0

JDownloader's website was breached on May 6, swapping official installers for malware. If you downloaded it between May 6-7, your system may be compromised.

Exploited in the Wild: “Dirty Frag” Linux Vulnerability Grants Instant Root Access Dirty Frag Vulnerability Linux Privilege Escalation
  • Vulnerability Report

Exploited in the Wild: “Dirty Frag” Linux Vulnerability Grants Instant Root Access

Do Son May 9, 2026 0

The Dirty Frag Linux vulnerability (CVE-2026-43284) is being actively exploited in the wild. Learn how to secure your servers from this root LPE exploit.
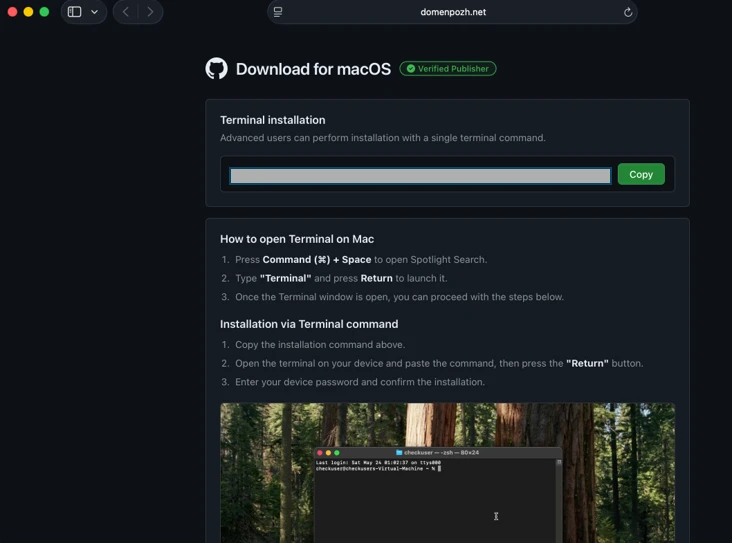
New “ClickFix” Campaign Bypasses Gatekeeper to Hijack macOS Devices macOS ClickFix Campaign Terminal Infostealer
  • Malware

New “ClickFix” Campaign Bypasses Gatekeeper to Hijack macOS Devices

Do Son May 9, 2026 0

Microsoft reveals a macOS ClickFix campaign using fake "fixes" to trick users into running Terminal commands that bypass Gatekeeper and steal crypto wallets.
Critical Sandboxie Escape Flaws Grant Total SYSTEM Takeover Sandboxie Escape CVE-2026-34459
  • Vulnerability Report

Critical Sandboxie Escape Flaws Grant Total SYSTEM Takeover

Do Son May 8, 2026 0

Security researchers expose catastrophic flaws in Sandboxie. CVE-2026-34459 enables a direct sandbox escape to SYSTEM privileges. Update to v1.17.3 today.
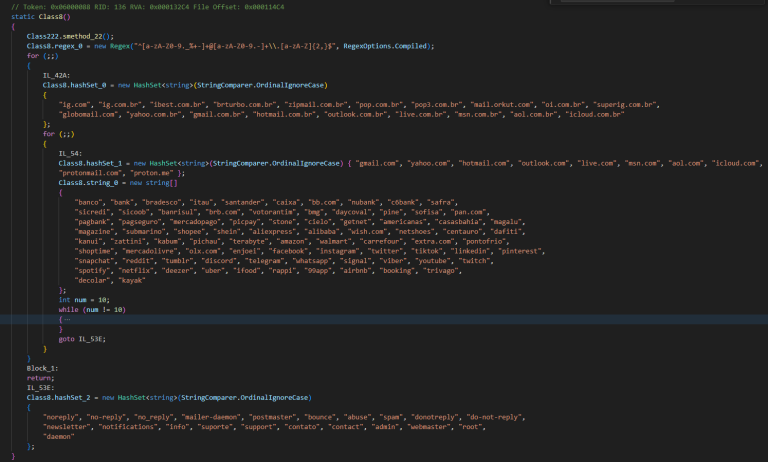
Self-Spreading TCLBANKER Trojan Hijacks WhatsApp to Drain Accounts TCLBANKER Trojan REF3076 Malware
  • Malware

Self-Spreading TCLBANKER Trojan Hijacks WhatsApp to Drain Accounts

Do Son May 8, 2026 0

Elastic Security Labs exposes TCLBANKER, an advanced banking trojan that hijacks WhatsApp to spread while blinding defenders with invisible WPF overlays.

North Korean “Laptop Farms” Infiltrated 70 U.S. Companies North Korean Laptop Farm DPRK Insider Threat North Korea WMD Cyber Funding, Australia Sanctions Insider threat, North Korean hackers Kimsuky, cyber-espionage NPM Malware, North Korea Cyber-espionage North Korea, Remote IT Job Scam Laptop Farm - DriverEasy - Kimsuky Watering Hole Attack
  • Cybercriminals

North Korean “Laptop Farms” Infiltrated 70 U.S. Companies

Do Son May 8, 2026 0

DOJ sentences U.S. enablers for running North Korean "laptop farms." Learn how the DPRK breached 70 companies and funded weapons via stolen identities.
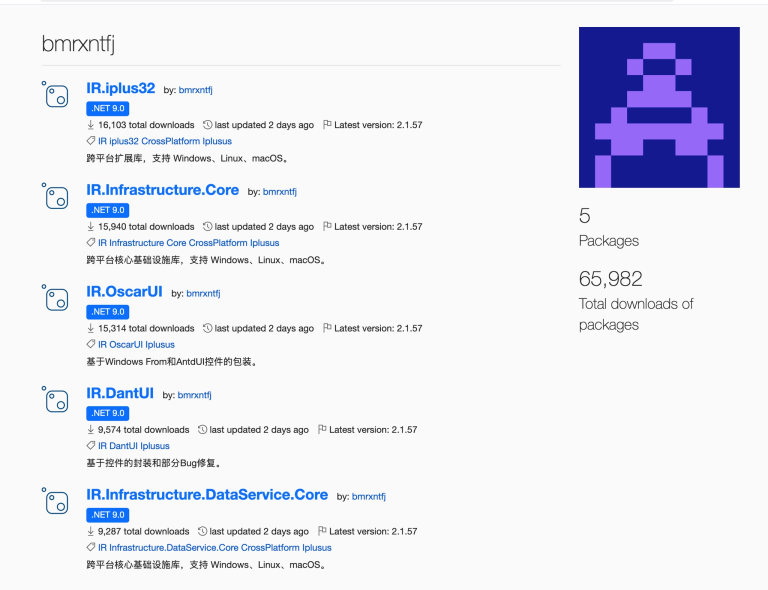
Highly Evasive NuGet Supply Chain Attack Hijacks 65,000 .NET Build Servers NuGet Supply Chain Attack .NET Malware
  • Malware

Highly Evasive NuGet Supply Chain Attack Hijacks 65,000 .NET Build Servers

Do Son May 8, 2026 0

Critical alert: A stealth NuGet supply chain attack has hijacked 65,000 .NET workstations. Audit your CI/CD for malicious IR.* packages immediately.

The 4GB Secret: Why Chrome is Surreptitiously Downloading AI Models to Your Hard Drive Chrome hidden weights.bin download Gemini Nano privacy controversy 2026 Google Antigravity account suspension Gemini Lyria 3 integration Google Gemini enterprise sales, Google Cloud AI revenue 2026 Google Gemini daily limits 2026, Gemini Thinking model quotas Google Gemini 3 Agentic Development Platform
  • Data Leak

The 4GB Secret: Why Chrome is Surreptitiously Downloading AI Models to Your Hard Drive

Do Son May 8, 2026 0

Google Chrome is under fire for surreptitiously downloading a 4GB "weights.bin" file to run Gemini Nano. Discover the GDPR and environmental risks involved.

Cloudflare Cuts 20% of Staff to Pivot Toward an “AI-First Agentic” Future Cloudflare layoffs 2026 AI bot traffic surge Content Signals Policy, AI Content Usage Cloudflare, Certificate Misissuance Salesforce, supply chain attack DDoS attack, Cloudflare Perplexity AI, Web Scraping Pay Per Crawl Cloudflare abuse R2 outage HTTP Cloudflare Blocking
  • Technology

Cloudflare Cuts 20% of Staff to Pivot Toward an “AI-First Agentic” Future

Do Son May 8, 2026 0

Cloudflare cuts 1,100+ jobs despite beating Q1 earnings. CEO Matthew Prince cites a 600% surge in AI agent use as the catalyst for this "AI-first" metamorphosis.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2019-25779CVSS 8.7
    WooThemes Diarise through 1.5.9 contains a file read vulnerability that allows unauthenticated attackers to read arbitrary files through...
    Watchtower Verified📅 Updated: Nov 4, 2026
  • CVE-2023-54413CVSS 5.1
    WPML Multilingual CMS plugin for WordPress before 4.6.1 contains a reflected cross-site scripting vulnerability that allows unauthenticated attackers...
    Watchtower Verified📅 Updated: Nov 4, 2026
  • CVE-2026-81648CVSS 10.0
    The CryptoPayment Gateway WordPress plugin from 1.2.1 to 1.2.2 does not apply an authorization check on one of...
    Admin intel📅 Updated: Nov 3, 2026
  • CVE-2026-58115CVSS 10.0
    A vulnerability has been identified in SIMATIC IoT2050 Advanced (6ES7647-0BA00-1YA2) (All versions < V4.3.4.1 running Industrial OS with...
    Admin intel📅 Updated: Nov 2, 2026
  • CVE-2026-20051CVSS 7.4
    A vulnerability with the Ethernet VPN (EVPN) Layer 2 ingress packet processing of Cisco Nexus 3600 Platform Switches...
    Watchtower Verified📅 Updated: Nov 1, 2026
  • CVE-2026-20118CVSS 6.8
    A vulnerability in the handling of an Egress Packet Network Interface (EPNI) Aligner interrupt in Cisco IOS XR...
    Watchtower Verified📅 Updated: Nov 1, 2026
  • CVE-2010-20125CVSS 8.7
    DedeCMS before 5.7 contains a file inclusion vulnerability in plus/carbuyaction.php that allows remote unauthenticated attackers to control the...
    Watchtower Verified📅 Updated: Oct 30, 2026
  • CVE-2026-111357CVSS 7.0
    Ivanti Connect Secure 22.8R2.4 mishandles the manner in which the dsinvoked broker trusts DSCache configuration data, leading to...
    CISA KEV📅 Added to KEV: Oct 30, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-44267CVSS 9.8
    Elo is a purely functional expression language for no-code tools. Prior to 1.0.1, plain Elo strings supplied to...
    📅 Updated: Nov 3, 2026
  • CVE-2026-44266CVSS 9.8
    Elo is a purely functional expression language for no-code tools. Prior to 1.0.1, the Ruby backend in src/compilers/ruby.ts...
    📅 Updated: Nov 3, 2026
  • CVE-2026-28336CVSS 9.9
    SolarWinds Dameware was found to be affected by a command injection vulnerability that could lead to the compromise...
    📅 Updated: Nov 3, 2026
  • CVE-2026-91495CVSS 9.8
    Vulnerability in the Oracle WebCenter Content product of Oracle Fusion Middleware (component: Content Server). Supported versions that are...
    📅 Updated: Nov 3, 2026
  • CVE-2026-64523CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: net/handshake: Take a long-lived file reference at submit...
    📅 Updated: Nov 3, 2026
  • CVE-2026-64459CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: tcp: restore RCU grace period in tcp_ao_destroy_sock Commit...
    📅 Updated: Nov 3, 2026
  • CVE-2026-64530CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: net/sched: cls_api: Handle TC_ACT_CONSUMED in tcf_qevent_handle tcf_classify() can...
    📅 Updated: Nov 3, 2026
  • CVE-2026-64534CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: nvmet-tcp: check INIT_FAILED before nvmet_req_uninit in digest error...
    📅 Updated: Nov 3, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.