Skip to content
November 3, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
The End of Whiteboard Coding: Google to Allow Gemini AI in Software Engineering Interviews Google Gemini Go app Google AI software engineering interview Google Gemini for Mac
  • Technology

The End of Whiteboard Coding: Google to Allow Gemini AI in Software Engineering Interviews

Do Son May 8, 2026 0

Google's new recruitment pilot allows candidates to use Gemini AI. Learn why "AI fluency" and code curation are replacing rote memorization in 2026.
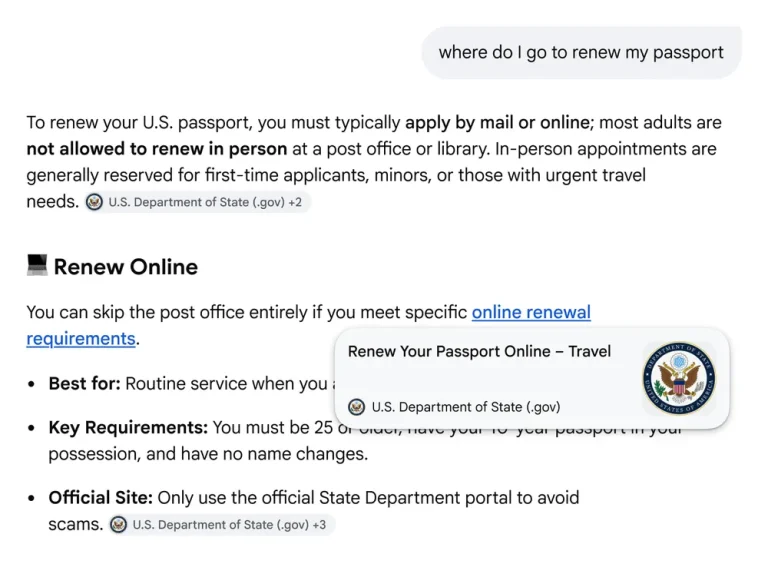
Reddit in the Spotlight: Google’s Search Pivot Puts “First-Hand Accounts” at the Core of AI Overviews Google AI Overviews Reddit integration
  • Technology

Reddit in the Spotlight: Google’s Search Pivot Puts “First-Hand Accounts” at the Core of AI Overviews

Do Son May 8, 2026 0

Google’s AI Overviews shift focus to first-hand accounts from Reddit and social media. Discover how "Expert Advice" and inline linking aim to reclaim user trust.
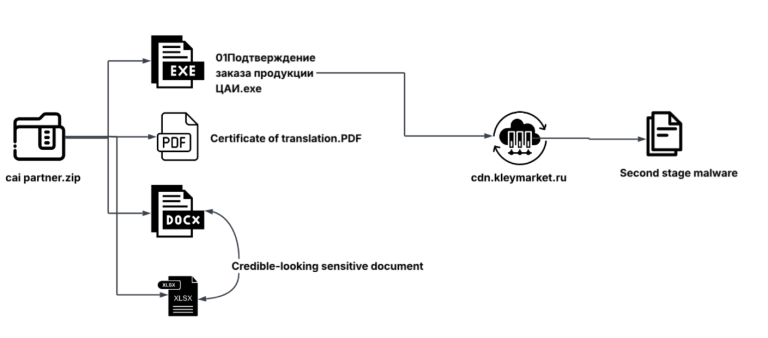
Silent Rotor: Targeted Rust Malware Infiltrates the 2026 Eurasian Unmanned Aviation Forum Operation Silent Rotor Rust Malware
  • Cybercriminals

Silent Rotor: Targeted Rust Malware Infiltrates the 2026 Eurasian Unmanned Aviation Forum

Do Son May 8, 2026 0

SEQRITE Labs uncovers Operation Silent Rotor, a targeted Rust-based cyberattack on the Eurasian unmanned aviation sector ahead of the 2026 Moscow forum.

Is Your React App Vulnerable to the CVE-2026-23870 DoS Attack? React Server Components Vulnerability CVE-2026-23870 React Server Components Server-Side DoS React DoS Vulnerability CVE-2026-23864 React Server Components DoS, Source Code Disclosure React RCE, Server Components Deserialization CVE-2025-55182
  • Vulnerability Report

Is Your React App Vulnerable to the CVE-2026-23870 DoS Attack?

Do Son May 8, 2026 0

Protect your app from CVE-2026-23870. Learn how this high-severity React Server Components DoS flaw crashes servers and how to patch your React 19 build today.
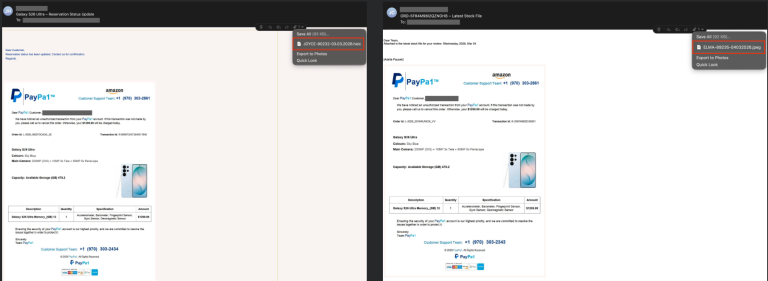
The TOAD Trap: Why Scammers are Trading Malicious Links for VoIP Phone Numbers TOAD Attacks Telephone-Oriented Attack Delivery
  • Cybercriminals

The TOAD Trap: Why Scammers are Trading Malicious Links for VoIP Phone Numbers

Do Son May 8, 2026 0

Cisco Talos reveals the rise of TOAD attacks. 55% of scam campaigns now use VoIP "anchors" to bypass email filters and trick victims into calling fraud centers.
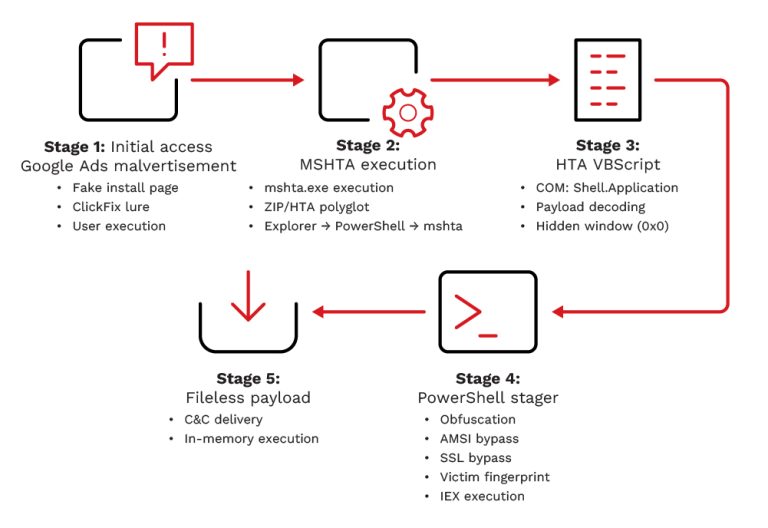
The InstallFix Trap: Fake Claude AI Google Ads Drop Fileless RedLine Malware on Developers InstallFix Malware Claude AI Phishing
  • Malware

The InstallFix Trap: Fake Claude AI Google Ads Drop Fileless RedLine Malware on Developers

Do Son May 8, 2026 0

Beware of InstallFix: Fake Claude AI Google Ads trick users into running fileless scripts that deploy RedLine Stealer to steal passwords and crypto.
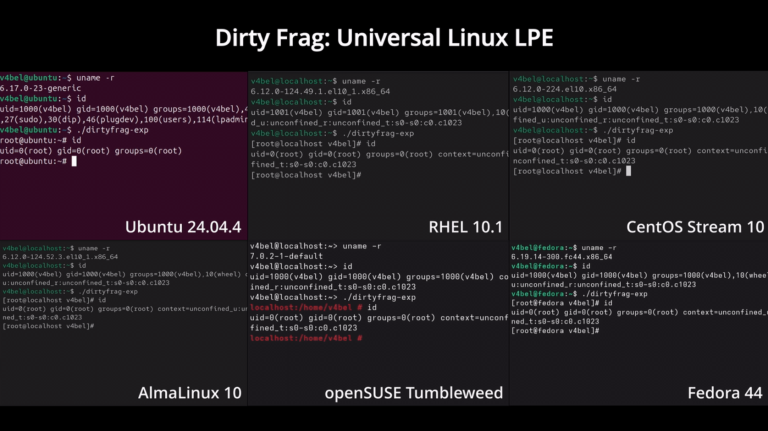
Embargo Broken: Public PoC Released for “Dirty Frag” Linux Kernel Exploit Granting Instant Root Access Dirty Frag Linux PoC v4bel Dirty Frag Exploit
  • Linux
  • Vulnerability Report

Embargo Broken: Public PoC Released for “Dirty Frag” Linux Kernel Exploit Granting Instant Root Access

Do Son May 8, 2026 0

Dirty Frag PoC released! Researcher v4bel discloses a universal Linux root exploit targeting the page cache. No patches yet—apply module mitigations now!

Critical 9.9 CVSS Rancher Fleet Flaw Grants Full Cluster-Admin Access Fleet security vulnerabilities cross namespace secret disclosure Rancher, GitOps Rancher Fleet Critical Vulnerability CVE-2026-41050
  • Vulnerability Report

Critical 9.9 CVSS Rancher Fleet Flaw Grants Full Cluster-Admin Access

Do Son May 8, 2026 0

Rancher Fleet fixes a 9.9 CVSS flaw (CVE-2026-41050) allowing tenants to bypass ServiceAccount isolation and steal secrets. Upgrade your GitOps engine now!

Zabbix Flaws Allow Monitored Hosts to Hijack Admin Dashboards Zabbix XSS Vulnerabilities CVE-2026-23926 zabbix - CVE-2024-22116 Zabbix SQL Injection CVE-2026-23921
  • Vulnerability Report

Zabbix Flaws Allow Monitored Hosts to Hijack Admin Dashboards

Do Son May 8, 2026 0

Zabbix fixes high-severity XSS (CVE-2026-23926) and Oracle injection flaws. Don't let your monitoring tool become a backdoor—upgrade your Zabbix server now!

Under Active Attack: Ivanti EPMM Zero-Day Exploited in the Wild via Harvested Admin Credentials Ivanti EPMM Zero-Day CVE-2026-6973 Exploitation CVE-2024-9379, CVE-2024-9380, CVE-2024-9381
  • Vulnerability Report

Under Active Attack: Ivanti EPMM Zero-Day Exploited in the Wild via Harvested Admin Credentials

Do Son May 7, 2026 0

Ivanti confirms active exploitation of EPMM (CVE-2026-6973). Attackers are using old credentials to hijack mobile management. Patch to v12.8.0.1 immediately!
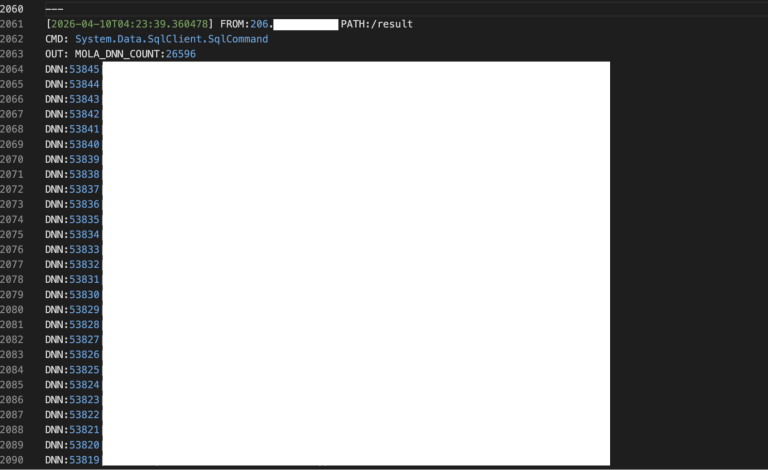
Omani Government Targeted in Blatant Iranian-Nexus Cyberespionage Oman Government Cyberattack Hunt Intelligence APT Report
  • Cyber Security
  • Data Leak

Omani Government Targeted in Blatant Iranian-Nexus Cyberespionage

Do Son May 7, 2026 0

Hunt Intelligence uncovers a massive Iranian-nexus breach targeting the Omani Ministry of Justice. 26k records leaked via an unprotected UAE staging server.
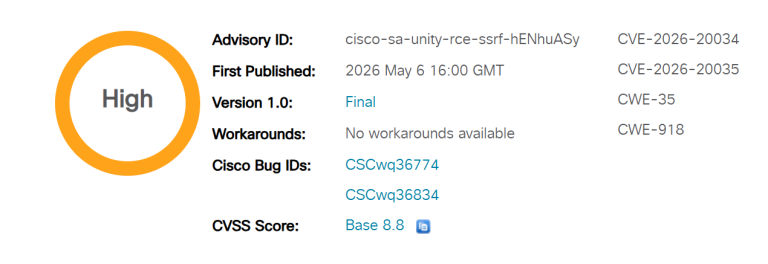
Cisco Unity Connection Flaws Enable Full System Takeover Cisco Unity Connection RCE CVE-2026-20034
  • Vulnerability Report

Cisco Unity Connection Flaws Enable Full System Takeover

Do Son May 7, 2026 0

Cisco warns of critical RCE (CVE-2026-20034) and SSRF flaws in Unity Connection. Authenticated root access and unauthenticated network probing are possible. Patch now!
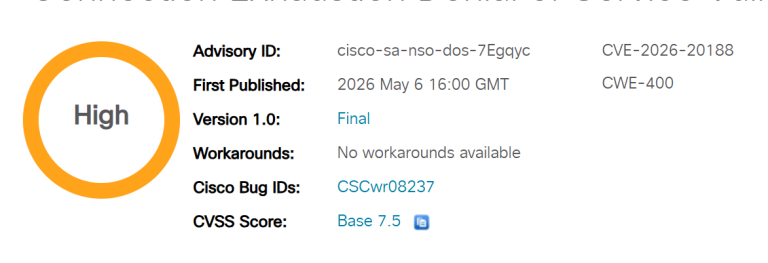
Cisco CNC and NSO Flaw Allows Remote Attackers to Lock Down Network Management Cisco NSO Denial of Service CVE-2026-20188
  • Vulnerability Report

Cisco CNC and NSO Flaw Allows Remote Attackers to Lock Down Network Management

Do Son May 7, 2026 0

Cisco warns of a critical DoS flaw (CVE-2026-20188) in CNC and NSO. Unauthenticated attackers can freeze network management. Patch to CNC 7.2 or NSO 6.4.1.3 now!

OceanLotus Hijacks PyPI to Deploy “ZiChatBot” via Enterprise Chat APIs Acreed Infostealer, BNB Smart Chain CVE-2023-20269 exploit
  • Cyber Security
  • Malware

OceanLotus Hijacks PyPI to Deploy “ZiChatBot” via Enterprise Chat APIs

Do Son May 7, 2026 0

OceanLotus targets Python developers worldwide via PyPI supply chain attacks. New ZiChatBot malware hijacks Zulip APIs for invisible C2 traffic. Patch now!

Orbital Ambitions: Anthropic Taps Musk’s “Colossus” to Double Claude’s Power and Eye the Stars Anthropic SpaceX partnership SpaceX IPO 1.75 trillion 2026 Tech IPO wave, SpaceX OpenAI Anthropic valuation SpaceX IPO 2026, $800 Billion Valuation SpaceX $1.5 Trillion IPO, Starship Starlink
  • Technology

Orbital Ambitions: Anthropic Taps Musk’s “Colossus” to Double Claude’s Power and Eye the Stars

Do Son May 7, 2026 0

Anthropic partners with SpaceX to use the Colossus 1 supercomputer. Discover how this massive compute boost is doubling Claude Code limits and targeting space.
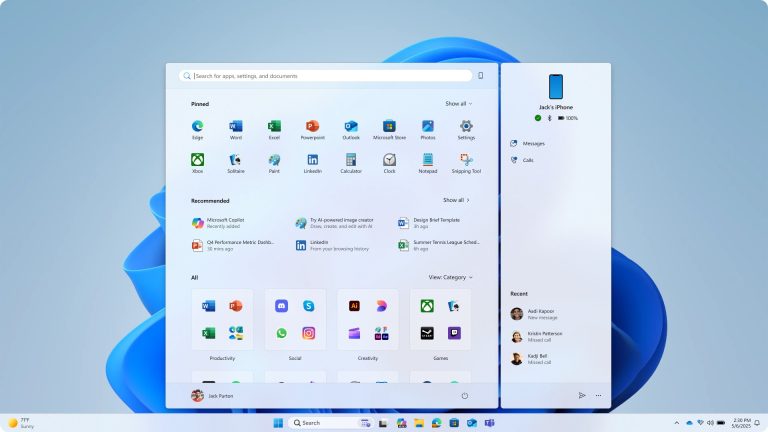
The 1.6 Billion User Pivot: Satya Nadella’s Plan to Fix Windows 11 and Save the 8GB PC Windows 11 CPU optimization Microsoft Windows user engagement
  • Windows

The 1.6 Billion User Pivot: Satya Nadella’s Plan to Fix Windows 11 and Save the 8GB PC

Do Son May 7, 2026 0

Microsoft CEO Satya Nadella reveals a pivot to optimize Windows 11 for low-memory devices and reclaim user trust as active Windows users hit 1.6 billion.
Attackers Hijack Trusted RMM Tools to Create Invisible, Permanent Backdoors RMM Hijacking Campaign Self-Healing Persistence
  • Cybercriminals

Attackers Hijack Trusted RMM Tools to Create Invisible, Permanent Backdoors

Do Son May 7, 2026 0

Securonix exposes an 80+ organization breach using "self-healing" RMM tools and Safe Mode persistence. Standard antivirus is blind—learn how to hunt it!
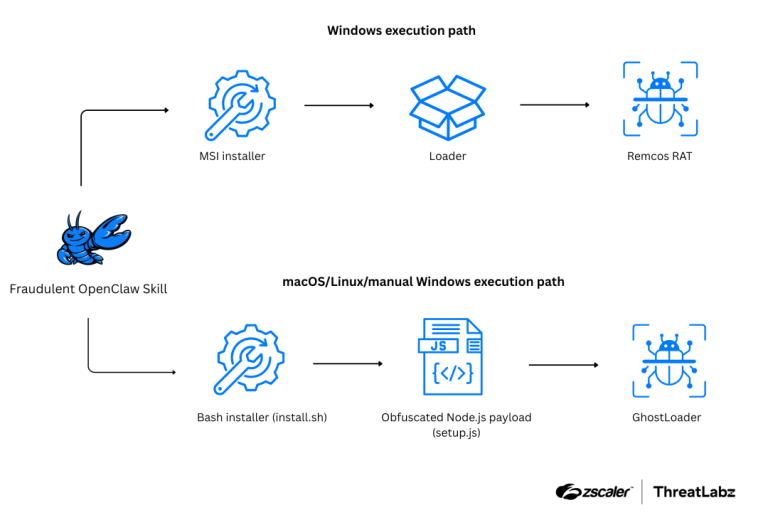
Deceptive “DeepSeek-Claw” Skill Hijacks OpenClaw Agents to Steal Credentials OpenClaw Framework Malware DeepSeek-Claw AI Skill
  • Malware

Deceptive “DeepSeek-Claw” Skill Hijacks OpenClaw Agents to Steal Credentials

Do Son May 7, 2026 0

Zscaler ThreatLabz exposes DeepSeek-Claw, a malicious AI skill targeting the OpenClaw framework to deploy GhostLoader and Remcos RAT. Secure your agents now!

New “Pheno” Malware Hijacks Microsoft Phone Link to Steal SMS and OTPs NATS-as-C2 Sysdig CVE-2026-33017 Langflow RCE Microsoft Phone Link Hijack CloudZ Pheno Plugin Insider Threat BlackCat (ALPHV) OFAC Sanctions DPRK IT Workers Transparent Tribe APT36 React2Shell, EtherRAT SideWinder Espionage, Netlify Phishing DDNS Abuse, C2 Infrastructure Hacking Health Club
  • Malware

New “Pheno” Malware Hijacks Microsoft Phone Link to Steal SMS and OTPs

Do Son May 7, 2026 0

Cisco Talos exposes Pheno, a malware plugin that hijacks Microsoft Phone Link to steal SMS and 2FA codes without touching your phone. Secure your PC today!
The impact of Colocation as a Service on the way businesses manage IT infrastructure CVE-2025-20059
  • Technique

The impact of Colocation as a Service on the way businesses manage IT infrastructure

Do Son May 7, 2026 0
Once upon a time, IT infrastructure management was all about one of two things. Back then, you...
Read More Read more about The impact of Colocation as a Service on the way businesses manage IT infrastructure
High-Severity WatchGuard Agent Flaws Grant Full SYSTEM Privileges on Windows WatchGuard Agent Privilege Escalation CVE-2026-6787 WatchGuard Vulnerability CVE-2026-1498 WatchGuard Firebox VPN Flaws, Command Injection WatchGuard Vulnerability CVE-2024-6592 and CVE-2024-6593
  • Vulnerability Report

High-Severity WatchGuard Agent Flaws Grant Full SYSTEM Privileges on Windows

Do Son May 7, 2026 0

WatchGuard Agent v1.25.03.0000 fixes critical privilege escalation flaws (CVE-2026-6787) and buffer overflows. Secure your Windows endpoints and patch now!

Critical 9.0 CVSS Flaw in ArcadeDB Allows Total Cross-Database Access ArcadeDB Authorization Bypass CVE-2026-44221
  • Vulnerability Report

Critical 9.0 CVSS Flaw in ArcadeDB Allows Total Cross-Database Access

Do Son May 7, 2026 0

ArcadeDB 26.4.1 fixes a critical 9.0 CVSS authorization bypass (CVE-2026-44221) that dismantles database isolation. Secure your multi-model data and patch now!

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-81648CVSS 10.0
    The CryptoPayment Gateway WordPress plugin from 1.2.1 to 1.2.2 does not apply an authorization check on one of...
    Admin intel📅 Updated: Nov 3, 2026
  • CVE-2026-58115CVSS 10.0
    A vulnerability has been identified in SIMATIC IoT2050 Advanced (6ES7647-0BA00-1YA2) (All versions < V4.3.4.1 running Industrial OS with...
    Admin intel📅 Updated: Nov 2, 2026
  • CVE-2026-20051CVSS 7.4
    A vulnerability with the Ethernet VPN (EVPN) Layer 2 ingress packet processing of Cisco Nexus 3600 Platform Switches...
    Watchtower Verified📅 Updated: Nov 1, 2026
  • CVE-2026-20118CVSS 6.8
    A vulnerability in the handling of an Egress Packet Network Interface (EPNI) Aligner interrupt in Cisco IOS XR...
    Watchtower Verified📅 Updated: Nov 1, 2026
  • CVE-2010-20125CVSS 8.7
    DedeCMS before 5.7 contains a file inclusion vulnerability in plus/carbuyaction.php that allows remote unauthenticated attackers to control the...
    Watchtower Verified📅 Updated: Oct 30, 2026
  • CVE-2015-20130CVSS 5.1
    Netsweeper before 4.0.11 and 4.1.0 before 4.1.5 contains a reflected cross-site scripting vulnerability in webadmin/reporter/view_server_log.php that allows remote...
    Watchtower Verified📅 Updated: Oct 30, 2026
  • CVE-2026-111357CVSS 7.0
    Ivanti Connect Secure 22.8R2.4 mishandles the manner in which the dsinvoked broker trusts DSCache configuration data, leading to...
    CISA KEV📅 Added to KEV: Oct 30, 2026
  • CVE-2026-118527CVSS 4.3
    Use of predictable filenames in Ivanti Connect Secure before versions 25.1.1.3 and 22.8R2.6 allows a remote authenticated attacker...
    CISA KEV📅 Added to KEV: Oct 30, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-44267CVSS 9.8
    Elo is a purely functional expression language for no-code tools. Prior to 1.0.1, plain Elo strings supplied to...
    📅 Updated: Nov 3, 2026
  • CVE-2026-44266CVSS 9.8
    Elo is a purely functional expression language for no-code tools. Prior to 1.0.1, the Ruby backend in src/compilers/ruby.ts...
    📅 Updated: Nov 3, 2026
  • CVE-2026-28336CVSS 9.9
    SolarWinds Dameware was found to be affected by a command injection vulnerability that could lead to the compromise...
    📅 Updated: Nov 3, 2026
  • CVE-2026-91495CVSS 9.8
    Vulnerability in the Oracle WebCenter Content product of Oracle Fusion Middleware (component: Content Server). Supported versions that are...
    📅 Updated: Nov 3, 2026
  • CVE-2026-64523CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: net/handshake: Take a long-lived file reference at submit...
    📅 Updated: Nov 3, 2026
  • CVE-2026-64459CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: tcp: restore RCU grace period in tcp_ao_destroy_sock Commit...
    📅 Updated: Nov 3, 2026
  • CVE-2026-64530CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: net/sched: cls_api: Handle TC_ACT_CONSUMED in tcf_qevent_handle tcf_classify() can...
    📅 Updated: Nov 3, 2026
  • CVE-2026-64534CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: nvmet-tcp: check INIT_FAILED before nvmet_req_uninit in digest error...
    📅 Updated: Nov 3, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.