Skip to content
November 4, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
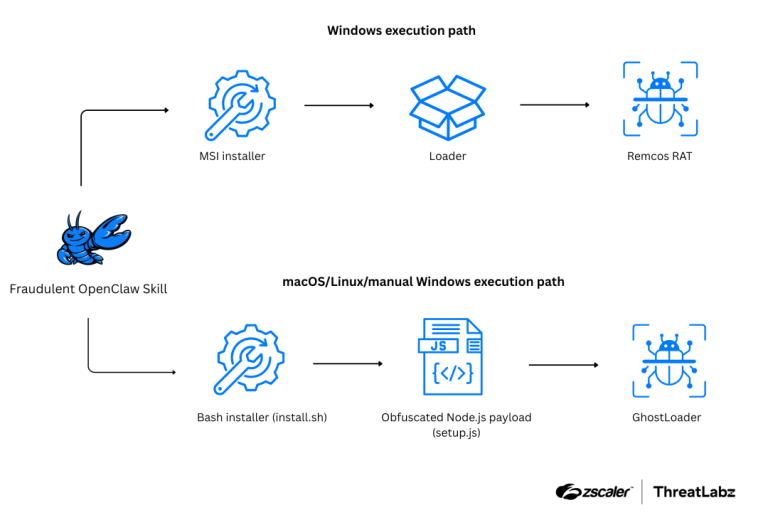
Deceptive “DeepSeek-Claw” Skill Hijacks OpenClaw Agents to Steal Credentials OpenClaw Framework Malware DeepSeek-Claw AI Skill
  • Malware

Deceptive “DeepSeek-Claw” Skill Hijacks OpenClaw Agents to Steal Credentials

Do Son May 7, 2026 0

Zscaler ThreatLabz exposes DeepSeek-Claw, a malicious AI skill targeting the OpenClaw framework to deploy GhostLoader and Remcos RAT. Secure your agents now!

New “Pheno” Malware Hijacks Microsoft Phone Link to Steal SMS and OTPs NATS-as-C2 Sysdig CVE-2026-33017 Langflow RCE Microsoft Phone Link Hijack CloudZ Pheno Plugin Insider Threat BlackCat (ALPHV) OFAC Sanctions DPRK IT Workers Transparent Tribe APT36 React2Shell, EtherRAT SideWinder Espionage, Netlify Phishing DDNS Abuse, C2 Infrastructure Hacking Health Club
  • Malware

New “Pheno” Malware Hijacks Microsoft Phone Link to Steal SMS and OTPs

Do Son May 7, 2026 0

Cisco Talos exposes Pheno, a malware plugin that hijacks Microsoft Phone Link to steal SMS and 2FA codes without touching your phone. Secure your PC today!
The impact of Colocation as a Service on the way businesses manage IT infrastructure CVE-2025-20059
  • Technique

The impact of Colocation as a Service on the way businesses manage IT infrastructure

Do Son May 7, 2026 0
Once upon a time, IT infrastructure management was all about one of two things. Back then, you...
Read More Read more about The impact of Colocation as a Service on the way businesses manage IT infrastructure
High-Severity WatchGuard Agent Flaws Grant Full SYSTEM Privileges on Windows WatchGuard Agent Privilege Escalation CVE-2026-6787 WatchGuard Vulnerability CVE-2026-1498 WatchGuard Firebox VPN Flaws, Command Injection WatchGuard Vulnerability CVE-2024-6592 and CVE-2024-6593
  • Vulnerability Report

High-Severity WatchGuard Agent Flaws Grant Full SYSTEM Privileges on Windows

Do Son May 7, 2026 0

WatchGuard Agent v1.25.03.0000 fixes critical privilege escalation flaws (CVE-2026-6787) and buffer overflows. Secure your Windows endpoints and patch now!

Critical 9.0 CVSS Flaw in ArcadeDB Allows Total Cross-Database Access ArcadeDB Authorization Bypass CVE-2026-44221
  • Vulnerability Report

Critical 9.0 CVSS Flaw in ArcadeDB Allows Total Cross-Database Access

Do Son May 7, 2026 0

ArcadeDB 26.4.1 fixes a critical 9.0 CVSS authorization bypass (CVE-2026-44221) that dismantles database isolation. Secure your multi-model data and patch now!
Critical Spring Cloud Config Flaws Expose Arbitrary Files and GCP Secrets Spring Cloud Config Vulnerability CVE-2026-40982 Spring Boot Vulnerability CVSS 9.1 Bypass CVE-2022-31692 Spring Boot Vulnerability Authentication Bypass
  • Vulnerability Report

Critical Spring Cloud Config Flaws Expose Arbitrary Files and GCP Secrets

Do Son May 7, 2026 0

Spring Cloud Config fixes a 9.1 CVSS directory traversal (CVE-2026-40982) and a GCP secret leak. Secure your distributed system—upgrade to the latest patches!

Bitcoin Core Fixes High-Severity Remote Crash Vulnerability Bitcoin Core Node Crash CVE-2024-52911 CVE-2024-35202 - Bitcoin Core
  • Vulnerability Report

Bitcoin Core Fixes High-Severity Remote Crash Vulnerability

Do Son May 7, 2026 0

Bitcoin Core v29.0 fixes a high-severity use-after-free bug (CVE-2024-52911) that could allow attackers to remotely crash nodes. Upgrade your node today.

State-Sponsored Actors Weaponize Critical PAN-OS Zero-Day for Root PAN-OS Root RCE CL-STA-1132 Exploitation Tianxin RCE CVE-2021-4473 React Native Supply Chain Attack AstrOOnauta Malware Gladinet Zero-Day, LFI RCE Chain WordPress Theme, Account Takeover CVE-2024-50623 - European Space Agency cyberattack
  • Vulnerability Report

State-Sponsored Actors Weaponize Critical PAN-OS Zero-Day for Root

Do Son May 7, 2026 0

Palo Alto Networks warns of active root RCE (CVE-2026-0300) in PAN-OS. State-sponsored cluster CL-STA-1132 is targeting edge assets. Patch and restrict now!

Chrome’s Security Overhaul: 127 Fixes and $100k+ in Bounties Power the New Chrome 148 Stable Release Chrome 148 Security Update CVE-2026-7896
  • Vulnerability Report

Chrome’s Security Overhaul: 127 Fixes and $100k+ in Bounties Power the New Chrome 148 Stable Release

Do Son May 7, 2026 0

Google Chrome 148 is out with 127 security fixes, including 3 Critical flaws in Blink and V8. Protect your data—check your version and update today!

Critical Redis Patches Fix RCE and Memory Corruption Flaws Redis RCE Vulnerabilities CVE-2026-25243 CVE-2024-31449 - Redis
  • Vulnerability Report

Critical Redis Patches Fix RCE and Memory Corruption Flaws

Do Son May 7, 2026 0

Redis releases critical patches for 5 vulnerabilities, including RCE via the RESTORE command (CVSS 7.7). Secure your self-managed Redis instances immediately!
Triple Critical Threat: Apache Wicket Patch Fixes Path Traversal, Session Hijacking, and Resource Bypass CVE-2024-36522 Apache Wicket Critical Vulnerabilities CVE-2026-43975
  • Vulnerability Report

Triple Critical Threat: Apache Wicket Patch Fixes Path Traversal, Session Hijacking, and Resource Bypass

Do Son May 7, 2026 0

Apache Wicket 10.9.0 fixes 3 Critical flaws: Path Traversal (CVE-2026-43975), Session Fixation, and Resource Guard bypass. Secure your Java apps and patch now!
Critical OpenMRS Flaws Enable Patient Data Theft and Remote Server Takeover OpenMRS RCE Vulnerability CVE-2026-41258
  • Vulnerability Report

Critical OpenMRS Flaws Enable Patient Data Theft and Remote Server Takeover

Do Son May 6, 2026 0

OpenMRS v2.8.6 fixes a critical 9.1 CVSS SSTI flaw and Zip Slip RCE. Protect global patient health records and upgrade your EMR infrastructure immediately!
Critical 9.0 CVSS Flaw in Thymeleaf Enables Remote Server Injection Thymeleaf SSTI Bypass CVE-2026-41901 Thymeleaf SSTI CVE-2026-40477
  • Vulnerability Report

Critical 9.0 CVSS Flaw in Thymeleaf Enables Remote Server Injection

Do Son May 6, 2026 0

Critical 9.0 CVSS flaw in Thymeleaf (CVE-2026-41901) allows SSTI and arbitrary code execution. Secure your Java web apps—upgrade to v3.1.5.RELEASE now!
Iran and Hezbollah Are Relocating Terror Networks Across Latin America IRGC Latin America Operations Hezbollah Relocation Venezuela
  • Cyber Security

Iran and Hezbollah Are Relocating Terror Networks Across Latin America

Do Son May 6, 2026 0

Resecurity reveals that IRGC and Hezbollah are shifting operations to Colombia and Ecuador after the Maduro arrest. Learn how cultural centers fuel terror.

The $200 Billion Tether: Anthropic’s Massive Google Deal Exposes the “Circular Economy” of Silicon Valley AI Anthropic confidential IPO filing Anthropic Google $200 billion deal Anthropic Mythos Preview Anthropic Pentagon blacklist Claude Max 20x open-source Model Distillation Anthropic vs DeepSeek Claude Free tier update 2026
  • Technology

The $200 Billion Tether: Anthropic’s Massive Google Deal Exposes the “Circular Economy” of Silicon Valley AI

Do Son May 6, 2026 0

Anthropic commits $200B to Google Cloud as the "Big Four" reach a $2T revenue backlog. Discover how AI startups are tethered to their own investors.
Apple to Shatter the Walled Garden with iOS 27 “AI Extensions” and Third-Party Model Swapping Apple Intelligence philosophy, Craig Federighi interview, Apple AI privacy, Siri AI companion iOS 27 AI Extensions
  • Technology

Apple to Shatter the Walled Garden with iOS 27 “AI Extensions” and Third-Party Model Swapping

Do Son May 6, 2026 0

Apple pivots to an "AI Marketplace" in iOS 27. New Extensions let users swap Apple Intelligence for GPT, Claude, and more to power Siri and Writing Tools.

The AI Inflection Point: Android 17, Gemini 4, and the Shocking Debut of “Aluminium OS” at Google I/O 2026 Android 17 rate limiting PIN lockout screen Google I/O 2026 highlights
  • Android

The AI Inflection Point: Android 17, Gemini 4, and the Shocking Debut of “Aluminium OS” at Google I/O 2026

Do Son May 6, 2026 0

Google I/O 2026 is here! From the Android 17 "Cinnamon Bun" reveal to the new Aluminium OS and Gemini 4, see how Google is redefining the future of computing.

New Quasar Linux (QLNX) RAT Hijacks Cloud Keys and NPM Tokens Quasar Linux RAT Supply Chain Hijacking
  • Malware

New Quasar Linux (QLNX) RAT Hijacks Cloud Keys and NPM Tokens

Do Son May 6, 2026 0

Trend Micro uncovers QLNX, a fileless Linux RAT targeting AWS, NPM, and Kubernetes keys. Learn how its eBPF rootkit hides from even the deepest system scans.

The Altman Realignment: Why OpenAI is Considering a “Google-Style” Split to Save Its IPO OpenAI token price reduction OpenAI Deployment Company DeployCo OpenAI IPO strategy OpenAI Privacy Filter 1.5B OpenAI $122 billion funding OpenAI GitHub alternative OpenAI military agreement 2026 OpenAI Stargate project collapse NVIDIA OpenAI investment stall ChatGPT Go $8 subscription, OpenAI GPT-5.2 Instant ads OpenAI Torch acquisition, Unified Medical Memory OpenAI Head of Preparedness 2025, Sam Altman AI safety lawsuits ChatGPT Advertising Speculation OpenAI Ad Code Denial OpenAI AI Confession Hallucination Mitigation ChatGPT Quality Focus OpenAI Gemini Red Alert ChatGPT Login, AI ecosystem OpenAI Mental Health, AI Well-Being Council ChatGPT Instant Checkout, Agentic Commerce OpenAI cloud computing OpenAI, startup incubator OpenAI chips, NVIDIA competition AI competition, antitrust lawsuit GPT-5, OpenAI Livestream OpenAI Open-Weight, AI Models OpenAI Infrastructure, AI Data Centers ChatGPT Business, Office Productivity OpenAI Open-Weight Model, WindSurf Acquisition OpenAI AI Browser, ChatGPT Integration Mattel AI, OpenAI Partnership OpenAI o3, Price Cut OpenAI's Next-Gen AI: O3-Pro's Enhanced Reasoning PowerOpenAI profit OpenAI Bid OpenAI Social Network ChatGPT Social OpenAI Non-profit OpenAI UAE ChatGPT Plus free
  • Technology

The Altman Realignment: Why OpenAI is Considering a “Google-Style” Split to Save Its IPO

Do Son May 6, 2026 0

OpenAI faces a $6.5B dilemma. Discover why Sam Altman may spin off robotics and hardware to protect OpenAI’s core profits ahead of its high-stakes IPO.

White House Considers Mandatory Federal Vetting for All New AI Models AI pre-release vetting AI copyright law US UK FoundationMotion, AI Motion Understanding AI Deregulation, DOGE AI Self-Preservation, GPT-4o Country of Geniuses
  • Technology

White House Considers Mandatory Federal Vetting for All New AI Models

Do Son May 6, 2026 0

The era of non-interference is over. The White House may soon mandate federal security reviews for all AI models before they can launch to the public.

The Day Germany Disappeared: How a Single Cryptographic Error Paralyzed the .de Namespace .de domain outage DNSSEC
  • Technology

The Day Germany Disappeared: How a Single Cryptographic Error Paralyzed the .de Namespace

Do Son May 6, 2026 0

A massive configuration error at DENIC paralyzed millions of .de domains. Discover how a routine DNSSEC key rotation caused a nationwide internet blackout.

Skeletal Scans and Height Checks: Meta Deploys Radical “Visual Analysis” AI to Purge Underage Users Meta AI visual age analysis
  • Technology

Skeletal Scans and Height Checks: Meta Deploys Radical “Visual Analysis” AI to Purge Underage Users

Do Son May 6, 2026 0

Meta is scanning user height and skeletal structure to find kids under 13. See how this "Visual Analysis" AI works to purge underage accounts on Instagram.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2019-25779CVSS 8.7
    WooThemes Diarise through 1.5.9 contains a file read vulnerability that allows unauthenticated attackers to read arbitrary files through...
    Watchtower Verified📅 Updated: Nov 4, 2026
  • CVE-2023-54413CVSS 5.1
    WPML Multilingual CMS plugin for WordPress before 4.6.1 contains a reflected cross-site scripting vulnerability that allows unauthenticated attackers...
    Watchtower Verified📅 Updated: Nov 4, 2026
  • CVE-2026-81648CVSS 10.0
    The CryptoPayment Gateway WordPress plugin from 1.2.1 to 1.2.2 does not apply an authorization check on one of...
    Admin intel📅 Updated: Nov 3, 2026
  • CVE-2026-119977CVSS 8.1
    WordPress Core is vulnerable to Remote Code Execution in versions 4.7 through 7.1.3. This is due to predictable,...
    CISA KEV📅 Added to KEV: Nov 3, 2026
  • CVE-2026-58115CVSS 10.0
    A vulnerability has been identified in SIMATIC IoT2050 Advanced (6ES7647-0BA00-1YA2) (All versions < V4.3.4.1 running Industrial OS with...
    Admin intel📅 Updated: Nov 2, 2026
  • CVE-2026-20051CVSS 7.4
    A vulnerability with the Ethernet VPN (EVPN) Layer 2 ingress packet processing of Cisco Nexus 3600 Platform Switches...
    Watchtower Verified📅 Updated: Nov 1, 2026
  • CVE-2026-20118CVSS 6.8
    A vulnerability in the handling of an Egress Packet Network Interface (EPNI) Aligner interrupt in Cisco IOS XR...
    Watchtower Verified📅 Updated: Nov 1, 2026
  • CVE-2010-20125CVSS 8.7
    DedeCMS before 5.7 contains a file inclusion vulnerability in plus/carbuyaction.php that allows remote unauthenticated attackers to control the...
    Watchtower Verified📅 Updated: Oct 30, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2022-29966CVSS 9.3
    Emerson Ovation has several protocols that have no authentication, which could allow an attacker to change controller configuration or...
    📅 Updated: Nov 3, 2026
  • CVE-2026-38600CVSS 9.8
    A Zip Slip vulnerability in the /upload endpoint of codeskyblue gohttpserver through v1.3.0 allows attackers to write arbitrary...
    📅 Updated: Nov 3, 2026
  • CVE-2026-121246CVSS 9.6
    Use after free in WebGL in Google Chrome on on Android prior to 157.0.8103.38 allowed a remote attacker...
    📅 Updated: Nov 3, 2026
  • CVE-2026-121247CVSS 9.6
    Buffer overflow in Dawn in Google Chrome on on Android prior to 157.0.8103.38 allowed a remote attacker to...
    📅 Updated: Nov 3, 2026
  • CVE-2026-121249CVSS 9.6
    Buffer overflow in ANGLE in Google Chrome prior to 157.0.8103.38 allowed a remote attacker to execute arbitrary code...
    📅 Updated: Nov 3, 2026
  • CVE-2026-121229CVSS 9.6
    Memory corruption in ANGLE in Google Chrome on on Android prior to 157.0.8103.38 allowed a remote attacker to...
    📅 Updated: Nov 3, 2026
  • CVE-2026-121234CVSS 9.6
    Privilege elevation in Contacts in Google Chrome on on Android prior to 157.0.8103.38 allowed a remote attacker to...
    📅 Updated: Nov 3, 2026
  • CVE-2026-121241CVSS 9.6
    Use after free in Navigation in Google Chrome on on Android prior to 157.0.8103.38 allowed a remote attacker...
    📅 Updated: Nov 3, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.