Do Son
A massive configuration error at DENIC paralyzed millions of .de domains. Discover how a routine DNSSEC key rotation caused a nationwide internet blackout.

Meta is scanning user height and skeletal structure to find kids under 13. See how this "Visual Analysis" AI works to purge underage accounts on Instagram.
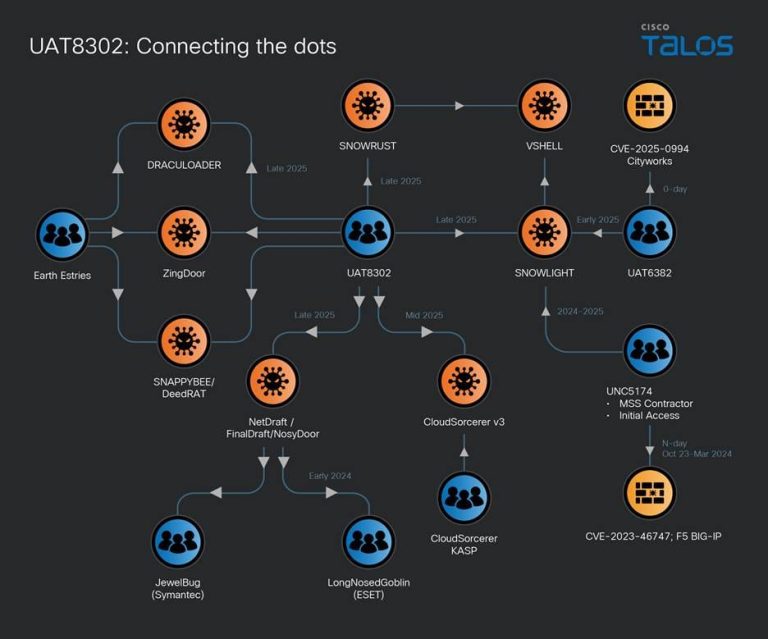
Cisco Talos exposes UAT-8302, a China-linked APT group infiltrating governments via NetDraft and CloudSorcerer. Learn how they share tools with notorious APTs.

OpenAI unveils GPT-5.5 Instant. Featuring a 52.5% reduction in hallucinations and new "Memory Attribution" tools, it’s now the default engine for all users.

Microsoft Teams for Android is adding native SIP support. Connect Zoom, WebEx, and Teams directly without installing extra apps. Full rollout starts June 2026.

Security researcher Tom reveals Microsoft Edge stores all saved credentials in plaintext memory. Learn why Microsoft calls this a feature, not a bug.

Google AppSheet is being abused by "AccountDumpling" to steal 30,000 Facebook accounts. Learn how this Vietnamese-linked group bypasses SPF/DKIM filters.
Kaspersky warns that DAEMON Tools installers (v12.5) are trojanized with the QUIC RAT. Signed binaries are being used for global espionage. Update and audit now!
A critical 7.5 CVSS flaw in Nix (CVE-2026-44028) allows standard users to gain root privileges via a stack overflow. Update your Nix installation immediately!

A critical 9.6 CVSS flaw in Argo CD (CVE-2026-42880) allows read-only users to extract plaintext Kubernetes secrets via Server-Side Diffs. Patch to v3.3.9 now!
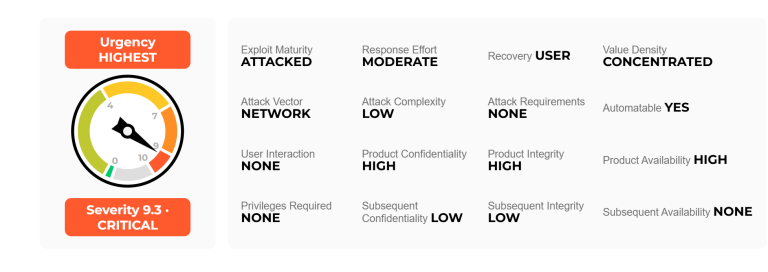
Palo Alto Networks confirms CVE-2026-0300 is being exploited in the wild. The 9.3 CVSS flaw allows unauthenticated root RCE. Secure your PAN-OS firewalls now!

Critical 9.8 CVSS flaws in vm2 affect 5.7M monthly users, allowing RCE via WASM and Promise bypasses. Upgrade to vm2 v3.11.0 immediately to secure your host.

Apache Thrift v0.23.0 fixes critical Rust DoS, Java MitM, and Node.js path traversal flaws. Secure your cross-language microservices and upgrade immediately!

 cybernewswire

Ransomware "closer" Deniss Zolotarjovs is sentenced to 102 months for extorting 50+ firms. See how the Conti-linked "Destroyer" was caught and prosecuted.

SUSE Rancher v2.14.1 fixes an 8.4 CVSS path traversal flaw (CVE-2026-25705) in UI Extensions. Prevent binary hijacking and host access—upgrade immediately!

Public PoC exploit released for OPNsense! A critical root-level RCE and lockout bypass allow total firewall takeover. Upgrade to OPNsense 26.1.7 immediately.
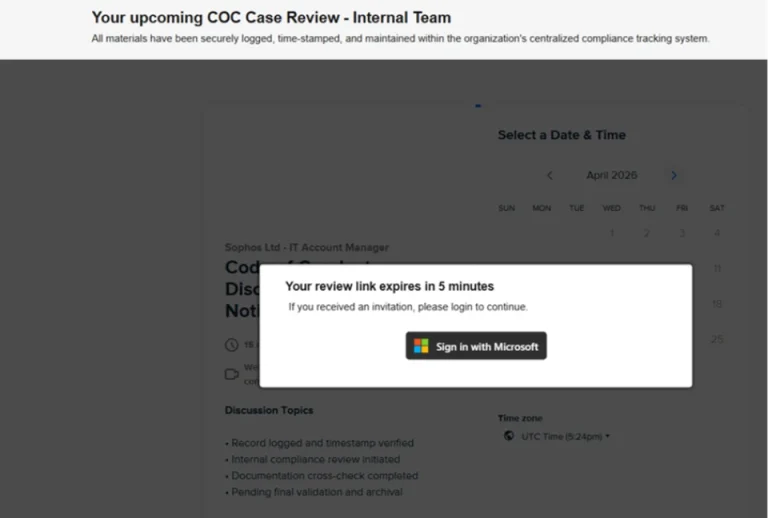
Microsoft warns of a massive AiTM phishing campaign targeting 13,000+ orgs. Using fake disciplinary lures, attackers bypass MFA to hijack active sessions.

Microsoft Defender erroneously flagged DigiCert root certificates as "Cerdigicert" malware. Discover the fix and how to restore your system's trusted root store.

Elon Musk settles with the SEC for $1.5M over his delayed 2022 Twitter stake disclosure. The record-breaking fine ends years of legal "harassment" and litigation.

Scammers are leveraging Amazon SES and leaked IAM keys to bypass security filters. Learn how to protect your organization from this high-trust phishing surge.