
 Do Son
Elon Musk settles with the SEC for $1.5M over his delayed 2022 Twitter stake disclosure. The record-breaking fine ends years of legal "harassment" and litigation.

Scammers are leveraging Amazon SES and leaked IAM keys to bypass security filters. Learn how to protect your organization from this high-trust phishing surge.

The FCC is banning equipment testing data from China. Discover how this "security" mandate will force Apple, Google, and Samsung to hike prices and delay US launches.
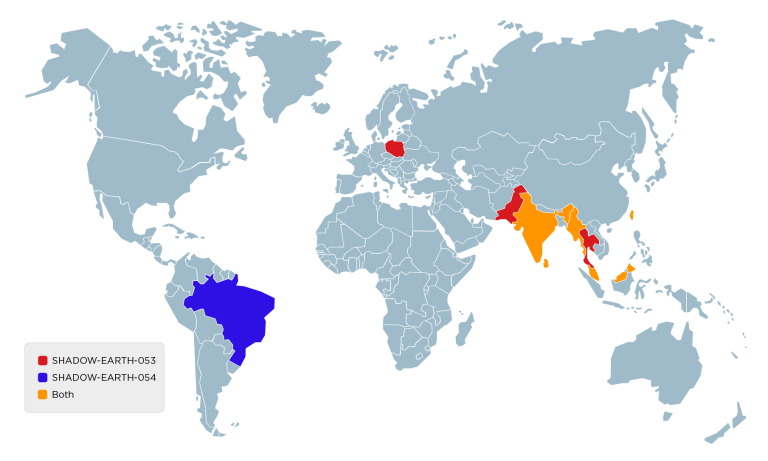
SHADOW-EARTH-053 is breaching governments and NATO using old ProxyLogon flaws and ShadowPad. Learn how this China-aligned group stays hidden via registry loading.

OpenAI and Anthropic are pivoting from API sales to $10B private equity alliances. Discover how Wall Street is becoming the ultimate AI system integrator.

Varonis uncovers Bluekit, a new phishing-as-a-service kit using AI and 40+ templates to automate session hijacking and credential theft. See how it works.

Qualcomm’s May 2026 bulletin reveals critical 9.8 CVSS flaws in Software Center & Bootloaders. Remote RCE and memory corruption affect millions of devices.

A critical injection flaw (CVE-2026-40563) in Apache Atlas lets attackers manipulate Gremlin logic to extract restricted enterprise data. Patch to v2.5.0!

Apache releases v2.4.67 to fix an HTTP/2 Double Free RCE (CVE-2026-23918) and auth bypasses. Millions of servers are affected—upgrade your infrastructure now!

Apache Polaris 1.4.1 fixes critical flaws allowing attackers to bypass S3/GCS boundaries and seize cloud credentials. Patch your Iceberg catalog now!

Google warns of CVE-2026-0073: a critical zero-click Android vulnerability allowing remote code execution via Wireless ADB. Patch to May 2026 level now!

Apache Neethi v3.2.2 patches critical flaws, including an exponential complexity attack and infinite loops. Secure your Java web services and patch today!

Gotenberg PDF API hit with a rare CVSS 10 flaw. Unauthenticated RCE, file overwrites, and SSRF bypasses discovered. Upgrade to version 8.32 immediately.

A practical explainer of multi-model AI for knowledge workers, including why it produces more reliable answers than any single LLM and how to use it.

GnuTLS v3.8.13 fixes critical heap overwrites, identity truncation, and OCSP bypasses. Secure your Linux comms and upgrade to the latest version now.
Sentry reveals a critical 9.1 CVSS flaw (CVE-2026-42354) in SAML SSO. Multi-org instances are at risk of account takeover via identity linking. Patch now!

A critical 9.1 CVSS flaw in a Go auth library causes a Patreon "identity collision," merging all users into one account. Upgrade to v2.1.2 immediately!

A public PoC has been disclosed for an Adobe Acrobat prototype pollution chain (CVE-2026-34621) actively exploited in the wild. Patch your systems today!
OpenAI launches Advanced Account Security for high-risk users. Features include mandatory passkeys, disabled SMS recovery, and automatic training exclusion.
A critical 9.9 CVSS IDOR flaw in Comet Backup allows complete cross-tenant account takeovers. Self-hosted administrators must patch servers immediately!

Anthropic eyes Fractile’s RISC-V chips to slash AI costs by 90%. Discover how this British "near-memory" architecture aims to beat NVIDIA inference by 100x.