 Do Son
Meta Description (152 Characters)Securonix uncovers Deep#Door: a self-contained Python RAT that uses TCP tunneling and obfuscated scripts to bypass traditional defense. Secure your systems now.

Apple’s security protocols are colliding with "Vibe Coding" startups. Is the tech giant protecting users from AI exploits, or stifling a new era of innovation?

OpenAI adds generative pets to Codex! Monitor background AI tasks with customizable floating companions that signal progress and errors at a glance.
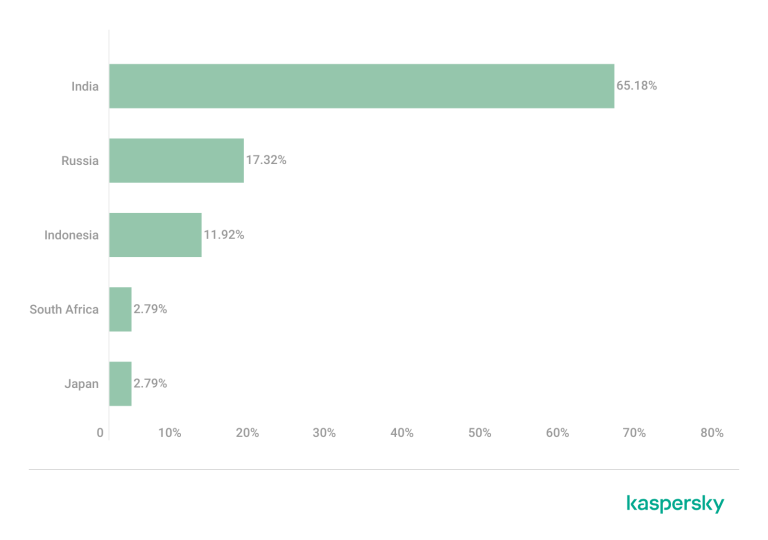
Silver Fox targets India and Russia with tax-themed phishing and the new ABCDoor backdoor. Learn how this Python-based threat hijacks screens and data.

Trend Micro uncovers a phishing campaign abusing Kuse.ai and VEC to steal credentials via markdown notes. Don't trust a domain just because of its reputation.

Why does compliance with ISO and PCI DSS remain formal without network penetration testing? Learn the role penetration testing plays in proving real security.

Apache MINA issues emergency patches for two 9.8 CVSS RCE flaws left behind by mistake. Unauthenticated attackers can bypass filters via deserialization.

MOVEit Automation faces a critical 9.8 CVSS flaw (CVE-2026-4670). Attackers can bypass auth to seize admin control and expose data. Patch immediately.

Weekly Triage: 1,134 new vulnerabilities found, including a 9.8 critical bypass in cPanel/WHM and active Express.js logic flaws. Patch your systems now.

FreeBSD warns of CVE-2026-42511: a critical dhclient flaw allowing rogue DHCP servers to execute code as root via BOOTP file injection. Patch and reboot now!

Snyk warns of active in-the-wild exploitation of the Qinglong platform. Two authentication bypass flaws grant attackers RCE to deploy .fullgc cryptominers.
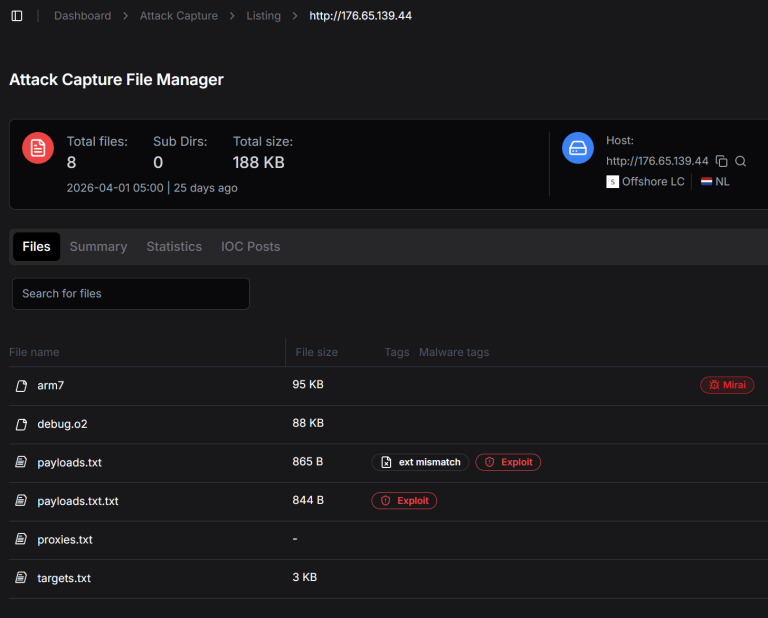
Hunt Intelligence dismantles xlabs_v1, a Mirai-derived botnet targeting 4M Android devices via port 5555. See how an exposed server leaked the entire toolkit.
A critical 9.8 CVSS vulnerability in the Temporary Login plugin puts 40,000+ WordPress sites at risk of account takeover. Patch to version 1.1.0 now!
Two US cybersecurity professionals get 4 years in prison for acting as ALPHV BlackCat ransomware affiliates, extorting victims and leaking patient data.
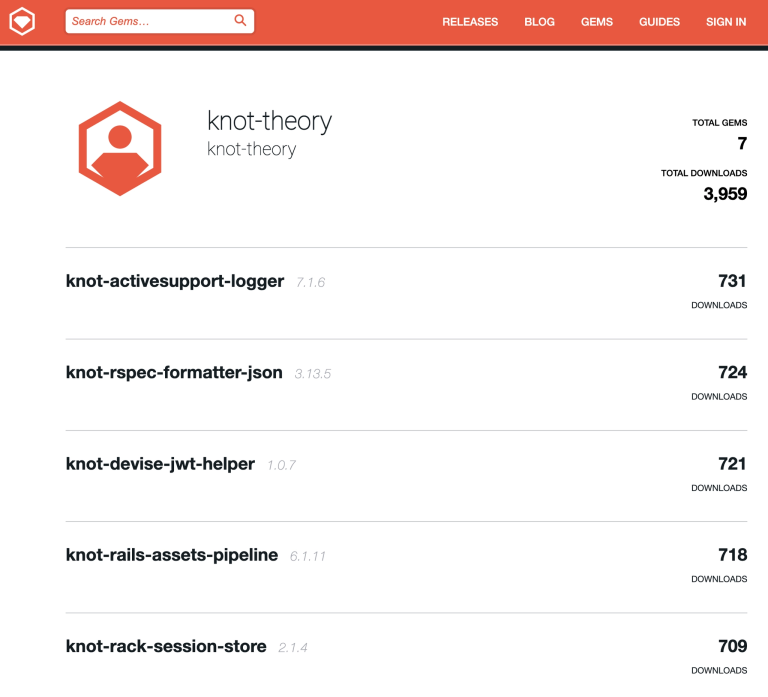
Socket uncovers a BufferZoneCorp "sleeper" campaign targeting Ruby and Go. Malicious packages steal SSH keys and subvert CI/CD pipelines. Patch now!

The alleged mastermind behind the massive "Versus Project" dark web market has been extradited to the US. He faces life in prison for cybercrime and drugs.
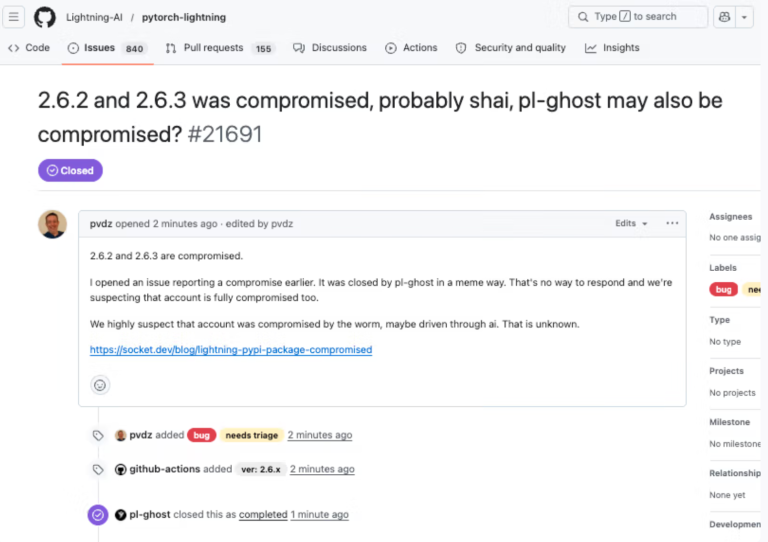
Lightning framework v2.6.2 & 2.6.3 are malicious. The "TEAM PCP" worm steals cloud secrets and poisons repos. Downgrade to 2.6.1 and rotate keys immediately!

A malicious unscoped "tanstack" npm package used live-debugged postinstall scripts to steal .env secrets via Svix webhooks. Check your dependencies now.
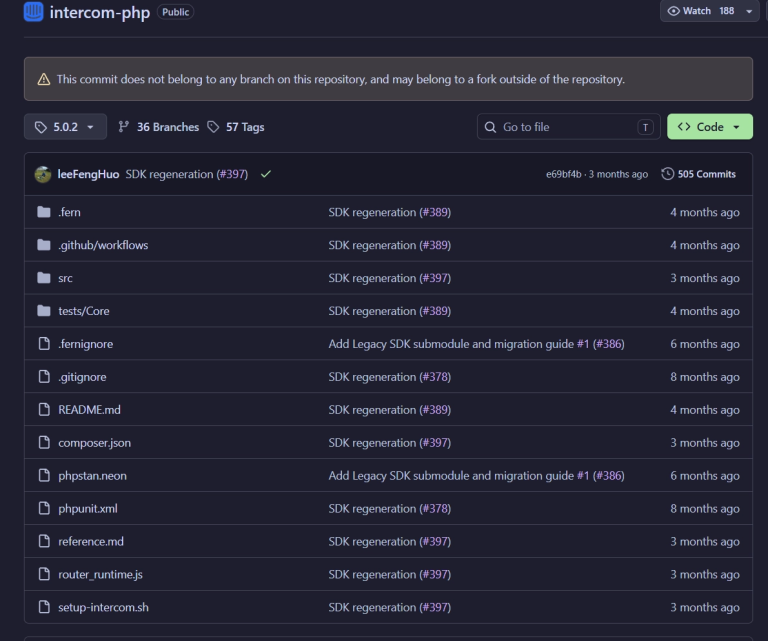
Socket uncovers a massive Mini Shai-Hulud breach in the Intercom PHP SDK. Malicious version 5.0.2 steals cloud secrets and GitHub tokens. Rotate keys now!

CISA warns "Copy Fail" (CVE-2026-31431) is exploited in the wild. Millions of Linux systems since 2017 are vulnerable to instant root privilege takeover.
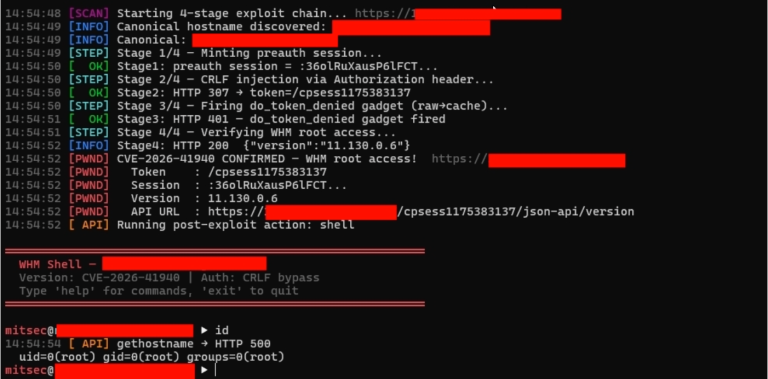
CISA warns of cPanel CVE-2026-41940 (CVSS 9.8). 44,000 IPs compromised via authentication bypass, fueling ransomware and botnets. Patch by May 3rd!

 cybernewswire
Torrance, United States / California, 1st May 2026, CyberNewswire