Skip to content
November 4, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
Legacy Leak: Deprecated GNU C Library Functions Spark New Security Fears glibc Security Legacy DNS Flaws glibc Vulnerabilities Linux Security Alert glibc Vulnerability CVE-2026-0861
  • Vulnerability Report

Legacy Leak: Deprecated GNU C Library Functions Spark New Security Fears

Do Son April 29, 2026 0

glibc warns of critical flaws (CVE-2026-5435 & CVE-2026-6238) in deprecated DNS functions. Patch legacy apps to avoid buffer overflows and memory leaks.
The Shittrix Disclosure: 89 Flaws Collapse 20 Years of Trust in Citrix and XCP-ng Shittrix Disclosure Hypervisor Vulnerabilities
  • Vulnerability Report

The Shittrix Disclosure: 89 Flaws Collapse 20 Years of Trust in Citrix and XCP-ng

Do Son April 29, 2026 0

Jakob Wolffhechel reveals "Shittrix," 89 critical flaws in Citrix XenServer & XCP-ng. CVSS 9.9 bugs allow full host takeover. Assume compromise today.
Label Leak: Hardcoded Credentials in Snap One WattBox Devices Open Door to Root Access WattBox Vulnerability Root Access Exploit
  • Vulnerability Report

Label Leak: Hardcoded Credentials in Snap One WattBox Devices Open Door to Root Access

Do Son April 29, 2026 0

Critical 9.2 CVSS flaw in WattBox 800/820 controllers (CVE-2026-41446) allows root RCE using plaintext hardware labels. Upgrade to firmware v2.10.0.0 now.

Brinker Introduces a Novel Approach to Deepfake Detection Picture1_1777442433Pk2kOwYHqu
  • Press Release

Brinker Introduces a Novel Approach to Deepfake Detection

cybernewswire April 29, 2026 0
WILMINGTON, Delaware, 29th April 2026, CyberNewswire
Read More Read more about Brinker Introduces a Novel Approach to Deepfake Detection
NVIDIA FLARE Alert: Critical SDK Vulnerabilities Open Doors to Full System Takeover NVIDIA FLARE Vulnerability Federated Learning Security NVIDIA Jetson Linux Edge AI Security BioNeMo Vulnerability Insecure Deserialization NVIDIA RTX 50 Super delay NVIDIA Nsight Vulnerability Merlin Transformers4Rec NVIDIA AI Bubble $57 Billion Revenue H20 AI chip NVIDIA earnings Blackwell AI Nvidia DGX-1 Vulnerabilities CVE-2024-0143 NVIDIA Linux Gaming, VKD3D Performance
  • Vulnerability Report

NVIDIA FLARE Alert: Critical SDK Vulnerabilities Open Doors to Full System Takeover

Do Son April 29, 2026 0

NVIDIA issued an urgent patch for a critical 9.8 CVSS flaw in the FLARE SDK. Stop unauthenticated RCE and data tampering. Upgrade to v2.7.2 immediately.

Google Translate Launches AI Pronunciation Practice for its 20th Anniversary Google Translate AI Pronunciation
  • Technology

Google Translate Launches AI Pronunciation Practice for its 20th Anniversary

Do Son April 29, 2026 0

Google Translate celebrates 20 years by adding AI-driven pronunciation feedback. Practice English, Spanish, and Hindi with real-time phonetic corrections.

OpenAI’s GPT and Codex Models Officially Join Amazon Bedrock OpenAI Amazon Bedrock
  • Technology

OpenAI’s GPT and Codex Models Officially Join Amazon Bedrock

Do Son April 29, 2026 0

AWS and OpenAI expand their alliance, bringing GPT models, Codex, and managed AI agents to Amazon Bedrock with enterprise-grade security and consolidated billing.

AWS Launches “Amazon Quick” to Bridge the Gap Between Desktop and Cloud Amazon Quick AI assistant
  • Technology

AWS Launches “Amazon Quick” to Bridge the Gap Between Desktop and Cloud

Do Son April 29, 2026 0

AWS unveils Amazon Quick, a "borderless" desktop AI assistant with long-term memory. It integrates local files with Slack, Teams, and Salesforce for proactive work.

iOS 27 and Google Gemini are Turning the iPhone into an AI Powerhouse iOS 27 Apple Intelligence Apple AI Extensions bazaar Siri iOS 27 Gemini integration Apple AI server Baltra Siri AI delay iOS 26.4 Apple Google Gemini Siri partnership, Siri powered by Google Gemini 2026 Siri Gemini, Apple Intelligence Siri, Apple AI Apple "Veritas", Siri AI Siri Gemini Supercharged Siri, AI assistant Siri Integration, App Intents Apple Siri Apple AI Strategy, ChatGPT Rival
  • Technology

iOS 27 and Google Gemini are Turning the iPhone into an AI Powerhouse

Do Son April 29, 2026 0

Apple’s iOS 27 leaks reveal a massive AI pivot: a Gemini-powered Siri App and generative "Extend" and "Reframe" tools to rival Google’s Magic Editor.

Silicon Valley’s Martial Pivot: Google Cedes “Veto Power” to the Pentagon in Classified AI Pact Google Gemini Pentagon deal Google AI Pro 5TB storage Gemini 3.1 Pro launch
  • Technology

Silicon Valley’s Martial Pivot: Google Cedes “Veto Power” to the Pentagon in Classified AI Pact

Do Son April 29, 2026 0

Google signs a secret deal with the Pentagon, allowing Gemini AI use for "any lawful purpose." With no veto power, 600 employees revolt over ethics and safety.

Tall Tales: China’s Private Contractors and the Global Hunt for Dissent UNC5221 HAFNIUM Extradition PRC State Espionage
  • Cyber Security

Tall Tales: China’s Private Contractors and the Global Hunt for Dissent

Do Son April 29, 2026 0

Citizen Lab reveals "Tall Tales," a PRC campaign using GLITTER CARP and SEQUIN CARP to hunt activists and ICIJ journalists via private contractors.

Amazon Connect Reinvents the Enterprise as an AI-Powered “Operating Brain” Amazon Connect Agentic AI
  • Technology

Amazon Connect Reinvents the Enterprise as an AI-Powered “Operating Brain”

Do Son April 29, 2026 0

Amazon Connect evolves into a suite of Agentic AI solutions for supply chain, hiring, and health. Discover how AWS is leading the shift to Agent-as-a-Service.
The Malware Factory: Unmasking the 108-Package North Korean Siege on npm npm Supply Chain Attack DPRK Malware Factory
  • Cybercriminals

The Malware Factory: Unmasking the 108-Package North Korean Siege on npm

Do Son April 29, 2026 0

Panther Research exposes a massive 2026 DPRK npm campaign using blockchain dead-drops to steal crypto keys and AI secrets. Secure your CI/CD pipelines now.

Full Exploit Disclosed: Public PoC and Technical Details Released for Critical ProFTPD SQL Injection ProFTPD SQL Injection CVE-2026-42167 Exploit
  • Vulnerability

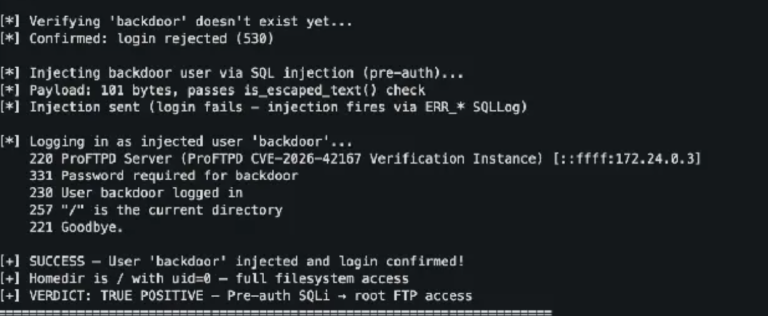
Full Exploit Disclosed: Public PoC and Technical Details Released for Critical ProFTPD SQL Injection
Do Son April 29, 2026 0

Critical SQLi in ProFTPD's mod_sql allows unauthenticated admin account injection. Full PoC code is public. Upgrade to v1.3.9a to secure your servers.

Checkmarx Falls Victim to Credential Harvesting Attack Check Point VPN vulnerability exploited in the wild Check Point VPN exploit CVE-2026-50751 zero-day Checkmarx Breach Supply Chain Attack Ivanti EPMM RCE CVE-2026-1281 Modular DS Vulnerability CVE-2026-23550 D-Link RCE Vulnerability CVE-2026-0625 Christmas 2025 GreyNoise Campaign, Japan-Based Initial Access Broker React2Shell Zero-Day, APT Active Exploitation WordPress vulnerability, authentication bypass FreePBX, zero-day Trend Micro Apex One, Remote Code Execution BitoPro Hack, Crypto Theft UNC5337 - CVE-2022-47945 Safe{Wallet} hack Fortinet vulnerability, CVE-2024-21762, FortiGate attack Balloonfly, Play ransomware Ivanti EPMM CVE-2025-4427 and CVE-2025-4428
  • Cybercriminals

Checkmarx Falls Victim to Credential Harvesting Attack

Do Son April 29, 2026 0

Checkmarx discloses a major GitHub breach via a Trivy supply chain flaw. Attackers injected malicious code and exfiltrated data for a month. Get the facts.
CISA Sounds the Alarm: State-Sponsored Hackers Weaponize New Windows and ScreenConnect Flaws State-Sponsored Exploitation CISA KEV Catalog F5 BIG-IP RCE CISA KEV Catalog SolarWinds WHD Exploit CVE-2025-40551 Zimbra XSS Zero-Day CVE-2025-27915 Exploited Windows Security Vulnerabilities
  • Vulnerability Report

CISA Sounds the Alarm: State-Sponsored Hackers Weaponize New Windows and ScreenConnect Flaws

Do Son April 29, 2026 0

CISA warns as North Korean and Russian hackers weaponize ConnectWise and Windows Shell flaws. Patch by May 12, 2026, to prevent state-sponsored espionage.

Vimeo Data Exposed in Anodot Supply Chain Attack Third-Party Risk Vimeo Data Breach
  • Data Leak

Vimeo Data Exposed in Anodot Supply Chain Attack

Do Son April 29, 2026 0

Vimeo metadata and customer emails were exposed via a breach at third-party vendor Anodot. Internal systems remain secure. Learn how to manage vendor risk.
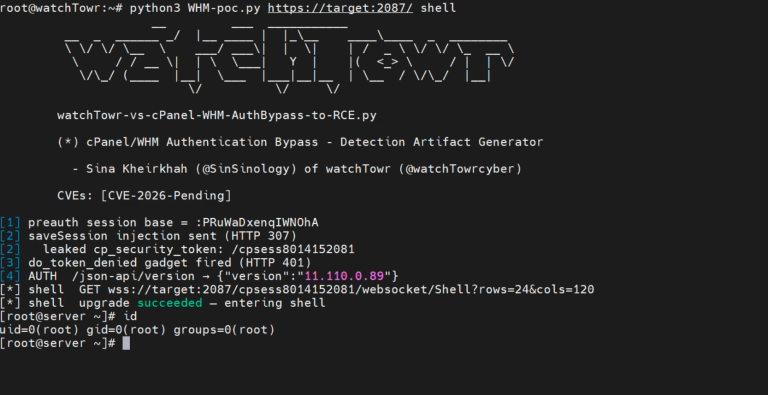
Exploited in the Wild: PoC Released for cPanel CVE-2026-41940 Authentication Bypass Zero-Day CVE-2026-41940 cPanel Authentication
  • Vulnerability Report

Exploited in the Wild: PoC Released for cPanel CVE-2026-41940 Authentication Bypass Zero-Day

Do Son April 29, 2026 0

cPanel issues emergency patches for a critical authentication vulnerability affecting all supported versions. Run /scripts/upcp --force immediately to patch.

Chrome Security Alert: Google Patches 30 Vulnerabilities in Massive Desktop Update Chrome Security Update Use After Free Chrome Security Update Critical Vulnerabilities Chrome Security Update CVE-2026-3062 Chrome Security Update V8 Engine Vulnerability Chrome Security Update CVE-2026-1862 CVE-2026-0628 Chrome 143 Update Chrome Safe Browsing UAF, CVE-2025-11756 Chrome Memory Flaws, CVE-2025-11460 Google Chrome, vulnerability CVE-2025-10200, CVE-2025-10201 Big Sleep CVE-2025-9478 Chrome Update, Security Vulnerabilities
  • Vulnerability Report

Chrome Security Alert: Google Patches 30 Vulnerabilities in Massive Desktop Update

Do Son April 29, 2026 0

Google Chrome version 147 is here with 30 vital security fixes. High-severity Use After Free bugs and V8 flaws are patched. Update your browser today.

ClickUp Discloses Exposure of Customer Emails and API Token Feature Flag Exposure ClickUp Data Breach
  • Data Leak

ClickUp Discloses Exposure of Customer Emails and API Token

Do Son April 29, 2026 0

ClickUp discloses a configuration flaw exposing 893 emails and a live API token via Split.io feature flags. Learn how client-side SDKs became a public leak.

Git Push to Root: AI-Augmented Research Uncovers Critical GitHub RCE (CVE-2026-3854) GitHub RCE CVE-2026-3854
  • Vulnerability Report

Git Push to Root: AI-Augmented Research Uncovers Critical GitHub RCE (CVE-2026-3854)

Do Son April 28, 2026 0

Wiz Research reveals CVE-2026-3854, a critical GitHub RCE. One git push could expose millions of repos. GHES users must patch to v3.19.3 immediately.
Langflow Alert: Path Traversal Flaw in Knowledge Bases API Risks Total Data Wipeout Langflow Vulnerability CVE-2026-42048 Langflow RCE CVE-2026-27966 Langflow Vulnerabilities CVE-2026-33017
  • Vulnerability Report

Langflow Alert: Path Traversal Flaw in Knowledge Bases API Risks Total Data Wipeout

Do Son April 28, 2026 0

Langflow patches a critical 9.6 CVSS path traversal vulnerability (CVE-2026-42048). Learn how an unsafe bulk delete function put entire filesystems at risk.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
  • CVE-2023-54413CVSS 6.1
    The WPML plugin for WordPress is vulnerable to Reflected Cross-Site Scripting via the wp_lang parameter in versions up...
    Watchtower Verified📅 Updated: Nov 4, 2026
  • CVE-2026-81648CVSS 10.0
    The CryptoPayment Gateway WordPress plugin from 1.2.1 to 1.2.2 does not apply an authorization check on one of...
    Admin intel📅 Updated: Nov 3, 2026
  • CVE-2026-119977CVSS 8.1
    WordPress Core is vulnerable to Remote Code Execution in versions 4.7 through 7.1.3. This is due to predictable,...
    CISA KEV📅 Added to KEV: Nov 3, 2026
  • CVE-2026-58115CVSS 10.0
    A vulnerability has been identified in SIMATIC IoT2050 Advanced (6ES7647-0BA00-1YA2) (All versions < V4.3.4.1 running Industrial OS with...
    Admin intel📅 Updated: Nov 2, 2026
  • CVE-2026-20051CVSS 7.4
    A vulnerability with the Ethernet VPN (EVPN) Layer 2 ingress packet processing of Cisco Nexus 3600 Platform Switches...
    Watchtower Verified📅 Updated: Nov 1, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-121802CVSS 9.1
    @better-auth/expo before 1.7.16 allows certain account-takeover outcomes (e.g., unauthenticated changes of any account's email address), because it signs...
    📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-118762CVSS 9.3
    Monkeytype is a minimalistic and customizable typing test. Prior to 26.43.0, the .github/workflows/fix-formatting.yml workflow runs on pull_request_target with...
    📅 Updated: Nov 4, 2026
  • CVE-2025-49602CVSS 9.8
    An issue was discovered in Keyfactor EJBCA 9. When an administrator is removed from its administrator role while...
    📅 Updated: Nov 4, 2026
  • CVE-2026-121615CVSS 10.0
    A vulnerability was determined in Linksys E5600 1.1.0.26. Affected is an unknown function of the file /cgi-bin/mesh_login.cgi of...
    📅 Updated: Nov 4, 2026
  • CVE-2026-121609CVSS 10.0
    A vulnerability was identified in Qihoo 360 Whole Home Router M5 4.0.17.1566. This issue affects the function Home...
    📅 Updated: Nov 4, 2026
  • CVE-2026-51912CVSS 9.8
    OpenBMB XAgent v1.0.0 contains directory traversal vulnerability in main-upload_file-the-preserved-live-upload-file-witness-directly-reaches (ToolServer/ToolServerNode/main.py:46).
    📅 Updated: Nov 4, 2026
  • CVE-2026-107056CVSS 9.1
    Insecure permissions in the io.file.importer.ImportActivity component of OpenTracks versionCode 6751 allows unauthorized attackers to inject crafted tracking data...
    📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.