
 Do Son
Apache Thrift fixes critical cross-language vulnerabilities (MitM, memory corruption, DoS). Secure your Java, Go, and C++ stacks by upgrading to version 0.23.0.

Critical 9.0 CVSS RCE in Nginx UI (CVE-2026-42238) exploits a 10-minute unauthenticated window. Attackers can seize root control. Patch to the latest version now.

Critical RCE flaws hit Apache Camel via header injection and unsafe deserialization. Secure your integrations and upgrade to version 4.20.0 today.

BlueNoroff uses a "self-reinforcing" deepfake pipeline to target crypto CEOs. Fake Zoom meetings and stolen footage lead to a 5-minute system compromise.
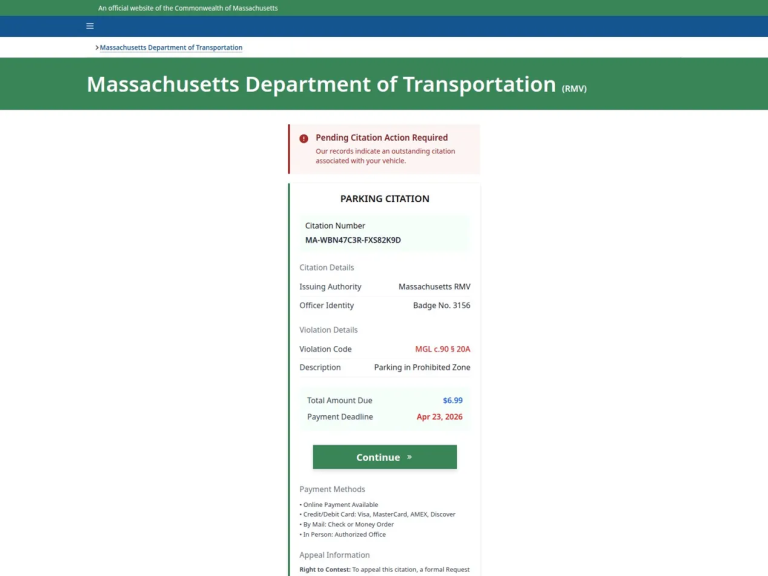
Cyble uncovers "Operation Trust Trap," a 16,800-domain network weaponizing *.gov trust to steal credentials. See how APT36 and others hijack the human eye.

Effective June 1, 2026, GitHub Copilot transitions to usage-based billing. Learn how AI credits, token throughput, and model multipliers will impact your workflow.
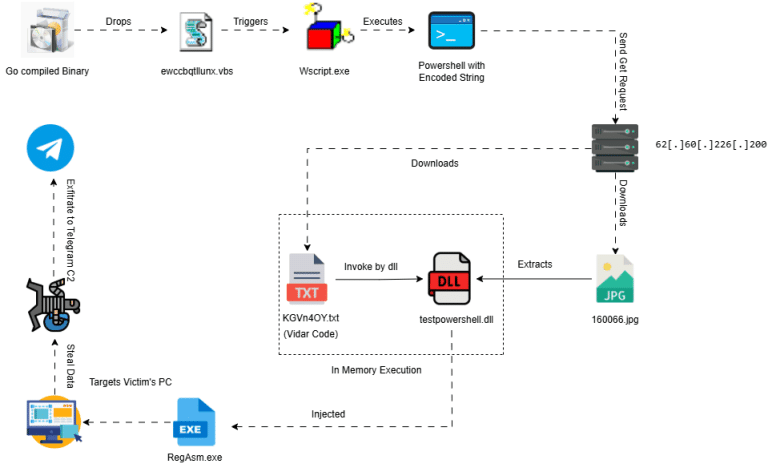
Vidar infostealer evolves into a fileless 2026 threat. From fake CAPTCHAs to "Claude Code" leaks, see how it steals crypto and passwords via Telegram C2.

China's NDRC halts Meta’s $2B acquisition of Manus AI. Despite relocating to Singapore, the "agentic" startup faces the first-ever forced unwinding of a foreign AI deal.
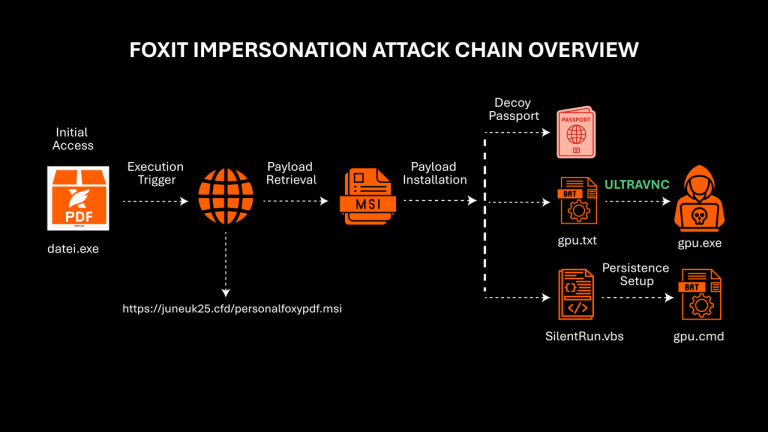
G DATA warns Foxit PDF users of a global malware campaign using fake installers and Danish passport decoys to deploy hidden UltraVNC remote access tools.

Critical CVSS 10 update for Gemini CLI (@google/gemini-cli). Fixes headless RCE and --yolo prompt injection risks. Upgrade to v1.83.7 to secure your pipelines.
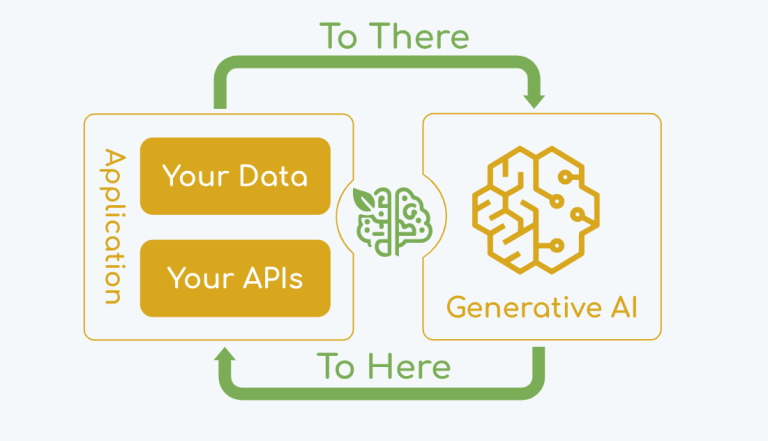
Spring AI discloses two critical injection flaws (CVE-2026-40967 & 40978) in Vector Store implementations. Upgrade to v1.0.6 or v1.1.5 now to prevent data leaks.

PRC national Xu Zewei extradited to the US for HAFNIUM intrusions and targeting COVID-19 research. He faces a 9-count indictment for state-sponsored hacks.
LiteLLM CVE-2026-42208 is under active exploitation. Attackers are using SQL injection to steal AI credentials. Patch to v1.83.7 and rotate keys immediately.

Apache MINA (CVE-2026-41635) suffers a critical 9.8 CVSS RCE flaw. Learn how a deserialization filter bypass puts servers at risk and how to patch today.
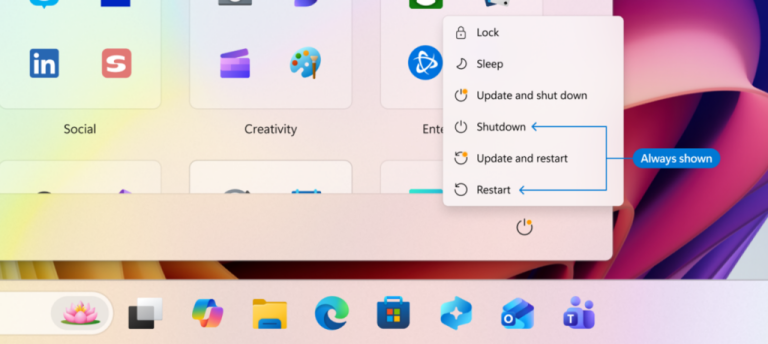
Microsoft is fixing the most frustrating part of Windows 11. Build 26300.8289 separates updates from standard restart/shutdown and allows indefinite pauses.

OpenAI is building an AI-first smartphone with MediaTek and Luxshare. Ditching apps for autonomous agents, this device aims to master the mobile ecosystem.

Amazon launches Claude Platform on AWS. Direct access to Anthropic's native AI features with AWS IAM security and billing—perfect for rapid AI innovation.
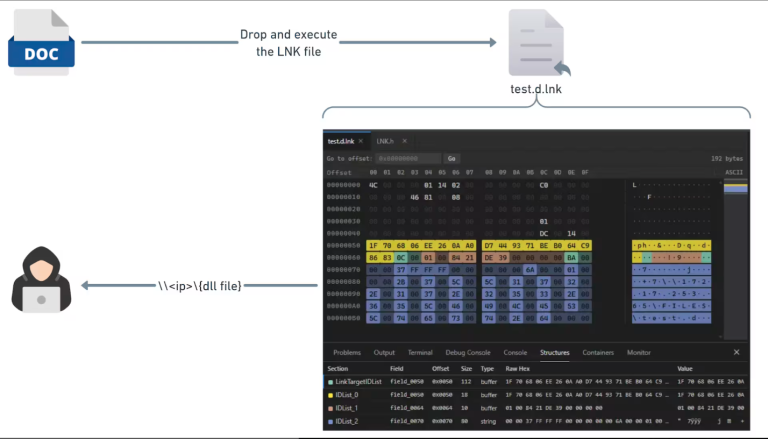
Akamai uncovers CVE-2026-32202: A zero-click LNK flaw used by APT28 to steal Windows NTLM hashes silently. No user interaction required. Patch alert!
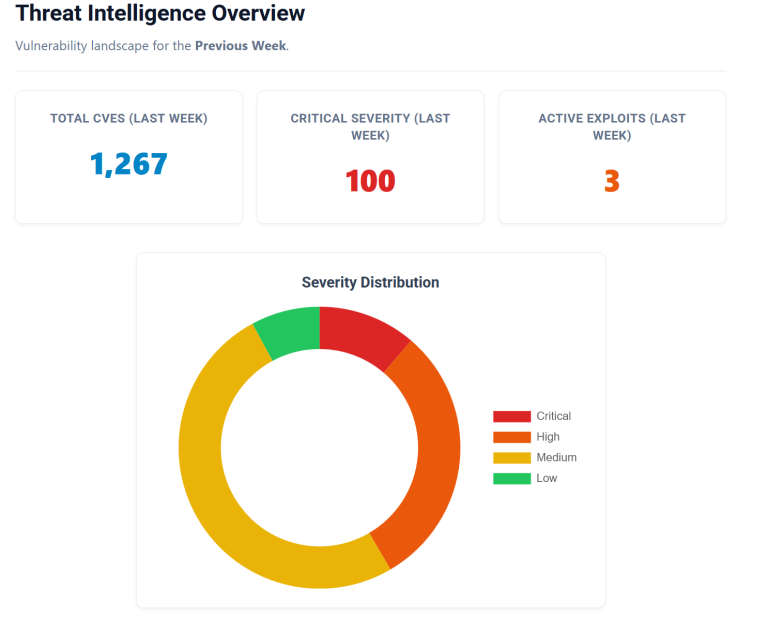
Triaging 1,200+ new flaws: AI toolkits and remote support under fire. Get the CISA KEV breakdown and CVSS 10.0 patches for the week of April 20,Triaging 1,200+ new flaws: AI toolkits and remote support under fire. Get the CISA KEV breakdown and CVSS 10.0 patches for the week of April 20, 2026. 2026.

Kaspersky reveals PhantomRPC, a novel Windows architectural flaw enabling LPE to SYSTEM. Microsoft denies a patch. Monitor SeImpersonatePrivilege now.

Critical 9.8 CVSS RCE in Pipecat (CVE-2025-62373)! Unsafe pickle deserialization allows remote code execution. Patch to v0.0.94 immediately to secure agents.

Carlson VASCO-B GNSS receivers face a critical 9.4 CVSS flaw with zero authentication. Stop remote attackers from drifting your location data. Update to v1.4.0.