Skip to content
November 4, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
Carlson VASCO-B GNSS Receivers Left Open to Remote Hijack GNSS Hijacking Carlson Software
  • Vulnerability Report

Carlson VASCO-B GNSS Receivers Left Open to Remote Hijack

Do Son April 27, 2026 0

Carlson VASCO-B GNSS receivers face a critical 9.4 CVSS flaw with zero authentication. Stop remote attackers from drifting your location data. Update to v1.4.0.

Critical 9.8 CVSS Flaw Exposes Intrado 911 Emergency Gateways Intrado 911 Gateway Vulnerability CVE-2026-6074
  • Vulnerability Report

Critical 9.8 CVSS Flaw Exposes Intrado 911 Emergency Gateways

Do Son April 27, 2026 0

Critical 9.8 CVSS flaw (CVE-2026-6074) in Intrado 911 Gateway allows unauthenticated access to management tools. Protect emergency services and patch today.
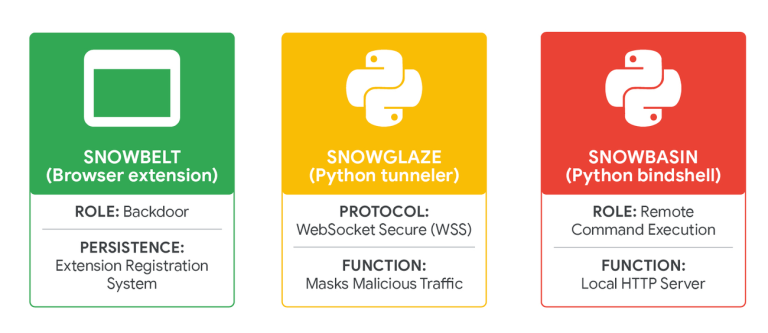
UNC6692 Uses MS Teams and Cloud Reputations to Hijack Active Directory UNC6692 SNOW Malware Suite
  • Malware

UNC6692 Uses MS Teams and Cloud Reputations to Hijack Active Directory

Do Son April 27, 2026 0

UNC6692 uses MS Teams impersonation to deploy the SNOW suite. Learn how "living off the cloud" bypasses reputation filters to hijack Active Directory.
Inside “HexagonalRodent”: The AI-Powered DPRK Syndicate Hauling Millions in Crypto HexagonalRodent Malware Web3 Developer Scams
  • Cybercriminals

Inside “HexagonalRodent”: The AI-Powered DPRK Syndicate Hauling Millions in Crypto

Do Son April 27, 2026 0

North Korean group HexagonalRodent stole millions in Q1 2026 using AI-generated lures and backdoored VS Code tasks. Protect your Web3 wallet now.
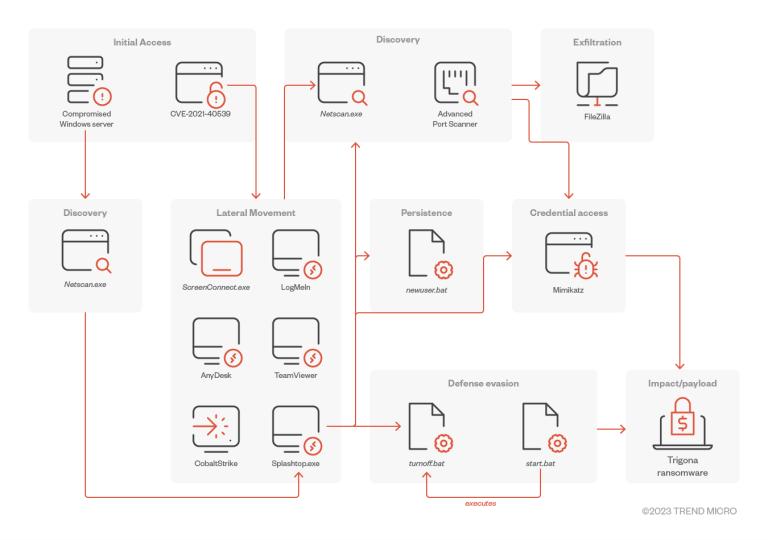
Tactical Evolution: Trigona Ransomware Debuts Custom Exfiltration Armory Trigona Ransomware Custom Exfiltration Tool
  • Cybercriminals

Tactical Evolution: Trigona Ransomware Debuts Custom Exfiltration Armory

Do Son April 25, 2026 0

Trigona ransomware swaps Rclone for a custom tool that rotates connections to evade monitoring. Learn how uploader_client.exe powers their data theft.

Academic Exposure: The Unpatched Flaw Siphoning Student Data from DRC INSIGHT Fortra BoKS vulnerability OS command injection, CVE-2026-9862 Altium Enterprise Server Vulnerability CVE-2026-9129 Path Traversal Patreon OAuth Vulnerability Identity Collision DRC INSIGHT Vulnerability Exam Data Hijacking Horner Automation PLC Industrial Brute Force Honeywell IQ4x Vulnerability CVE-2026-3611 DJI Romo vacuum security flaw Python Cryptography Vulnerability CVE-2026-26007 Open5GS Vulnerability CVE-2026-0622 Vivotek IP7137 Vulnerabilities CVE-2025-66049 Forcepoint DLP Vulnerability CVE-2025-14026 Cellopoint Secure Email Gateway - CVE-2024-9043
  • Vulnerability Report

Academic Exposure: The Unpatched Flaw Siphoning Student Data from DRC INSIGHT

Do Son April 24, 2026 0

Unpatched CVE-2026-5756 in DRC INSIGHT allows unauthenticated hijacking of student exam responses and traffic manipulation. Secure your school's network now.
The 9.1 CVSS Flaw: Why Millions of Spring Boot Apps May Be Exposed Spring Cloud Config Vulnerability CVE-2026-40982 Spring Boot Vulnerability CVSS 9.1 Bypass CVE-2022-31692 Spring Boot Vulnerability Authentication Bypass
  • Vulnerability Report

The 9.1 CVSS Flaw: Why Millions of Spring Boot Apps May Be Exposed

Do Son April 24, 2026 0

New Spring Boot flaws (CVSS 9.1) bypass security filters and enable RCE via timing attacks. Impacting versions 2.7.x to 4.0.x—secure your Java apps now.
Triple Threat: Apache ActiveMQ Vulnerabilities Expose Enterprises to RCE and XSS ActiveMQ security flaws Jolokia web console exploit ActiveMQ RCE Jolokia Spring Vulnerability ActiveMQ MQTT Vulnerability CVE-2025-66168 Apache Artemis Vulnerability CVE-2026-27446
  • Vulnerability Report

Triple Threat: Apache ActiveMQ Vulnerabilities Expose Enterprises to RCE and XSS

Do Son April 24, 2026 0

Critical RCE and XSS vulnerabilities hit Apache ActiveMQ (CVE-2026-41044, 40466). Authenticated attackers can hijack the JVM. Update to 5.19.6 or 6.2.5 now.

Workflow Warning: The n8n CVSS 10.0 Prototype Pollution Crisis n8n RCE Automation Security n8n Vulnerability Prototype Pollution RCE
  • Vulnerability Report

Workflow Warning: The n8n CVSS 10.0 Prototype Pollution Crisis

Do Son April 24, 2026 0

Critical CVSS 10 and 9.4 vulnerabilities hit n8n. Prototype pollution in XML nodes can lead to full RCE. Patch to v2.18.1 or v1.123.32 immediately.

The Global Surge in Modbus/TCP Probes Targeting Our Physical World Modbus Exploitation ICS Security
  • Cybercriminals

The Global Surge in Modbus/TCP Probes Targeting Our Physical World

Do Son April 24, 2026 0

Cato Networks reveals 235,500+ Modbus probes on PLCs across 70 countries. Learn how attackers fingerprint and hijack industrial control systems. Patch now.

Beyond Stuxnet: Uncovering fast16, the Apex Saboteur That Rewrites Mathematical Reality fast16 Malware Cyber Sabotage IronWind malware Stealc
  • Malware

Beyond Stuxnet: Uncovering fast16, the Apex Saboteur That Rewrites Mathematical Reality

Do Son April 24, 2026 0

SentinelLABS reveals fast16, a 2005 framework that predates Stuxnet. It sabotages high-precision calculations in nuclear research by patching math in memory.

Inside the Rise of Dabai Guarantee and the Telegram “Sweeping” Economy Dabai Guarantee Ghost-Tapping Fraud
  • Cybercriminals

Inside the Rise of Dabai Guarantee and the Telegram “Sweeping” Economy

Do Son April 24, 2026 0

Dabai Guarantee emerges as the new hub for Chinese cybercrime, using Telegram and "ghost-tapping" to coordinate global retail fraud and USDT money laundering.

Beyond the Chatbot: GPT-5.5 and the Dawn of the Autonomous AI Workforce OpenAI subscription quota changes GPT-5.5 Agentic AI GPT-5.5 Instant release
  • Technology

Beyond the Chatbot: GPT-5.5 and the Dawn of the Autonomous AI Workforce

Do Son April 24, 2026 0

OpenAI launches GPT-5.5: a revolutionary agentic model co-designed with NVIDIA. Discover how it solves 58% of GitHub issues and automates senior engineering.
Microsoft Buries “Microsoft Gaming” to Launch the Xbox PC-Hybrid Era Xbox Project Helix Xbox Mode Windows 11
  • Technology

Microsoft Buries “Microsoft Gaming” to Launch the Xbox PC-Hybrid Era

Do Son April 24, 2026 0

Xbox is back. Microsoft retires the "Microsoft Gaming" name and unveils Project Helix—a radical console-PC hybrid designed to win the living room in 2026.

AI in the Driver’s Seat: How the ‘Bissa’ Scanner Hijacked 900+ Firms in Weeks AI-Assisted Exploitation Bissa Scanner
  • Cybercriminals

AI in the Driver’s Seat: How the ‘Bissa’ Scanner Hijacked 900+ Firms in Weeks

Do Son April 24, 2026 0

Dr. Tube’s AI-assisted Bissa scanner exploited 900+ companies using React2Shell (CVE-2025-55182) to steal 30,000 .env files. See the AI-led attack workflow.

OpenAI Launches “Workspace Agents” to Industrialize Corporate Labor OpenAI Workspace Agents
  • Technology

OpenAI Launches “Workspace Agents” to Industrialize Corporate Labor

Do Son April 24, 2026 0

OpenAI debuts Workspace Agents: Codex-powered digital laborers that work 24/7 in cloud sandboxes to manage sales, IT audits, and reporting autonomously.

The Grok-Powered Pivot: X Unveils Custom Timelines and “Snooze” Tools to Conquer Feed Slop X Custom Timelines Grok AI
  • Technology

The Grok-Powered Pivot: X Unveils Custom Timelines and “Snooze” Tools to Conquer Feed Slop

Do Son April 24, 2026 0

X product lead Nikita Bier debuts Custom Timelines and Snooze Topics. Powered by Grok AI, these Premium-only tools offer 75+ categories for a bespoke feed.

Tropic Trooper Weaponizes GitHub and VS Code for East Asian Espionage Tropic Trooper Espionage VS Code Tunnels
  • Cybercriminals

Tropic Trooper Weaponizes GitHub and VS Code for East Asian Espionage

Do Son April 24, 2026 0

Tropic Trooper's 2026 campaign uses trojanized SumatraPDF and VS Code tunnels for stealthy East Asian espionage. Learn how to defend your infrastructure.

The Great Linux Purge: Why the Kernel is Dumping 27,000 Lines of Code to Stop the AI Vulnerability Deluge Linux Kernel legacy driver removal Linux kernel x86 page fault, interrupt state asymmetry fix Linux ISO, false positive CVE-2023-6200 - Linux Kernel 6.12 LTS 6.14
  • Linux

The Great Linux Purge: Why the Kernel is Dumping 27,000 Lines of Code to Stop the AI Vulnerability Deluge

Do Son April 24, 2026 0

Linux maintainers propose purging 27,646 lines of legacy network code to combat a flood of AI-generated vulnerability reports and focus on modern security.

The Local Guardian: OpenAI Unveils a 1.5B Open-Source Model to Redact PII Locally OpenAI token price reduction OpenAI Deployment Company DeployCo OpenAI IPO strategy OpenAI Privacy Filter 1.5B OpenAI $122 billion funding OpenAI GitHub alternative OpenAI military agreement 2026 OpenAI Stargate project collapse NVIDIA OpenAI investment stall ChatGPT Go $8 subscription, OpenAI GPT-5.2 Instant ads OpenAI Torch acquisition, Unified Medical Memory OpenAI Head of Preparedness 2025, Sam Altman AI safety lawsuits ChatGPT Advertising Speculation OpenAI Ad Code Denial OpenAI AI Confession Hallucination Mitigation ChatGPT Quality Focus OpenAI Gemini Red Alert ChatGPT Login, AI ecosystem OpenAI Mental Health, AI Well-Being Council ChatGPT Instant Checkout, Agentic Commerce OpenAI cloud computing OpenAI, startup incubator OpenAI chips, NVIDIA competition AI competition, antitrust lawsuit GPT-5, OpenAI Livestream OpenAI Open-Weight, AI Models OpenAI Infrastructure, AI Data Centers ChatGPT Business, Office Productivity OpenAI Open-Weight Model, WindSurf Acquisition OpenAI AI Browser, ChatGPT Integration Mattel AI, OpenAI Partnership OpenAI o3, Price Cut OpenAI's Next-Gen AI: O3-Pro's Enhanced Reasoning PowerOpenAI profit OpenAI Bid OpenAI Social Network ChatGPT Social OpenAI Non-profit OpenAI UAE ChatGPT Plus free
  • Technology

The Local Guardian: OpenAI Unveils a 1.5B Open-Source Model to Redact PII Locally

Do Son April 24, 2026 0

OpenAI's new 1.5B Privacy Filter uses semantic reasoning to tag sensitive data locally. Run PII protection on consumer hardware with 128K context support.

The Notification Trap: How Apple’s New iOS Patch Blocks Forensic Recovery of “Deleted” Signal Messages iOS 26.4.2 CVE-2026-28950 CVE-2024-27842, Wang Tielei has also released a PoC exploit for CVE-2023-40404
  • Vulnerability Report

The Notification Trap: How Apple’s New iOS Patch Blocks Forensic Recovery of “Deleted” Signal Messages

Do Son April 24, 2026 0

Apple’s iOS 26.4.2 fixes a flaw (CVE-2026-28950) that let the FBI recover deleted Signal messages from notification logs. Update now to secure your private chats.

The Cloud Runs Dry: ClawCloud Abruptly Terminates Container Services—Is Your Data Safe? ClawCloud Run shutdown
  • Technology

The Cloud Runs Dry: ClawCloud Abruptly Terminates Container Services—Is Your Data Safe?

Do Son April 24, 2026 0

ClawCloud Run is shutting down. With free tiers ending May 11, 2026, and a strict refund deadline of May 20, users must migrate data immediately to avoid loss.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
  • CVE-2023-54413CVSS 6.1
    The WPML plugin for WordPress is vulnerable to Reflected Cross-Site Scripting via the wp_lang parameter in versions up...
    Watchtower Verified📅 Updated: Nov 4, 2026
  • CVE-2026-81648CVSS 10.0
    The CryptoPayment Gateway WordPress plugin from 1.2.1 to 1.2.2 does not apply an authorization check on one of...
    Admin intel📅 Updated: Nov 3, 2026
  • CVE-2026-119977CVSS 8.1
    WordPress Core is vulnerable to Remote Code Execution in versions 4.7 through 7.1.3. This is due to predictable,...
    CISA KEV📅 Added to KEV: Nov 3, 2026
  • CVE-2026-58115CVSS 10.0
    A vulnerability has been identified in SIMATIC IoT2050 Advanced (6ES7647-0BA00-1YA2) (All versions < V4.3.4.1 running Industrial OS with...
    Admin intel📅 Updated: Nov 2, 2026
  • CVE-2026-20051CVSS 7.4
    A vulnerability with the Ethernet VPN (EVPN) Layer 2 ingress packet processing of Cisco Nexus 3600 Platform Switches...
    Watchtower Verified📅 Updated: Nov 1, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-28336CVSS 9.9
    SolarWinds Dameware was found to be affected by a command injection vulnerability that could lead to the compromise...
    📅 Updated: Nov 4, 2026
  • CVE-2026-13594CVSS 9.1
    Zoho Corporation's ManageEngine Log360 and EventLog Analyzer versions 13062 and below are vulnerable to an issue that could...
    📅 Updated: Nov 4, 2026
  • CVE-2026-13214CVSS 9.8
    The OCPP 1.6 client in subsys/net/lib/ocpp/ocpp_j.c contains a stack buffer overflow in parse_getconfig_msg(). When handling a GetConfiguration request...
    📅 Updated: Nov 4, 2026
  • CVE-2026-121246CVSS 9.6
    Use after free in WebGL in Google Chrome on on Android prior to 157.0.8103.38 allowed a remote attacker...
    📅 Updated: Nov 4, 2026
  • CVE-2026-121247CVSS 9.6
    Buffer overflow in Dawn in Google Chrome on on Android prior to 157.0.8103.38 allowed a remote attacker to...
    📅 Updated: Nov 4, 2026
  • CVE-2026-121185CVSS 9.6
    Use after free in PictureInPicture in Google Chrome prior to 157.0.8103.38 allowed a remote attacker leveraging social engineering...
    📅 Updated: Nov 4, 2026
  • CVE-2026-121229CVSS 9.6
    Memory corruption in ANGLE in Google Chrome on on Android prior to 157.0.8103.38 allowed a remote attacker to...
    📅 Updated: Nov 4, 2026
  • CVE-2026-121156CVSS 9.6
    Buffer overflow in Dawn in Google Chrome prior to 157.0.8103.38 allowed a remote attacker to potentially execute arbitrary...
    📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.