Skip to content
November 4, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
The Notification Trap: How Apple’s New iOS Patch Blocks Forensic Recovery of “Deleted” Signal Messages iOS 26.4.2 CVE-2026-28950 CVE-2024-27842, Wang Tielei has also released a PoC exploit for CVE-2023-40404
  • Vulnerability Report

The Notification Trap: How Apple’s New iOS Patch Blocks Forensic Recovery of “Deleted” Signal Messages

Do Son April 24, 2026 0

Apple’s iOS 26.4.2 fixes a flaw (CVE-2026-28950) that let the FBI recover deleted Signal messages from notification logs. Update now to secure your private chats.

The Cloud Runs Dry: ClawCloud Abruptly Terminates Container Services—Is Your Data Safe? ClawCloud Run shutdown
  • Technology

The Cloud Runs Dry: ClawCloud Abruptly Terminates Container Services—Is Your Data Safe?

Do Son April 24, 2026 0

ClawCloud Run is shutting down. With free tiers ending May 11, 2026, and a strict refund deadline of May 20, users must migrate data immediately to avoid loss.

Unpatched and Exposed: Public PoC Released for Critical 9.8 CVSS Xiongmai IP Camera Flaw KMW CCTV vulnerability unauthenticated password reset Xiongmai IP Camera Vulnerability CVE-2025-65856 CVE-2024-8956 (CVSS 9.1): PTZOptics Cameras
  • Vulnerability Report

Unpatched and Exposed: Public PoC Released for Critical 9.8 CVSS Xiongmai IP Camera Flaw

Do Son April 24, 2026 0

Critical 9.8 CVSS auth bypass hits Xiongmai IP cameras. Public PoC is live with NO patch available. Secure your live feeds and isolate your devices now!
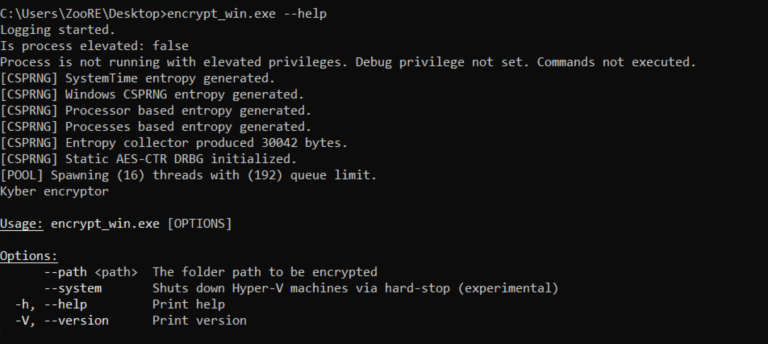
Operational Blackout: How Kyber Ransomware Targets the Heart of Virtualized Environments Kyber Ransomware ESXi Virtualization Attack
  • Malware

Operational Blackout: How Kyber Ransomware Targets the Heart of Virtualized Environments

Do Son April 24, 2026 0

Rapid7 uncovers Kyber, a dual-platform ransomware targeting VMware ESXi and Windows. Learn how it causes operational blackouts and bypasses recovery.

Supply Chain Sabotage: Bitwarden CLI Compromised in Global “Checkmarx” Campaign Bitwarden CLI Compromise Dune Supply Chain Attack
  • Malware

Supply Chain Sabotage: Bitwarden CLI Compromised in Global “Checkmarx” Campaign

Do Son April 24, 2026 0

Bitwarden CLI v2026.4.0 compromised in "Dune"-themed supply chain attack. Malware steals cloud secrets and SSH keys. Rotate your credentials immediately.

Arcane Door Reopened: The Cisco Firepower Backdoor That Only a Hard Reboot Can Kill FortiClient EMS exploitation Cisco FIRESTARTER Backdoor Arcane Door Campaign Dell RecoverPoint Zero-Day UNC6201 Espionage Notepad++ Compromise Supply Chain Attack Magento SessionReaper CVE-2025-54236 ShadowRay 2.0, AI-Generated Malware WordPress Auth Bypass, CVE-2025-5947 Exploited EcoStruxure Vulnerabilities, Industrial Control System UNC5820 - CVE-2014-2120 - CVE-2021-44207
  • Malware
  • Vulnerability Report

Arcane Door Reopened: The Cisco Firepower Backdoor That Only a Hard Reboot Can Kill

Do Son April 24, 2026 0

Cisco Talos uncovers the FIRESTARTER backdoor in Arcane Door's latest attack on Firepower devices. Patch CVE-2025-20333 now to stop state-sponsored espionage.

Harvester APT Goes Cross-Platform: New Linux Backdoor Abuses Microsoft Graph API Harvester APT Linux Backdoor OT Cyberattack Iranian APT Operation Olalampo MuddyWater APT Prince of Persia APT, Tonnerre v50 Patchwork APT, DLL Sideloading Subtle Snail, cyber espionage ShadowSilk, cyber espionage Volt Typhoon APT Group - Chinese Cybersecurity Firm
  • Cyber Security
  • Malware

Harvester APT Goes Cross-Platform: New Linux Backdoor Abuses Microsoft Graph API

Do Son April 24, 2026 0

Harvester APT expands to Linux using Microsoft Graph API for C2. Learn how the "GoGra" variant uses Outlook and "Zomato Pizza" lures to evade detection.

Windows Python Users Warned of High-Severity “asyncio” Memory Flaw Python asyncio Vulnerability Windows Buffer Overflow ormar SQL Injection CVE-2026-26198 CVE-2024-49768 - Waitress WSGI server
  • Vulnerability Report

Windows Python Users Warned of High-Severity “asyncio” Memory Flaw

Do Son April 23, 2026 0

Python’s asyncio on Windows faces a high-severity RCE (CVE-2026-3298). A missing boundary check in ProacterEventLoop risks memory corruption. Update now.

Mailcow Critical Alert: Unauthenticated XSS Threatens Admin Takeover mailcow XSS CVE-2026-40872
  • Vulnerability Report

Mailcow Critical Alert: Unauthenticated XSS Threatens Admin Takeover

Do Son April 23, 2026 0

Unauthenticated attackers can hijack mailcow admin sessions via a critical CVSS 9.3 Stored XSS in Autodiscover logs. Patch to version 2026-03b immediately.

Unpatch Ollama Flaw: Malicious Model Uploads Can Leak Server Heap Memory Ollama Heap Leak CVE-2026-5757 Anritsu Vulnerability Authentication Bypass Gootloader Malware Malformed ZIP Evasion Blender Malware, StealC V2 Lectora, XSS CVE-2025-9125 HFS RCE, Template Injection Arch Linux Malware, CHAOS RAT CVE-2024-56404 - CVE-2024-39327 CVE-2025-2538
  • Vulnerability Report

Unpatch Ollama Flaw: Malicious Model Uploads Can Leak Server Heap Memory

Do Son April 23, 2026 0

Unpatched CVE-2026-5757 in Ollama allows unauthenticated heap memory exfiltration via crafted GGUF files. No patch available—secure your LLM servers now.

Critical Authentication Bypass in Apache HttpClient 5.6 Apache HttpClient Vulnerability SCRAM-SHA-256 Auth Bypass
  • Vulnerability Report

Critical Authentication Bypass in Apache HttpClient 5.6

Do Son April 23, 2026 0

Apache HttpClient 5.6 reveals a critical auth flaw (CVE-2026-40542) in SCRAM-SHA-256. Secure your Java microservices—upgrade to 5.6.1 immediately.

Critical 9.8 CVSS Flaws Hit ArcGIS Infrastructure ArcGIS Server security patch directory traversal vulnerability ArcGIS Vulnerability GIS Security
  • Vulnerability Report

Critical 9.8 CVSS Flaws Hit ArcGIS Infrastructure

Do Son April 23, 2026 0

Esri issues an urgent fix for critical 9.8 CVSS flaws in ArcGIS. Over-scoped developer credentials could expose GIS data. Patch your portal immediately.
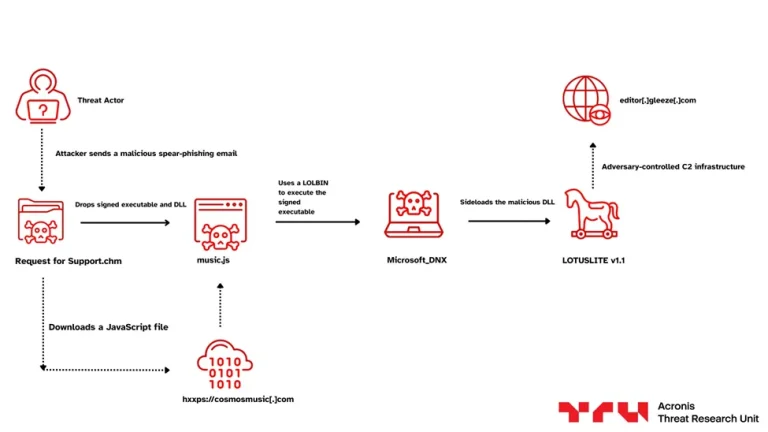
The Lotus Evolves: Mustang Panda Targets Indian Banks in a New Espionage Pivot Mustang Panda LOTUSLITE Financial Cyber-Espionage
  • Cybercriminals

The Lotus Evolves: Mustang Panda Targets Indian Banks in a New Espionage Pivot

Do Son April 23, 2026 0

Mustang Panda targets India’s financial sector with the LOTUSLITE malware. Learn how this DLL sideloading campaign bypasses defenses for cyber-espionage.

Lotus Wiper: A Destructive New Threat Strikes Venezuela’s Energy Sector Lotus Wiper Digital Sabotage G_Wagon Malware NPM Supply Chain Attack IMAPLoader malware ResolverRAT Malware Evasion
  • Malware

Lotus Wiper: A Destructive New Threat Strikes Venezuela’s Energy Sector

Do Son April 23, 2026 0

Kaspersky uncovers Lotus Wiper, a destructive malware targeting Venezuela's energy sector. Designed for pure sabotage, it leaves systems unrecoverable.

In the Wild: Information Disclosure (CVE-2026-20133) Exploited in Cisco SD-WAN Manager Cisco SD-WAN Vulnerability CVE-2026-20133 FortiGate Compromise Ivanti EPMM Zero-Day CVE-2026-1281 SmarterMail Vulnerability Storm-2603 WatchGuard Zero-Day, IKEv2 Out-of-Bounds Write Cisco Zero-Day, UAT-9686 Chinese APT FortiWeb RCE Exploitation CVE-2025-58034 VMware Zero-Day, Privilege Escalation Sitecore, remote code execution CVE-2025-53690 Windows CLFS, Privilege Escalation CVE-2024-47575 & CVE-2024-11120 CVE-2025-24983 vulnerability
  • Vulnerability Report

In the Wild: Information Disclosure (CVE-2026-20133) Exploited in Cisco SD-WAN Manager

Do Son April 23, 2026 0

Cisco warns of active exploitation for CVE-2026-20133 in Catalyst SD-WAN Manager. Unauthenticated attackers can leak OS data. Patch by April 24, 2026.
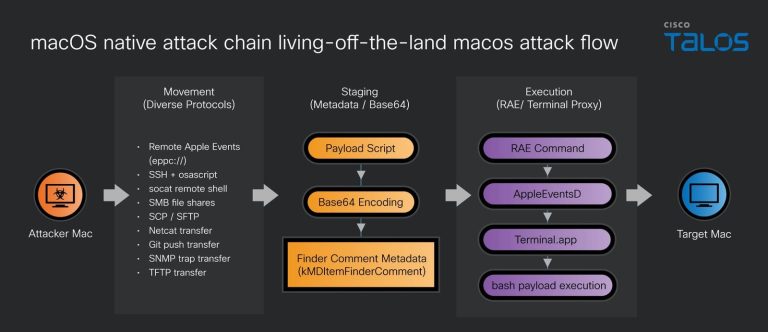
Cisco Talos Unveils “Living-off-the-Land” Tactics Threatening macOS macOS LOTL Techniques Enterprise Mac Security
  • Malware

Cisco Talos Unveils “Living-off-the-Land” Tactics Threatening macOS

Do Son April 23, 2026 0

Cisco Talos reveals how attackers use native macOS features like Spotlight and SNMP to hijack enterprise workstations. Secure your DevOps environment today.
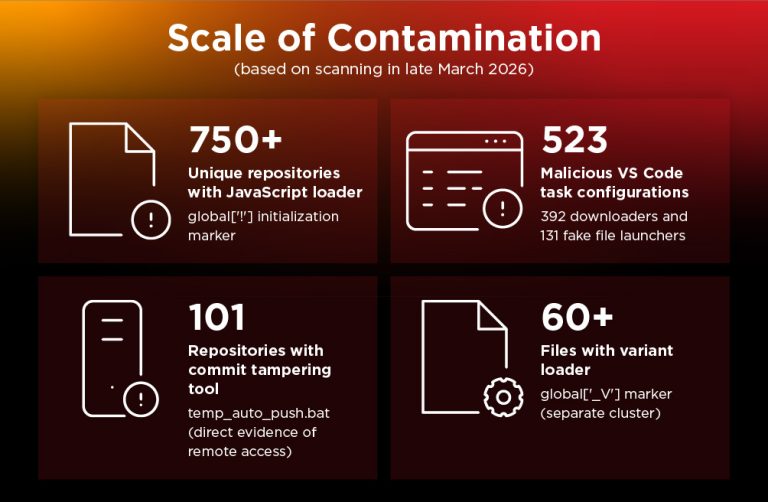
Void Dokkaebi Unmasked: The “Worm-Like” Supply Chain Threat Targeting Developers Void Dokkaebi Supply Chain Infected VS Code Tasks
  • Malware

Void Dokkaebi Unmasked: The “Worm-Like” Supply Chain Threat Targeting Developers

Do Son April 23, 2026 0

Void Dokkaebi turns developers into vectors. With 750+ infected repos and malicious VS Code tasks, this supply chain worm is hunting your CI/CD and crypto.

Linux Privilege Escalation: “Pack2TheRoot” Flaw Impacts Major Distributions Pack2TheRoot Vulnerability PackageKit Privilege Escalation
  • Linux
  • Vulnerability Report

Linux Privilege Escalation: “Pack2TheRoot” Flaw Impacts Major Distributions

Do Son April 23, 2026 0

The critical "Pack2TheRoot" flaw (CVE-2026-41651) in PackageKit gives root access on Linux. It went undetected for 12 years. Update to version 1.3.5 now!
Over 400,000 WordPress Sites at Risk as “Breeze” Plugin Zero-Day Is Exploited in the Wild WordPress RCE Breeze Plugin Vulnerability
  • Vulnerability Report

Over 400,000 WordPress Sites at Risk as “Breeze” Plugin Zero-Day Is Exploited in the Wild

Do Son April 23, 2026 0

Critical 9.8 CVSS RCE hits 400,000+ WordPress sites using the Breeze plugin. Attackers are exploiting arbitrary file uploads. Update to v2.4.5 immediately!
CVE-2026-33626: High-Severity SSRF Exploited in the Wild to Hijack AI Inference Engines CVE-2026-33626 LMDeploy SSRF
  • Vulnerability Report

CVE-2026-33626: High-Severity SSRF Exploited in the Wild to Hijack AI Inference Engines

Do Son April 23, 2026 0

CVE-2026-33626: A critical SSRF in LMDeploy exploited in under 13 hours. Learn how attackers hijack AI nodes and how to secure your inference cloud now.
TeamPCP Hijacks Checkmarx in Sprawling Supply Chain Strike Checkmarx Supply Chain Attack TeamPCP
  • Malware

TeamPCP Hijacks Checkmarx in Sprawling Supply Chain Strike

Do Son April 23, 2026 0

Checkmarx Docker images and VS Code extensions hijacked by TeamPCP to siphon cloud secrets and spread via npm. Audit your "Dune" repositories today.
Supply Chain Alert: TeamPCP Strikes Popular AI Framework Xinference Xinference Supply Chain Attack TeamPCP
  • Malware

Supply Chain Alert: TeamPCP Strikes Popular AI Framework Xinference

Do Son April 23, 2026 0

Critical supply chain attack hits Xinference (v2.6.0-2.6.2). TeamPCP’s malware siphons cloud credentials and MLOps secrets. Audit your MLOps pipeline today.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
  • CVE-2023-54413CVSS 6.1
    The WPML plugin for WordPress is vulnerable to Reflected Cross-Site Scripting via the wp_lang parameter in versions up...
    Watchtower Verified📅 Updated: Nov 4, 2026
  • CVE-2026-81648CVSS 10.0
    The CryptoPayment Gateway WordPress plugin from 1.2.1 to 1.2.2 does not apply an authorization check on one of...
    Admin intel📅 Updated: Nov 3, 2026
  • CVE-2026-119977CVSS 8.1
    WordPress Core is vulnerable to Remote Code Execution in versions 4.7 through 7.1.3. This is due to predictable,...
    CISA KEV📅 Added to KEV: Nov 3, 2026
  • CVE-2026-58115CVSS 10.0
    A vulnerability has been identified in SIMATIC IoT2050 Advanced (6ES7647-0BA00-1YA2) (All versions < V4.3.4.1 running Industrial OS with...
    Admin intel📅 Updated: Nov 2, 2026
  • CVE-2026-20051CVSS 7.4
    A vulnerability with the Ethernet VPN (EVPN) Layer 2 ingress packet processing of Cisco Nexus 3600 Platform Switches...
    Watchtower Verified📅 Updated: Nov 1, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-28336CVSS 9.9
    SolarWinds Dameware was found to be affected by a command injection vulnerability that could lead to the compromise...
    📅 Updated: Nov 4, 2026
  • CVE-2026-13594CVSS 9.1
    Zoho Corporation's ManageEngine Log360 and EventLog Analyzer versions 13062 and below are vulnerable to an issue that could...
    📅 Updated: Nov 4, 2026
  • CVE-2026-13214CVSS 9.8
    The OCPP 1.6 client in subsys/net/lib/ocpp/ocpp_j.c contains a stack buffer overflow in parse_getconfig_msg(). When handling a GetConfiguration request...
    📅 Updated: Nov 4, 2026
  • CVE-2026-121246CVSS 9.6
    Use after free in WebGL in Google Chrome on on Android prior to 157.0.8103.38 allowed a remote attacker...
    📅 Updated: Nov 4, 2026
  • CVE-2026-121247CVSS 9.6
    Buffer overflow in Dawn in Google Chrome on on Android prior to 157.0.8103.38 allowed a remote attacker to...
    📅 Updated: Nov 4, 2026
  • CVE-2026-121185CVSS 9.6
    Use after free in PictureInPicture in Google Chrome prior to 157.0.8103.38 allowed a remote attacker leveraging social engineering...
    📅 Updated: Nov 4, 2026
  • CVE-2026-121229CVSS 9.6
    Memory corruption in ANGLE in Google Chrome on on Android prior to 157.0.8103.38 allowed a remote attacker to...
    📅 Updated: Nov 4, 2026
  • CVE-2026-121156CVSS 9.6
    Buffer overflow in Dawn in Google Chrome prior to 157.0.8103.38 allowed a remote attacker to potentially execute arbitrary...
    📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.