Skip to content
November 4, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
Supply Chain Alert: TeamPCP Strikes Popular AI Framework Xinference Xinference Supply Chain Attack TeamPCP
  • Malware

Supply Chain Alert: TeamPCP Strikes Popular AI Framework Xinference

Do Son April 23, 2026 0

Critical supply chain attack hits Xinference (v2.6.0-2.6.2). TeamPCP’s malware siphons cloud credentials and MLOps secrets. Audit your MLOps pipeline today.
PureRAT Unmasked: The Stealthy, Multi-Stage “Dynamic Loader” Targeting Windows PureRAT Malware Steganography Evasion
  • Malware

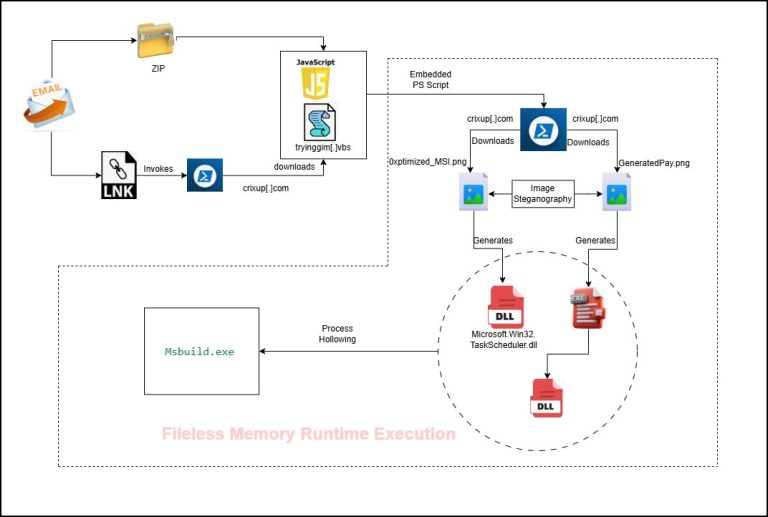
PureRAT Unmasked: The Stealthy, Multi-Stage “Dynamic Loader” Targeting Windows

Do Son April 23, 2026 0

Trellix uncovers PureRAT, a modular Trojan hiding malware in PNG images. Learn how it uses steganography and fileless delivery to bypass Windows security.

Microsoft Defender Zero-Day “BlueHammer” Hits KEV Catalog Following Researcher’s Protest BlueHammer Exploit Microsoft Defender LPE
  • Vulnerability Report

Microsoft Defender Zero-Day “BlueHammer” Hits KEV Catalog Following Researcher’s Protest

Do Son April 23, 2026 0

CISA adds BlueHammer (CVE-2026-33825) to the KEV catalog. This Microsoft Defender LPE exploit uses TOCTOU to hijack SAM databases. Patch by May 6, 2026.
ClickFix 2026: New AppleScript Malware Held macOS Users Hostage for Passwords ClickFix macOS Terminal Infostealer
  • Malware

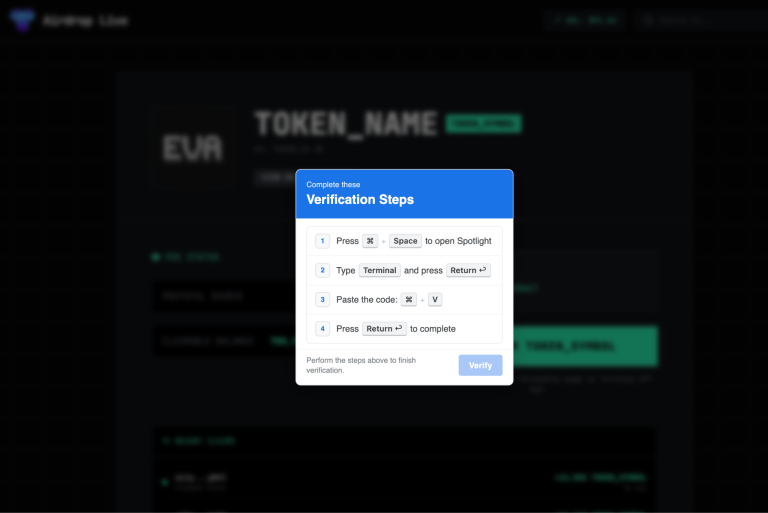
ClickFix 2026: New AppleScript Malware Held macOS Users Hostage for Passwords

Do Son April 23, 2026 0

Netskope uncovers a ClickFix macOS campaign that holds the UI hostage to steal system passwords, Keychains, and 200+ browser extensions.
Total Database Collapse: Inside the ElectricSQL CVSS 10.0 SQL Injection ElectricSQL SQL Injection PostgreSQL Tenant Isolation
  • Vulnerability Report

Total Database Collapse: Inside the ElectricSQL CVSS 10.0 SQL Injection

Do Son April 22, 2026 0

ElectricSQL reveals a critical 10.0 CVSS SQL injection (CVE-2026-40906). Attackers can hijack PostgreSQL and bypass tenant isolation. Patch to v1.5.0 now.

High-Severity PHPUnit Vulnerability Enables Remote Code Execution PHPUnit RCE Poisoned Pipeline Execution PHPUnit Vulnerability CVE-2026-24765
  • Vulnerability Report

High-Severity PHPUnit Vulnerability Enables Remote Code Execution

Do Son April 22, 2026 0

PHPUnit CVE-2026-41570 allows RCE via invisible newline injection in CI/CD pipelines. Secure your build servers—update to 12.5.22 or 13.1.6 today.

NVIDIA Fixes High-Severity Flaws in KAI Scheduler and CUDA-Q NVIDIA GPU Security CUDA-Q Vulnerability NVIDIA Apex Vulnerability AI Infrastructure Security NVIDIA Cumulus Linux CVE-2025-33179 NVIDIA Arm divestment NVIDIA DGX Spark, CVE-2025-33187 NVIDIA Isaac-GROOT, Code Injection Megatron-LM Vulnerability, AI Code Injection NVIDIA China NVIDIA GPUs, Hardware Kill Switches NVIDIA Megatron-LM, LLM Vulnerabilities NVIDIA Base Command Manager - CVE-2024-0138
  • Vulnerability Report

NVIDIA Fixes High-Severity Flaws in KAI Scheduler and CUDA-Q

Do Son April 22, 2026 0

NVIDIA patches critical flaws in KAI Scheduler and CUDA-Q. CVE-2026-24189 and CVE-2026-24177 risk data leaks and DoS. Secure your GPU workloads—update today!

GitLab Security Update: High-Severity Vulnerabilities Patched in April Release GitLab security updates, GitLab patch release, CVE-2026-6552, CVE-2026-10087, CVE-2026-7250 GitLab Security Update May 2026 GitLab XSS and DoS Vulnerabilities GitLab Security Session Hijacking GitLab Security Update, CI/CD Vulnerability GitLab DoS, Security Update bypassing SAML - CVE-2024-8312 and CVE-2024-6826
  • Vulnerability Report

GitLab Security Update: High-Severity Vulnerabilities Patched in April Release

Do Son April 22, 2026 0

GitLab fixes high-severity GraphQL CSRF and Web IDE vulnerabilities in versions 18.11.1, 18.10.4, and 18.9.6. Protect your sessions and projects—patch now!
CVE-2026-40342: CVSS 10.0 Path Traversal to RCE in Firebird Database Firebird Database RCE CVE-2026-40342
  • Vulnerability Report

CVE-2026-40342: CVSS 10.0 Path Traversal to RCE in Firebird Database

Do Son April 22, 2026 0

Critical 10.0 CVSS flaw in Firebird Database allows RCE via path traversal in the engine loader. Attackers gain root/SYSTEM privileges. Patch to 5.0.4+ now.

The $600 Billion Orbit: SpaceX and xAI Join Forces with Cursor to Command the Future of Coding Cursor SpaceX acquisition
  • Technology

The $600 Billion Orbit: SpaceX and xAI Join Forces with Cursor to Command the Future of Coding

Do Son April 22, 2026 0

SpaceX secures a $600 billion option to acquire Cursor AI. Discover how the "Vibe Coding" pioneer is leveraging xAI’s Colossus supercomputer to build the world's most powerful models.

The 271-Zero-Day Sweep: How Anthropic’s “Project Glasswing” Just Saved Firefox Anthropic Claude Lawsuit Claude Max limits, AI subscription lawsuit, Claude Pro vs Max Claude Mythos security audit Claude Identity Verification Anthropic DMCA GitHub takedown bugs Nuclear weapons Xcode, Claude AI Anthropic, Claude Sonnet 4 Claude AI, AI safety
  • Vulnerability Report

The 271-Zero-Day Sweep: How Anthropic’s “Project Glasswing” Just Saved Firefox

Do Son April 22, 2026 0

Mozilla used Anthropic’s Claude Mythos to fix 271 Firefox vulnerabilities. Discover how AI is finally flipping the script on the cybersecurity "cost asymmetry."

OpenAI Unveils ChatGPT Images 2.0 with Native Reasoning and 2K Precision ChatGPT Images 2.0 reasoning
  • Technology

OpenAI Unveils ChatGPT Images 2.0 with Native Reasoning and 2K Precision

Do Son April 22, 2026 0

OpenAI launches ChatGPT Images 2.0! Discover the new "Thinking" mode, near-perfect multilingual text rendering, and flexible 2K resolutions for all users.

TikTok’s Secret Tracker: The “Featured” Extensions Harvesting Your Data TikTok Downloader Malware Browser Extension Fingerprinting
  • Data Leak

TikTok’s Secret Tracker: The “Featured” Extensions Harvesting Your Data

Do Son April 22, 2026 0

LayerX unmasks 12 TikTok downloader extensions tracking 130,000+ users. Even "Featured" tools can be traps. Learn how this resilient malware ecosystem works.

Command Injection Vulnerability (CVE-2025-29635) Exploited in the Wild Cloudflare DDoS attacks 2 Tbps
  • Vulnerability Report

Command Injection Vulnerability (CVE-2025-29635) Exploited in the Wild

Do Son April 22, 2026 0

Akamai SIRT warns of a new Mirai campaign weaponizing EOL D-Link routers via CVE-2025-29635. Protect your network from zombie botnets—retire old hardware now.
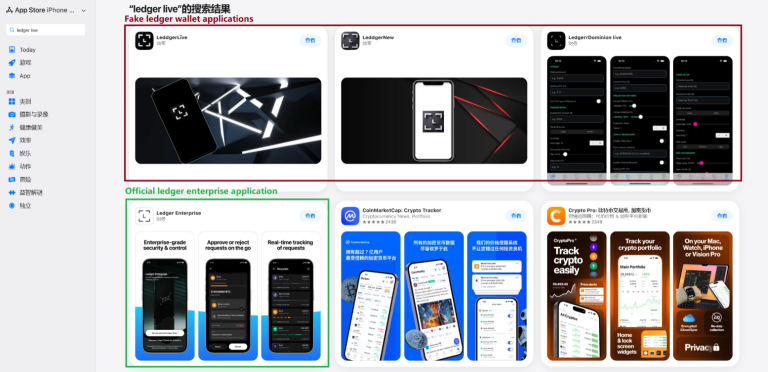
“FakeWallet” Trojan Masquerades as Crypto Wallets to Drain Assets FakeWallet Trojan Crypto Phishing
  • Malware

“FakeWallet” Trojan Masquerades as Crypto Wallets to Drain Assets

Do Son April 22, 2026 0

Kaspersky unmasks "FakeWallet," a Trojan on the Apple App Store using stubs & enterprise profiles to steal crypto seed phrases. Learn how to protect your keys.

How to Remove Video Backgrounds Online Without Editing Skills PICTURE 1
  • Technique

How to Remove Video Backgrounds Online Without Editing Skills

Do Son April 22, 2026 0
You do not get a suitable background in all videos. Recording most of them follows this process:...
Read More Read more about How to Remove Video Backgrounds Online Without Editing Skills
The Rise of Payouts King and the Resurrection of BlackBasta Payouts King Ransomware BlackBasta Successor
  • Malware

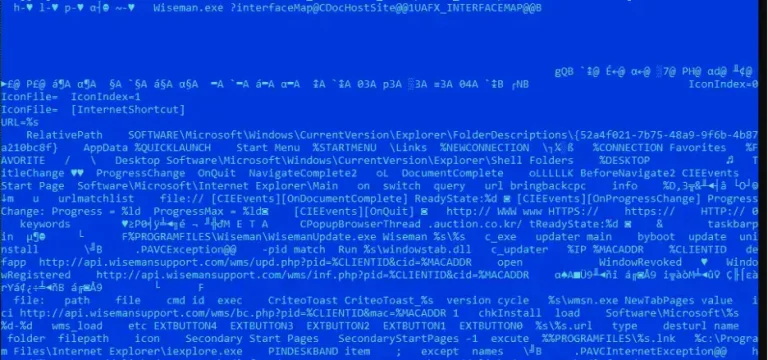
The Rise of Payouts King and the Resurrection of BlackBasta

Do Son April 22, 2026 0

Payouts King, the successor to BlackBasta, uses vishing and direct syscalls to bypass EDR and strike global targets. Learn how to defend your enterprise.
Splunk Unmasks New Malware Campaign Pairing Ghost RAT with CloverPlus Adware Ghost RAT RDP Credential Theft
  • Malware

Splunk Unmasks New Malware Campaign Pairing Ghost RAT with CloverPlus Adware

Do Son April 22, 2026 0

Splunk STRT identifies a new campaign bundling Ghost RAT with CloverPlus adware to steal RDP credentials and monetize infections. Patch your systems now!

CrowdStrike Issues Critical Alert: LogScale Vulnerability Allows Unauthenticated File Access LogScale Vulnerability Path Traversal Falcon Sensor File Deletion, CVE-2025-42701 CrowdStrike update crashes - CVE 2025-1146
  • Vulnerability Report

CrowdStrike Issues Critical Alert: LogScale Vulnerability Allows Unauthenticated File Access

Do Son April 22, 2026 0

CrowdStrike reveals a critical 9.8 CVSS flaw in LogScale Self-Hosted. Unauthenticated attackers can read arbitrary server files. Patch to v1.235.1+ now!

Critical RCE Alert: Bamboo Data Center Vulnerable to OS Command Injection CVE-2023-22518 Bamboo RCE CI/CD Supply Chain Security
  • Vulnerability Report

Critical RCE Alert: Bamboo Data Center Vulnerable to OS Command Injection

Do Son April 22, 2026 0

Atlassian Bamboo Data Center hit by critical 9.4 RCE (CVE-2026-21571). Attackers can hijack your build pipeline. Secure your supply chain—patch now!
Emergency .NET Update: Critical Data Protection Flaw Allows Authentication Forgery Windows DNS Client RCE .NET 10 Auth Bypass CVE-2026-40372
  • Vulnerability Report

Emergency .NET Update: Critical Data Protection Flaw Allows Authentication Forgery

Do Son April 22, 2026 0

Microsoft's OOB update for .NET 10 (CVE-2026-40372) hits Linux/macOS users. Authentication is at risk. Stop the bypass and rotate your keys today.

7 Critical Vulnerabilities Threaten Spring Security 7.0 cve-2024-38810 Spring Security 7.0 Vulnerabilities Authorization Bypass
  • Vulnerability Report

7 Critical Vulnerabilities Threaten Spring Security 7.0

Do Son April 22, 2026 0

Spring Security reveals 7 flaws, including a critical 9.6 CVSS vulnerability in version 7.0. From auth bypass to X.509 impersonation, upgrade to 7.0.5 now.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
  • CVE-2023-54413CVSS 6.1
    The WPML plugin for WordPress is vulnerable to Reflected Cross-Site Scripting via the wp_lang parameter in versions up...
    Watchtower Verified📅 Updated: Nov 4, 2026
  • CVE-2026-81648CVSS 10.0
    The CryptoPayment Gateway WordPress plugin from 1.2.1 to 1.2.2 does not apply an authorization check on one of...
    Admin intel📅 Updated: Nov 3, 2026
  • CVE-2026-119977CVSS 8.1
    WordPress Core is vulnerable to Remote Code Execution in versions 4.7 through 7.1.3. This is due to predictable,...
    CISA KEV📅 Added to KEV: Nov 3, 2026
  • CVE-2026-58115CVSS 10.0
    A vulnerability has been identified in SIMATIC IoT2050 Advanced (6ES7647-0BA00-1YA2) (All versions < V4.3.4.1 running Industrial OS with...
    Admin intel📅 Updated: Nov 2, 2026
  • CVE-2026-20051CVSS 7.4
    A vulnerability with the Ethernet VPN (EVPN) Layer 2 ingress packet processing of Cisco Nexus 3600 Platform Switches...
    Watchtower Verified📅 Updated: Nov 1, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-28336CVSS 9.9
    SolarWinds Dameware was found to be affected by a command injection vulnerability that could lead to the compromise...
    📅 Updated: Nov 4, 2026
  • CVE-2026-13594CVSS 9.1
    Zoho Corporation's ManageEngine Log360 and EventLog Analyzer versions 13062 and below are vulnerable to an issue that could...
    📅 Updated: Nov 4, 2026
  • CVE-2026-13214CVSS 9.8
    The OCPP 1.6 client in subsys/net/lib/ocpp/ocpp_j.c contains a stack buffer overflow in parse_getconfig_msg(). When handling a GetConfiguration request...
    📅 Updated: Nov 4, 2026
  • CVE-2026-121246CVSS 9.6
    Use after free in WebGL in Google Chrome on on Android prior to 157.0.8103.38 allowed a remote attacker...
    📅 Updated: Nov 4, 2026
  • CVE-2026-121247CVSS 9.6
    Buffer overflow in Dawn in Google Chrome on on Android prior to 157.0.8103.38 allowed a remote attacker to...
    📅 Updated: Nov 4, 2026
  • CVE-2026-121185CVSS 9.6
    Use after free in PictureInPicture in Google Chrome prior to 157.0.8103.38 allowed a remote attacker leveraging social engineering...
    📅 Updated: Nov 4, 2026
  • CVE-2026-121229CVSS 9.6
    Memory corruption in ANGLE in Google Chrome on on Android prior to 157.0.8103.38 allowed a remote attacker to...
    📅 Updated: Nov 4, 2026
  • CVE-2026-121156CVSS 9.6
    Buffer overflow in Dawn in Google Chrome prior to 157.0.8103.38 allowed a remote attacker to potentially execute arbitrary...
    📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.