Skip to content
November 4, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
Emergency .NET Update: Critical Data Protection Flaw Allows Authentication Forgery Windows DNS Client RCE .NET 10 Auth Bypass CVE-2026-40372
  • Vulnerability Report

Emergency .NET Update: Critical Data Protection Flaw Allows Authentication Forgery

Do Son April 22, 2026 0

Microsoft's OOB update for .NET 10 (CVE-2026-40372) hits Linux/macOS users. Authentication is at risk. Stop the bypass and rotate your keys today.

7 Critical Vulnerabilities Threaten Spring Security 7.0 cve-2024-38810 Spring Security 7.0 Vulnerabilities Authorization Bypass
  • Vulnerability Report

7 Critical Vulnerabilities Threaten Spring Security 7.0

Do Son April 22, 2026 0

Spring Security reveals 7 flaws, including a critical 9.6 CVSS vulnerability in version 7.0. From auth bypass to X.509 impersonation, upgrade to 7.0.5 now.
The Intel “AppDomain” Hijack: Unmasking a Sophisticated Post-Exploitation Framework phan
  • Malware

The Intel “AppDomain” Hijack: Unmasking a Sophisticated Post-Exploitation Framework

Do Son April 22, 2026 0

CYFIRMA uncovers an elite stealth framework hijacking signed Intel utilities via AppDomain Manager. It targets EMEA finance with undetectable memory-only code.

Microsoft Teams Exploited for Silent Enterprise Takeovers Teams Impersonation Administrative Abuse
  • Cybercriminals

Microsoft Teams Exploited for Silent Enterprise Takeovers

Do Son April 22, 2026 0

Microsoft warns of a Teams campaign using fake IT support to hijack workstations via Quick Assist, move laterally with WinRM, and steal data using Rclone.

Three Silent Vulnerabilities Discovered in the glibc Core glibc Security Legacy DNS Flaws glibc Vulnerabilities Linux Security Alert glibc Vulnerability CVE-2026-0861
  • Vulnerability Report

Three Silent Vulnerabilities Discovered in the glibc Core

Do Son April 21, 2026 0

glibc version 2.43 and older face heap overflows and memory leaks. Learn about CVE-2026-5358, CVE-2026-5450, and CVE-2026-5928. Update your Linux systems now.

BreachLock Named Representative Vendor in the 2026 Gartner Market Guide for Adversarial Exposure Validation BreachLock_Named_Representative_Vendor_in_2026_Gar_1776721618nJIDraNFL9
  • Press Release

BreachLock Named Representative Vendor in the 2026 Gartner Market Guide for Adversarial Exposure Validation

cybernewswire April 21, 2026 0
New York, United States, 21st April 2026, CyberNewswire
Read More Read more about BreachLock Named Representative Vendor in the 2026 Gartner Market Guide for Adversarial Exposure Validation
The Dual CVSS 10.0 RCE Flaws Threatening Spinnaker Pipelines Spinnaker RCE CVSS 10.0
  • Vulnerability Report

The Dual CVSS 10.0 RCE Flaws Threatening Spinnaker Pipelines

Do Son April 21, 2026 0

Two critical CVSS 10.0 RCE flaws in Spinnaker's Clouddriver and Echo services allow full JVM and shell access. Patch your multi-cloud pipelines immediately.

The Ungoverned Workforce: Cybersecurity Insiders Finds 92% Lack Visibility Into AI Identities Report-Post-Image-Apr-20_1776736093vYskEx4Tpb
  • Press Release

The Ungoverned Workforce: Cybersecurity Insiders Finds 92% Lack Visibility Into AI Identities

cybernewswire April 21, 2026 0
Washington D.C., USA, 21st April 2026, CyberNewswire
Read More Read more about The Ungoverned Workforce: Cybersecurity Insiders Finds 92% Lack Visibility Into AI Identities
Critical 9.8 RCE Threat to SGLang AI Infrastructure SGLang RCE Vulnerability CVE-2026-7301 Zero-Day SGLang RCE AI Infrastructure Vulnerability
  • Vulnerability Report

Critical 9.8 RCE Threat to SGLang AI Infrastructure

Do Son April 21, 2026 0

SGLang faces a critical 9.8 CVSS RCE flaw (CVE-2026-5760). Malicious GGUF models can hijack AI servers via unsandboxed Jinja2 templates. Learn how to fix it.

MOVEit WAF Critical Alert: Multi-Level RCE and WAF Bypass Vulnerabilities Disclosed CVE-2024-4358 MOVEit WAF RCE Progress ADC Vulnerabilities
  • Vulnerability Report

MOVEit WAF Critical Alert: Multi-Level RCE and WAF Bypass Vulnerabilities Disclosed

Do Son April 21, 2026 0

Progress Software warns of 5 critical MOVEit WAF & ADC flaws. RCE and WAF bypass risks allow total system hijack. Upgrade to v7.2.63.0 now to stay secure.

OVN Security Alert: Critical Heap Over-Read Flaws Risk Sensitive Data Leaks OVN Heap Over-read Network Memory Leak
  • Vulnerability Report

OVN Security Alert: Critical Heap Over-Read Flaws Risk Sensitive Data Leaks

Do Son April 21, 2026 0

OVN reveals two critical heap over-read flaws in ICMP and DHCPv6 processing. Learn how crafted packets can siphon sensitive memory and find the patch versions.
Nexcorium Botnet Turns Unpatched DVRs into DDoS Foot Soldiers Nexcorium Botnet Mirai Variant
  • Malware

Nexcorium Botnet Turns Unpatched DVRs into DDoS Foot Soldiers

Do Son April 21, 2026 0

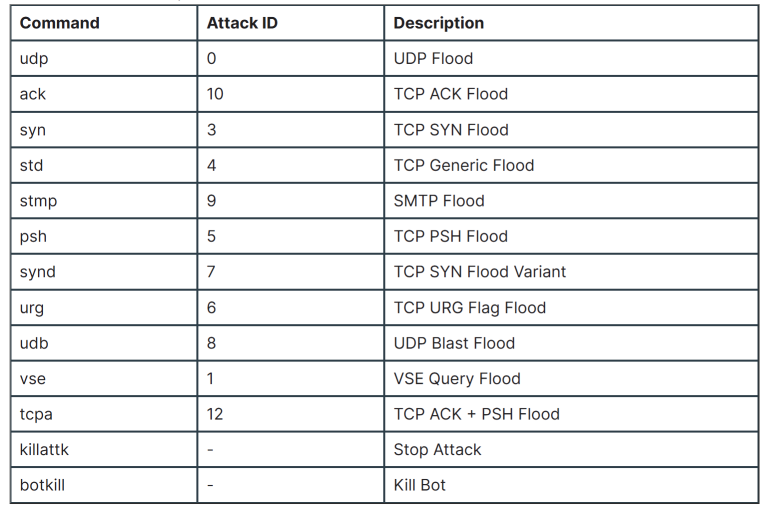
FortiGuard unmasks Nexcorium, a Mirai variant targeting DVRs via CVE-2024-3721. Secure your IoT devices against this multi-arch DDoS botnet. Patch now!

Ubuntu 26.10 Set to Deliver Linux Kernel 7.2 and Rapid Innovation Ubuntu 26.10 Stonking Stingray Ubuntu Security Alert: Three Ways to Bypass User Namespace Restrictions
  • Linux

Ubuntu 26.10 Set to Deliver Linux Kernel 7.2 and Rapid Innovation

Do Son April 21, 2026 0

Canonical unveils the "Stonking Stingray." Ubuntu 26.10 arrives Oct 15, 2026, featuring Linux Kernel 7.2 and GNOME 51. See the full development roadmap here.
The NTFS Resurrection: Linux Kernel 7.1 Delivers a Native Driver with 110% Faster Write Speeds CVE-2022-41850 Linux Kernel 7.1 NTFS driver
  • Linux

The NTFS Resurrection: Linux Kernel 7.1 Delivers a Native Driver with 110% Faster Write Speeds

Do Son April 21, 2026 0

Linux Kernel 7.1 introduces a ground-up NTFS driver rewrite. Experience up to 110% faster multi-threaded writes and 4x faster drive mounting in 2026.
SEO Poisoning & NativeAOT: Unmasking the “Kong RAT” Campaign Targeting IT Professionals Kong RAT SEO Poisoning
  • Malware

SEO Poisoning & NativeAOT: Unmasking the “Kong RAT” Campaign Targeting IT Professionals

Do Son April 21, 2026 0

Kong RAT: A year-long SEO poisoning campaign targeting developers with trojanized SSH/VPN tools and .NET NativeAOT stealth. Learn how to stay protected.

Meta Unveils a New Premium Tier to Personalize Your WhatsApp Experience WhatsApp Plus subscription
  • Technology

Meta Unveils a New Premium Tier to Personalize Your WhatsApp Experience

Do Son April 21, 2026 0

Meta is testing "WhatsApp Plus," a new subscription tier offering exclusive themes, 20 pinned chats, and animated stickers. See what’s changing in 2026.

The 100-Billion-Dollar Power Play: Anthropic and Amazon Forge an 8.5GW AI Empire Motorola Smart Feed redirect Anthropic Amazon 5GW partnership Amazon Perplexity lawsuit AWS-LC Vulnerabilities Cryptographic Bypass AWS Middle East drone strikes Amazon layoffs 2026, Amazon AI restructuring Amazon Kindle DRM Policy, Publisher Control EPUB AWS Nova Forge AI Model Customization AWS Trainium3 EC2 Trn3 UltraServer Route 53 Accelerated Recovery AWS DNS Resilience AI Browser War, Amazon Comet Amazon layoffs, cost reduction AWS outage, DynamoDB DNS AWS outage, cloud dependency AWS VPN Client, Root Privilege Escalation WSA shutdown, Amazon Appstore Amazon Wondery, Podcast Restructuring Amazon Q2 2025 Generative AI AWS Client VPN, Privilege Escalation Amazon AI, Wearable AI
  • Technology

The 100-Billion-Dollar Power Play: Anthropic and Amazon Forge an 8.5GW AI Empire

Do Son April 21, 2026 0

Anthropic and Amazon ink a historic $100B deal for 5GW of power. See how "Project Rainier" and Trainium chips are set to challenge the OpenAI-Microsoft throne.
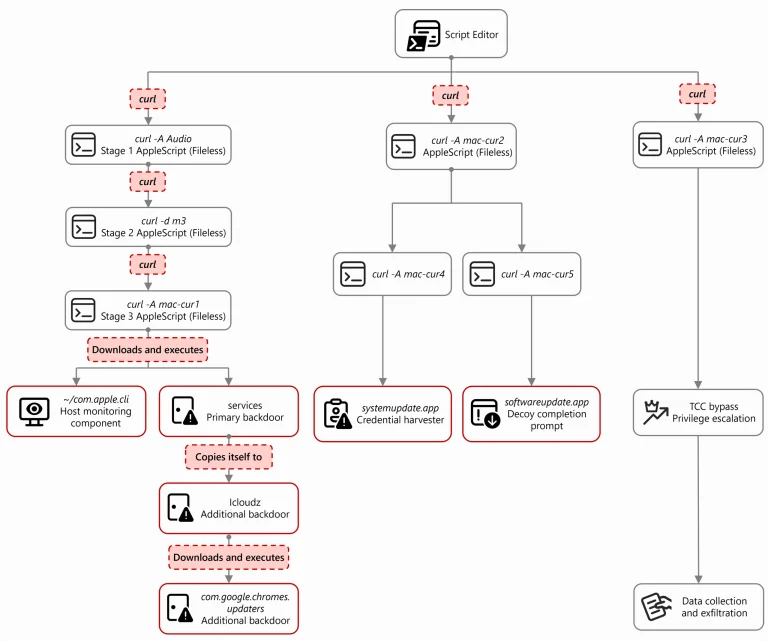
Beyond Gatekeeper: How Sapphire Sleet’s AppleScript Trap Hijacks macOS and Crypto Wallets Sapphire Sleet macOS TCC Bypass Malware
  • Malware

Beyond Gatekeeper: How Sapphire Sleet’s AppleScript Trap Hijacks macOS and Crypto Wallets

Do Son April 21, 2026 0

Microsoft uncovers Sapphire Sleet's macOS campaign. Using fake recruiters and AppleScript, they bypass TCC to steal crypto wallets, Telegram, and SSH keys.

The Negotiator Turned Traitor: Insider Betrayal in the BlackCat Ransomware Ring NATS-as-C2 Sysdig CVE-2026-33017 Langflow RCE Microsoft Phone Link Hijack CloudZ Pheno Plugin Insider Threat BlackCat (ALPHV) OFAC Sanctions DPRK IT Workers Transparent Tribe APT36 React2Shell, EtherRAT SideWinder Espionage, Netlify Phishing DDNS Abuse, C2 Infrastructure Hacking Health Club
  • Cybercriminals

The Negotiator Turned Traitor: Insider Betrayal in the BlackCat Ransomware Ring

Do Son April 21, 2026 0

Former ransomware negotiator Angelo Martino pleaded guilty to working with BlackCat to extort his own clients. $10M in luxury assets seized. Facing 20 years.
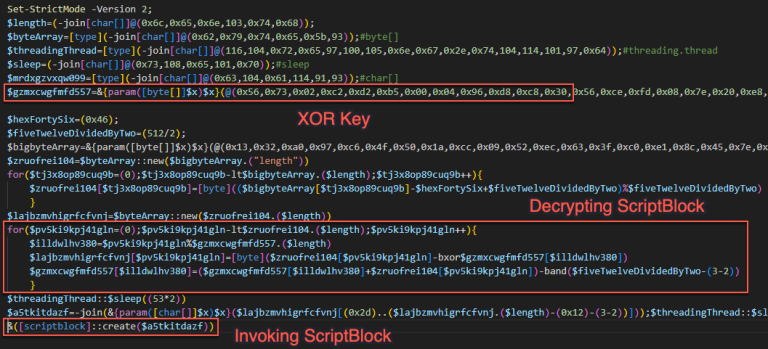
AI Hype Hijacked: How a Fake Claude Installer Blinds Windows Security Claude AI Phishing MSIX Malware
  • Malware

AI Hype Hijacked: How a Fake Claude Installer Blinds Windows Security

Do Son April 21, 2026 0

Rapid7 uncovers a fake Claude AI installer using ClickFix techniques to bypass AMSI and inject shellcode. Stay safe from this sophisticated AI-themed threat.

The Price of Privacy: Atlassian to Train AI on Jira and Confluence Data Starting August 2026 CVE-2024-21687 & CVE-2024-21686 Atlassian AI data contribution
  • Data Leak

The Price of Privacy: Atlassian to Train AI on Jira and Confluence Data Starting August 2026

Do Son April 21, 2026 0

Atlassian’s new AI policy arrives Aug 17, 2026. Learn which tiers face mandatory data collection and how to protect your Jira and Confluence content.

The Ghost in the Browser: Is Claude Desktop Clandestinely Installing a Surveillance Bridge? Claude Cowork quota update Claude Desktop native messaging bridge Anthropic Opus 4.5 Claude Excel Integration
  • Data Leak

The Ghost in the Browser: Is Claude Desktop Clandestinely Installing a Surveillance Bridge?

Do Son April 21, 2026 0

Privacy expert Alexander Hanff warns that Claude Desktop installs a "native messaging bridge" without consent, potentially bypassing browser security sandboxes.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
  • CVE-2023-54413CVSS 6.1
    The WPML plugin for WordPress is vulnerable to Reflected Cross-Site Scripting via the wp_lang parameter in versions up...
    Watchtower Verified📅 Updated: Nov 4, 2026
  • CVE-2026-81648CVSS 10.0
    The CryptoPayment Gateway WordPress plugin from 1.2.1 to 1.2.2 does not apply an authorization check on one of...
    Admin intel📅 Updated: Nov 3, 2026
  • CVE-2026-119977CVSS 8.1
    WordPress Core is vulnerable to Remote Code Execution in versions 4.7 through 7.1.3. This is due to predictable,...
    CISA KEV📅 Added to KEV: Nov 3, 2026
  • CVE-2026-58115CVSS 10.0
    A vulnerability has been identified in SIMATIC IoT2050 Advanced (6ES7647-0BA00-1YA2) (All versions < V4.3.4.1 running Industrial OS with...
    Admin intel📅 Updated: Nov 2, 2026
  • CVE-2026-20051CVSS 7.4
    A vulnerability with the Ethernet VPN (EVPN) Layer 2 ingress packet processing of Cisco Nexus 3600 Platform Switches...
    Watchtower Verified📅 Updated: Nov 1, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-114425CVSS 9.2
    SEPPmail Secure Email Gateway before 15.1.1 trusts a file path supplied in externally provided Large File Transfer attachment...
    📅 Updated: Nov 4, 2026
  • CVE-2026-114424CVSS 9.2
    SEPPmail Secure Email Gateway before 15.1.1 can evaluate attacker-influenced replacement text as Perl code in sender or recipient...
    📅 Updated: Nov 4, 2026
  • CVE-2026-28336CVSS 9.9
    SolarWinds Dameware was found to be affected by a command injection vulnerability that could lead to the compromise...
    📅 Updated: Nov 4, 2026
  • CVE-2026-13594CVSS 9.1
    Zoho Corporation's ManageEngine Log360 and EventLog Analyzer versions 13062 and below are vulnerable to an issue that could...
    📅 Updated: Nov 4, 2026
  • CVE-2026-13214CVSS 9.8
    The OCPP 1.6 client in subsys/net/lib/ocpp/ocpp_j.c contains a stack buffer overflow in parse_getconfig_msg(). When handling a GetConfiguration request...
    📅 Updated: Nov 4, 2026
  • CVE-2026-121246CVSS 9.6
    Use after free in WebGL in Google Chrome on on Android prior to 157.0.8103.38 allowed a remote attacker...
    📅 Updated: Nov 4, 2026
  • CVE-2026-121247CVSS 9.6
    Buffer overflow in Dawn in Google Chrome on on Android prior to 157.0.8103.38 allowed a remote attacker to...
    📅 Updated: Nov 4, 2026
  • CVE-2026-121185CVSS 9.6
    Use after free in PictureInPicture in Google Chrome prior to 157.0.8103.38 allowed a remote attacker leveraging social engineering...
    📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.