Skip to content
November 4, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
AI Hype Hijacked: How a Fake Claude Installer Blinds Windows Security Claude AI Phishing MSIX Malware
  • Malware

AI Hype Hijacked: How a Fake Claude Installer Blinds Windows Security

Do Son April 21, 2026 0

Rapid7 uncovers a fake Claude AI installer using ClickFix techniques to bypass AMSI and inject shellcode. Stay safe from this sophisticated AI-themed threat.

The Price of Privacy: Atlassian to Train AI on Jira and Confluence Data Starting August 2026 CVE-2024-21687 & CVE-2024-21686 Atlassian AI data contribution
  • Data Leak

The Price of Privacy: Atlassian to Train AI on Jira and Confluence Data Starting August 2026

Do Son April 21, 2026 0

Atlassian’s new AI policy arrives Aug 17, 2026. Learn which tiers face mandatory data collection and how to protect your Jira and Confluence content.

The Ghost in the Browser: Is Claude Desktop Clandestinely Installing a Surveillance Bridge? Claude Cowork quota update Claude Desktop native messaging bridge Anthropic Opus 4.5 Claude Excel Integration
  • Data Leak

The Ghost in the Browser: Is Claude Desktop Clandestinely Installing a Surveillance Bridge?

Do Son April 21, 2026 0

Privacy expert Alexander Hanff warns that Claude Desktop installs a "native messaging bridge" without consent, potentially bypassing browser security sandboxes.

Scotland Man Pleads Guilty in Massive $8 Million Crypto-Heist and Phishing Campaign Seedworm Espionage Campaign 2026 ChromElevator Stealer DLL Sideloading SIM Swapping Crypto Theft Lazarus Comebacker, Aerospace Espionage Delete PlugX Malware
  • Cybercriminals

Scotland Man Pleads Guilty in Massive $8 Million Crypto-Heist and Phishing Campaign

Do Son April 21, 2026 0

Tyler Buchanan pleads guilty in US court for an $8M cyber heist. Discover how SMS phishing and SIM swapping bypassed 2FA to drain corporate & crypto assets.

CISA Warns of Active Exploitation in Cisco, PaperCut, and Zimbra TP-Link, CISA CVE-2023-32315 CISA KEV Catalog Active Exploitation
  • Vulnerability Report

CISA Warns of Active Exploitation in Cisco, PaperCut, and Zimbra

Do Son April 21, 2026 0

CISA adds 8 vulnerabilities to the KEV Catalog, including Cisco, PaperCut, and Zimbra flaws. Actively exploited threats require immediate patching.

Cybersecurity: How to Keep NoSQL Databases Safe tech
  • Technique

Cybersecurity: How to Keep NoSQL Databases Safe

Do Son April 21, 2026 0
Cyber attacks are increasing at an alarming rate, with organizations across the globe facing more frequent and...
Read More Read more about Cybersecurity: How to Keep NoSQL Databases Safe
Progress Kemp LoadMaster Alert: Multiple RCE and WAF Bypass Flaws Patched Kemp LoadMaster flaws command injection remote execution Kemp LoadMaster Vulnerability WAF Bypass Technique Progress WhatsUp Gold Vulnerabilities
  • Vulnerability Report

Progress Kemp LoadMaster Alert: Multiple RCE and WAF Bypass Flaws Patched

Do Son April 21, 2026 0

Progress Kemp LoadMaster reveals 5 high-severity vulnerabilities, including a WAF bypass and OS command injection. Secure your ADC with the April 2026 patch.

RondoDox Botnet Hijacks Everything from IoT to Fortnite RondoDox Botnet Nanomite Anti-Debugging
  • Malware

RondoDox Botnet Hijacks Everything from IoT to Fortnite

Do Son April 21, 2026 0

BitSight unmasks RondoDox: a modular botnet using "nanomites" to dodge debuggers while hijacking 18 architectures for Monero mining and gaming DoS attacks.

ASUSTOR Issues Critical Patch: Command Injection Vulnerability Threatens ADM Users ASUSTOR ADM Vulnerability CVE-2026-6644
  • Vulnerability Report

ASUSTOR Issues Critical Patch: Command Injection Vulnerability Threatens ADM Users

Do Son April 21, 2026 0

ASUSTOR issues an urgent fix for CVE-2026-6644, a critical 9.4 CVSS flaw in ADM's VPN client allowing full NAS takeover. Patch to ADM 5.1.3.RGL1 now.

ZionSiphon: The “Defanged” Malware Aiming for the Water Supply Energy Meter RCE CVE-2025-41709 ICS Exposure, Power Grid Security CVE-2025-1393 & CVE-2024-23943
  • Malware

ZionSiphon: The “Defanged” Malware Aiming for the Water Supply

Do Son April 21, 2026 0

Darktrace uncovers ZionSiphon, a malware strain targeting water treatment via Modbus logic. Discover the new frontier of Israel-focused industrial sabotage.

Detection as Code: The Quiet Discipline Reshaping How Large Enterprises Run Their SOCs WD Discovery Vulnerability CVE-2025-30248 binary-parser Vulnerability CVE-2026-1245 H3C RCE Vulnerability CVE-2025-60262 Telenium RCE, CVE-2025-10659 Fuel station security, ICS vulnerabilities FreePBX vulnerability CVE-2024-9478 & CVE-2024-9479 SysTrack Vulnerability, Privilege Escalation
  • Technique

Detection as Code: The Quiet Discipline Reshaping How Large Enterprises Run Their SOCs

Nikolay Milyaev April 20, 2026 0
Walk into a security operations center at almost any large enterprise in 2026 and the scene is...
Read More Read more about Detection as Code: The Quiet Discipline Reshaping How Large Enterprises Run Their SOCs
Top 10 MDR Providers for Healthcare Organizations WD Discovery Vulnerability CVE-2025-30248 binary-parser Vulnerability CVE-2026-1245 H3C RCE Vulnerability CVE-2025-60262 Telenium RCE, CVE-2025-10659 Fuel station security, ICS vulnerabilities FreePBX vulnerability CVE-2024-9478 & CVE-2024-9479 SysTrack Vulnerability, Privilege Escalation
  • Technique

Top 10 MDR Providers for Healthcare Organizations

Do Son April 20, 2026 0
Healthcare organizations face some of the highest-stakes cybersecurity risks of any industry. A successful ransomware attack, credential...
Read More Read more about Top 10 MDR Providers for Healthcare Organizations
Rclone Critical Vulnerability Alert: Public PoC Released for Administrative Auth Bypass and RCE rclone command execution execute local commands Rclone RCE CVE-2026-41176
  • Vulnerability

Rclone Critical Vulnerability Alert: Public PoC Released for Administrative Auth Bypass and RCE

Do Son April 20, 2026 0

Technical details and PoC for Rclone’s critical 9.2 CVSS vulnerabilities (CVE-2026-41176/41179) are now public. Patch to version 1.73.5 to prevent RCE.

Public PoC and Technical Details Disclosed for Apache Syncope RCE Apache Syncope RCE CVE-2025-57738
  • Vulnerability Report

Public PoC and Technical Details Disclosed for Apache Syncope RCE

Do Son April 20, 2026 0

Apache Syncope CVE-2025-57738 allows root RCE via unsandboxed Groovy. Technical details and PoC are now public. Upgrade to v3.0.14 or 4.0.2 immediately.

Critical 9.4 CVSS Flaw Leaves Dolibarr ERP Open to RCE Dolibarr RCE CVE-2026-23500
  • Vulnerability Report

Critical 9.4 CVSS Flaw Leaves Dolibarr ERP Open to RCE

Do Son April 20, 2026 0

Dolibarr ERP faces a critical 9.4 CVSS RCE flaw (CVE-2026-23500) in its PDF conversion logic. Unsanitized commands allow full system takeover. Upgrade to 23.0!
Paperclip Unclipped: The 9.8 CVSS Flaw Handing Your AI Agents to the Public Paperclip RCE AI Agent Security Paperclip RCE Cross-Tenant AI Takeover
  • Vulnerability Report

Paperclip Unclipped: The 9.8 CVSS Flaw Handing Your AI Agents to the Public

Do Son April 20, 2026 0

Paperclip’s 9.8 CVSS flaw and cross-tenant leaks expose AI agents to total takeover. Learn how a simple command could compromise your entire business.

Critical 9.1 CVSS Bypass in Clerk’s Middleware Gating Clerk Middleware Bypass createRouteMatcher Vulnerability
  • Vulnerability Report

Critical 9.1 CVSS Bypass in Clerk’s Middleware Gating

Do Son April 20, 2026 0

Clerk reveals a critical 9.1 CVSS flaw in createRouteMatcher. Crafted requests can bypass middleware gating in Next.js, Nuxt, and Astro. Patch your apps now!
New “PowMix” Botnet Preys on Czech Workforce with Lure of Compliance PowMix Botnet AMSI Bypass
  • Malware

New “PowMix” Botnet Preys on Czech Workforce with Lure of Compliance

Do Son April 20, 2026 0

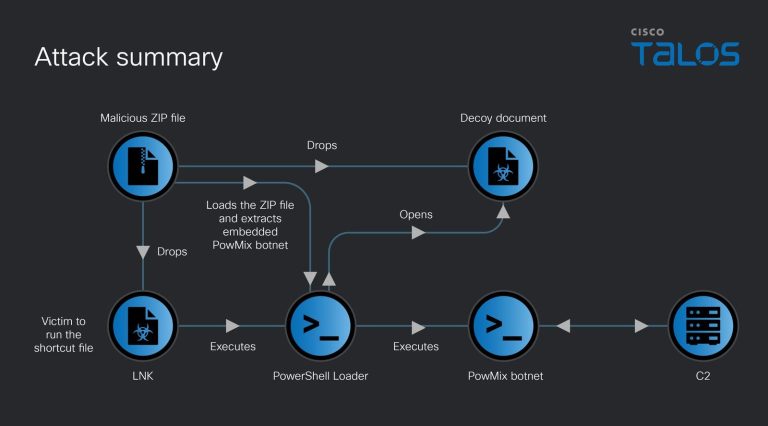
Cisco Talos uncovers PowMix, a stealthy botnet targeting Czech HR via AMSI bypass and Heroku-hosted C2. Learn how this malware evades modern EDR systems.

Cyber-Actors are “Laundering Trust” to Hijack the Global Supply Chain Load Board Phishing Signing-as-a-Service
  • Cybercriminals

Cyber-Actors are “Laundering Trust” to Hijack the Global Supply Chain

Do Son April 20, 2026 0

Proofpoint monitors a 30-day supply chain attack using "signing-as-a-service" to bypass Windows security. Protect your load boards and fleet payments now.
Critical 9.1 Auth Bypass Hits Budibase Operations Platform Budibase Authentication Bypass Regex URL Injection
  • Vulnerability Report

Critical 9.1 Auth Bypass Hits Budibase Operations Platform

Do Son April 20, 2026 0

A critical 9.1 CVSS flaw in Budibase lets attackers bypass auth via unanchored regex. Protect your user database—update to version 3.35.4 immediately.

Beyond the Glow: How iOS 27’s “Snow Leopard” Focus and Siri App Will Redefine the iPhone in 2026 iOS 27 rumors iOS 26.2.1 Update Apple Intelligence, iOS 26 iOS Notification Forwarding, EU DMA Compliance
  • Technology

Beyond the Glow: How iOS 27’s “Snow Leopard” Focus and Siri App Will Redefine the iPhone in 2026

Do Son April 20, 2026 0

iOS 27 is coming to WWDC 2026! Discover the new Siri "Search or Ask" interface, the standalone Siri App, and the long-awaited Home Screen Undo functionality.

The 32GB Ceiling Shatters: Microsoft Finally Ends the “Arbitrary” FAT32 Limit After 30 Years Windows 11 FAT32 limit Microsoft OOB update January 2026, Remote Desktop login shutdown bug Windows Edge Light PowerToys Ring Light
  • Windows

The 32GB Ceiling Shatters: Microsoft Finally Ends the “Arbitrary” FAT32 Limit After 30 Years

Do Son April 20, 2026 0

Microsoft has officially raised the FAT32 formatting limit to 2TB in Windows 11. Say goodbye to the 32GB restriction and third-party tools like Rufus.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
  • CVE-2023-54413CVSS 6.1
    The WPML plugin for WordPress is vulnerable to Reflected Cross-Site Scripting via the wp_lang parameter in versions up...
    Watchtower Verified📅 Updated: Nov 4, 2026
  • CVE-2026-81648CVSS 10.0
    The CryptoPayment Gateway WordPress plugin from 1.2.1 to 1.2.2 does not apply an authorization check on one of...
    Admin intel📅 Updated: Nov 3, 2026
  • CVE-2026-119977CVSS 8.1
    WordPress Core is vulnerable to Remote Code Execution in versions 4.7 through 7.1.3. This is due to predictable,...
    CISA KEV📅 Added to KEV: Nov 3, 2026
  • CVE-2026-58115CVSS 10.0
    A vulnerability has been identified in SIMATIC IoT2050 Advanced (6ES7647-0BA00-1YA2) (All versions < V4.3.4.1 running Industrial OS with...
    Admin intel📅 Updated: Nov 2, 2026
  • CVE-2026-20051CVSS 7.4
    A vulnerability with the Ethernet VPN (EVPN) Layer 2 ingress packet processing of Cisco Nexus 3600 Platform Switches...
    Watchtower Verified📅 Updated: Nov 1, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-114425CVSS 9.2
    SEPPmail Secure Email Gateway before 15.1.1 trusts a file path supplied in externally provided Large File Transfer attachment...
    📅 Updated: Nov 4, 2026
  • CVE-2026-114424CVSS 9.2
    SEPPmail Secure Email Gateway before 15.1.1 can evaluate attacker-influenced replacement text as Perl code in sender or recipient...
    📅 Updated: Nov 4, 2026
  • CVE-2026-28336CVSS 9.9
    SolarWinds Dameware was found to be affected by a command injection vulnerability that could lead to the compromise...
    📅 Updated: Nov 4, 2026
  • CVE-2026-13594CVSS 9.1
    Zoho Corporation's ManageEngine Log360 and EventLog Analyzer versions 13062 and below are vulnerable to an issue that could...
    📅 Updated: Nov 4, 2026
  • CVE-2026-13214CVSS 9.8
    The OCPP 1.6 client in subsys/net/lib/ocpp/ocpp_j.c contains a stack buffer overflow in parse_getconfig_msg(). When handling a GetConfiguration request...
    📅 Updated: Nov 4, 2026
  • CVE-2026-121246CVSS 9.6
    Use after free in WebGL in Google Chrome on on Android prior to 157.0.8103.38 allowed a remote attacker...
    📅 Updated: Nov 4, 2026
  • CVE-2026-121247CVSS 9.6
    Buffer overflow in Dawn in Google Chrome on on Android prior to 157.0.8103.38 allowed a remote attacker to...
    📅 Updated: Nov 4, 2026
  • CVE-2026-121185CVSS 9.6
    Use after free in PictureInPicture in Google Chrome prior to 157.0.8103.38 allowed a remote attacker leveraging social engineering...
    📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.