
 Do Son
ETH Zurich researchers unmasked "Fabricked" (CVE-2025-54510), a flaw in AMD Infinity Fabric that bypasses SEV-SNP memory isolation. Patch your firmware today!

The NSA is bypassing Trump’s federal ban to use Anthropic’s Mythos Preview. Discover how this restricted "cyber-weapon" AI is transforming U.S. intelligence.

Google launches the Android CLI for agent-centric workflows. Reduce LLM token usage by 70% and accelerate app development 3x with official AI-ready tools.

AI didn't kill the app—it became the production line. Discover how Vibe Coding fueled a 104% surge in new apps and the security risks facing Apple in 2026.

A new QR code "drainer" targets Trust Wallet users on Telegram. It exploits the ERC-20 approve mechanism to wipe USDT. Learn how to protect your assets now.

Apple’s next Mac Studio is reportedly delayed until October. Global memory shortages and a pivot toward MacBook production have left power users in the lurch.

Industry stakeholders submit the IPv8 draft to the IETF. Discover how its 64-bit address space and 100% IPv4 backward compatibility aim to end address exhaustion.

Microsoft Defender faces a critical "Red Sun" vulnerability. Learn how this zero-day exploit bypasses security to grant hackers full administrative control.

Microsoft is rebuilding the Windows 11 Start menu with WinUI 3. Codenamed "K2," this update promises near-instant speed and the ability to hide "Recommended."

Critical 9.1 CVSS flaw in FortiSandbox: Full PoC & details for CVE-2026-39808 are now public. Unauthenticated root RCE is possible. Upgrade to 4.4.9 immediately.
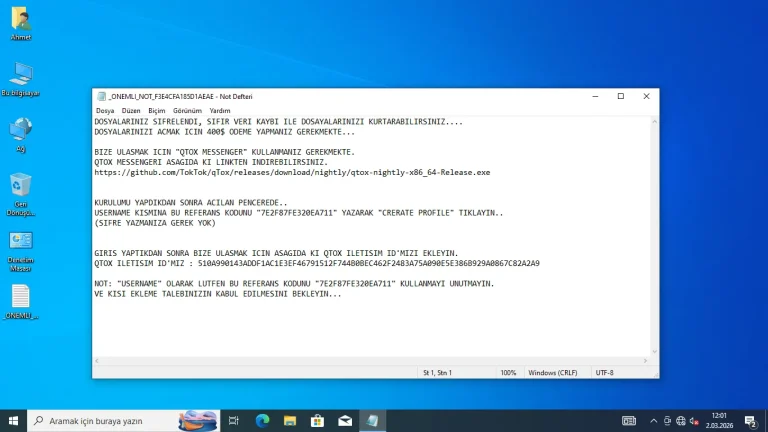
Acronis uncovers JanaWare, a persistent ransomware targeting Turkey since 2020. Discover how geofencing and polymorphism keep this threat in the shadows.
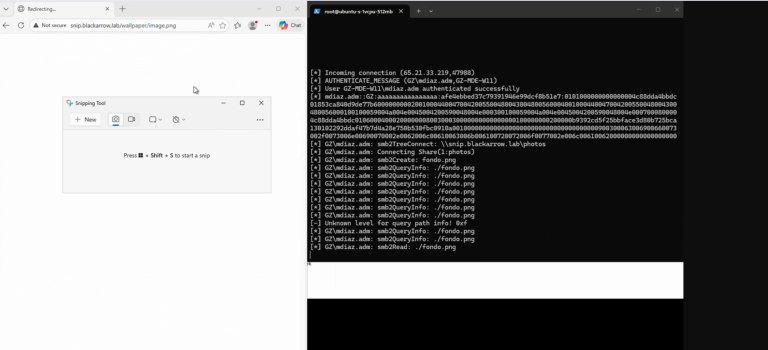
Detailed PoC and exploit code for CVE-2026-33829 are now public. See how the Windows Snipping Tool can leak NTLM hashes and how to patch the flaw.
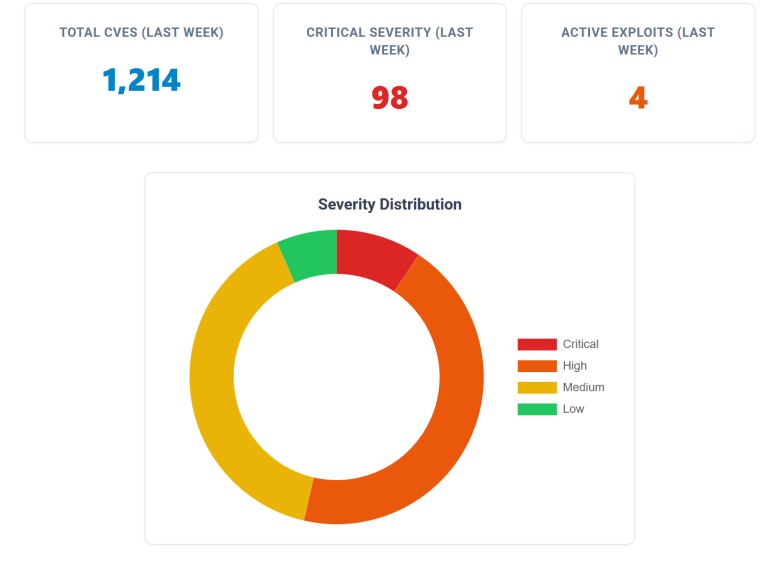
This week's digest: 1,214 new bugs, including active exploits on 2009 Excel fossils and critical 10.0 flaws in new AI/MCP infrastructure. Priority: Patch now.
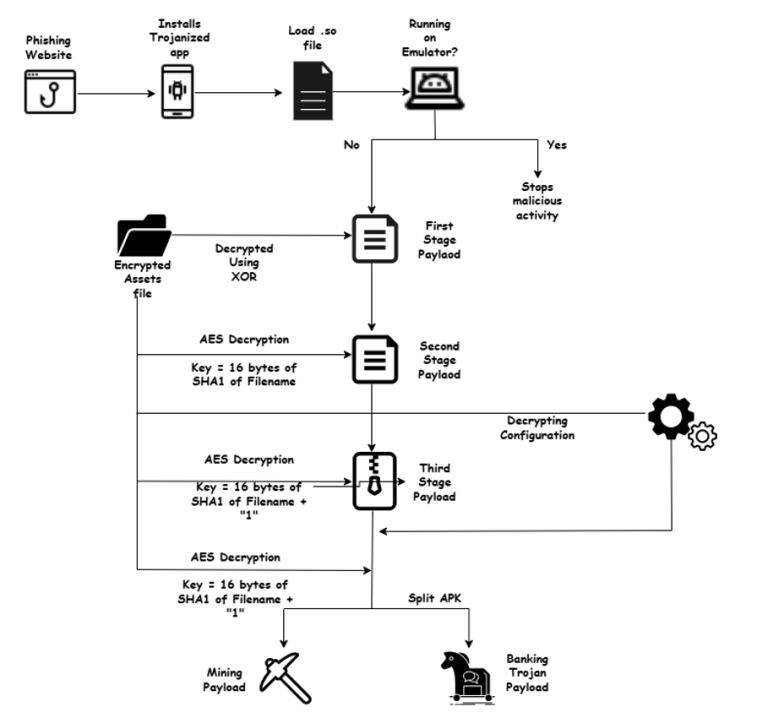
Cyble reveals MiningDropper, a modular Android threat delivering RATs and infostealers via multi-stage payloads. Protect your mobile devices now.
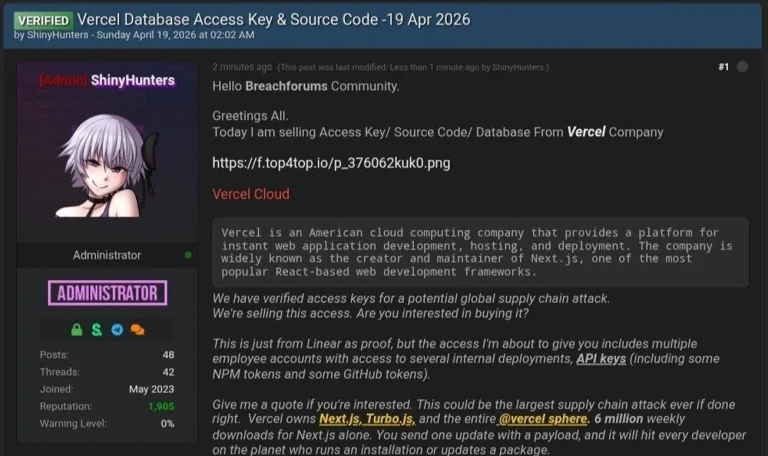
Vercel investigates a major breach by ShinyHunters. With Next.js source code and tokens at risk, developers must rotate secrets immediately. Stay updated.

Dgraph (CVE-2026-40173) leaks admin tokens in plain text via unauthenticated debug endpoints. This critical 9.4 CVSS flaw allows full DB takeover. Patch now!

North Korea's UNC1069 uses fake video calls and "ClickFix" prompts to drain crypto assets and record victims for deepfakes. Audit your meetings now!

Apache Kafka faces a critical OAUTHBEARER bypass (CVE-2026-33557) and sensitive logging leaks. Secure your data pipelines—patch to v4.1.2 or v4.2.0 today.

The EU’s 2026 DMA draft orders Google to share query, click, and ranking data with rivals. Explore how this "data handover" aims to level the search market.
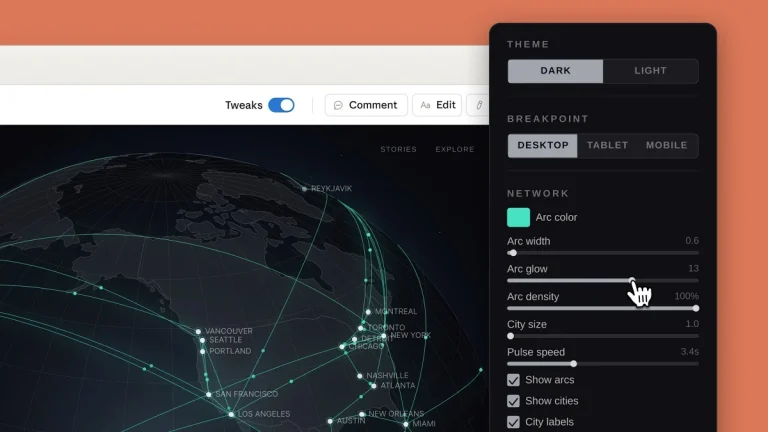
Anthropic launches Claude Design! Powered by the Opus 4.7 vision model, it creates UI prototypes and brand-aligned assets that follow your specific codebase.
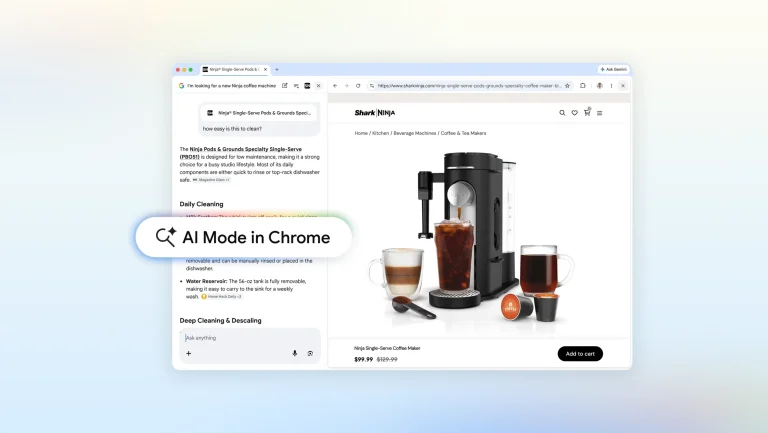
Google Chrome’s April 2026 update ends tab-switching. Use the new side-by-side AI Mode and "Plus" menu to synthesize data across tabs, PDFs, and images instantly.

AVEVA alerts on a 9.3 critical flaw in Pipeline Simulation. Unauthenticated users can hijack admin roles and alter data. Upgrade to version 2025 SP1 P01 now.