Skip to content
November 4, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
Critical 9.1 SSTI Flaws Unmasked in Thymeleaf Template Engine Thymeleaf SSTI Bypass CVE-2026-41901 Thymeleaf SSTI CVE-2026-40477
  • Vulnerability Report

Critical 9.1 SSTI Flaws Unmasked in Thymeleaf Template Engine

Do Son April 17, 2026 0

Thymeleaf 3.1.4 fixes two critical 9.1 CVSS vulnerabilities. Unauthenticated attackers can bypass security for SSTI. Audit your user input and patch today!

Critical 9.1 CVSS Flaw in Horner Automation PLCs Invites Industrial Takeovers Fortra BoKS vulnerability OS command injection, CVE-2026-9862 Altium Enterprise Server Vulnerability CVE-2026-9129 Path Traversal Patreon OAuth Vulnerability Identity Collision DRC INSIGHT Vulnerability Exam Data Hijacking Horner Automation PLC Industrial Brute Force Honeywell IQ4x Vulnerability CVE-2026-3611 DJI Romo vacuum security flaw Python Cryptography Vulnerability CVE-2026-26007 Open5GS Vulnerability CVE-2026-0622 Vivotek IP7137 Vulnerabilities CVE-2025-66049 Forcepoint DLP Vulnerability CVE-2025-14026 Cellopoint Secure Email Gateway - CVE-2024-9043
  • Vulnerability

Critical 9.1 CVSS Flaw in Horner Automation PLCs Invites Industrial Takeovers

Do Son April 17, 2026 0

Critical 9.1 CVSS flaw in Horner Automation PLCs allows unauthenticated brute force attacks. Secure your industrial systems—patch XL4, XL7, and Cscape now!
Froxlor’s CVSS 10 Flaw Turns Config Files into Persistent Backdoors Froxlor RCE Persistent Backdoor
  • Vulnerability Report

Froxlor’s CVSS 10 Flaw Turns Config Files into Persistent Backdoors

Do Son April 17, 2026 0

Froxlor faces two critical flaws, including a CVSS 10. Learn how path traversal and config injection allow persistent RCE. Patch your server management today!

Critical Command Injection Flaw Hits upKeeper Instant Privilege Access shell-quote command injection AI-Driven Vulnerabilities Q1 2026 Cyber Threats vm2 Sandbox Escape Node.js RCE upKeeper Privilege Escalation CVE-2026-2449 Pharos Controls Vulnerability Root Access Exploit Cybersecurity Vulnerability Roundup CVSS 10.0 Flaws Shadow Archives CVE-2026-0866 MS-Agent Prompt Injection CVE-2026-2256 basic-ftp Path Traversal CVE-2026-27699 telnetd Root Vulnerability CVE-1999-0073 Regression USR-W610 Vulnerabilities End-of-Life IoT Security IceWarp Security Update IceWarp Vulnerabilities Airleader Master Vulnerability CVE-2026-1358 ZLAN5143D Vulnerability CISA ICS Advisory Acronis Cyber Protect Vulnerability CVE-2025-30411 WAGO 852 Vulnerability OT Network Security SandboxJS Vulnerability Sandbox Escape (CVSS 10.0) Kubernetes Local Path Provisioner CVE-2025-62878 CISA Unresponsive Vendors Avation & RISS Vulnerabilities KiloView Vulnerability CVE-2026-1453 OpenClaw RCE vulnerability Johnson Controls Vulnerability CVE-2025-26385 SandboxJS Vulnerability CVE-2026-23830 ibaPDA Vulnerability CVE-2025-14988 Protobuf Vulnerability CVE-2026-0994 AVEVA Process Optimization Vulnerability CVE-2025-61937 ConnectWise PSA Vulnerability CVE-2026-0695 Aruba VIA Vulnerability CVE-2025-37186 aiohttp v3.13.3, Denial of Service (DoS) SmarterMail RCE, CVE-2025-52691 Airoha RACE, Headphone Jacking HPE OneView RCE CVE-2025-37164 FreePBX Auth Bypass, PBX Takeover ScreenConnect Config Flaw, Untrusted Extensions Ruby SAML Auth Bypass, XML Parser Differential Devolutions SQL Injection, Password Manager Flaw Vivotek Unauthenticated RCE, EOL IP Camera Flaw Lynx+ Critical Flaw, Unauthenticated Reset Firebox Default Credentials, CVE-2025-59396 Veeder-Root RCE, Critical ATG Flaw ArcGIS Server SQLi Watchdoc RCE, CVE-2025-58384 Delta DIALink Daikin Security Gateway, authentication bypass Frostbyte10, industrial controller security SunPower, vulnerability Ubiquiti UniFi Connect, EV Station Vulnerabilities Adobe Experience Manager, RCE Vulnerability UniFi Access, Command Injection LDAPNightmare - CVE-2025-1316
  • Vulnerability Report

Critical Command Injection Flaw Hits upKeeper Instant Privilege Access

Do Son April 17, 2026 0

Critical 9.1 flaw in upKeeper Instant Privilege allows standard users to gain LocalSystem rights via command injection. Patch to v1.6.0.4576 immediately.
Opera’s “Browser Connector” Gives ChatGPT and Claude the Power to “See” Your Tabs Opera Browser Connector
  • Technology

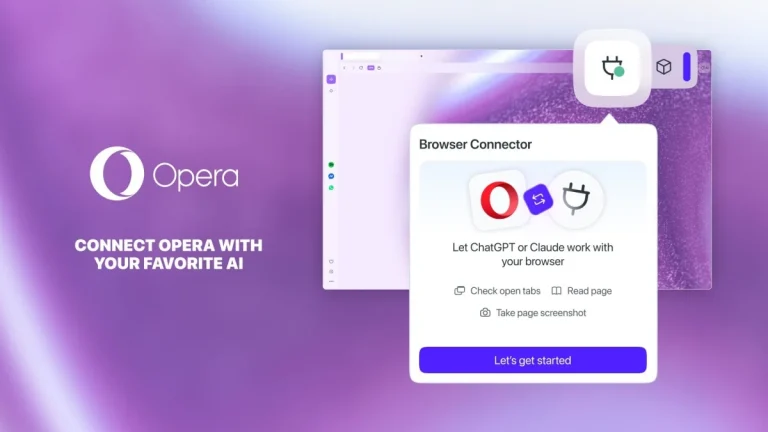
Opera’s “Browser Connector” Gives ChatGPT and Claude the Power to “See” Your Tabs

Do Son April 17, 2026 0

Opera shatters vendor lock-in with "Browser Connector." Now, ChatGPT and Claude can read your active tabs and summarize web content directly within Opera One.
Gemini vs. GenAI Fraud: How Google Blocked 8.3 Billion Malicious Ads in 2025 Google Ads Safety Report 2025
  • Malware

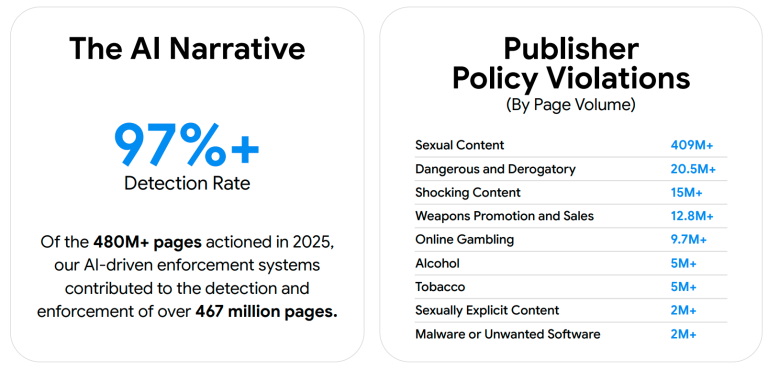
Gemini vs. GenAI Fraud: How Google Blocked 8.3 Billion Malicious Ads in 2025

Do Son April 17, 2026 0

Google’s 2025 Ads Safety Report reveals how Gemini AI intercepted 99% of bad ads and reduced false account suspensions by 80%. Read the full scale of the defense.
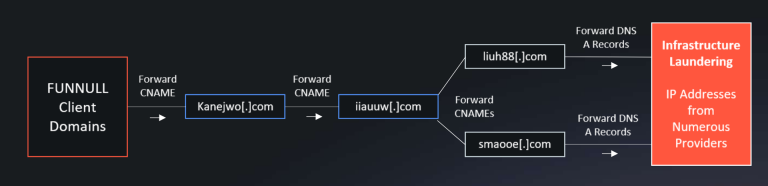
Triad Nexus’ $300M “Infrastructure Laundering” Machine Exposed Infrastructure Laundering Triad Nexus
  • Cybercriminals

Triad Nexus’ $300M “Infrastructure Laundering” Machine Exposed

Do Son April 17, 2026 0

Triad Nexus has built a $300M fraud engine using "Infrastructure Laundering" on AWS and Google. See how they use geo-fencing and CNAME chains to evade the law.
Critical Pre-Auth RCE Found in OpenAM Identity Platform OpenAM RCE CVE-2026-33439
  • Vulnerability Report

Critical Pre-Auth RCE Found in OpenAM Identity Platform

Do Son April 17, 2026 0

Critical 9.3 RCE in OpenAM (CVE-2026-33439) allows unauthenticated attackers to execute OS commands via jato.clientSession. Patch your 16.0.5 servers now!
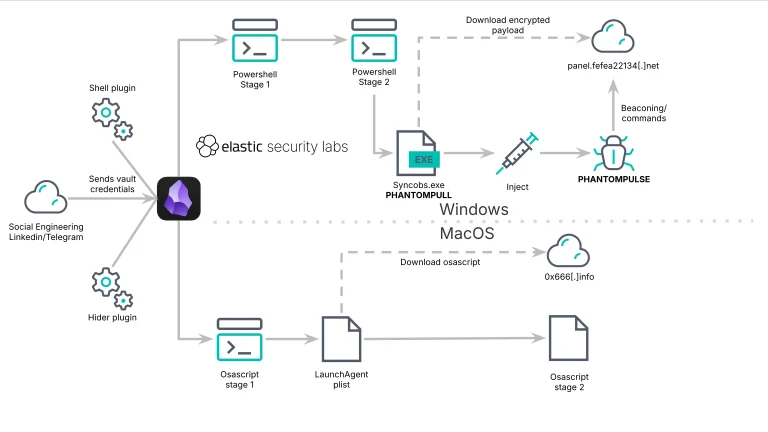
AI-Generated RAT “PHANTOMPULSE” Targets Crypto Sector via Social Engineering PHANTOMPULSE RAT Obsidian Malware Abuse
  • Malware

AI-Generated RAT “PHANTOMPULSE” Targets Crypto Sector via Social Engineering

Do Son April 17, 2026 0

Elastic uncovers PHANTOMPULSE: A novel RAT abusing Obsidian plugins and blockchain C2. Stay safe from this AI-assisted campaign targeting crypto firms.
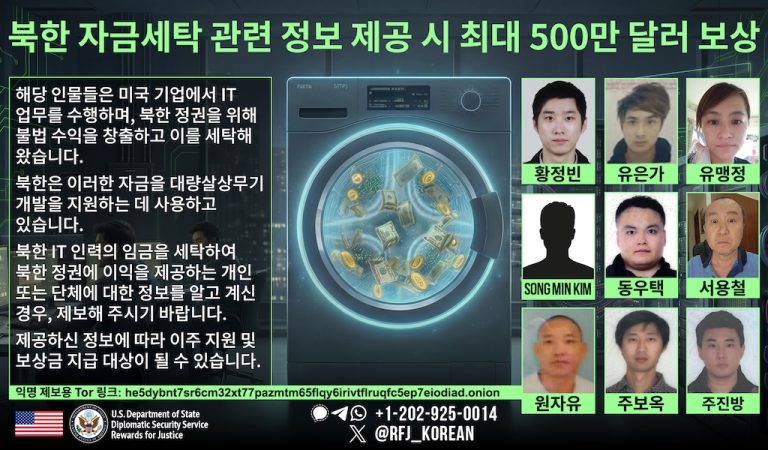
The “Laptop Farm” Fallout: Two NJ Men Sentenced for Facilitating $5M North Korean Work Scheme Laptop Farm North Korean IT Fraud
  • Cybercriminals

The “Laptop Farm” Fallout: Two NJ Men Sentenced for Facilitating $5M North Korean Work Scheme

Do Son April 17, 2026 0

Two NJ residents sentenced for running a "laptop farm" allowing North Korean workers to infiltrate 100+ U.S. companies and steal $5M in revenue.

Wormable Bugs: Microsoft April 2026 Patch Tuesday Fixes Two “Zero-Interaction” RCE Flaws Microsoft Patch Tuesday fixes disclosed zero day vulnerabilities Windows Wormable Exploit April 2026 Patch Tuesday Microsoft Patch Tuesday Zero-Day Vulnerabilities Microsoft, Patch Tuesday CVE-2025-55234 CVE-2024-43573 and CVE-2024-43572 Microsoft Patch Tuesday Security Vulnerabilities
  • Vulnerability Report

Wormable Bugs: Microsoft April 2026 Patch Tuesday Fixes Two “Zero-Interaction” RCE Flaws

Do Son April 17, 2026 0

Microsoft’s April 2026 Patch Tuesday fixes two "wormable" CVEs (9.8 & 8.1 CVSS). Secure your network against zero-click RCE and lateral movement now.
220 Million at Risk: Critical 9.4 CVSS Remote Code Execution Hits protobuf.js protobuf.js RCE Protocol Buffers Vulnerability
  • Vulnerability Report

220 Million at Risk: Critical 9.4 CVSS Remote Code Execution Hits protobuf.js

Do Son April 17, 2026 0

A critical 9.4 CVSS vulnerability in protobuf.js puts 220 million monthly downloads at risk of RCE. Patch your Node.js and browser apps to version 8.0.1+.

High-Severity SSRF Flaw Uncovered in Angular’s Server-Side Rendering Angular hostname hijacking vulnerability Angular SSRF Origin Hijacking Angular XSS Vulnerability CVE-2026-32635 Angular i18n XSS CVE-2026-27970 Angular SSR SSRF CVE-2026-27739 Angular Vulnerability CVE-2026-22610 CVE-2025-59052 Angular security Angular XSS Bypass, SVG Injection
  • Vulnerability Report

High-Severity SSRF Flaw Uncovered in Angular’s Server-Side Rendering

Do Son April 17, 2026 0

Angular patches a critical 8.7 SSRF flaw in @angular/platform-server. Attackers can hijack SSR origins via URL normalization. Patch v19, v20, or v21 now!
CISA Adds Critical Apache ActiveMQ RCE Flaw to KEV Catalog CISA active exploit catalog known exploited vulnerabilities ActiveMQ RCE CVE-2026-34197 CISA KEV Catalog Actively Exploited Vulnerabilities CISA KEV Catalog CVE-2025-37164 GeoServer XXE, CISA KEV FortiWeb SQLi, CISA KEV Critical Vulnerabilities CVE-2024-20953
  • Vulnerability Report

CISA Adds Critical Apache ActiveMQ RCE Flaw to KEV Catalog

Do Son April 17, 2026 0

CISA adds CVE-2026-34197 to KEV. Apache ActiveMQ's Jolokia bridge flaw allows RCE via remote Spring XML loading. Remediate by April 30, 2026. Patch now!

The Invisible Patch: How PolinRider Rewrites Git History to Hide North Korean Malware PolinRider Malware Git History Falsification
  • Malware

The Invisible Patch: How PolinRider Rewrites Git History to Hide North Korean Malware

Do Son April 17, 2026 0

PolinRider targets 1,900+ GitHub repos using "history-falsification" to hide malware. DPRK's Lazarus Group uses fake job tests to breach developers.
Critical Hardcoded Credential Bug Hits Nexus Repository 3 Nexus Repository Vulnerability Hardcoded Credentials
  • Vulnerability Report

Critical Hardcoded Credential Bug Hits Nexus Repository 3

Do Son April 16, 2026 0

Sonatype Nexus Repository (CVE-2026-5189) faces a critical 9.2 CVSS flaw. A hardcoded database credential grants full host access. Patch to v3.71.0 now!

Synology DSM Update Fixes High-Severity File Manipulation Flaws Synology Chat Server vulnerabilities Synology security update Synology DSM Update NAS Security Vulnerability Synology VPN Update SSL VPN Vulnerability Synology Telnet Flaw DSM Security Update Synology DSM Telnet vulnerability BeeStation Zero-Day, Pwn2Own RCE CVE-2024-11131 & CVE-2024-10442 CVE-2025-2848 Synology, NAS
  • Vulnerability Report

Synology DSM Update Fixes High-Severity File Manipulation Flaws

Do Son April 16, 2026 0

Synology patches critical DSM flaws (CVSS 8.0) allowing file manipulation and data leaks. Secure your NAS—upgrade to DSM 7.3, 7.2.2, or 7.2.1 immediately!

Critical 9.1 Bypass in OAuth2 Proxy Exposes Upstream Resources OAuth2 Proxy Auth Bypass CVE-2026-34457 OAuth2-Proxy, Authentication Bypass
  • Vulnerability Report

Critical 9.1 Bypass in OAuth2 Proxy Exposes Upstream Resources

Do Son April 16, 2026 0

A critical 9.1 CVSS flaw in OAuth2 Proxy allows unauthenticated users to bypass security via User-Agent spoofing. Secure your upstream apps—patch v7.15.2 today.
CVE-2026-38526: Critical CVSS 10 Vulnerability Discovered in Krayin CRM Krayin CRM RCE CVE-2026-38526
  • Vulnerability Report

CVE-2026-38526: Critical CVSS 10 Vulnerability Discovered in Krayin CRM

Do Son April 16, 2026 0

Krayin CRM faces a critical CVSS 10 RCE flaw in its TinyMCE upload endpoint. Authenticated users can seize server control. Patch version 2.2.x immediately!
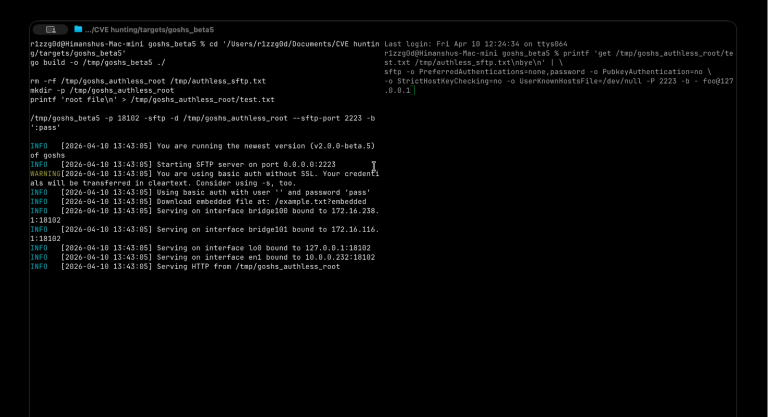
CVE-2026-40884: Critical 9.8 Bypass Hits goshs SFTP Servers goshs Authentication Bypass CVE-2026-40884
  • Vulnerability Report

CVE-2026-40884: Critical 9.8 Bypass Hits goshs SFTP Servers

Do Son April 16, 2026 0

Critical 9.8 flaw in goshs (CVE-2026-40884) allows unauthenticated SFTP access when using specific auth syntax. Secure your files—upgrade to v2.0.0-beta.6 now!

Google’s New Prepaid Credits Prevent Gemini API Key Disasters Google licenses app code Gemini API Prepaid Billing Gemini macOS Desktop Intelligence Gemini API Tier 2 upgrade Google Workspace CLI AI Google Gemini Import AI Chats Google AI Plus subscription 2026, Gemini 3 Pro vs AI Pro cost Apple, Google Gemini, Siri, Apple Intelligence, iOS 26, The Information, Fine-tuning, Private Cloud Compute, AI Partnership, Tech News 2026 Gemini Assistant transition 2026, Google Assistant sunset delay Nano Banana Pro AI Image Text Gemini Deep Research, Workspace Integration Gemini Canvas, presentation generation
  • Technology

Google’s New Prepaid Credits Prevent Gemini API Key Disasters

Do Son April 16, 2026 0

Google introduces Prepaid Credits and Project Spend Caps for the Gemini API. Protect your cloud account from leaked key overages and surprise billing cycles.

The New Lockdown: How Microsoft’s April 2026 Update Silos Remote Desktop to Kill Phishing Microsoft source code Windows RDP Security Update
  • Windows

The New Lockdown: How Microsoft’s April 2026 Update Silos Remote Desktop to Kill Phishing

Do Son April 16, 2026 0

Microsoft hardens RDP in the April 2026 update. Discover how new default isolation policies and security warnings stop malicious servers from stealing your data.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
  • CVE-2023-54413CVSS 6.1
    The WPML plugin for WordPress is vulnerable to Reflected Cross-Site Scripting via the wp_lang parameter in versions up...
    Watchtower Verified📅 Updated: Nov 4, 2026
  • CVE-2026-81648CVSS 10.0
    The CryptoPayment Gateway WordPress plugin from 1.2.1 to 1.2.2 does not apply an authorization check on one of...
    Admin intel📅 Updated: Nov 3, 2026
  • CVE-2026-119977CVSS 8.1
    WordPress Core is vulnerable to Remote Code Execution in versions 4.7 through 7.1.3. This is due to predictable,...
    CISA KEV📅 Added to KEV: Nov 3, 2026
  • CVE-2026-58115CVSS 10.0
    A vulnerability has been identified in SIMATIC IoT2050 Advanced (6ES7647-0BA00-1YA2) (All versions < V4.3.4.1 running Industrial OS with...
    Admin intel📅 Updated: Nov 2, 2026
  • CVE-2026-20051CVSS 7.4
    A vulnerability with the Ethernet VPN (EVPN) Layer 2 ingress packet processing of Cisco Nexus 3600 Platform Switches...
    Watchtower Verified📅 Updated: Nov 1, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-114425CVSS 9.2
    SEPPmail Secure Email Gateway before 15.1.1 trusts a file path supplied in externally provided Large File Transfer attachment...
    📅 Updated: Nov 4, 2026
  • CVE-2026-114424CVSS 9.2
    SEPPmail Secure Email Gateway before 15.1.1 can evaluate attacker-influenced replacement text as Perl code in sender or recipient...
    📅 Updated: Nov 4, 2026
  • CVE-2026-28336CVSS 9.9
    SolarWinds Dameware was found to be affected by a command injection vulnerability that could lead to the compromise...
    📅 Updated: Nov 4, 2026
  • CVE-2026-13594CVSS 9.1
    Zoho Corporation's ManageEngine Log360 and EventLog Analyzer versions 13062 and below are vulnerable to an issue that could...
    📅 Updated: Nov 4, 2026
  • CVE-2026-13214CVSS 9.8
    The OCPP 1.6 client in subsys/net/lib/ocpp/ocpp_j.c contains a stack buffer overflow in parse_getconfig_msg(). When handling a GetConfiguration request...
    📅 Updated: Nov 4, 2026
  • CVE-2026-121246CVSS 9.6
    Use after free in WebGL in Google Chrome on on Android prior to 157.0.8103.38 allowed a remote attacker...
    📅 Updated: Nov 4, 2026
  • CVE-2026-121247CVSS 9.6
    Buffer overflow in Dawn in Google Chrome on on Android prior to 157.0.8103.38 allowed a remote attacker to...
    📅 Updated: Nov 4, 2026
  • CVE-2026-121185CVSS 9.6
    Use after free in PictureInPicture in Google Chrome prior to 157.0.8103.38 allowed a remote attacker leveraging social engineering...
    📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.