Skip to content
October 24, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
  • Home
  • News
  • Technology
  • Riot Games Login Outage Traced to Expired SSL Certificate
  • Technology

Riot Games Login Outage Traced to Expired SSL Certificate

Do Son January 5, 2026 2 minutes read
0
Riot Games, Certificate Expiration

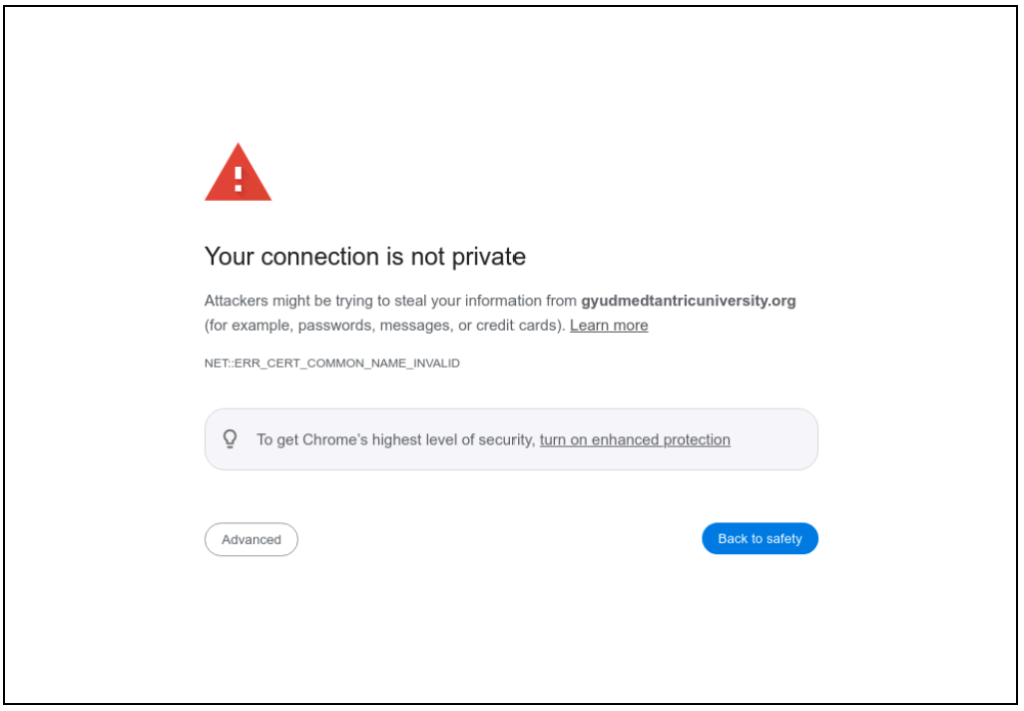
odified Chrome TLS certificate error page Source: urlscan)

Add Daily CyberSecurity as a preferred source on Google

The well-known game developer Riot Games recently suffered another widespread service disruption after failing to renew an expired digital certificate in time. The certificate in question expired on January 4, 2026, and once it lapsed, all HTTPS connections were rejected.

The immediate consequence was that the League of Legends client could no longer connect to the servers. Notably, this was not the first such incident. Back in January 2016, Riot Games similarly neglected to renew a certificate, and the replacement certificate issued at that time was set to expire in January 2026. A decade ago, Riot employees stated that the certificate would be automatically renewed and that similar issues would not recur. Ten years on, however, it appears the underlying certificate renewal problem remains unresolved.

The client certificate used by Riot is self-signed. In theory, this means Riot could issue a certificate valid for 20 years or even longer. However, longer validity periods increase the risk associated with potential private key compromise, which is why certificates are generally not issued for excessively long durations.

Forgetting to renew digital certificates is, of course, a long-standing and industry-wide problem. Google, Microsoft, and Apple have all experienced similar lapses. Apple, in fact, previously proposed shortening certificate validity periods to just 47 days—a move that ultimately gained industry support.

Under new rules set by the CA/Browser Forum, certificates issued by 2028 will have a maximum validity of only 47 days, excluding root and intermediate certificates. As a result, incidents caused by expired certificates and missed renewals are likely to become increasingly frequent.

Returning to the recent outage, a Riot Games employee reportedly became aware of the expired certificate only after seeing user complaints on Reddit. The employee then coordinated with the technical team to implement an emergency fix, and server connectivity was restored after several hours of downtime.

That said, some players may still encounter “unknown player” messages upon entering the game. Affected users are advised to update the client, restart the application, and ensure that their system clock is set to the correct time.

Related Posts:

  • Riot Games has been hacked: League of Legends and other game source codes stolen
  • League of Legends Fans Targeted: Beware the Lumma Stealer Lurking in Fake Ads!
  • DeepSeek’s Exposed Database Leaks Sensitive User Information
  • Windows Security Alert: Secure Boot Certificates Expiring in 2026, Update Now
  • CVE-2023-33975: RIOT-OS Code Execution Vulnerability

Related coverage

  • Microsoft Xbox Layoffs: Profound Corporate Restructuring
  • Metaverse Retreat: Meta Cuts 1,000 Staff to Pivot Toward AI Wearables
  • The Reasoning Car: NVIDIA Launches Alpamayo to Give AI Vehicles Human Logic
  • A New AI Header: The IETF Is Building a Standard to Label AI-Generated Content
  • Wine 3.0: Android phone can run Windows apps
  • ChatGPT for Linux Desktop Preview Launches for Ubuntu, Debian, and Fedora
Track all actively exploited CVEs →

Support Our Threat Intelligence

Find our tech and OS security coverage helpful? Support our work today and unlock a 100% ad-free reading experience!

Buy Me a Coffee Logo Buy Me a Coffee
Select your plan
Free Pro Team

Hover over a plan to see its benefits.

Get Zero-Hour Vulnerability Alerts

Critical CVEs, CVSS scores, and PoC updates — straight to your inbox every week.

We respect your inbox. Unsubscribe anytime.

SHARE
Share on FacebookShare on XShare on LinkedInShare on TelegramShare on BlueskyShare on Mastodon
Written by
@DdoS · Security Researcher

Do Son

Do Son is the Founder and Editor of SecurityOnline.info. Working in cybersecurity since 2013, he reports on vulnerabilities, malware, and emerging threats, providing timely analysis to help organizations and individuals stay ahead of evolving risks.

Tags: CA/Browser Forum cybersecurity Digital Trust https League of Legends LoL Login Fix Networking outage Riot Games SSL Certificate

Leave a Reply Cancel reply

You must be logged in to post a comment.

Search

Translation

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2020-13125CVSS 7.2
    An issue was discovered in the "Ultimate Addons for Elementor" plugin before 1.24.2 for WordPress, as exploited in...
    Watchtower Verified📅 Updated: Oct 24, 2026
  • CVE-2020-13126CVSS 9.9
    An issue was discovered in the Elementor Pro plugin before 2.9.4 for WordPress, as exploited in the wild...
    Watchtower Verified📅 Updated: Oct 24, 2026
  • CVE-2019-20180CVSS 8.0
    The TablePress plugin for WordPress is vulnerable to CSV Injection in versions up to and including 1.14 via...
    Watchtower Verified📅 Updated: Oct 24, 2026
  • CVE-2014-125133CVSS 8.7
    NativeChurch theme for WordPress before 1.6.2 contains a path traversal vulnerability that allows unauthenticated attackers to download arbitrary...
    Watchtower Verified📅 Updated: Oct 24, 2026
  • CVE-2015-20128CVSS 8.8
    FooSun DotNetCMS 1.0 and 2.0 contains an SQL injection vulnerability that allows unauthenticated attackers to manipulate MSSQL queries...
    Watchtower Verified📅 Updated: Oct 24, 2026
  • CVE-2016-20104CVSS 8.7
    EyeLock nano NXT 3.05.1193, 3.04.1108, 3.03.944, and 3.01.646 contain a path traversal vulnerability that allows unauthenticated attackers to...
    Watchtower Verified📅 Updated: Oct 24, 2026
  • CVE-2026-110447CVSS 9.2
    Collabora Online Built-in CODE Server before 26.4.303 (richdocumentscode), a Nextcloud app, allows remote code execution, as exploited in...
    CISA KEV📅 Added to KEV: Oct 23, 2026
  • CVE-2026-114625CVSS 9.9
    VeloCloud Orchestrator (VCO) on-prem has a security issue where this issue may allow a remote attacker to access...
    CISA KEV📅 Added to KEV: Oct 23, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-114820CVSS 9.1
    No description available
    📅 Updated: Oct 24, 2026
  • CVE-2026-60328CVSS 9.8
    Vulnerability in the Oracle Access Manager product of Oracle Fusion Middleware (component: Authentication Engine). Supported versions that are...
    📅 Updated: Oct 24, 2026
  • CVE-2026-60329CVSS 9.8
    Vulnerability in the Oracle Identity Manager product of Oracle Fusion Middleware (component: OIM Legacy UI). Supported versions that...
    📅 Updated: Oct 24, 2026
  • CVE-2026-60333CVSS 9.9
    Vulnerability in the Oracle Access Manager product of Oracle Fusion Middleware (component: Authentication Engine). Supported versions that are...
    📅 Updated: Oct 24, 2026
  • CVE-2026-60355CVSS 9.8
    Vulnerability in the Oracle Access Manager product of Oracle Fusion Middleware (component: Authentication Engine). Supported versions that are...
    📅 Updated: Oct 24, 2026
  • CVE-2026-60358CVSS 10.0
    Vulnerability in the Oracle Access Manager product of Oracle Fusion Middleware (component: Authentication Engine). Supported versions that are...
    📅 Updated: Oct 24, 2026
  • CVE-2026-60360CVSS 10.0
    Vulnerability in the Oracle Unified Directory product of Oracle Fusion Middleware (component: OUD Core). Supported versions that are...
    📅 Updated: Oct 24, 2026
  • CVE-2026-60361CVSS 9.9
    Vulnerability in the Oracle Unified Directory product of Oracle Fusion Middleware (component: OUD Core). Supported versions that are...
    📅 Updated: Oct 24, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.