 Do Son
Microsoft announced Windows CLAT IPv6 support in Windows 11, enabling legacy IPv4 applications to run seamlessly on modern IPv6-only enterprise networks.
Networking
TP-Link router assembly moves to the US via a Key Tronic partnership, aiming for FCC compliance and Wi-Fi 8 production in Mississippi.
Discover the controversy surrounding ICANN gTLD applications for the .lan domain. Learn how this impacts OpenWrt and local network configurations worldwide.

Cisco warns of active exploitation for CVE-2026-20133 in Catalyst SD-WAN Manager. Unauthenticated attackers can leak OS data. Patch by April 24, 2026.

Industry stakeholders submit the IPv8 draft to the IETF. Discover how its 64-bit address space and 100% IPv4 backward compatibility aim to end address exhaustion.

HPE Aruba Networking patches a critical 8.8 CVSS open redirect in its Private 5G Core. Prevent credential harvesting—update to version 1.25.3.1 immediately.

Cisco patches a critical 9.8 CVSS flaw (CVE-2026-20093) in IMC. Unauthenticated attackers can change admin passwords and seize full control. Update now!
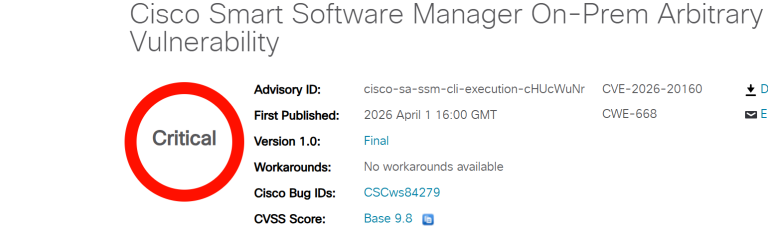
Cisco patches a critical 9.8 CVSS flaw (CVE-2026-20160) in SSM On-Prem. Unauthenticated attackers gain root access via exposed APIs. Update to 9-202601 now!

The FCC has banned the sale of foreign-made consumer routers in the US. Discover how this 2026 mandate affects brands like Netgear and your home internet costs.

OpenWrt One gets a Debian boost in Jan 2026. Use the M.2 NVMe slot to turn this "unbrickable" WiFi 6 router into a full Linux micro-server for $89.

MediaTek's Filogic 8000 brings Wi-Fi 8 to life at CES 2026. Focused on reliability and AI, it cuts latency and interference for the next-gen smart home.

Riot Games suffers a global League of Legends login outage after a digital certificate expired on Jan 4, 2026—echoing a similar lapse from 2016.

A critical UAF flaw in the Linux Traffic Control subsystem (CVE-2023-4921, CVSS 7.8) allows local privilege escalation to root. A fully detailed PoC exploit has been released.
Cisco has issued a security advisory for a high-severity DoS vulnerability (CVE-2025-20241) in its Nexus switches that could allow an unauthenticated attacker to crash a device.

A new report reveals a high-severity flaw (CVE-2025-40779) in the Kea DHCP server that allows a single crafted packet to crash the service, leading to a DoS condition.

NVIDIA has unveiled Spectrum-XGS, a new Ethernet technology that links geographically distributed data centers, allowing them to function as a single AI superfactory.

Qualcomm unveils Wi-Fi 8 (802.11bn), focusing on "Ultra High Reliability" to deliver wired-like stability, with 25% lower latency and packet loss for AI, IoT, and enterprise automation.

Linux Kernel 6.16 is officially out, bringing significant enhancements to hardware support, new drivers, and optimizations for filesystems and networking, including Intel TDX and Nvidia GPU support.

HPE officially completed its $14B acquisition of Juniper Networks, doubling its networking business to bolster AI-native and cloud-native solutions in hybrid cloud infrastructure.

The Wi-Fi Alliance is developing Wi-Fi 8 (802.11bn) for a 2028 release, focusing on ultra-reliable performance, throughput efficiency, and coordinated multi-AP operation.

Two high-severity Ubiquiti flaws allow privilege escalation via XSS in UCRM and authenticated SQL injection in UISP. Update immediately!

A high-severity flaw (CVE-2025-37100) in HPE Aruba Private 5G Core allows unauthorized access to sensitive system files. Update to 1.25.1.1 immediately!