Skip to content
November 4, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
“AccountDumpling” Hijacked Google Infrastructure to Steal 30,000 Facebook Accounts AccountDumpling Phishing Google AppSheet Abuse AI-Generated Malware PureRAT Campaign RondoDoX Botnet, Next.js React2Shell EchoGather, Paper Werewolf Salt Typhoon, Telecom Espionage BreachForums, Conor Fitzpatrick Ransomware Negotiation, DOJ Investigation MirrorFace group - Earth Kasha Emperor Dragonfly
  • Cybercriminals

“AccountDumpling” Hijacked Google Infrastructure to Steal 30,000 Facebook Accounts

Do Son May 6, 2026 0

Google AppSheet is being abused by "AccountDumpling" to steal 30,000 Facebook accounts. Learn how this Vietnamese-linked group bypasses SPF/DKIM filters.
Trojanized Tools: DAEMON Tools Supply Chain Attack Compromises Global Systems DAEMON Tools Supply Chain Attack QUIC RAT Malware
  • Malware

Trojanized Tools: DAEMON Tools Supply Chain Attack Compromises Global Systems

Do Son May 6, 2026 0

Kaspersky warns that DAEMON Tools installers (v12.5) are trojanized with the QUIC RAT. Signed binaries are being used for global espionage. Update and audit now!
Nix Vulnerability Grants Root Access via NAR Parser Overflow CVE-2026-25137 Nix Daemon Privilege Escalation CVE-2026-44028
  • Vulnerability Report

Nix Vulnerability Grants Root Access via NAR Parser Overflow

Do Son May 6, 2026 0

A critical 7.5 CVSS flaw in Nix (CVE-2026-44028) allows standard users to gain root privileges via a stack overflow. Update your Nix installation immediately!

GitOps Security Breach: Critical 9.6 CVSS Argo CD Flaw Exposes Plaintext Kubernetes Secrets Argo CD Secret Leak CVE-2026-42880 CVE-2024-28175 Argo CD DoS, Webhook Flaws
  • Vulnerability Report

GitOps Security Breach: Critical 9.6 CVSS Argo CD Flaw Exposes Plaintext Kubernetes Secrets

Do Son May 6, 2026 0

A critical 9.6 CVSS flaw in Argo CD (CVE-2026-42880) allows read-only users to extract plaintext Kubernetes secrets via Server-Side Diffs. Patch to v3.3.9 now!
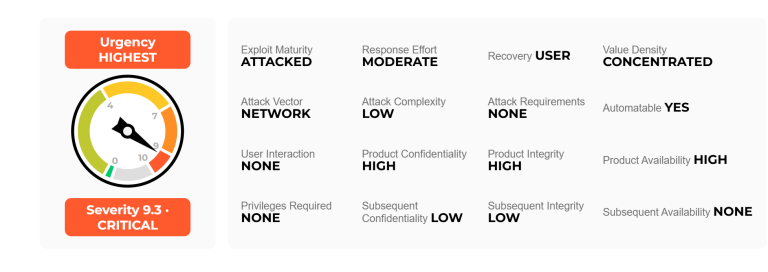
Exploited in the Wild: Critical PAN-OS Buffer Overflow Grants Root Access to Palo Alto Firewalls PAN-OS Active Exploitation CVE-2026-0300 Root RCE
  • Vulnerability Report

Exploited in the Wild: Critical PAN-OS Buffer Overflow Grants Root Access to Palo Alto Firewalls

Do Son May 6, 2026 0

Palo Alto Networks confirms CVE-2026-0300 is being exploited in the wild. The 9.3 CVSS flaw allows unauthenticated root RCE. Secure your PAN-OS firewalls now!

5.7 Million Users at Risk: Multiple 9.8 CVSS Breakthroughs Enable Remote Code Execution in vm2 Sandbox shell-quote command injection AI-Driven Vulnerabilities Q1 2026 Cyber Threats vm2 Sandbox Escape Node.js RCE upKeeper Privilege Escalation CVE-2026-2449 Pharos Controls Vulnerability Root Access Exploit Cybersecurity Vulnerability Roundup CVSS 10.0 Flaws Shadow Archives CVE-2026-0866 MS-Agent Prompt Injection CVE-2026-2256 basic-ftp Path Traversal CVE-2026-27699 telnetd Root Vulnerability CVE-1999-0073 Regression USR-W610 Vulnerabilities End-of-Life IoT Security IceWarp Security Update IceWarp Vulnerabilities Airleader Master Vulnerability CVE-2026-1358 ZLAN5143D Vulnerability CISA ICS Advisory Acronis Cyber Protect Vulnerability CVE-2025-30411 WAGO 852 Vulnerability OT Network Security SandboxJS Vulnerability Sandbox Escape (CVSS 10.0) Kubernetes Local Path Provisioner CVE-2025-62878 CISA Unresponsive Vendors Avation & RISS Vulnerabilities KiloView Vulnerability CVE-2026-1453 OpenClaw RCE vulnerability Johnson Controls Vulnerability CVE-2025-26385 SandboxJS Vulnerability CVE-2026-23830 ibaPDA Vulnerability CVE-2025-14988 Protobuf Vulnerability CVE-2026-0994 AVEVA Process Optimization Vulnerability CVE-2025-61937 ConnectWise PSA Vulnerability CVE-2026-0695 Aruba VIA Vulnerability CVE-2025-37186 aiohttp v3.13.3, Denial of Service (DoS) SmarterMail RCE, CVE-2025-52691 Airoha RACE, Headphone Jacking HPE OneView RCE CVE-2025-37164 FreePBX Auth Bypass, PBX Takeover ScreenConnect Config Flaw, Untrusted Extensions Ruby SAML Auth Bypass, XML Parser Differential Devolutions SQL Injection, Password Manager Flaw Vivotek Unauthenticated RCE, EOL IP Camera Flaw Lynx+ Critical Flaw, Unauthenticated Reset Firebox Default Credentials, CVE-2025-59396 Veeder-Root RCE, Critical ATG Flaw ArcGIS Server SQLi Watchdoc RCE, CVE-2025-58384 Delta DIALink Daikin Security Gateway, authentication bypass Frostbyte10, industrial controller security SunPower, vulnerability Ubiquiti UniFi Connect, EV Station Vulnerabilities Adobe Experience Manager, RCE Vulnerability UniFi Access, Command Injection LDAPNightmare - CVE-2025-1316
  • Vulnerability Report

5.7 Million Users at Risk: Multiple 9.8 CVSS Breakthroughs Enable Remote Code Execution in vm2 Sandbox

Do Son May 6, 2026 0

Critical 9.8 CVSS flaws in vm2 affect 5.7M monthly users, allowing RCE via WASM and Promise bypasses. Upgrade to vm2 v3.11.0 immediately to secure your host.

Critical Flaws in Apache Thrift Threaten Multi-Language Apache Thrift Vulnerabilities Cross-Language Service Security Apache Thrift Security RPC Vulnerability
  • Vulnerability Report

Critical Flaws in Apache Thrift Threaten Multi-Language

Do Son May 6, 2026 0

Apache Thrift v0.23.0 fixes critical Rust DoS, Java MitM, and Node.js path traversal flaws. Secure your cross-language microservices and upgrade immediately!

LuxSci Launches Enterprise-Grade HIPAA-Compliant Email Security for Mid-Sized Healthcare Organizations LuxSci_Secure_Email_Mid-Sized_PR_1777922928HSMMEp3uoy
  • Press Release

LuxSci Launches Enterprise-Grade HIPAA-Compliant Email Security for Mid-Sized Healthcare Organizations

cybernewswire May 5, 2026 0
Cambridge, MA, 5th May 2026, CyberNewswire
Read More Read more about LuxSci Launches Enterprise-Grade HIPAA-Compliant Email Security for Mid-Sized Healthcare Organizations
Conti Ransomware Leader Sentenced for Pediatric Extortion and Global Terror Conti ransomware guilty plea, ransomware attacks Deniss Zolotarjovs Sentencing Karakurt Ransomware Leader
  • Cybercriminals

Conti Ransomware Leader Sentenced for Pediatric Extortion and Global Terror

Do Son May 5, 2026 0

Ransomware "closer" Deniss Zolotarjovs is sentenced to 102 months for extorting 50+ firms. See how the Conti-linked "Destroyer" was caught and prosecuted.

Rancher Flaw Allows Malicious Plugins to Hijack Kubernetes Clusters Rancher security flaws cluster privilege escalation Rancher Path Traversal CVE-2026-25705 Rancher Vulnerabilities, SAML Phishing CVE-2024-22036 Rancher, vulnerability
  • Vulnerability Report

Rancher Flaw Allows Malicious Plugins to Hijack Kubernetes Clusters

Do Son May 5, 2026 0

SUSE Rancher v2.14.1 fixes an 8.4 CVSS path traversal flaw (CVE-2026-25705) in UI Extensions. Prevent binary hijacking and host access—upgrade immediately!

Root RCE and Authentication Lockout Bypass: Public PoC Released for Critical OPNsense Firewall Vulnerabilities OPNsense Root RCE PoC Exploit Disclosed
  • Vulnerability Report

Root RCE and Authentication Lockout Bypass: Public PoC Released for Critical OPNsense Firewall Vulnerabilities

Do Son May 5, 2026 0

Public PoC exploit released for OPNsense! A critical root-level RCE and lockout bypass allow total firewall takeover. Upgrade to OPNsense 26.1.7 immediately.
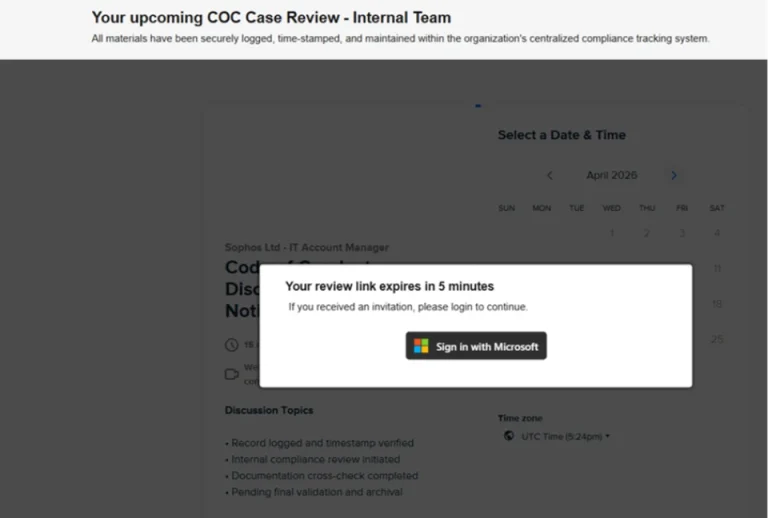
The Compliance Trap: How a 13,000-Org Phishing Wave Bypasses MFA via AiTM Proxying AiTM Phishing Campaign Microsoft MFA Bypass
  • Cybercriminals

The Compliance Trap: How a 13,000-Org Phishing Wave Bypasses MFA via AiTM Proxying

Do Son May 5, 2026 0

Microsoft warns of a massive AiTM phishing campaign targeting 13,000+ orgs. Using fake disciplinary lures, attackers bypass MFA to hijack active sessions.

Microsoft Defender Flaw Erased DigiCert Root Certificates and Paralyzed Windows Systems Microsoft Defender DigiCert false positive
  • Malware

Microsoft Defender Flaw Erased DigiCert Root Certificates and Paralyzed Windows Systems

Do Son May 5, 2026 0

Microsoft Defender erroneously flagged DigiCert root certificates as "Cerdigicert" malware. Discover the fix and how to restore your system's trusted root store.

The $1.5 Million Truce: Elon Musk Settles SEC Lawsuit Over “Hidden” Twitter Stake and Acquisition Gamesmanship Elon Musk SEC settlement X bootloader verification X Creator Revenue Sharing suspension X Platform, AI Training X open-source algorithm 2026, Elon Musk ad transparency
  • Technology

The $1.5 Million Truce: Elon Musk Settles SEC Lawsuit Over “Hidden” Twitter Stake and Acquisition Gamesmanship

Do Son May 5, 2026 0

Elon Musk settles with the SEC for $1.5M over his delayed 2022 Twitter stake disclosure. The record-breaking fine ends years of legal "harassment" and litigation.

Scammers Weaponize Amazon SES to Bypass Security Amazon SES Phishing AWS IAM Credential Leak
  • Cybercriminals

Scammers Weaponize Amazon SES to Bypass Security

Do Son May 5, 2026 0

Scammers are leveraging Amazon SES and leaked IAM keys to bypass security filters. Learn how to protect your organization from this high-trust phishing surge.
Apple Unveils End-to-End Encryption for iPhone-to-Android RCS Messaging iPhone 18 Pro leak from the Tata Electronics data breach exposing Apple supplier lists, components, and drop-test photos RCS End-to-End Encryption
  • Technology

Apple Unveils End-to-End Encryption for iPhone-to-Android RCS Messaging

Do Son May 5, 2026 0

Privacy without borders: Apple’s iOS 26.5 beta finally brings End-to-End Encryption to RCS. enjoy iMessage-level security when texting Android users.

The New Wall: How the FCC’s Ban on Chinese Testing Labs will Inflate Flagship Phone Prices and Delay Launches FCC Chinese lab ban iPhone NATO certification iPhone 18 Pro Deep Red iOS 27 Snow Leopard update 2026 smartphone memory shortage, IDC mobile market forecast iPhone Satellite Natural Usage iPhone 17 Speaker Issue, USB-C Static iPhone 17 Pro, MagSafe Scratches iPhone 17 Pro, professional filmmaking
  • Technology

The New Wall: How the FCC’s Ban on Chinese Testing Labs will Inflate Flagship Phone Prices and Delay Launches

Do Son May 5, 2026 0

The FCC is banning equipment testing data from China. Discover how this "security" mandate will force Apple, Google, and Samsung to hike prices and delay US launches.
The N-Day Nightmare: How SHADOW-EARTH-053 Breaches Governments Using “Old” Exploits SHADOW-EARTH-053 ShadowPad Espionage
  • Cyber Security
  • Vulnerability Report

The N-Day Nightmare: How SHADOW-EARTH-053 Breaches Governments Using “Old” Exploits

Do Son May 5, 2026 0

SHADOW-EARTH-053 is breaching governments and NATO using old ProxyLogon flaws and ShadowPad. Learn how this China-aligned group stays hidden via registry loading.

Wall Street’s VIP Mandate: Why OpenAI and Anthropic are Using Private Equity to Force AI into the “Real Economy” OpenAI confidential IPO filing OpenAI code signing certificate rotation AI private equity joint ventures OpenAI Axios Supply Chain Attack OpenAI Promptfoo acquisition OpenAI military resignation ChatGPT Plus military fraud OpenAI smart speaker Jony Ive OpenAI Frontier platform ChatGPT AI age prediction 2026, OpenAI Persona age verification Sarah Friar OpenAI infrastructure, AI Scaling Law revenue OpenAI Gumdrop AI pen, Jony Ive OpenAI hardware 2027 OpenAI New CRO, Denise Dresser Monetization Strategy OpenAI Competitive Pressure Gemini 3 Overtake OpenAI Infrastructure, AI Closed Loop Economy
  • Technology

Wall Street’s VIP Mandate: Why OpenAI and Anthropic are Using Private Equity to Force AI into the “Real Economy”

Do Son May 5, 2026 0

OpenAI and Anthropic are pivoting from API sales to $10B private equity alliances. Discover how Wall Street is becoming the ultimate AI system integrator.

The AI-Powered Cybercrime Factory: Unmasking the Bluekit “All-in-One” Phishing Revolution Bluekit Phishing AI-Powered Phishing
  • Cybercriminals

The AI-Powered Cybercrime Factory: Unmasking the Bluekit “All-in-One” Phishing Revolution

Do Son May 5, 2026 0

Varonis uncovers Bluekit, a new phishing-as-a-service kit using AI and 40+ templates to automate session hijacking and credential theft. See how it works.

Critical 9.8 CVSS Flaws in Qualcomm Chipsets Enable Remote Takeover Qualcomm Security Bulletin CVE-2026-25254 RCE Qualcomm Diversification, Mobile Chip Competition CVE-2023-33025
  • Vulnerability Report

Critical 9.8 CVSS Flaws in Qualcomm Chipsets Enable Remote Takeover

Do Son May 5, 2026 0

Qualcomm’s May 2026 bulletin reveals critical 9.8 CVSS flaws in Software Center & Bootloaders. Remote RCE and memory corruption affect millions of devices.

Gremlin Injection Flaw in Apache Atlas Exposes Enterprise Data CVE-2024-46910 Apache Atlas Vulnerability Gremlin Code Injection
  • Vulnerability Report

Gremlin Injection Flaw in Apache Atlas Exposes Enterprise Data

Do Son May 5, 2026 0

A critical injection flaw (CVE-2026-40563) in Apache Atlas lets attackers manipulate Gremlin logic to extract restricted enterprise data. Patch to v2.5.0!

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
  • CVE-2023-54413CVSS 6.1
    The WPML plugin for WordPress is vulnerable to Reflected Cross-Site Scripting via the wp_lang parameter in versions up...
    Watchtower Verified📅 Updated: Nov 4, 2026
  • CVE-2026-81648CVSS 10.0
    The CryptoPayment Gateway WordPress plugin from 1.2.1 to 1.2.2 does not apply an authorization check on one of...
    Admin intel📅 Updated: Nov 3, 2026
  • CVE-2026-119977CVSS 8.1
    WordPress Core is vulnerable to Remote Code Execution in versions 4.7 through 7.1.3. This is due to predictable,...
    CISA KEV📅 Added to KEV: Nov 3, 2026
  • CVE-2026-58115CVSS 10.0
    A vulnerability has been identified in SIMATIC IoT2050 Advanced (6ES7647-0BA00-1YA2) (All versions < V4.3.4.1 running Industrial OS with...
    Admin intel📅 Updated: Nov 2, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-121952CVSS 9.3
    FreeRDP before 3.32.2 has an out-of-bounds write in the proxy because rdp_read_bitmap_cache_v2_capability_set rejects only numCellCaches values above 5,...
    📅 Updated: Nov 4, 2026
  • CVE-2026-121953CVSS 9.3
    FreeRDP before 3.32.2 has a use-after-free in the client's rdpgfx dynamic virtual channel: a duplicate-name channel with a...
    📅 Updated: Nov 4, 2026
  • CVE-2026-86574CVSS 9.8
    Heap-based Buffer Overflow Vulnerability in JP1/Base. This issue affects JP1/Base: from 11-00 before 12-50-54.
    📅 Updated: Nov 4, 2026
  • CVE-2026-86575CVSS 9.4
    Stack-based Buffer Overflow Vulnerability in JP1 Products. This issue affects JP1/Integrated Management 3 - Manager: from 13-00 before...
    📅 Updated: Nov 4, 2026
  • CVE-2026-86576CVSS 9.4
    Heap-based Buffer Overflow Vulnerability in JP1 Products. This issue affects JP1/Integrated Management 3 - Manager: from 13-00 before...
    📅 Updated: Nov 4, 2026
  • CVE-2026-86577CVSS 9.4
    Out-of-bounds Write Vulnerability in JP1 Products. This issue affects JP1/Integrated Management 3 - Manager: from 13-00 before 13-50-31;...
    📅 Updated: Nov 4, 2026
  • CVE-2026-84539CVSS 9.8
    An out-of-bounds write issue was addressed with improved bounds checking. This issue is fixed in macOS Golden Gate...
    📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.