 Do Son
Google releases Gemini for Mac. With Option+Space shortcuts, screen awareness, and Nano Banana 2 integration, it’s a direct challenge to Apple Intelligence.
Cisco alerts on a critical 9.9 CVSS flaw in ISE. Even "Read-Only" admins can escalate to root and trigger a total network lockout. Patch immediately.
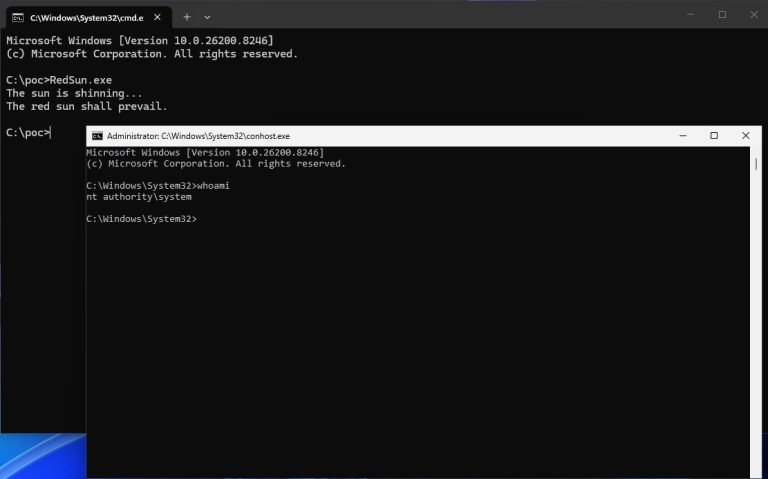
Windows Defender "RedSun" zero-day revealed! This unpatched EoP flaw turns antivirus into a delivery tool for malicious payloads. PoC is public—patch now!
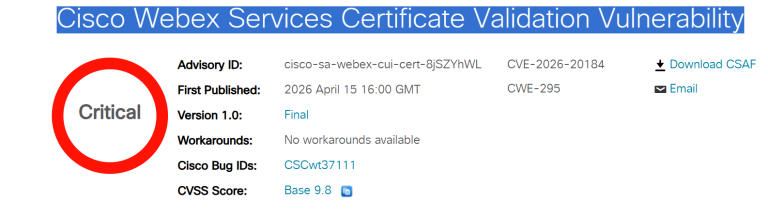
Cisco Webex CVE-2026-20184 allows unauthenticated user impersonation via SSO flaw. Fix requires a manual certificate update in Control Hub. Act now!

Splunk fixes CVE-2026-20204, a critical RCE flaw where low-privilege users can hijack servers via temp files. Patch Enterprise and Cloud instances now!
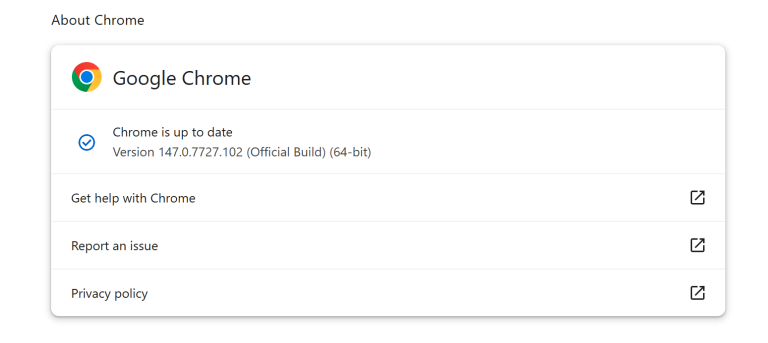
Google patches 31 Chrome flaws, including a $90K graphics engine bug. Update to version 147.0.7727.101 now to block critical sandbox escapes and RCE risks.
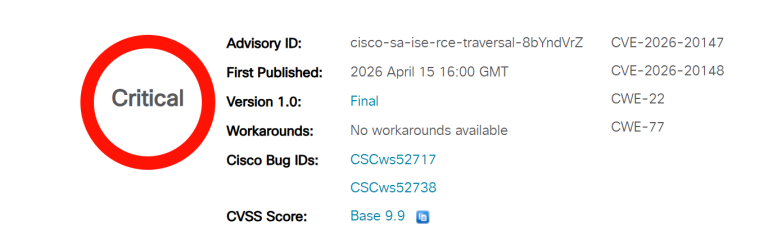
Cisco warns of a critical 9.1 RCE flaw in Identity Services Engine (ISE). Attackers can escalate to root access—apply official security patches now!
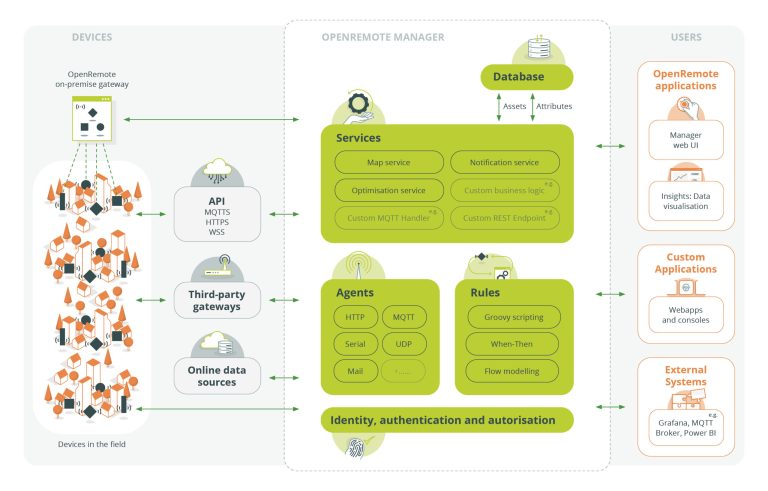
OpenRemote CVE-2026-39842 is a critical CVSS 10 flaw allowing RCE via JavaScript and Groovy injection. Secure your IoT assets—upgrade to v1.22.0 now!
Vendure Core faces a critical 9.1 SQL Injection via the Shop API. Unauthenticated attackers can hijack databases—upgrade to 3.6.2, 3.5.7, or 2.3.4 now!
AVideo’s YPTSocket plugin faces a critical CVSS 10 vulnerability. Unauthenticated attackers can hijack every active session at once. No patch is available.

MinIO faces a critical 8.8 CVSS vulnerability allowing unauthenticated object writes by bypassing signature checks. Secure your AI/ML data—upgrade now!
Proofpoint warns that 10% of M365 account takeovers use malicious mailbox rules to steal data and hide alerts. Secure your cloud identity—check your rules!
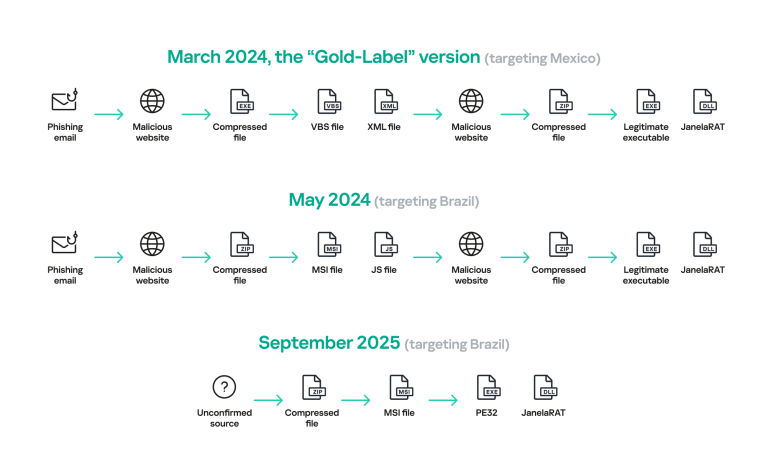
JanelaRAT targets banking users in Brazil and Mexico using window monitoring and fake updates. Learn how this 2026 threat bypasses MFA to hijack sessions.
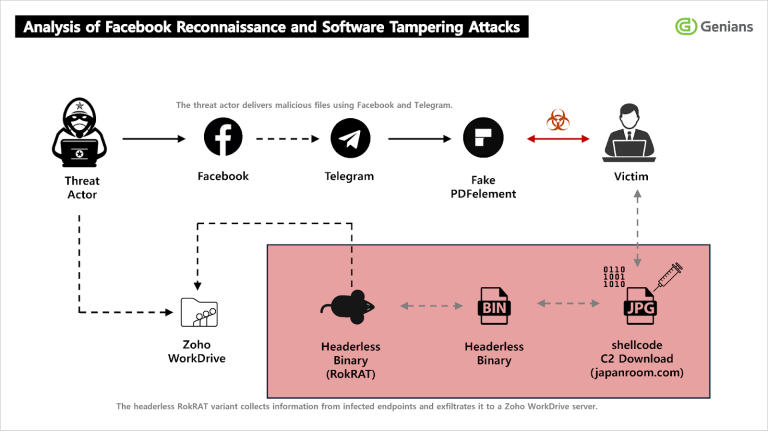
APT37 pivots to Facebook social engineering, using Wondershare PDFelement "code caves" to deploy RokRAT. Learn how they bypass EDR with memory-only payloads.
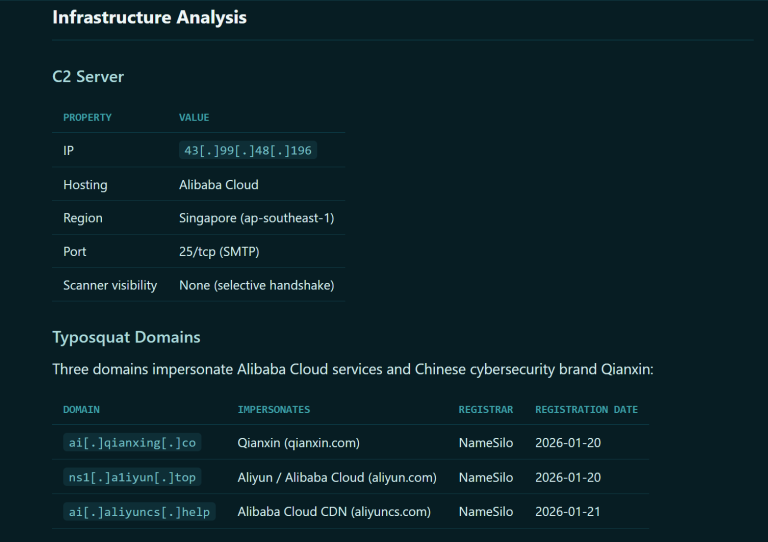
APT41's new zero-detection ELF backdoor uses SMTP (Port 25) to hijack Linux cloud workloads invisibly. Secure your credentials—audit your SMTP traffic today.

North Korea’s "graphalgo" campaign uses fake job interviews and real Florida LLCs to infect developers. Learn how to spot this sophisticated state-sponsored trap.
The FBI and Indonesia dismantle W3LL, a $20M phishing kit that bypassed MFA and hijacked live sessions. Learn about the takedown of this MaaS powerhouse.
Adobe patches critical RCE and security bypass flaws in ColdFusion 2023 & 2025. Protect your enterprise servers from takeover—update to the latest version now.

Fortinet issues a critical 9.1 CVSS alert for FortiSandbox. Unauthenticated auth bypass and command injection risks. Patch to 5.0.6 or 4.4.9 immediately.
CISA adds Microsoft SharePoint spoofing (CVE-2026-32201) and legacy Office RCE (CVE-2009-0238) to its KEV Catalog. Remediation deadline: April 28, 2026.

Fastify (25M+ downloads) reveals CVE-2026-33806. A public PoC exploit shows how a single space bypasses schema validation. Upgrade to v5.8.5 now to stay safe.
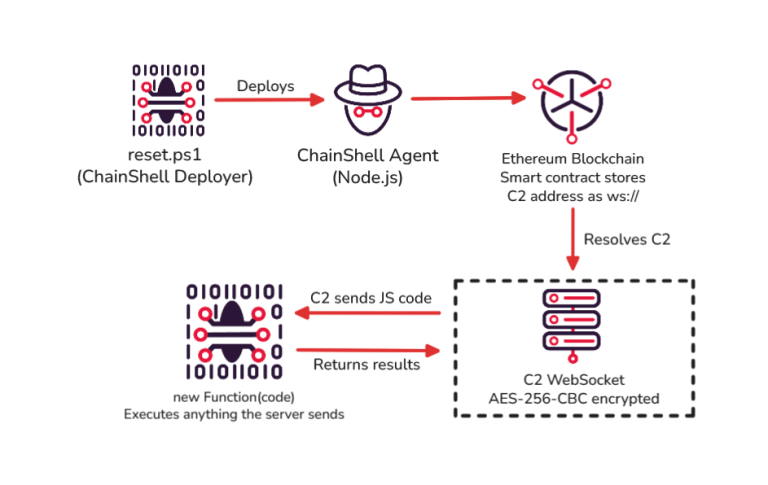
Iranian state actor Muddy Water adopts CastleRAT and ChainShell to hijack browsers and bypass MFA invisibly. A professional-grade shift in APT strategy.