Skip to content
November 9, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
Open Access: How a Simple Fiverr Config Error Exposed 30,000 Private Documents to Google Fiverr Data Leak Claude Code Leak Anthropic DMCA Takedown Coupang 33.7M Breach South Korea Data Leak Red Hat Breach, Customer Data Theft Farmers Insurance, Salesforce ESLint Plugin -Mamont Android banking Trojan
  • Data Leak

Open Access: How a Simple Fiverr Config Error Exposed 30,000 Private Documents to Google

Do Son April 16, 2026 0

Fiverr fails to fix a critical flaw exposing 30,000+ private PDFs, including taxpayer info, to Google Search. Learn how public Cloudinary URLs caused the leak.

Microsoft Opens “Expedited Channel” After Open-Source Developer Accounts Vanish Microsoft OpenAI $97 billion savings Microsoft Developer Account Suspension Microsoft Managed Desktop
  • Technology

Microsoft Opens “Expedited Channel” After Open-Source Developer Accounts Vanish

Do Son April 16, 2026 0

Microsoft launches a manual review channel to restore suspended developer accounts. If your driver signing is paralyzed, find out how to reclaim your access.

North Korea’s “OtterCookie” Hides Inside Benign npm Wrappers Seedworm Espionage Campaign 2026 ChromElevator Stealer DLL Sideloading SIM Swapping Crypto Theft Lazarus Comebacker, Aerospace Espionage Delete PlugX Malware
  • Data Leak

North Korea’s “OtterCookie” Hides Inside Benign npm Wrappers

Do Son April 16, 2026 0

Panther uncovers "OtterCookie," a North Korean npm campaign hiding malware in benign wrappers. It steals crypto wallets and installs SSH backdoors. Audit now!

Hardened Signals: Google’s Pixel 10 Uses Rust to Kill Modem Exploits Pixel 10 Modem Security Rust Memory Safety
  • Android

Hardened Signals: Google’s Pixel 10 Uses Rust to Kill Modem Exploits

Do Son April 16, 2026 0

Google’s Pixel 10 series is the first to use a memory-safe Rust DNS parser in its modem. Learn how this proactive shift eliminates critical cellular exploits.
The $500 Countermove: Can Microsoft’s College Bundle Stop the MacBook Neo Defection? Microsoft College Offer 2026
  • Technology

The $500 Countermove: Can Microsoft’s College Bundle Stop the MacBook Neo Defection?

Do Son April 16, 2026 0

Microsoft fights back! Buy a Windows 11 laptop and get $500 in perks, including Xbox Game Pass and Microsoft 365. Is it enough to beat the $500 MacBook Neo?
Desktop AI War: Google Launches Native Gemini for Mac with “Screen Awareness” and Video Gen Google Gemini Go app Google AI software engineering interview Google Gemini for Mac
  • Technology

Desktop AI War: Google Launches Native Gemini for Mac with “Screen Awareness” and Video Gen

Do Son April 16, 2026 0

Google releases Gemini for Mac. With Option+Space shortcuts, screen awareness, and Nano Banana 2 integration, it’s a direct challenge to Apple Intelligence.
Cisco Patches Critical CVSS 9.9 RCE Flaws in Identity Services Engine Cisco ISE Root Escalation * Read-Only Admin Exploit Cisco Secure FMC Vulnerability CVE-2026-20131 Cisco Meeting Management Vulnerability CVE-2026-20098 Cisco vulnerability, RCE flaw CVE-2025-20265 Cisco Meraki, VPN Vulnerability Cisco Nexus Dashboard - CVE-2024-20424 CVE-2025-20115 Cisco Vulnerability CVE-2018-0171 Privilege Escalation Cisco Unified Intelligence Center
  • Vulnerability Report

Cisco Patches Critical CVSS 9.9 RCE Flaws in Identity Services Engine

Do Son April 16, 2026 0

Cisco alerts on a critical 9.9 CVSS flaw in ISE. Even "Read-Only" admins can escalate to root and trigger a total network lockout. Patch immediately.
RedSun: New Windows Defender Zero-Day Turns Protector into Attacker, PoC Publishes RedSun Zero-Day Windows Defender EoP
  • Vulnerability Report

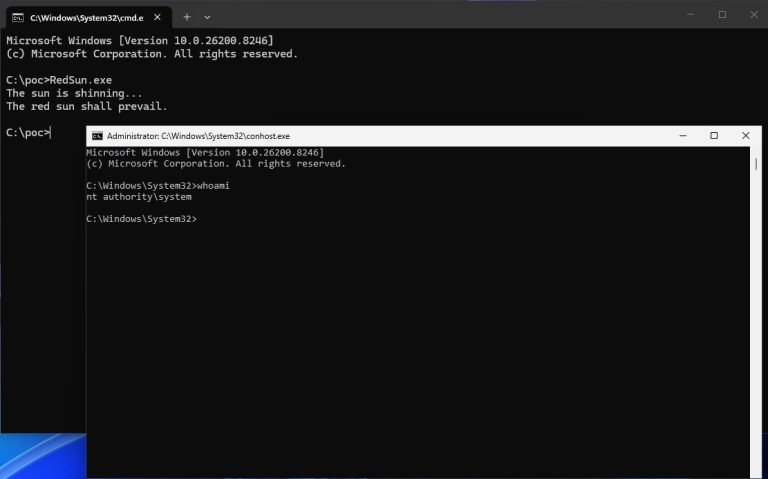
RedSun: New Windows Defender Zero-Day Turns Protector into Attacker, PoC Publishes

Do Son April 16, 2026 0

Windows Defender "RedSun" zero-day revealed! This unpatched EoP flaw turns antivirus into a delivery tool for malicious payloads. PoC is public—patch now!
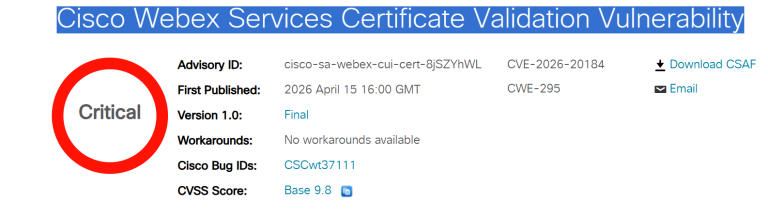
Critical 9.8 Webex Flaw Lets Attackers Impersonate Any User Cisco Webex SSO Webex Impersonation Flaw
  • Vulnerability Report

Critical 9.8 Webex Flaw Lets Attackers Impersonate Any User

Do Son April 16, 2026 0

Cisco Webex CVE-2026-20184 allows unauthenticated user impersonation via SSO flaw. Fix requires a manual certificate update in Control Hub. Act now!

Splunk Issues Urgent Fixes for RCE and Clear-Text Token Leaks Splunk Enterprise vulnerabilities, CVSS 9.8 flaw, CVE-2026-20253, CVE-2026-20251, CVE-2026-20258 Splunk Enterprise Vulnerabilities CVE-2026-20240 Splunk RCE CVE-2026-20204 Splunk RCE Vulnerability CVE-2026-20163 Splunk Enterprise Vulnerabilities CVE-2026-20140 Splunk Permission Flaw, Local Privilege Escalation Splunk Vulnerabilities CVE-2024-53247 - Splunk Secure Gateway App CVE-2025-20229 & CVE-2025-20231
  • Vulnerability Report

Splunk Issues Urgent Fixes for RCE and Clear-Text Token Leaks

Do Son April 16, 2026 0

Splunk fixes CVE-2026-20204, a critical RCE flaw where low-privilege users can hijack servers via temp files. Patch Enterprise and Cloud instances now!
Chrome 147 Update: Google Patches Critical $90,000 ANGLE Flaw and 30 Other Security Gaps Chrome Security Update $90K Bug Bounty
  • Vulnerability Report

Chrome 147 Update: Google Patches Critical $90,000 ANGLE Flaw and 30 Other Security Gaps

Do Son April 16, 2026 0

Google patches 31 Chrome flaws, including a $90K graphics engine bug. Update to version 147.0.7727.101 now to block critical sandbox escapes and RCE risks.
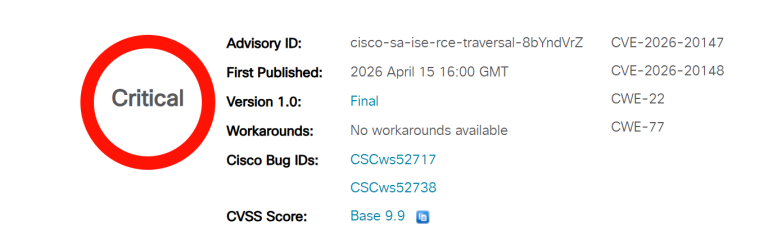
Root Access via Admin: The 9.9 RCE Crisis Threatening Cisco ISE Networks Cisco ISE RCE Identity Services Engine Vulnerability
  • Vulnerability Report

Root Access via Admin: The 9.9 RCE Crisis Threatening Cisco ISE Networks

Do Son April 16, 2026 0

Cisco warns of a critical 9.1 RCE flaw in Identity Services Engine (ISE). Attackers can escalate to root access—apply official security patches now!
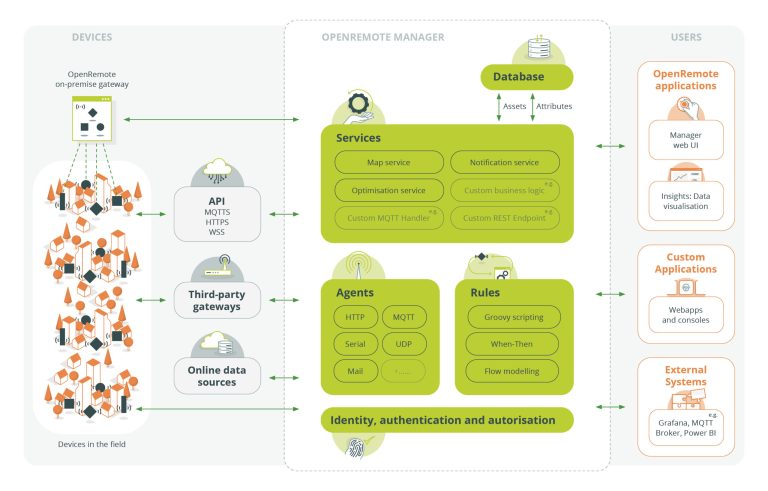
IoT Under Fire: Critical CVSS 10 Expression Injection Hits OpenRemote Platform OpenRemote RCE IoT Security
  • Vulnerability Report

IoT Under Fire: Critical CVSS 10 Expression Injection Hits OpenRemote Platform

Do Son April 15, 2026 0

OpenRemote CVE-2026-39842 is a critical CVSS 10 flaw allowing RCE via JavaScript and Groovy injection. Secure your IoT assets—upgrade to v1.22.0 now!
Critical 9.1 SQL Injection Threatens Vendure Core Stores Vendure SQL Injection Shop API Vulnerability
  • Vulnerability Report

Critical 9.1 SQL Injection Threatens Vendure Core Stores

Do Son April 15, 2026 0

Vendure Core faces a critical 9.1 SQL Injection via the Shop API. Unauthenticated attackers can hijack databases—upgrade to 3.6.2, 3.5.7, or 2.3.4 now!
No Patch Available: The CVSS 10 Flaw Turning AVideo into an Attacker’s Playground AVideo RCE YPTSocket Vulnerability AVideo Vulnerabilities Streaming Platform Security AVideo Vulnerabilities CVE-2026-28501
  • Vulnerability Report

No Patch Available: The CVSS 10 Flaw Turning AVideo into an Attacker’s Playground

Do Son April 15, 2026 0

AVideo’s YPTSocket plugin faces a critical CVSS 10 vulnerability. Unauthenticated attackers can hijack every active session at once. No patch is available.

High-Severity Authentication Bypass Discovered in MinIO Storage MinIO Signature Bypass Unauthenticated Object Write MinIO Privilege Escalation, Policy Bypass CVE-2024-55949
  • Vulnerability Report

High-Severity Authentication Bypass Discovered in MinIO Storage

Do Son April 15, 2026 0

MinIO faces a critical 8.8 CVSS vulnerability allowing unauthenticated object writes by bypassing signature checks. Secure your AI/ML data—upgrade now!
Attackers Weaponize Mailbox Rules to Control Your Inbox M365 Persistence Malicious Mailbox Rules
  • Cybercriminals

Attackers Weaponize Mailbox Rules to Control Your Inbox

Do Son April 15, 2026 0

Proofpoint warns that 10% of M365 account takeovers use malicious mailbox rules to steal data and hide alerts. Secure your cloud identity—check your rules!
JanelaRAT Uses Fake Windows Updates to Empty LATAM Bank Accounts JanelaRAT LATAM Banking Malware
  • Malware

JanelaRAT Uses Fake Windows Updates to Empty LATAM Bank Accounts

Do Son April 15, 2026 0

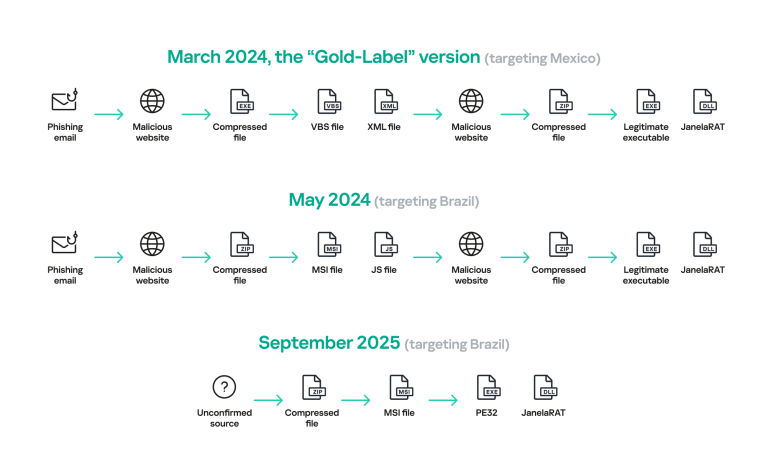
JanelaRAT targets banking users in Brazil and Mexico using window monitoring and fake updates. Learn how this 2026 threat bypasses MFA to hijack sessions.
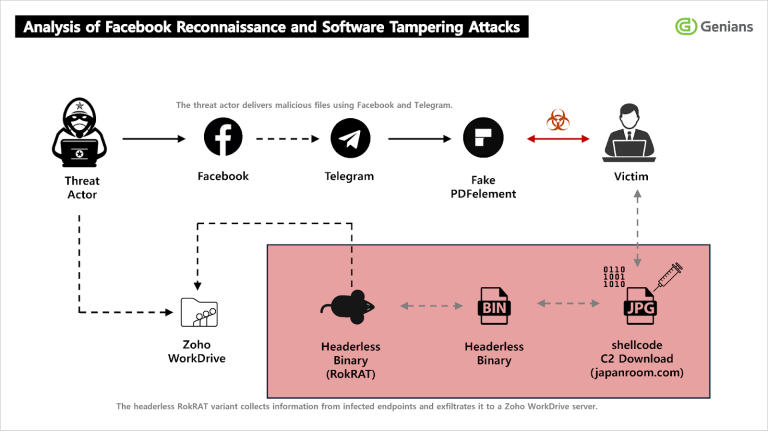
The Friend Request from Pyongyang: How APT37 Hijacks Facebook to Deploy RokRAT APT37 RokRAT Social Engineering Phishing
  • Cybercriminals

The Friend Request from Pyongyang: How APT37 Hijacks Facebook to Deploy RokRAT

Do Son April 15, 2026 0

APT37 pivots to Facebook social engineering, using Wondershare PDFelement "code caves" to deploy RokRAT. Learn how they bypass EDR with memory-only payloads.
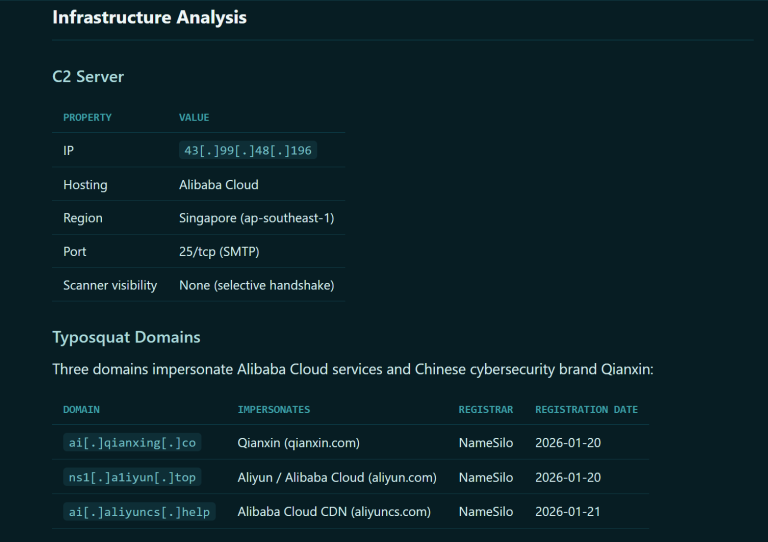
APT41’s New “Zero-Detection” Backdoor Targets Linux Workloads APT41 Linux Backdoor SMTP Command and Control
  • Malware

APT41’s New “Zero-Detection” Backdoor Targets Linux Workloads

Do Son April 15, 2026 0

APT41's new zero-detection ELF backdoor uses SMTP (Port 25) to hijack Linux cloud workloads invisibly. Secure your credentials—audit your SMTP traffic today.

The “Graphalgo” Evolution: How North Korea Built a Fake Florida LLC to Hack Developers Graphalgo Campaign State-Sponsored Phishing
  • Cybercriminals

The “Graphalgo” Evolution: How North Korea Built a Fake Florida LLC to Hack Developers

Do Son April 15, 2026 0

North Korea’s "graphalgo" campaign uses fake job interviews and real Florida LLCs to infect developers. Learn how to spot this sophisticated state-sponsored trap.
FBI and Indonesian Authorities Dismantle Prolific “W3LL” Phishing Empire W3LL Phishing Kit MFA Bypass Takedown
  • Cybercriminals

FBI and Indonesian Authorities Dismantle Prolific “W3LL” Phishing Empire

Do Son April 15, 2026 0

The FBI and Indonesia dismantle W3LL, a $20M phishing kit that bypassed MFA and hijacked live sessions. Learn about the takedown of this MaaS powerhouse.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123751
    The WP Duplicate WordPress plugin through 1.1.11 does not properly verify a request authentication value and does not...
    Watchtower Verified📅 Updated: Nov 9, 2026
  • CVE-2026-111793CVSS 4.3
    Openwave Webtop Media Transcoder does not enforce administrator-defined file type restrictions to restrict the file-types to be converted....
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-114713CVSS 8.6
    The labeled-response module in UnrealIRCd 6.0.0 before 6.2.7.1 does not escape the IRCv3 "label" message tag when echoing...
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-17408CVSS 9.8
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote attacker to execute arbitrary...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17399CVSS 9.9
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote authenticated attacker to execute...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17340CVSS 9.8
    IBM API Connect 12.1.0.0 through 12.1.1.2 could allow a remote attacker to execute arbitrary code due to a...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17342CVSS 9.9
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote authenticated attacker to execute...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17359CVSS 9.9
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote authenticated attacker to execute...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17147CVSS 9.9
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote authenticated attacker to execute...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17150CVSS 9.9
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote authenticated attacker to execute...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17239CVSS 9.9
    IBM API Connect 12.1.0.0 through 12.1.1.2 could allow a remote authenticated attacker to execute arbitrary code due to...
    📅 Updated: Nov 9, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.