Skip to content
November 9, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
Adobe Rushes Patches for Critical ColdFusion RCE and Security Bypasses ColdFusion RCE Adobe Security Patch
  • Vulnerability Report

Adobe Rushes Patches for Critical ColdFusion RCE and Security Bypasses

Do Son April 15, 2026 0

Adobe patches critical RCE and security bypass flaws in ColdFusion 2023 & 2025. Protect your enterprise servers from takeover—update to the latest version now.

Critical 9.1 Flaws Hit Fortinet FortiSandbox FortiSandbox Vulnerability Unauthenticated RCE FortiClient EMS Vulnerability CVE-2026-21643 FortiClient EMS Vulnerability CVE-2026-21643 CVE-2023-34992 - CVE-2023-37936 Fortinet Vulnerabilities CVE-2025-64155
  • Vulnerability Report

Critical 9.1 Flaws Hit Fortinet FortiSandbox

Do Son April 15, 2026 0

Fortinet issues a critical 9.1 CVSS alert for FortiSandbox. Unauthenticated auth bypass and command injection risks. Patch to 5.0.6 or 4.4.9 immediately.
Active SharePoint Spoofing and Legacy Office RCE: CISA Alerts on New KEV Exploits CISA KEV Catalog Updates Langflow CVE-2025-34291 Exploit SharePoint Spoofing CISA KEV Catalog Actively Exploited Vulnerability
  • Vulnerability Report

Active SharePoint Spoofing and Legacy Office RCE: CISA Alerts on New KEV Exploits

Do Son April 15, 2026 0

CISA adds Microsoft SharePoint spoofing (CVE-2026-32201) and legacy Office RCE (CVE-2009-0238) to its KEV Catalog. Remediation deadline: April 28, 2026.

25 Million Users at Risk: Fastify Publicly Discloses PoC Exploit for Single-Space Security Bypass Fastify CVE-2026-33806 Public PoC Exploit
  • Vulnerability Report

25 Million Users at Risk: Fastify Publicly Discloses PoC Exploit for Single-Space Security Bypass

Do Son April 15, 2026 0

Fastify (25M+ downloads) reveals CVE-2026-33806. A public PoC exploit shows how a single space bypasses schema validation. Upgrade to v5.8.5 now to stay safe.
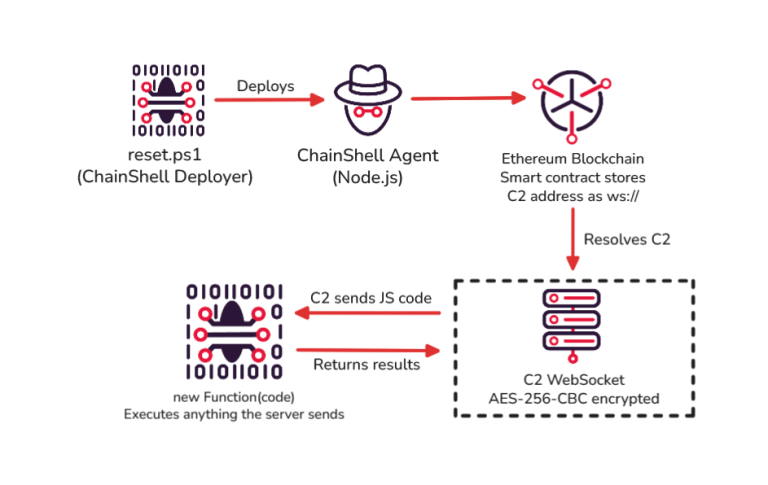
JUMPSEC Unmasks Iranian ‘Muddy Water’ Using Russian ‘CastleRAT’ Malware Muddy Water CastleRAT HVNC Browser Hijacking
  • Cyber Security
  • Malware

JUMPSEC Unmasks Iranian ‘Muddy Water’ Using Russian ‘CastleRAT’ Malware

Do Son April 15, 2026 0

Iranian state actor Muddy Water adopts CastleRAT and ChainShell to hijack browsers and bypass MFA invisibly. A professional-grade shift in APT strategy.

OpenStack Keystone Flaw Grants Access to Disabled LDAP Users CVE-2024-44082 - OpenStack Ironic OpenStack Keystone LDAP Identity Service Vulnerability
  • Vulnerability Report

OpenStack Keystone Flaw Grants Access to Disabled LDAP Users

Do Son April 15, 2026 0

OpenStack Keystone vulnerability allows disabled LDAP users to authenticate. Logic flaw in attribute mapping affects releases up to 2026.1. Patch now!

Urgent Patch Alert: SharePoint Spoofing Under Active Attack as Microsoft Releases April 2026 Updates Microsoft Patch Tuesday May 2026 Netlogon RCE CVE-2026-41089 SharePoint Exploit Patch Tuesday Windows DWM Zero-Day CVE-2026-21519 CVE-2024-49039 Microsoft Patch Tuesday March 2025
  • Vulnerability Report

Urgent Patch Alert: SharePoint Spoofing Under Active Attack as Microsoft Releases April 2026 Updates

Do Son April 15, 2026 0

Microsoft’s April 2026 Patch Tuesday fixes 163 flaws, including an exploited SharePoint spoofing bug (CVE-2026-32201). Patch by April 28 per CISA mandate.

108 Coordinated Chrome Extensions Hijack Your Private Telegram Sessions Chrome Extension Malware Telegram Session Hijacking
  • Malware

108 Coordinated Chrome Extensions Hijack Your Private Telegram Sessions

Do Son April 15, 2026 0

Socket identifies 108 malicious Chrome extensions stealing Telegram sessions and Google IDs. 20,000 installs hit—audit your browser extensions immediately!

Security Risk Advisors Purple Team Participants Can Now Earn CPE Credits sra-purple-team-cpe-credits-pr-featured_1776180900VZhTqvBTWp
  • Press Release

Security Risk Advisors Purple Team Participants Can Now Earn CPE Credits

cybernewswire April 14, 2026 0
Philadelphia, United States / Pennsylvania, 14th April 2026, CyberNewswire
Read More Read more about Security Risk Advisors Purple Team Participants Can Now Earn CPE Credits
Critical—9 Vulnerabilities in Orthanc DICOM Servers Threaten Medical Data Integrity CVE-2025-2263 Orthanc Security DICOM Vulnerabilities
  • Vulnerability Report

Critical—9 Vulnerabilities in Orthanc DICOM Servers Threaten Medical Data Integrity

Do Son April 14, 2026 0

Orthanc v1.12.11 patches 9 critical flaws, including RCE risks and "decompression bombs" in DICOM servers. Secure your healthcare data—upgrade now!

Juju’s CVSS 10 Flaw Hands Over Master Cloud Credentials Juju Orchestration Cloud Credential Theft Juju Orchestration Vulnerability CVE-2026-4370
  • Vulnerability Report

Juju’s CVSS 10 Flaw Hands Over Master Cloud Credentials

Do Son April 14, 2026 0

Juju's critical CVSS 10 flaw (CVE-2026-5412) allows low-level users to steal master cloud credentials. Secure your AWS/Azure/GCP environments—upgrade now!
CVE-2026-4810: Critical 9.3 RCE Flaw Hits Google’s AI Agent Development Kit Google ADK Vulnerability AI Agent RCE
  • Vulnerability Report

CVE-2026-4810: Critical 9.3 RCE Flaw Hits Google’s AI Agent Development Kit

Do Son April 14, 2026 0

Google ADK (CVE-2026-4810) faces a critical 9.3 CVSS RCE flaw. Unauthenticated attackers can hijack AI agents on GKE & Cloud Run. Update and redeploy now!
5 Best Autonomous Penetration Testing Tools in 2026 Employees Risk
  • Technique

5 Best Autonomous Penetration Testing Tools in 2026

Do Son April 14, 2026 0
Most pentest reports start losing value the moment the environment changes. That happens fast. New assets appear,...
Read More Read more about 5 Best Autonomous Penetration Testing Tools in 2026
The Final Countdown: Microsoft Sets October 2026 for Office 2021 Support Shutdown Office 2021 End of Life CVE-2024-21413 KB5002700 Office 2016 Update
  • Technology

The Final Countdown: Microsoft Sets October 2026 for Office 2021 Support Shutdown

Do Son April 14, 2026 0

Office 2021 reaches its end of life on October 13, 2026. Learn about the security risks and discover your upgrade paths to Office 2024 or Microsoft 365.
CVE-2026-4631: Critical 9.8 RCE Flaw in Cockpit Allows Unauthenticated Server Takeover Cockpit RCE CVE-2026-4631
  • Vulnerability Report

CVE-2026-4631: Critical 9.8 RCE Flaw in Cockpit Allows Unauthenticated Server Takeover

Do Son April 14, 2026 0

Cockpit CVE-2026-4631 allows unauthenticated RCE on Linux servers via SSH injection. Stop the unauthorized takeover—upgrade to Cockpit version 360 now!

The Sunset of Speed: Microsoft Sets Final Shutdown Date for Outlook Lite on Android Outlook Lite Retirement 2026
  • Technology

The Sunset of Speed: Microsoft Sets Final Shutdown Date for Outlook Lite on Android

Do Son April 14, 2026 0

Outlook Lite for Android is officially shutting down on May 25, 2026. Learn how to migrate to the full Outlook Mobile app to keep your emails and calendar safe.

Supply Chain Sabotage: The Critical RCE Flaws Lurking in PHP Composer CVE-2026-40176, CVE-2026-40261 Composer GitHub Token Leak CVE-2026-45793
  • Vulnerability Report

Supply Chain Sabotage: The Critical RCE Flaws Lurking in PHP Composer

Do Son April 14, 2026 0

Critical Remote Command Injection flaws in PHP Composer's Perforce integration (CVE-2026-40176 & CVE-2026-40261) could lead to full system compromise. Patch now.

Breaking the 5-Week Limit: Windows 11 to Finally Grant Users Total Update Autonomy Windows 11 Update Deferral
  • Windows

Breaking the 5-Week Limit: Windows 11 to Finally Grant Users Total Update Autonomy

Do Son April 14, 2026 0

Microsoft is testing a new date-selection tool for Windows 11 that could let you pause updates for years. Say goodbye to forced reboots and the 5-week limit.
Check Your Inbox: Booking.com Forced to Reset PINs After Major Data Leak Booking.com Data Breach Claude Code Leak Anthropic Source Code YggTorrent data breach PS5 BootROM key leak 2026, PlayStation 5 unpatchable jailbreak Great Firewall data leak Dating App Breach, Tea App Leak 23andMe Data Leak
  • Data Leak

Check Your Inbox: Booking.com Forced to Reset PINs After Major Data Leak

Do Son April 14, 2026 0

Booking.com confirms a data breach exposing names, emails, and itineraries. Learn how to verify official alerts and protect yourself from new phone scams.

The Archival Crisis: Why The New York Times and Reddit are Purging The Wayback Machine Wayback Machine AI Blockade Internet Archive, FDLP Designation Internet Archive, copyright lawsuit
  • Technology

The Archival Crisis: Why The New York Times and Reddit are Purging The Wayback Machine

Do Son April 14, 2026 0

Major publishers are blocking the Internet Archive to stop AI firms from stealing data. Discover how the "ia_archiver" became collateral damage in the AI wars.

Google’s New Deadline: Why Your Site’s “Back Button” Could Get You De-Indexed by June 15 Low carbon cloud computing Smartphone clusters, Green technology, Data centers, Google research Google Agentic AI search G Suite legacy free commercial reclassification 2026 Agent Payments Protocol AP2 Back-Button Hijacking Google Search AI headlines Google Play Store fee reduction Google Antigravity account recovery Google Advanced Air-Cooling Alphabet $185 billion CapEx 2026 Google Aluminum OS 2026 ai-disclosure HTML attribute, Chrome AI content transparency 2026 Google monopoly appeal 2026, Search data sharing stay Change @gmail.com address, Gmail email alias feature 2025 Google Play Store external download fees, Epic vs Google 2026 billing Google Dark Web Report Retirement, Data Breach Monitoring Google Antitrust One-Year Limit Default Search Contract Term Google AI Headlines Discover Headline Distortion Aluminium OS Android ChromeOS Merge Google Accelerator Impact $31.2 Billion Funding Google Texas Investment AI Data Center Expansion Google Play payments, external billing Gmail HIBP leak Privacy Sandbox Termination, Third-Party Cookies Google Strategic Market Status, CMA Antitrust ICEBlock Removal, DOJ Pressure Google Logo, AI Branding
  • Technology

Google’s New Deadline: Why Your Site’s “Back Button” Could Get You De-Indexed by June 15

Do Son April 14, 2026 0

Google formally classifies back-button hijacking as a "malicious practice." Fix your navigation scripts by June 15, 2026, or face total search de-indexing.

Python Under Pressure: Critical Memory Flaws and Command Injection Bypass Uncovered Python Security Memory Safety PLY Vulnerability CVE-2025-56005 Python Software Foundation, NSF DEI CVE-2024-12254
  • Vulnerability

Python Under Pressure: Critical Memory Flaws and Command Injection Bypass Uncovered

Do Son April 14, 2026 0

Python patches a critical 9.1 UAF flaw in decompressors and a browser command injection bypass. Protect your infrastructure—audit your CPython code today!

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123751
    The WP Duplicate WordPress plugin through 1.1.11 does not properly verify a request authentication value and does not...
    Watchtower Verified📅 Updated: Nov 9, 2026
  • CVE-2026-111793CVSS 4.3
    Openwave Webtop Media Transcoder does not enforce administrator-defined file type restrictions to restrict the file-types to be converted....
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-114713CVSS 8.6
    The labeled-response module in UnrealIRCd 6.0.0 before 6.2.7.1 does not escape the IRCv3 "label" message tag when echoing...
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-17408CVSS 9.8
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote attacker to execute arbitrary...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17399CVSS 9.9
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote authenticated attacker to execute...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17340CVSS 9.8
    IBM API Connect 12.1.0.0 through 12.1.1.2 could allow a remote attacker to execute arbitrary code due to a...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17342CVSS 9.9
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote authenticated attacker to execute...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17359CVSS 9.9
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote authenticated attacker to execute...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17147CVSS 9.9
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote authenticated attacker to execute...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17150CVSS 9.9
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote authenticated attacker to execute...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17239CVSS 9.9
    IBM API Connect 12.1.0.0 through 12.1.1.2 could allow a remote authenticated attacker to execute arbitrary code due to...
    📅 Updated: Nov 9, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.