 Do Son
Sonatype Nexus Repository (CVE-2026-5189) faces a critical 9.2 CVSS flaw. A hardcoded database credential grants full host access. Patch to v3.71.0 now!

Synology patches critical DSM flaws (CVSS 8.0) allowing file manipulation and data leaks. Secure your NAS—upgrade to DSM 7.3, 7.2.2, or 7.2.1 immediately!

A critical 9.1 CVSS flaw in OAuth2 Proxy allows unauthenticated users to bypass security via User-Agent spoofing. Secure your upstream apps—patch v7.15.2 today.
Krayin CRM faces a critical CVSS 10 RCE flaw in its TinyMCE upload endpoint. Authenticated users can seize server control. Patch version 2.2.x immediately!
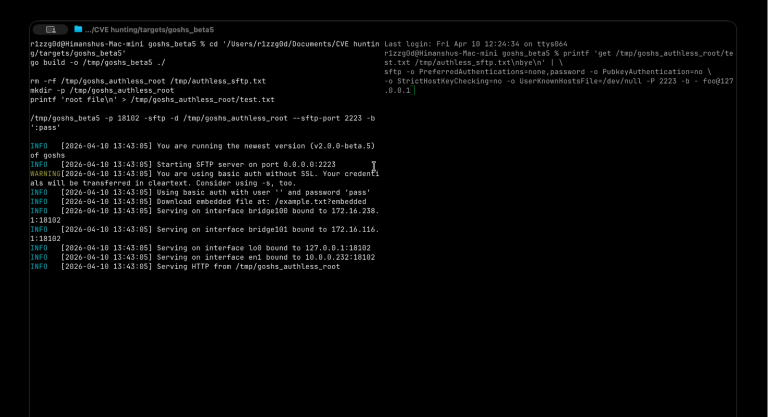
Critical 9.8 flaw in goshs (CVE-2026-40884) allows unauthenticated SFTP access when using specific auth syntax. Secure your files—upgrade to v2.0.0-beta.6 now!

Google introduces Prepaid Credits and Project Spend Caps for the Gemini API. Protect your cloud account from leaked key overages and surprise billing cycles.

Microsoft hardens RDP in the April 2026 update. Discover how new default isolation policies and security warnings stop malicious servers from stealing your data.
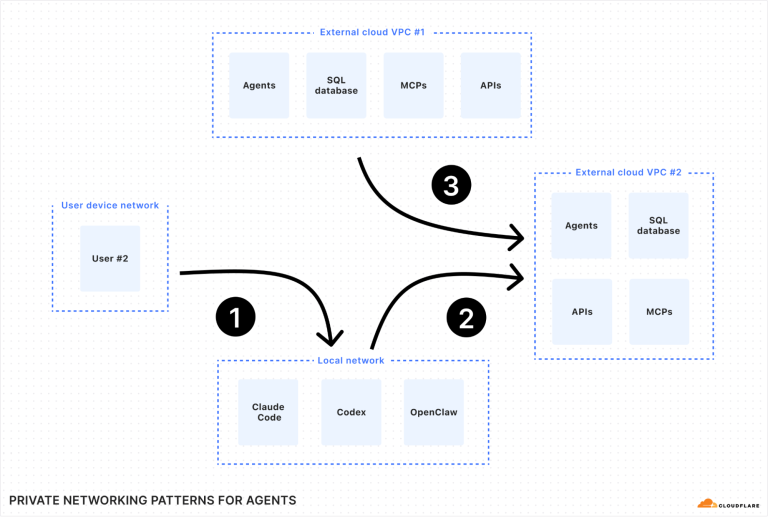
Cloudflare Mesh is here. Discover how this post-quantum encrypted network secures AI agents and infrastructure, offering a 50-node free tier to rival Tailscale.

Cloudflare adds regional and jurisdictional constraints to Containers. Easily enforce GDPR and FedRAMP compliance by pinning data to specific global locales.
Telegram launches Manager Mode! Now bots can create and manage sub-bots, enabling developers to deploy multi-tenant AI agent services with zero user setup.

Microsoft resolves the bug causing Windows Server 2019/2022 to auto-upgrade to 2025. Learn about the KB5082063 fix and the 10-day rollback window.

Microsoft releases KB5083769 for Windows 11, fixing BitLocker recovery loops and preparing for the critical June 2026 UEFI certificate expiration.

GitHub has suspended all Copilot Pro trials as of April 13, 2026. Learn how bad-faith exploitation forced a service-wide shutdown and what it means for you.
OpenAI unveils GPT-5.4-Cyber to counter Anthropic’s Claude Mythos. Explore the "cyber-permissive" model that reverse-engineers malware for verified defenders.
Google I/O 2026 kicks off May 19! Explore the shift to agentic AI, Android 17, and autonomous developer workflows that redefine software engineering.

NVIDIA denies rumors of a major PC manufacturer acquisition. Explore the strategy behind the "AI Factory" and the new N1 chips aimed at Windows on Arm.

Anthropic introduces mandatory identity audits for Claude users via Persona. Learn which IDs are accepted and how your biometric data is (and isn't) used.

Use-after-free flaw in Rsync versions 3.0.1–3.4.1 allows DoS and info leaks via malicious xattr traffic. Learn how a simple qsort fix secures your syncs.
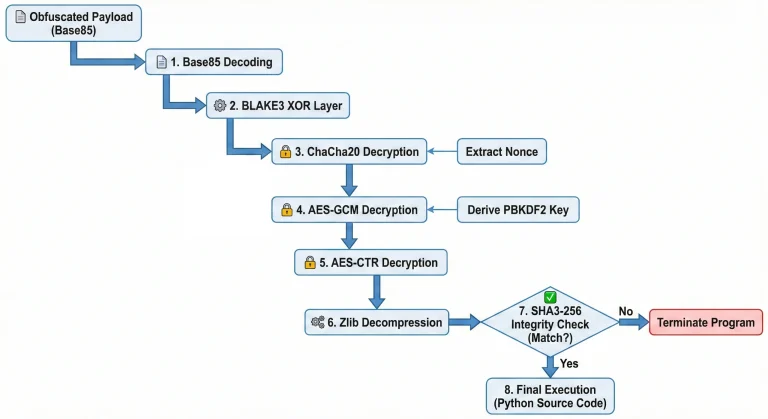
InfoGuard unmasks VIPERTUNNEL, a Python backdoor using sitecustomize.py for stealthy persistence in DragonForce ransomware attacks. Learn how to detect it.

Faced with a massive surge in CVEs, NIST has overhauled the NVD. Starting April 2026, only high-risk flaws get full analysis. Check the new triage rules.
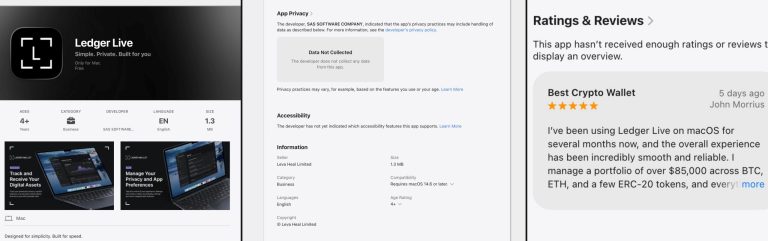
A malicious fake Ledger Live app on the Mac App Store has stolen $9.5M from users. Learn how the scam bypassed Apple's security and why your seed phrase is at risk.

Fiverr fails to fix a critical flaw exposing 30,000+ private PDFs, including taxpayer info, to Google Search. Learn how public Cloudinary URLs caused the leak.