Skip to content
November 9, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
Dgraph’s Debug Endpoint Hands Over Admin Tokens to Anyone Dgraph Vulnerability CVSS 10.0 Dgraph Admin Leak CVE-2026-40173
  • Vulnerability Report

Dgraph’s Debug Endpoint Hands Over Admin Tokens to Anyone

Do Son April 19, 2026 0

Dgraph (CVE-2026-40173) leaks admin tokens in plain text via unauthenticated debug endpoints. This critical 9.4 CVSS flaw allows full DB takeover. Patch now!

North Korea’s UNC1069 Uses Fake Video Calls to Hijack Crypto UNC1069 Fake Meetings ClickFix Malware
  • Cybercriminals

North Korea’s UNC1069 Uses Fake Video Calls to Hijack Crypto

Do Son April 19, 2026 0

North Korea's UNC1069 uses fake video calls and "ClickFix" prompts to drain crypto assets and record victims for deepfakes. Audit your meetings now!

OAUTHBEARER Bypass and Sensitive Logging Leaks Hit Apache Kafka Kafka Authentication Bypass JWT Signature Validation Apache Kafka - CVE-2024-27309 & CVE-2024-31141
  • Vulnerability Report

OAUTHBEARER Bypass and Sensitive Logging Leaks Hit Apache Kafka

Do Son April 19, 2026 0

Apache Kafka faces a critical OAUTHBEARER bypass (CVE-2026-33557) and sensitive logging leaks. Secure your data pipelines—patch to v4.1.2 or v4.2.0 today.

The Great Data Handover: Why the EU is Forcing Google to Share Its “Search Crown Jewels” Digital Markets Act Google search data Google Search, Preferred Sources
  • Technology

The Great Data Handover: Why the EU is Forcing Google to Share Its “Search Crown Jewels”

Do Son April 19, 2026 0

The EU’s 2026 DMA draft orders Google to share query, click, and ranking data with rivals. Explore how this "data handover" aims to level the search market.
Beyond the Chatbot: Anthropic Unveils “Claude Design” to Challenge Adobe and Canva Claude Design preview
  • Technology

Beyond the Chatbot: Anthropic Unveils “Claude Design” to Challenge Adobe and Canva

Do Son April 19, 2026 0

Anthropic launches Claude Design! Powered by the Opus 4.7 vision model, it creates UI prototypes and brand-aligned assets that follow your specific codebase.
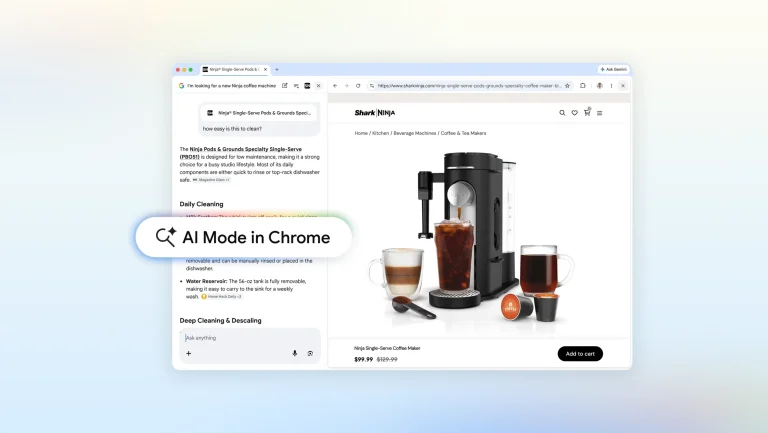
Chrome’s New Desktop Update Lets You Browse Side-by-Side with AI Chrome AI Mode side-by-side
  • Technology

Chrome’s New Desktop Update Lets You Browse Side-by-Side with AI

Do Son April 19, 2026 0

Google Chrome’s April 2026 update ends tab-switching. Use the new side-by-side AI Mode and "Plus" menu to synthesize data across tabs, PDFs, and images instantly.

Critical 9.3 Flaw Lets Outsiders Hijack AVEVA Pipeline Simulations AVEVA Pipeline Simulation Flaw CVE-2026-5387
  • Vulnerability Report

Critical 9.3 Flaw Lets Outsiders Hijack AVEVA Pipeline Simulations

Do Son April 18, 2026 0

AVEVA alerts on a 9.3 critical flaw in Pipeline Simulation. Unauthenticated users can hijack admin roles and alter data. Upgrade to version 2025 SP1 P01 now.
Critical 9.1 SSTI Flaws Unmasked in Thymeleaf Template Engine Thymeleaf SSTI Bypass CVE-2026-41901 Thymeleaf SSTI CVE-2026-40477
  • Vulnerability Report

Critical 9.1 SSTI Flaws Unmasked in Thymeleaf Template Engine

Do Son April 17, 2026 0

Thymeleaf 3.1.4 fixes two critical 9.1 CVSS vulnerabilities. Unauthenticated attackers can bypass security for SSTI. Audit your user input and patch today!

Critical 9.1 CVSS Flaw in Horner Automation PLCs Invites Industrial Takeovers Fortra BoKS vulnerability OS command injection, CVE-2026-9862 Altium Enterprise Server Vulnerability CVE-2026-9129 Path Traversal Patreon OAuth Vulnerability Identity Collision DRC INSIGHT Vulnerability Exam Data Hijacking Horner Automation PLC Industrial Brute Force Honeywell IQ4x Vulnerability CVE-2026-3611 DJI Romo vacuum security flaw Python Cryptography Vulnerability CVE-2026-26007 Open5GS Vulnerability CVE-2026-0622 Vivotek IP7137 Vulnerabilities CVE-2025-66049 Forcepoint DLP Vulnerability CVE-2025-14026 Cellopoint Secure Email Gateway - CVE-2024-9043
  • Vulnerability

Critical 9.1 CVSS Flaw in Horner Automation PLCs Invites Industrial Takeovers

Do Son April 17, 2026 0

Critical 9.1 CVSS flaw in Horner Automation PLCs allows unauthenticated brute force attacks. Secure your industrial systems—patch XL4, XL7, and Cscape now!
Froxlor’s CVSS 10 Flaw Turns Config Files into Persistent Backdoors Froxlor RCE Persistent Backdoor
  • Vulnerability Report

Froxlor’s CVSS 10 Flaw Turns Config Files into Persistent Backdoors

Do Son April 17, 2026 0

Froxlor faces two critical flaws, including a CVSS 10. Learn how path traversal and config injection allow persistent RCE. Patch your server management today!

Critical Command Injection Flaw Hits upKeeper Instant Privilege Access shell-quote command injection AI-Driven Vulnerabilities Q1 2026 Cyber Threats vm2 Sandbox Escape Node.js RCE upKeeper Privilege Escalation CVE-2026-2449 Pharos Controls Vulnerability Root Access Exploit Cybersecurity Vulnerability Roundup CVSS 10.0 Flaws Shadow Archives CVE-2026-0866 MS-Agent Prompt Injection CVE-2026-2256 basic-ftp Path Traversal CVE-2026-27699 telnetd Root Vulnerability CVE-1999-0073 Regression USR-W610 Vulnerabilities End-of-Life IoT Security IceWarp Security Update IceWarp Vulnerabilities Airleader Master Vulnerability CVE-2026-1358 ZLAN5143D Vulnerability CISA ICS Advisory Acronis Cyber Protect Vulnerability CVE-2025-30411 WAGO 852 Vulnerability OT Network Security SandboxJS Vulnerability Sandbox Escape (CVSS 10.0) Kubernetes Local Path Provisioner CVE-2025-62878 CISA Unresponsive Vendors Avation & RISS Vulnerabilities KiloView Vulnerability CVE-2026-1453 OpenClaw RCE vulnerability Johnson Controls Vulnerability CVE-2025-26385 SandboxJS Vulnerability CVE-2026-23830 ibaPDA Vulnerability CVE-2025-14988 Protobuf Vulnerability CVE-2026-0994 AVEVA Process Optimization Vulnerability CVE-2025-61937 ConnectWise PSA Vulnerability CVE-2026-0695 Aruba VIA Vulnerability CVE-2025-37186 aiohttp v3.13.3, Denial of Service (DoS) SmarterMail RCE, CVE-2025-52691 Airoha RACE, Headphone Jacking HPE OneView RCE CVE-2025-37164 FreePBX Auth Bypass, PBX Takeover ScreenConnect Config Flaw, Untrusted Extensions Ruby SAML Auth Bypass, XML Parser Differential Devolutions SQL Injection, Password Manager Flaw Vivotek Unauthenticated RCE, EOL IP Camera Flaw Lynx+ Critical Flaw, Unauthenticated Reset Firebox Default Credentials, CVE-2025-59396 Veeder-Root RCE, Critical ATG Flaw ArcGIS Server SQLi Watchdoc RCE, CVE-2025-58384 Delta DIALink Daikin Security Gateway, authentication bypass Frostbyte10, industrial controller security SunPower, vulnerability Ubiquiti UniFi Connect, EV Station Vulnerabilities Adobe Experience Manager, RCE Vulnerability UniFi Access, Command Injection LDAPNightmare - CVE-2025-1316
  • Vulnerability Report

Critical Command Injection Flaw Hits upKeeper Instant Privilege Access

Do Son April 17, 2026 0

Critical 9.1 flaw in upKeeper Instant Privilege allows standard users to gain LocalSystem rights via command injection. Patch to v1.6.0.4576 immediately.
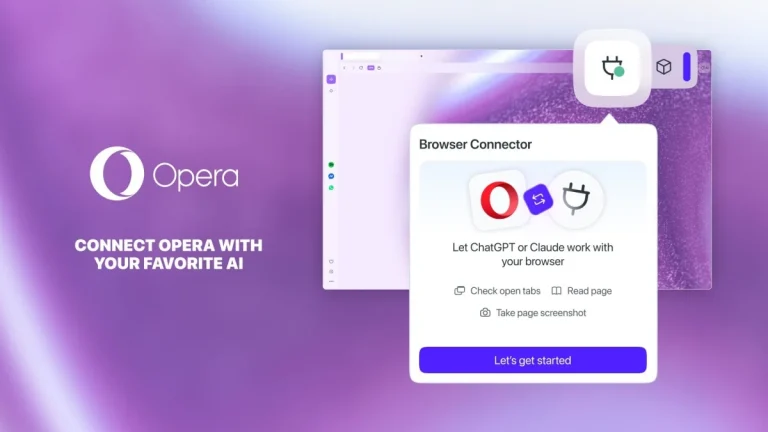
Opera’s “Browser Connector” Gives ChatGPT and Claude the Power to “See” Your Tabs Opera Browser Connector
  • Technology

Opera’s “Browser Connector” Gives ChatGPT and Claude the Power to “See” Your Tabs

Do Son April 17, 2026 0

Opera shatters vendor lock-in with "Browser Connector." Now, ChatGPT and Claude can read your active tabs and summarize web content directly within Opera One.
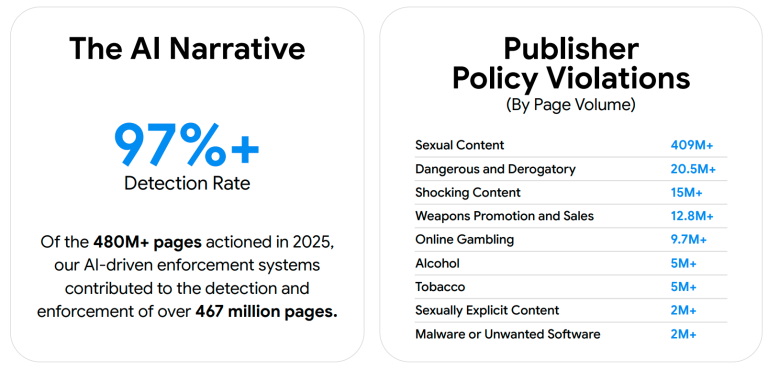
Gemini vs. GenAI Fraud: How Google Blocked 8.3 Billion Malicious Ads in 2025 Google Ads Safety Report 2025
  • Malware

Gemini vs. GenAI Fraud: How Google Blocked 8.3 Billion Malicious Ads in 2025

Do Son April 17, 2026 0

Google’s 2025 Ads Safety Report reveals how Gemini AI intercepted 99% of bad ads and reduced false account suspensions by 80%. Read the full scale of the defense.
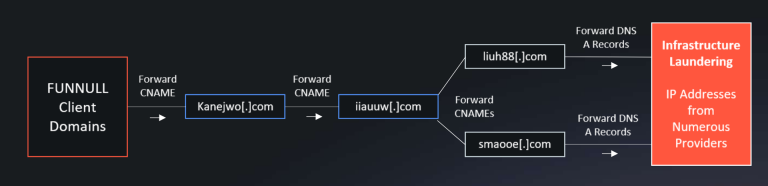
Triad Nexus’ $300M “Infrastructure Laundering” Machine Exposed Infrastructure Laundering Triad Nexus
  • Cybercriminals

Triad Nexus’ $300M “Infrastructure Laundering” Machine Exposed

Do Son April 17, 2026 0

Triad Nexus has built a $300M fraud engine using "Infrastructure Laundering" on AWS and Google. See how they use geo-fencing and CNAME chains to evade the law.
Critical Pre-Auth RCE Found in OpenAM Identity Platform OpenAM RCE CVE-2026-33439
  • Vulnerability Report

Critical Pre-Auth RCE Found in OpenAM Identity Platform

Do Son April 17, 2026 0

Critical 9.3 RCE in OpenAM (CVE-2026-33439) allows unauthenticated attackers to execute OS commands via jato.clientSession. Patch your 16.0.5 servers now!
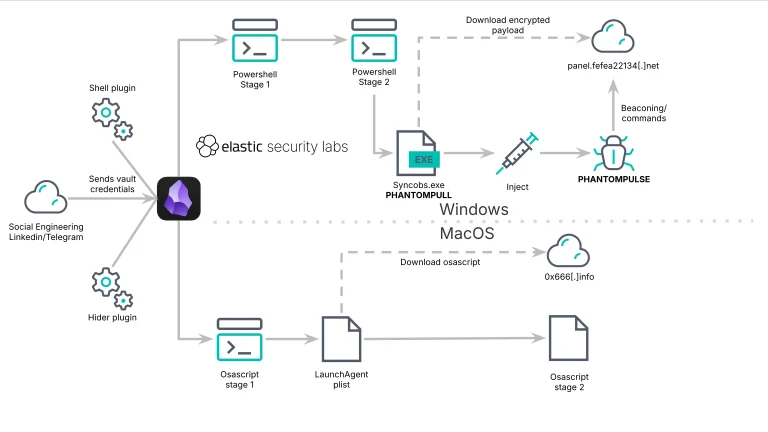
AI-Generated RAT “PHANTOMPULSE” Targets Crypto Sector via Social Engineering PHANTOMPULSE RAT Obsidian Malware Abuse
  • Malware

AI-Generated RAT “PHANTOMPULSE” Targets Crypto Sector via Social Engineering

Do Son April 17, 2026 0

Elastic uncovers PHANTOMPULSE: A novel RAT abusing Obsidian plugins and blockchain C2. Stay safe from this AI-assisted campaign targeting crypto firms.
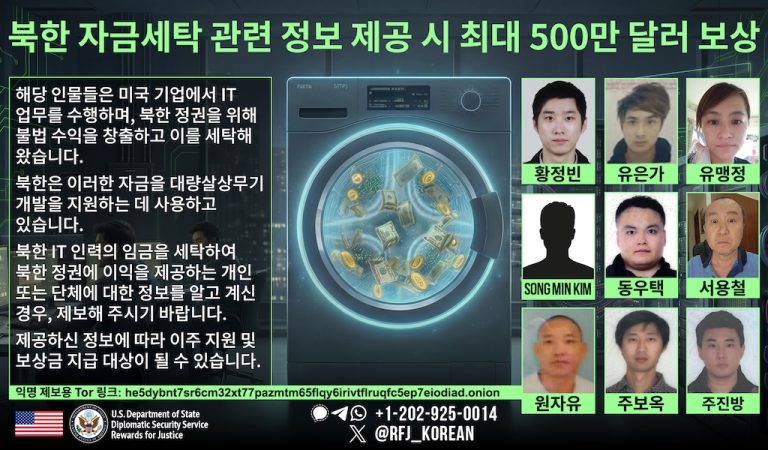
The “Laptop Farm” Fallout: Two NJ Men Sentenced for Facilitating $5M North Korean Work Scheme Laptop Farm North Korean IT Fraud
  • Cybercriminals

The “Laptop Farm” Fallout: Two NJ Men Sentenced for Facilitating $5M North Korean Work Scheme

Do Son April 17, 2026 0

Two NJ residents sentenced for running a "laptop farm" allowing North Korean workers to infiltrate 100+ U.S. companies and steal $5M in revenue.

Wormable Bugs: Microsoft April 2026 Patch Tuesday Fixes Two “Zero-Interaction” RCE Flaws Microsoft Patch Tuesday fixes disclosed zero day vulnerabilities Windows Wormable Exploit April 2026 Patch Tuesday Microsoft Patch Tuesday Zero-Day Vulnerabilities Microsoft, Patch Tuesday CVE-2025-55234 CVE-2024-43573 and CVE-2024-43572 Microsoft Patch Tuesday Security Vulnerabilities
  • Vulnerability Report

Wormable Bugs: Microsoft April 2026 Patch Tuesday Fixes Two “Zero-Interaction” RCE Flaws

Do Son April 17, 2026 0

Microsoft’s April 2026 Patch Tuesday fixes two "wormable" CVEs (9.8 & 8.1 CVSS). Secure your network against zero-click RCE and lateral movement now.
220 Million at Risk: Critical 9.4 CVSS Remote Code Execution Hits protobuf.js protobuf.js RCE Protocol Buffers Vulnerability
  • Vulnerability Report

220 Million at Risk: Critical 9.4 CVSS Remote Code Execution Hits protobuf.js

Do Son April 17, 2026 0

A critical 9.4 CVSS vulnerability in protobuf.js puts 220 million monthly downloads at risk of RCE. Patch your Node.js and browser apps to version 8.0.1+.

High-Severity SSRF Flaw Uncovered in Angular’s Server-Side Rendering Angular hostname hijacking vulnerability Angular SSRF Origin Hijacking Angular XSS Vulnerability CVE-2026-32635 Angular i18n XSS CVE-2026-27970 Angular SSR SSRF CVE-2026-27739 Angular Vulnerability CVE-2026-22610 CVE-2025-59052 Angular security Angular XSS Bypass, SVG Injection
  • Vulnerability Report

High-Severity SSRF Flaw Uncovered in Angular’s Server-Side Rendering

Do Son April 17, 2026 0

Angular patches a critical 8.7 SSRF flaw in @angular/platform-server. Attackers can hijack SSR origins via URL normalization. Patch v19, v20, or v21 now!
CISA Adds Critical Apache ActiveMQ RCE Flaw to KEV Catalog CISA active exploit catalog known exploited vulnerabilities ActiveMQ RCE CVE-2026-34197 CISA KEV Catalog Actively Exploited Vulnerabilities CISA KEV Catalog CVE-2025-37164 GeoServer XXE, CISA KEV FortiWeb SQLi, CISA KEV Critical Vulnerabilities CVE-2024-20953
  • Vulnerability Report

CISA Adds Critical Apache ActiveMQ RCE Flaw to KEV Catalog

Do Son April 17, 2026 0

CISA adds CVE-2026-34197 to KEV. Apache ActiveMQ's Jolokia bridge flaw allows RCE via remote Spring XML loading. Remediate by April 30, 2026. Patch now!

The Invisible Patch: How PolinRider Rewrites Git History to Hide North Korean Malware PolinRider Malware Git History Falsification
  • Malware

The Invisible Patch: How PolinRider Rewrites Git History to Hide North Korean Malware

Do Son April 17, 2026 0

PolinRider targets 1,900+ GitHub repos using "history-falsification" to hide malware. DPRK's Lazarus Group uses fake job tests to breach developers.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-111793CVSS 4.3
    Openwave Webtop Media Transcoder does not enforce administrator-defined file type restrictions to restrict the file-types to be converted....
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-114713CVSS 8.6
    The labeled-response module in UnrealIRCd 6.0.0 before 6.2.7.1 does not escape the IRCv3 "label" message tag when echoing...
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-17408CVSS 9.8
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote attacker to execute arbitrary...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17399CVSS 9.9
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote authenticated attacker to execute...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17340CVSS 9.8
    IBM API Connect 12.1.0.0 through 12.1.1.2 could allow a remote attacker to execute arbitrary code due to a...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17342CVSS 9.9
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote authenticated attacker to execute...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17359CVSS 9.9
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote authenticated attacker to execute...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17147CVSS 9.9
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote authenticated attacker to execute...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17150CVSS 9.9
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote authenticated attacker to execute...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17239CVSS 9.9
    IBM API Connect 12.1.0.0 through 12.1.1.2 could allow a remote authenticated attacker to execute arbitrary code due to...
    📅 Updated: Nov 9, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.