
 Do Son
PTC issues a critical advisory for Windchill and FlexPLM. CVE-2026-4681 is an RCE flaw allowing full server control via deserialization. Patch now!

Cisco alerts of public flaws in IOS XE. Authenticated users can trigger a network-wide DoS or escalate privileges via the Lobby Ambassador API. Patch now.

Jamf Threat Labs uncovers GhostClaw, a macOS threat exploiting GitHub stars and AI workflows to steal credentials. Protect your dev environment today!

Elastic Security Labs uncovers SILENTCONNECT, a stealthy loader using Cloudflare and Google Drive to deliver RMM tools for "hands-on keyboard" attacks.

Synology patches a critical 9.8 CVSS Telnet flaw (CVE-2026-32746). Unauthenticated attackers can hijack your NAS. Update DSM or disable Telnet now!

NVIDIA issues critical updates for Megatron-LM, Triton, and NeMo to fix RCE and DoS flaws. Upgrade now to secure your AI development and inference servers.

Cisco alerts of public flaws in IOx app hosting. Unauthenticated actors can manipulate logs (CVE-2026-20113), plus a stored XSS risk (CVE-2026-20112). Patch now!

A critical flaw in IDrive for Windows (CVE-2026-1995) allows low-privilege users to seize SYSTEM control via weak folder permissions. Audit your PC today.

F5 warns of high-severity flaws in NGINX Plus and Open Source (CVSS 8.8). Fixes for DAV and MP4 buffer overflows are now available. Update your servers today!
Node.js releases critical updates for 20.x to 25.x, fixing high-severity flaws like the __proto__ header crash and TLS errors. Update to v25.8.2 now.

Squid Proxy patches critical 9.2 CVSS DoS and memory leak flaws in ICP. Standard access rules won't block the attack—upgrade to version 7.5 now.

GitLab has released a critical security advisory alongside versions 18.10.1, 18.9.3, and 18.8.7 for its Community (CE)...

NVIDIA patches a critical 9.0 CVSS vulnerability (CVE-2025-33244) in the Apex library. Protect your AI models from RCE—upgrade to PyTorch 2.6+ now.

 cybernewswire

Microsoft resurrects "Project 20/20" to cut Windows 11 memory and storage by 20%. Discover the 2026 plan to ditch WebView2 for a faster, leaner WinUI 3 system.
GoHarbor's Harbor faces a critical 9.4 CVSS flaw (CVE-2026-4404). Default admin passwords allow total registry compromise and image poisoning. Update now.

Full disclosure: Technical details and a GitHub PoC for CVE-2025-39946 are live. This Linux TLS vulnerability allows root escalation via memory shaping.
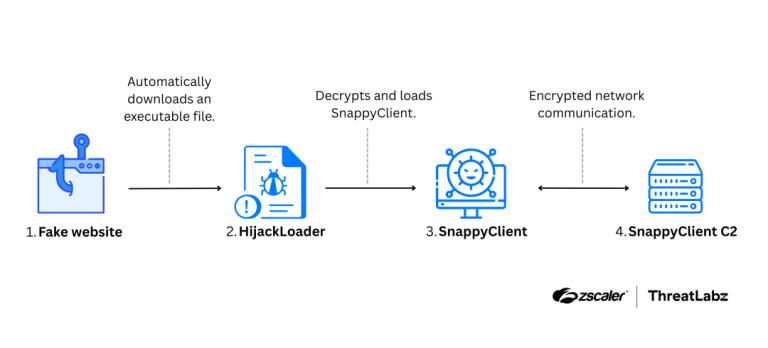
Zscaler ThreatLabz unmasks SnappyClient, a C++ C2 framework linked to HijackLoader. It uses AMSI bypass and Heaven’s Gate to steal crypto and gain remote access.
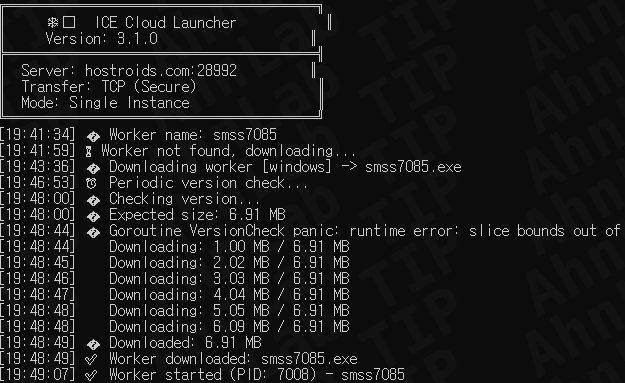
Larva-26002 strikes again with "ICE Cloud," a Go-based scanner using AI-assisted code to hijack MS-SQL servers. Discover the technical breakdown and defense.
AVideo faces a security crisis with 5 unpatched critical flaws (CVSS 10.0). Attackers can hijack streams and execute code. Learn how to protect your server.

OpenAI is shuttering Sora as a standalone product. Discover the 2026 strategic shift toward an AI super-app and the end of the Disney video partnership.
Russia’s Roskomnadzor has blocked Archive.today using DPI technology, while Wikipedia has banned the site over hidden DDoS code. Is the paywall-killer dead?