Skip to content
November 5, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
Beyond the SCSI Bottleneck: How to Unlock the Hidden Native NVMe Driver in Windows 11 Windows 11 native NVMe driver NVMe IOPS performance boost
  • Windows

Beyond the SCSI Bottleneck: How to Unlock the Hidden Native NVMe Driver in Windows 11

Do Son March 25, 2026 0

Boost your SSD speed! Discover how to enable the hidden native NVMe driver in Windows 11 to bypass SCSI translation and supercharge your IOPS performance.

3 Steps to Reduce Phishing MTTR to Minutes in Your SOC Screenshot 2026-03-24 at 13.36.12
  • Technique

3 Steps to Reduce Phishing MTTR to Minutes in Your SOC

Do Son March 25, 2026 0
Phishing no longer needs a fake login page to succeed. Today’s attacks increasingly abuse legitimate services, trusted...
Read More Read more about 3 Steps to Reduce Phishing MTTR to Minutes in Your SOC
VoidStealer Debuts Novel Debugger Bypass for Chrome and Edge Encryption VoidStealer ABE Bypass
  • Malware

VoidStealer Debuts Novel Debugger Bypass for Chrome and Edge Encryption

Do Son March 25, 2026 0

Gen Threat Labs uncovers VoidStealer, the first malware using a debugger-based bypass to extract Chrome and Edge encryption keys via hardware breakpoints.
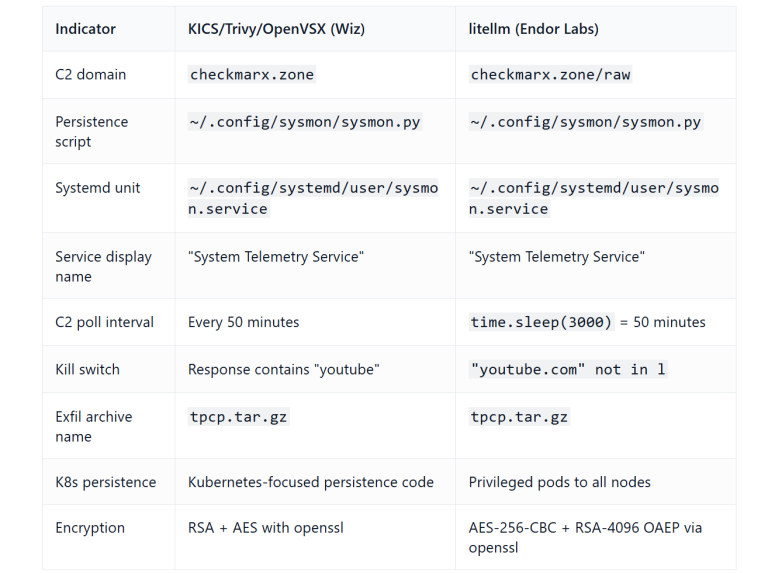
95 Million Downloads Hijacked: The LiteLLM PyPI Backdoor Targeting AI Developers LiteLLM PyPI Supply Chain Attack
  • Malware

95 Million Downloads Hijacked: The LiteLLM PyPI Backdoor Targeting AI Developers

Do Son March 25, 2026 0

95M-download LiteLLM library hijacked on PyPI. TeamPCP's backdoor steals cloud tokens and hijacks Kubernetes clusters. Check for version 1.82.8 now.
From Viewer to SYSTEM: Critical 10.0 CVSS Flaw in GeoVision ERM Allows Full Host Takeover GeoVision CVE-2026-4606 Local Privilege Escalation
  • Vulnerability Report

From Viewer to SYSTEM: Critical 10.0 CVSS Flaw in GeoVision ERM Allows Full Host Takeover

Do Son March 25, 2026 0

GeoVision fixes a critical 10.0 CVSS flaw in GV-Edge Recording Manager. CVE-2026-4606 allows local users to gain SYSTEM-level control. Update to V2.3.2 now.
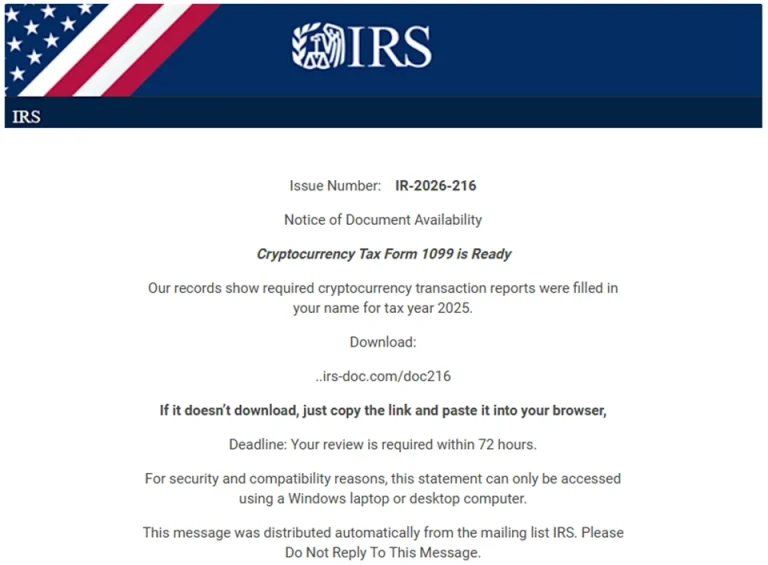
Tax Season Terror: Phishing Campaigns Weaponize Urgency to Deliver Remote Access Tools Tax Phishing ScreenConnect RAT
  • Cybercriminals

Tax Season Terror: Phishing Campaigns Weaponize Urgency to Deliver Remote Access Tools

Do Son March 24, 2026 0

Microsoft warns of a surge in tax-themed phishing using PhaaS and ScreenConnect RATs to bypass MFA and hijack systems. Protect your W-2 data this season.
High-Severity JSON Schema Flaw Threatens MariaDB Database Stability MariaDB Vulnerability JSON Schema Overflow
  • Vulnerability Report

High-Severity JSON Schema Flaw Threatens MariaDB Database Stability

Do Son March 24, 2026 0

MariaDB patches a high-severity buffer overflow (CVE-2026-32710) in its JSON validation function. Upgrade to 11.4.10 or 11.8.6 to prevent server crashes.

PolyShell Alert: Critical Magento REST API Vulnerability Faces Massive Global Exploitation in the Wild PolyShell Magento RCE Magento PolyShell REST API RCE CosmicSting (CVE-2024-34102) Magento Security Updates
  • Vulnerability Report

PolyShell Alert: Critical Magento REST API Vulnerability Faces Massive Global Exploitation in the Wild

Do Son March 24, 2026 0

Active exploitation alert: The PolyShell flaw in the Magento REST API allows unauthenticated RCE via malicious images. Learn how to protect your store now.
The Ransomware ‘Locksmith’: Russian Access Broker Aleksei Volkov Sentenced to 7 Years for $9M Cyber Heist Initial Access Broker Aleksei Volkov
  • Cybercriminals

The Ransomware ‘Locksmith’: Russian Access Broker Aleksei Volkov Sentenced to 7 Years for $9M Cyber Heist

Do Son March 24, 2026 0

Russian national Aleksei Volkov was sentenced to 81 months in prison and ordered to pay $9.1M for his role as an access broker in major U.S. ransomware attacks.

‘Keenadu’ Firmware Backdoor Hijacks Android from the Inside Out Keenadu Malware Android Firmware Backdoor
  • Malware

‘Keenadu’ Firmware Backdoor Hijacks Android from the Inside Out

Do Son March 24, 2026 0

Sophos uncovers Keenadu, a persistent Android firmware backdoor embedded in core libraries that gives attackers total control via the Zygote process.

Checkmarx Alert: Malicious Plugins and GitHub Actions Hit OpenVSX in New Supply Chain Attack GemStuffer RubyGems Campaign RubyGems Data Exfiltration TanStack npm Compromise Supply Chain Attack DNS Hijacking APT28 (Fancy Bear) OpenVSX Supply Chain Attack Checkmarx Plugin Breach Stryker Cyberattack CISA Alert Trans-Regional Cyber Conflict Operation Epic Fury Cyber Operation MacroMaze APT28 Cyber Espionage Notepad++ Supply Chain Attack Lotus Blossom Group Defense Industrial Base Threats GTIG Report APT28 Operation Neusploit CVE-2026-21509 Bookworm Malware
  • Malware

Checkmarx Alert: Malicious Plugins and GitHub Actions Hit OpenVSX in New Supply Chain Attack

Do Son March 24, 2026 0

Checkmarx warns of a supply chain breach on the OpenVSX registry and KICS GitHub Action. Malicious plugins were active briefly on March 23. Update now.
Zuckerberg’s “CEO Agent” and the Dawn of Autonomous AI Conclaves at Meta Meta AI usage limits token minimization strategy, Meta AI budget caps, enterprise AI cost control Meta CEO Agent Mark Zuckerberg MobileLLM-R1, on-device AI Meta Midjourney Meta Pika Labs, AI Video Generation EU AI Regulation, Meta AI Stance Meta AI, PlayAI Acquisition Proactive Chatbots Meta AI, Photo Privacy
  • Technology

Zuckerberg’s “CEO Agent” and the Dawn of Autonomous AI Conclaves at Meta

Do Son March 24, 2026 0

Mark Zuckerberg is building a "CEO Agent" to bypass corporate layers. Discover how Meta's new AI-to-AI conclaves are reshaping the future of management in 2026.
Apple to Launch Search Ads in Maps as Services Revenue Hits $100 Billion Apple Maps advertising update
  • Technology

Apple to Launch Search Ads in Maps as Services Revenue Hits $100 Billion

Do Son March 24, 2026 0

Apple is set to launch search ads in Apple Maps by summer 2026. Discover how Mark Gurman's report links this to a $100B services revenue goal and regulatory pressure.
Bridge or Backdoor? Critical 9.8 RCE Flaw Threatens Helmholz Industrial Networks Helmholz myREX24V2 Industrial RCE
  • Vulnerability Report

Bridge or Backdoor? Critical 9.8 RCE Flaw Threatens Helmholz Industrial Networks

Do Son March 24, 2026 0
Industrial connectivity specialist Helmholz GmbH & Co. KG has issued an urgent security advisory regarding multiple vulnerabilities...
Read More Read more about Bridge or Backdoor? Critical 9.8 RCE Flaw Threatens Helmholz Industrial Networks
Vibe-Coded Fraud: How AI Deepfakes and Digital ‘Cloaking’ Bypass Security to Drain Bank Accounts AI-Generated Scams Digital Cloaking
  • Cybercriminals

Vibe-Coded Fraud: How AI Deepfakes and Digital ‘Cloaking’ Bypass Security to Drain Bank Accounts

Do Son March 24, 2026 0

Infoblox and Confiant reveal a global operation using generative AI deepfakes and commercial "cloaking" tools to scale high-fidelity investment scams.

Gcore Radar report reveals 150% surge in DDoS attacks year-on-year photo_2026-03-19_20-41-31_1_17739279109am8K8aq4r
  • Press Release

Gcore Radar report reveals 150% surge in DDoS attacks year-on-year

cybernewswire March 24, 2026 0
Luxembourg, Luxembourg, 24th March 2026, CyberNewswire
Read More Read more about Gcore Radar report reveals 150% surge in DDoS attacks year-on-year
Master Keys and Open Backdoors: TP-Link Issues Urgent Patch for Archer NX-Series Routers Archer MR600 command injection WireGuard client configuration Tapo smart device vulnerability unencrypted Bluetooth transmission TP-Link router vulnerability CVE-2026-5509 patch Archer AX53 Vulnerability TP-Link Router Security Tapo C520WS Vulnerability TP-Link Security Patch TP-Link Archer NX Router Vulnerability TP-Link Archer Vulnerability CVE-2025-15568 TP-Link Archer BE230 Vulnerability Command Injection TP-Link Omada Vulnerability CVE-2025-9520 TP-Link Archer MR600 Vulnerability CVE-2025-14756 CVE-2026-0629 TP-Link Omada RCE, CVE-2025-6542 TP-Link, Smart plug vulnerability TP-Link Archer C50, Hardcoded DES Key TP-Link NVR, Command Injection TP-Link Routers cybersecurity
  • Vulnerability Report

Master Keys and Open Backdoors: TP-Link Issues Urgent Patch for Archer NX-Series Routers

Do Son March 24, 2026 0

TP-Link releases critical firmware updates for Archer NX200, NX210, NX500, and NX600 models to patch authentication bypass and command injection flaws.

Shattering a 45-Year Tradition: Why Ubuntu 26.04 is Finally Adding Asterisks to Sudo Ubuntu 26.04 sudo-rs Ubuntu 26.04 LTS, Release Schedule Ubuntu update bug, Rust coreutils Ubuntu, sudo-rs NVIDIA CUDA, Ubuntu
  • Linux

Shattering a 45-Year Tradition: Why Ubuntu 26.04 is Finally Adding Asterisks to Sudo

Do Son March 24, 2026 0

Ubuntu 26.04 LTS is moving to sudo-rs and enabling visual password feedback by default. Discover why Canonical is ending 45 years of terminal silence in 2026.

High-Severity Spring Cloud Config Flaw Triggers File Leaks and SSRF Spring Data vulnerabilities Spring Cloud Config CVE-2026-22739 Spring Gateway SpEL, STOMP WebSocket CSRF Spring Security, vulnerability CVE-2024-38819 CVE-2025-41243 Spring Cloud Gateway, vulnerability
  • Vulnerability Report

High-Severity Spring Cloud Config Flaw Triggers File Leaks and SSRF

Do Son March 24, 2026 0

Spring Cloud Config faces a high-severity CVSS 8.6 flaw (CVE-2026-22739). Attackers can manipulate profiles to access local files or launch SSRF attacks.

The Great Disconnection: FCC Bans Foreign-Made Routers in a Massive National Security Crackdown FCC drone router firmware extension 2029 CVE-2024-21833 FCC foreign router ban 2026
  • Technology

The Great Disconnection: FCC Bans Foreign-Made Routers in a Massive National Security Crackdown

Do Son March 24, 2026 0

The FCC has banned the sale of foreign-made consumer routers in the US. Discover how this 2026 mandate affects brands like Netgear and your home internet costs.

Europe’s Cloud Leviathan Pierced: The Alleged 1.6 Million Dossier Exfiltration at OVHcloud OVHcloud data breach 2026
  • Data Leak

Europe’s Cloud Leviathan Pierced: The Alleged 1.6 Million Dossier Exfiltration at OVHcloud

Do Son March 24, 2026 0

Malefactors claim a massive breach of OVHcloud, allegedly stealing 1.6M customer dossiers and 5.9M domain records. Discover the risks to Europe’s cloud giant.

WWDC 2026 Slated to Reveal iOS 27 and the Software Soul of the “iPhone Fold” WWDC 2026 iOS 27
  • Technology

WWDC 2026 Slated to Reveal iOS 27 and the Software Soul of the “iPhone Fold”

Do Son March 24, 2026 0

Apple confirms WWDC 2026 for June 8-12. Explore the debut of iOS 27, the long-awaited "Siri 2.0" chatbot, and software groundwork for the rumored iPhone Fold.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
  • CVE-2023-54413CVSS 6.1
    The WPML plugin for WordPress is vulnerable to Reflected Cross-Site Scripting via the wp_lang parameter in versions up...
    Watchtower Verified📅 Updated: Nov 4, 2026
  • CVE-2024-27834CVSS 5.5
    The issue was addressed with improved checks. This issue is fixed in Safari 17.5, iOS 16.7.8 and iPadOS...
    CISA KEV📅 Added to KEV: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-73996CVSS 9.8
    Unrestricted Upload of File with Dangerous Type vulnerability in ThemeGrill Masteriyo - LMS learning-management-system allows Upload a Web...
    📅 Updated: Nov 5, 2026
  • CVE-2026-100109CVSS 9.8
    The Security For WooCommerce WordPress plugin from 1.0.10 to 1.0.16 does not perform capability checks when creating users...
    📅 Updated: Nov 5, 2026
  • CVE-2026-16438CVSS 9.4
    Incorrect Privilege Assignment vulnerability in Mitsubishi Electric GENESIS64 versions 10.97.3 and prior, ICONICS Suite versions 10.97.3 and prior,...
    📅 Updated: Nov 5, 2026
  • CVE-2026-16436CVSS 9.2
    Weak Password Recovery Mechanism for Forgotten Password vulnerability in Mitsubishi Electric GENESIS versions 11.03 and prior, GENESIS64 versions...
    📅 Updated: Nov 5, 2026
  • CVE-2026-123025CVSS 9.4
    An OS Command Injection vulnerability was discovered in the Google Cloud DNS validation module of the OPNsense os-acme-client...
    📅 Updated: Nov 5, 2026
  • CVE-2026-121241CVSS 9.6
    Use after free in Navigation in Google Chrome on on Android prior to 157.0.8103.38 allowed a remote attacker...
    📅 Updated: Nov 5, 2026
  • CVE-2026-121249CVSS 9.6
    Buffer overflow in ANGLE in Google Chrome prior to 157.0.8103.38 allowed a remote attacker to execute arbitrary code...
    📅 Updated: Nov 5, 2026
  • CVE-2026-121257CVSS 9.6
    Use after free in TabStrip in Google Chrome prior to 157.0.8103.38 allowed a remote attacker to potentially execute...
    📅 Updated: Nov 5, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.