Skip to content
November 6, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
The Rust-Powered Brain: Why OpenAI Just Acquired Astral to Build the First True AI Software Engineer OpenAI confidential IPO filing OpenAI code signing certificate rotation AI private equity joint ventures OpenAI Axios Supply Chain Attack OpenAI Promptfoo acquisition OpenAI military resignation ChatGPT Plus military fraud OpenAI smart speaker Jony Ive OpenAI Frontier platform ChatGPT AI age prediction 2026, OpenAI Persona age verification Sarah Friar OpenAI infrastructure, AI Scaling Law revenue OpenAI Gumdrop AI pen, Jony Ive OpenAI hardware 2027 OpenAI New CRO, Denise Dresser Monetization Strategy OpenAI Competitive Pressure Gemini 3 Overtake OpenAI Infrastructure, AI Closed Loop Economy
  • Technology

The Rust-Powered Brain: Why OpenAI Just Acquired Astral to Build the First True AI Software Engineer

Do Son March 21, 2026 0

OpenAI acquires Astral, the creators of Ruff and uv. Discover how Rust-powered tools will transform Codex from a code generator into a full AI software engineer.

The Death of Open Sideloading? Google’s New “Anti-Fraud Crucible” for Android APKs Android sideloading restrictions 2026
  • Android

The Death of Open Sideloading? Google’s New “Anti-Fraud Crucible” for Android APKs

Do Son March 21, 2026 0

Google's 2026 "Anti-Fraud Crucible" introduces a 24-hour wait and mandatory reboots for sideloading. Discover how Limited Distribution Accounts save hobbyists.

Critical 9.3 CVSS Flaws Uncovered in Netwrix Password Secure Netwrix Vulnerability Password Secure
  • Vulnerability Report

Critical 9.3 CVSS Flaws Uncovered in Netwrix Password Secure

Do Son March 21, 2026 0

Netwrix issues an urgent advisory for critical vulnerabilities in its Password Secure platform allowing arbitrary code execution. Update to v26.3.100 now.

Critical 9.3 CVSS Flaw in QNAP QVR Pro Exposes Surveillance Systems QNAP QVR Pro Vulnerability CVE-2026-22898 CVE-2022-27595 - CVE-2024-48860 & CVE-2024-48861
  • Vulnerability Report

Critical 9.3 CVSS Flaw in QNAP QVR Pro Exposes Surveillance Systems

Do Son March 21, 2026 0

QNAP warns of a critical 9.3 CVSS flaw (CVE-2026-22898) allowing remote attackers to bypass authentication and access QVR Pro surveillance systems. Patch now.

Critical 9.8 CVSS Flaw Exposes Oracle Identity Manager to Total Takeover IRGC Oracle Cloud Dubai strike Oracle global layoffs 2026 Oracle Fusion Middleware Vulnerability CVE-2026-21992 Oracle Edge Cloud Vulnerability CVE-2026-21994 Oracle Critical RCE, EBS Marketing Flaws CVE-2024-21182 PoC Exploit Oracle EBS Auth Bypass, CVE-2025-61884
  • Vulnerability Report

Critical 9.8 CVSS Flaw Exposes Oracle Identity Manager to Total Takeover

Do Son March 21, 2026 0

Oracle warns of a critical 9.8 CVSS vulnerability (CVE-2026-21992) allowing unauthenticated attackers to take over Fusion Middleware and Identity Manager.

Weaponizing gcc: Inside the Stealthy ‘Hex’ Botnet’s On-Host Compilation Strategy Hex Botnet On-Host Compilation
  • Malware

Weaponizing gcc: Inside the Stealthy ‘Hex’ Botnet’s On-Host Compilation Strategy

Do Son March 21, 2026 0

Hunt Intelligence uncovers the "Hex" botnet, a stealthy campaign using stolen SSH credentials and on-host compilation to evade traditional binary scanners.

PoC Exploit Publicly Disclosed: Apple Deploys First-Ever Background Security Patch for Cross-Origin Flaw Apple Background Security CVE-2026-20643 Apple Background Security Improvement Apple Backdoor Apple Lawsuit, Data Exfiltration CVE-2024-44131 - CVE-2025-24118 PoC
  • Vulnerability Report

PoC Exploit Publicly Disclosed: Apple Deploys First-Ever Background Security Patch for Cross-Origin Flaw

Do Son March 21, 2026 0

PoC exploit code is now public for CVE-2026-20643. Apple issues its first Background Security Improvement to fix this cross-origin Navigation API flaw.

Two High-Severity Spring Boot Flaws Expose Actuator Endpoints Spring Cloud Config Vulnerability CVE-2026-40982 Spring Boot Vulnerability CVSS 9.1 Bypass CVE-2022-31692 Spring Boot Vulnerability Authentication Bypass
  • Vulnerability Report

Two High-Severity Spring Boot Flaws Expose Actuator Endpoints

Do Son March 20, 2026 0

Two high-severity flaws (CVE-2026-22731 & CVE-2026-22733) in Spring Boot Actuators allow authentication bypass. Update your framework today to stay secure.

New Mirai Variant and “Monaco” Miner Targeting Linux Devices Linux Malware CondiBot
  • Malware

New Mirai Variant and “Monaco” Miner Targeting Linux Devices

Do Son March 20, 2026 0

Eclypsium uncovers two new Linux malware strains: a CondiBot DDoS variant and the Monaco SSH cryptominer targeting servers and IoT. Secure your network.

PoC Exploit Publicly Disclosed: Windows ‘libarchive’ Flaw Leaks NetNTLMv2 Hashes Windows libarchive Flaw CVE-2025-59284
  • Vulnerability Report

PoC Exploit Publicly Disclosed: Windows ‘libarchive’ Flaw Leaks NetNTLMv2 Hashes

Do Son March 20, 2026 0

Exploit code and details for CVE-2025-59284 are now public. Discover how a Windows libarchive flaw leaks NetNTLMv2 hashes via malicious .tar archives.

High-Severity ingress-nginx Flaw Exposes Kubernetes Secrets CVE-2024-9042 ingress-nginx Vulnerability CVE-2026-4342
  • Vulnerability Report

High-Severity ingress-nginx Flaw Exposes Kubernetes Secrets

Do Son March 20, 2026 0

A high-severity 8.8 CVSS flaw (CVE-2026-4342) in ingress-nginx allows attackers to inject malicious code and steal Kubernetes Secrets. Patch immediately.

Engineering-First List: Top California Software Development Companies Andariel APT
  • Technique

Engineering-First List: Top California Software Development Companies

Do Son March 20, 2026 0

Compare California software development companies by AI/ML & DevOps capabilities, and delivery model. Profiles, pricing, and a framework to make the right call.

Game Over: Vidar Stealer 2.0 is Hijacking Gamers with Fake Cheats DriverFixer0428, Contagious Interview Cache Smuggling, ClickFix Evasion North Korean Cyber Espionage
  • Malware

Game Over: Vidar Stealer 2.0 is Hijacking Gamers with Fake Cheats

Do Son March 20, 2026 0

Acronis uncovers a massive campaign targeting gamers with fake cheats to deliver Vidar Stealer 2.0, a highly evasive malware stealing crypto and passwords.

The Invisible Breach: ‘Operation GhostMail’ Uses Zero-Click XSS to Hijack Ukrainian Webmail Operation GhostMail Zero-Click XSS
  • Cyber Security

The Invisible Breach: ‘Operation GhostMail’ Uses Zero-Click XSS to Hijack Ukrainian Webmail

Do Son March 20, 2026 0

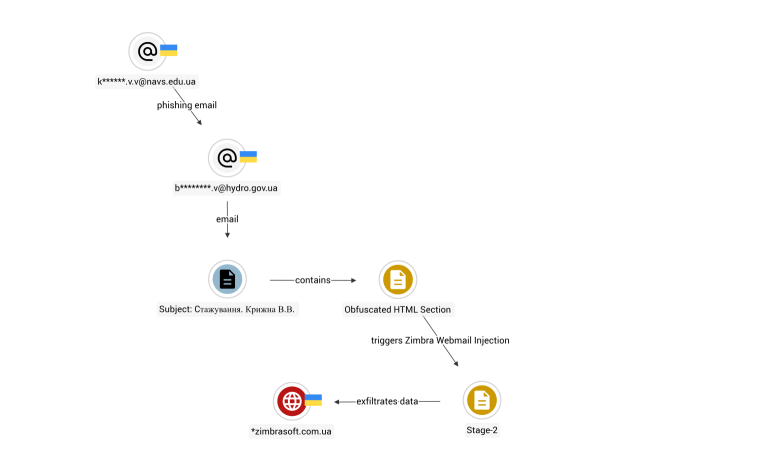
Seqrite Labs uncovers Operation GhostMail, an APT28-linked campaign using a zero-click XSS flaw in Zimbra to silently hijack Ukrainian government webmail.

Developer Alert: “CursorJack” Technique Weaponizes Deeplinks to Hijack Cursor IDE CursorJack Cursor Vulnerability
  • Vulnerability Report

Developer Alert: “CursorJack” Technique Weaponizes Deeplinks to Hijack Cursor IDE

Do Son March 20, 2026 0

Proofpoint details 'CursorJack', a novel exploit using malicious MCP deeplinks in the Cursor AI editor to execute arbitrary code on developer machines.

Operation Takedown: DOJ and Global Allies Smash 30-Terabit IoT Botnet Empire P2P cryptominer malware threat Ollama endpoint attacks IoT Botnets DDoS Attacks
  • Malware

Operation Takedown: DOJ and Global Allies Smash 30-Terabit IoT Botnet Empire

Do Son March 20, 2026 0

The US DOJ, alongside Canada and Germany, has dismantled four massive IoT botnets responsible for record-breaking 30 Tbps DDoS attacks worldwide.

The AI-Powered Arsenal: How ‘Forbidden Hyena’ Uses Generative AI to Spawn BlackReaperRAT Forbidden Hyena BlackReaperRAT
  • Cybercriminals

The AI-Powered Arsenal: How ‘Forbidden Hyena’ Uses Generative AI to Spawn BlackReaperRAT

Do Son March 20, 2026 0

BI.ZONE uncovers Forbidden Hyena using AI-generated code to deploy the new BlackReaperRAT and Milkyway ransomware in highly evasive cyberattacks.

The Silent Leak: Critical 9.1 CVSS Spring Security Flaw Strips Away Vital HTTP Headers CVE-2024-22234 Spring Security Vulnerability CVE-2026-22732
  • Vulnerability Report

The Silent Leak: Critical 9.1 CVSS Spring Security Flaw Strips Away Vital HTTP Headers

Do Son March 20, 2026 0

A critical 9.1 CVSS flaw in Spring Security (CVE-2026-22732) fails to write HTTP headers, exposing Java apps to severe data leaks. Update immediately.

Takedown: DOJ Seizes Iranian MOIS Domains Used for Global Hacking and Hit Squad Threats Iranian Cyberwarfare DOJ Domain Seizure
  • Cybercriminals

Takedown: DOJ Seizes Iranian MOIS Domains Used for Global Hacking and Hit Squad Threats

Do Son March 20, 2026 0

The US DOJ has seized four domains used by Iran's MOIS to orchestrate global cyberwarfare, doxing, and death threats against dissidents and governments.

Bypassed Boundaries: Two New Vulnerabilities Threaten Spring Framework Apps CVE-2024-22259 Spring Framework Vulnerabilities CVE-2026-22737
  • Vulnerability Report

Bypassed Boundaries: Two New Vulnerabilities Threaten Spring Framework Apps

Do Son March 20, 2026 0

Researchers found two flaws in Spring Framework (CVE-2026-22737 & CVE-2026-22735) allowing path bypasses and stream corruption. Patch your apps today.

Urgent Patch: Massive Google Chrome Update Patches 26 Flaws, Including 3 Critical Bugs Chrome Security Update Critical Vulnerabilities
  • Vulnerability Report

Urgent Patch: Massive Google Chrome Update Patches 26 Flaws, Including 3 Critical Bugs

Do Son March 20, 2026 0

Google releases an urgent Chrome update patching 26 security flaws, including 3 critical WebGL and Base vulnerabilities. Update to version 146 today.

The Typosquatting Trap: Fake Telegram Portal Delivers Stealthy Memory-Resident Malware kill chain
  • Malware

The Typosquatting Trap: Fake Telegram Portal Delivers Stealthy Memory-Resident Malware

Do Son March 20, 2026 0

Researchers uncover a fake Telegram site distributing stealthy, memory-resident malware that bypasses Windows Defender. Always verify your download URLs.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-59104CVSS 9.3
    UgCS server before 6.2 contains an authentication bypass in the HCI protocol login handler (LoginHandler) exposed on TCP...
    📅 Updated: Nov 6, 2026
  • CVE-2026-54143CVSS 9.8
    OpenHuman is an open-source agent harness available as a desktop application and Rust library. Before version 0.57.13, an...
    📅 Updated: Nov 6, 2026
  • CVE-2026-54141CVSS 9.0
    OpenHuman is an open-source agent harness available as a desktop application and Rust library. Before 0.57.13, a remote...
    📅 Updated: Nov 6, 2026
  • CVE-2026-77596CVSS 9.6
    Kubeflow Pipelines enables users to build and deploy portable, scalable machine learning workflows. Prior to 2.18.0, the multi-user...
    📅 Updated: Nov 6, 2026
  • CVE-2026-102940CVSS 9.6
    OpenEMR is a free and open source electronic health records and medical practice management application. Prior to 8.4.0,...
    📅 Updated: Nov 6, 2026
  • CVE-2026-123279CVSS 9.0
    In JetBrains Datalore before 2026.4 code execution was possible in a notebook's computation by view-only collaborators
    📅 Updated: Nov 6, 2026
  • CVE-2026-123294CVSS 9.6
    In JetBrains Hub before 2026.2.52556 privilege escalation was possible by changing email authentication details during the verification flow
    📅 Updated: Nov 6, 2026
  • CVE-2026-123831CVSS 9.6
    In JetBrains CLion before 2026.2, 2026.1.4 code execution was possible in Safe Mode via Meson project settings
    📅 Updated: Nov 6, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.