Skip to content
November 7, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
The ‘Must-Patch’ Release: WordPress 6.9.2 Scrambles to Fix 10 Critical Flaws from XSS to SSRF WordPress 6.9.2 WordPress 6.9.2 WordPress Security Update WordPress Security Update WordPress.org Suspended
  • Vulnerability Report

The ‘Must-Patch’ Release: WordPress 6.9.2 Scrambles to Fix 10 Critical Flaws from XSS to SSRF

Do Son March 11, 2026 0

Urgent: WordPress 6.9.2 patches 10 critical security flaws, including XSS, SSRF, and path traversal. Update your site immediately to prevent exploitation.

High-Severity SQL Injection in Ally WordPress Plugin Threatens 400K Sites Ally Plugin Vulnerability SQL Injection
  • Vulnerability Report

High-Severity SQL Injection in Ally WordPress Plugin Threatens 400K Sites

Do Son March 11, 2026 0

A critical SQL injection flaw (CVE-2026-2413) in the Ally WordPress plugin exposes 400K+ sites to database theft. Update to version 4.1.0 immediately.

The Default Danger: Maximum 10.0 CVSS Vulnerability Leaves Honeywell IQ4x Controllers Wide Open Fortra BoKS vulnerability OS command injection, CVE-2026-9862 Altium Enterprise Server Vulnerability CVE-2026-9129 Path Traversal Patreon OAuth Vulnerability Identity Collision DRC INSIGHT Vulnerability Exam Data Hijacking Horner Automation PLC Industrial Brute Force Honeywell IQ4x Vulnerability CVE-2026-3611 DJI Romo vacuum security flaw Python Cryptography Vulnerability CVE-2026-26007 Open5GS Vulnerability CVE-2026-0622 Vivotek IP7137 Vulnerabilities CVE-2025-66049 Forcepoint DLP Vulnerability CVE-2025-14026 Cellopoint Secure Email Gateway - CVE-2024-9043
  • Vulnerability Report

The Default Danger: Maximum 10.0 CVSS Vulnerability Leaves Honeywell IQ4x Controllers Wide Open

Do Son March 11, 2026 0

A critical 10.0 CVSS flaw (CVE-2026-3611) in Honeywell IQ4x BMS controllers leaves web HMIs exposed without authentication. Secure your systems immediately.
Industrial Alert: Critical Stored XSS Vulnerability Discovered in Siemens SIMATIC S7-1500 Siemens SIMATIC Vulnerability CVE-2025-40943 CVE-2024-47901 - Siemens InterMesh system CVE-2025-40804 Siemens SIVaaS
  • Vulnerability Report

Industrial Alert: Critical Stored XSS Vulnerability Discovered in Siemens SIMATIC S7-1500

Do Son March 11, 2026 0

A critical 9.6 CVSS XSS vulnerability (CVE-2025-40943) in Siemens SIMATIC S7-1500 CPUs allows attackers to inject malicious code via trace files.

Microsoft Patch Tuesday March 2026: 93 Vulnerabilities Addressed, Including Two Zero-Days Microsoft Patch Tuesday fixes disclosed zero day vulnerabilities Windows Wormable Exploit April 2026 Patch Tuesday Microsoft Patch Tuesday Zero-Day Vulnerabilities Microsoft, Patch Tuesday CVE-2025-55234 CVE-2024-43573 and CVE-2024-43572 Microsoft Patch Tuesday Security Vulnerabilities
  • Vulnerability Report

Microsoft Patch Tuesday March 2026: 93 Vulnerabilities Addressed, Including Two Zero-Days

Do Son March 11, 2026 0

Microsoft's March 2026 Patch Tuesday addresses 93 vulnerabilities, including two public zero-days affecting SQL Server and .NET. Patch your systems now.

Maximum 10.0 CVSS Flaws in OneUptime Allow Full Account Takeovers and RCE OneUptime Vulnerabilities CVE-2026-30956
  • Vulnerability Report

Maximum 10.0 CVSS Flaws in OneUptime Allow Full Account Takeovers and RCE

Do Son March 11, 2026 0

Two critical 10.0 CVSS flaws (CVE-2026-30956, CVE-2026-30957) in OneUptime allow full account takeovers and Server-Side RCE. Update to 10.0.21 immediately.
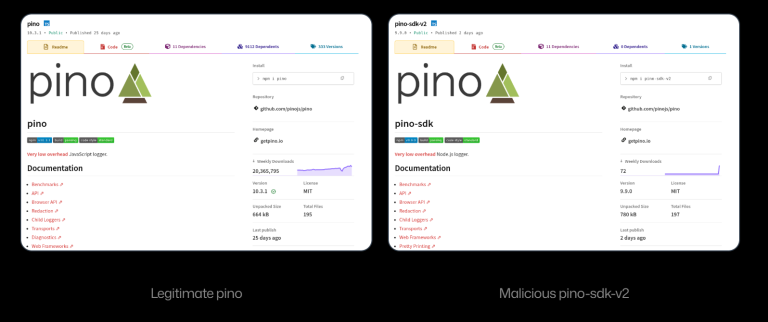
Malicious npm Package “pino-sdk-v2” Caught Harvesting Secrets pino-sdk-v2 npm Supply Chain Attack
  • Malware

Malicious npm Package “pino-sdk-v2” Caught Harvesting Secrets

Do Son March 11, 2026 0

SafeDep uncovers pino-sdk-v2, a malicious npm package impersonating the pino logger to silently steal .env secrets and exfiltrate them via Discord.
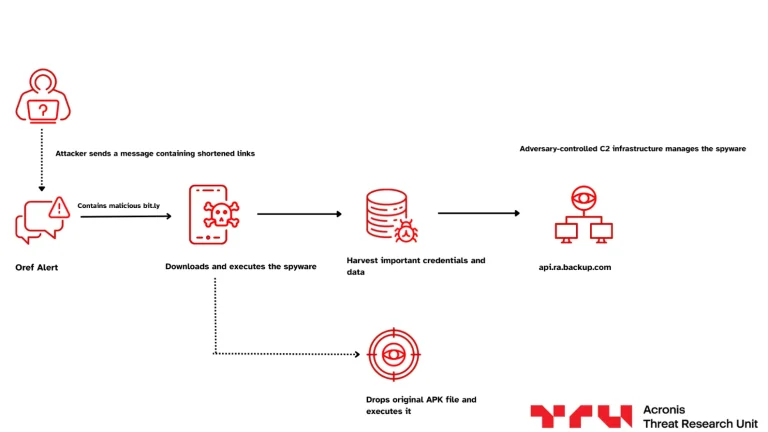
APT-C-23 Weaponized Israel’s ‘Red Alert’ App for Mobile Espionage Red Alert Trojan APT-C-23
  • Cybercriminals

APT-C-23 Weaponized Israel’s ‘Red Alert’ App for Mobile Espionage

Do Son March 11, 2026 0

Acronis TRU uncovers a trojanized Red Alert rocket warning app targeting Israelis. Linked to APT-C-23, this Android malware steals data while alerting users.
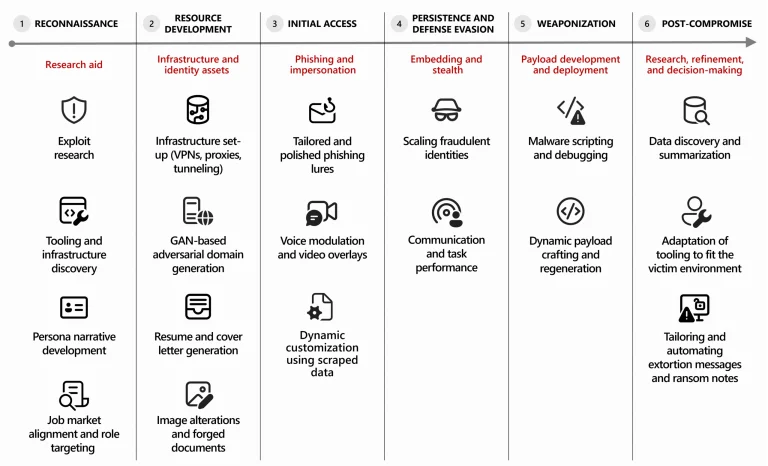
Microsoft Exposes How Hackers Use Generative Models as a Force Multiplier Malicious AI AI Memory Poisoning
  • Cybercriminals

Microsoft Exposes How Hackers Use Generative Models as a Force Multiplier

Do Son March 11, 2026 0

Microsoft Threat Intelligence reveals how cybercriminals and North Korean APTs are weaponizing generative AI to scale attacks and poison AI assistants.
The Vibe-Coding Trap: Fake Claude Code Installers Unleash Amatera Malware via Search Ads Claude Code Malvertising Amatera Malware
  • Malware

The Vibe-Coding Trap: Fake Claude Code Installers Unleash Amatera Malware via Search Ads

Do Son March 11, 2026 0

Hackers are targeting AI developers with a fake Claude Code "InstallFix" malvertising campaign, using malicious terminal commands to drop Amatera malware.

Zscaler Uncovers 8,000+ Domains and APT Backdoors Exploiting Middle East Tensions Middle East Cyber Threats
  • Cybercriminals

Zscaler Uncovers 8,000+ Domains and APT Backdoors Exploiting Middle East Tensions

Do Son March 11, 2026 0

Zscaler ThreatLabz reveals a surge in Middle East conflict-themed cyberattacks, uncovering 8,000+ malicious domains, LOTUSLITE backdoors, and scams.
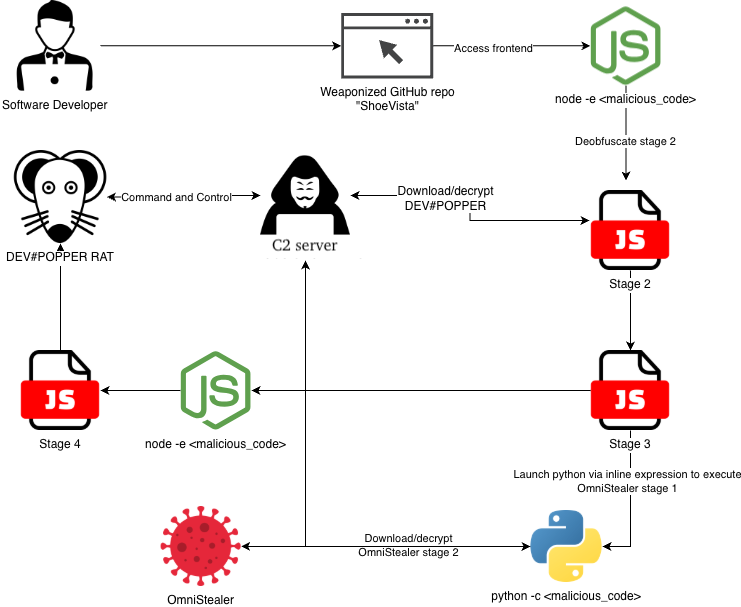
North Korean APT Unleashes DEV#POPPER RAT via GitHub to Drain Crypto Wallets DEV#POPPER OmniStealer
  • Malware

North Korean APT Unleashes DEV#POPPER RAT via GitHub to Drain Crypto Wallets

Do Son March 11, 2026 0

eSentire exposes DEV#POPPER, a North Korean RAT hiding in GitHub repos. It uses blockchain to deploy OmniStealer, targeting crypto and dev secrets.
CL-UNK-1068: The Stealthy Chinese Threat Actor Haunting Asian Infrastructure CL-UNK-1068 Chinese APT
  • Cybercriminals

CL-UNK-1068: The Stealthy Chinese Threat Actor Haunting Asian Infrastructure

Do Son March 11, 2026 0

Unit 42 uncovers CL-UNK-1068, a Chinese APT targeting Asian critical infrastructure using stealthy web shells, LOLBINs, and screen-printed exfiltration.

Critical RCE Vulnerabilities Uncovered in Janitza and Weidmueller Energy Meters Energy Meter RCE CVE-2025-41709 ICS Exposure, Power Grid Security CVE-2025-1393 & CVE-2024-23943
  • Vulnerability Report

Critical RCE Vulnerabilities Uncovered in Janitza and Weidmueller Energy Meters

Do Son March 11, 2026 0

Critical flaws (CVE-2025-41709) in Janitza and Weidmueller energy meters allow remote code execution and full system takeover. Update to firmware 3.14 now.
Unauthenticated Takeover: Critical 9.6 CVSS Zoom Flaw Exposes Windows Users to Remote Privilege Escalation CVE-2022-36926 Zoom Vulnerability CVE-2026-30903
  • Vulnerability Report

Unauthenticated Takeover: Critical 9.6 CVSS Zoom Flaw Exposes Windows Users to Remote Privilege Escalation

Do Son March 10, 2026 0

Zoom patches a critical 9.6 CVSS flaw (CVE-2026-30903) allowing unauthenticated remote privilege escalation on Windows. Update your clients immediately.
The ‘Must-Patch’ List: CISA Adds Actively Exploited SolarWinds, Ivanti, and Omnissa Flaws to KEV CISA active exploit catalog known exploited vulnerabilities ActiveMQ RCE CVE-2026-34197 CISA KEV Catalog Actively Exploited Vulnerabilities CISA KEV Catalog CVE-2025-37164 GeoServer XXE, CISA KEV FortiWeb SQLi, CISA KEV Critical Vulnerabilities CVE-2024-20953
  • Vulnerability Report

The ‘Must-Patch’ List: CISA Adds Actively Exploited SolarWinds, Ivanti, and Omnissa Flaws to KEV

Do Son March 10, 2026 0

CISA adds three actively exploited flaws in SolarWinds, Ivanti, and Omnissa to its KEV catalog. Patch these critical enterprise vulnerabilities immediately.
The Silent Rhythm: How BeatBanker Malware Uses a Looping Audio File to Hijack Android Devices BeatBanker Android Malware
  • Malware

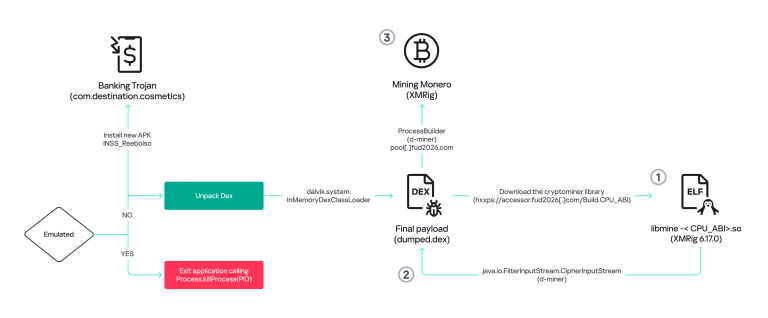
The Silent Rhythm: How BeatBanker Malware Uses a Looping Audio File to Hijack Android Devices

Do Son March 10, 2026 0

Kaspersky uncovers BeatBanker, an Android malware in Brazil using an audio loop to evade detection while mining crypto and stealing banking credentials.
Leading Myanmar Fleet Management Company Yoma Fleet Selects AccuKnox SIEM to Replace Legacy Tools Screenshot_2026-03-10_at_122108_1773131171NfYbS8nzTq
  • Press Release

Leading Myanmar Fleet Management Company Yoma Fleet Selects AccuKnox SIEM to Replace Legacy Tools

cybernewswire March 10, 2026 0
Menlo Park, USA, 10th March 2026, CyberNewswire
Read More Read more about Leading Myanmar Fleet Management Company Yoma Fleet Selects AccuKnox SIEM to Replace Legacy Tools
How a Professional Headshot Closes More Clients Before You Even Speak Fractile AI inference chip AI Market Trends 2025, Similarweb AI Report
  • Technique

How a Professional Headshot Closes More Clients Before You Even Speak

Do Son March 10, 2026 0
In the gig economy, your face is your brand. Before a prospect reads your proposal, scrolls through...
Read More Read more about How a Professional Headshot Closes More Clients Before You Even Speak
Dutch Intelligence Warning: Russian State Actors Targeting Signal and WhatsApp WhatsApp Worm, Brazilian Banking Trojan LAPSUS$ Alliance, Scattered Spider Ransomware, Cybercrime RedCurl APT group Russian Cyberespionage, ApolloShadow Malware
  • Cybercriminals

Dutch Intelligence Warning: Russian State Actors Targeting Signal and WhatsApp

Do Son March 10, 2026 0

Dutch intelligence (MIVD/AIVD) warns of a global campaign using social engineering to silently hijack Signal and WhatsApp accounts of high-profile targets.

Critical Alert: SAP’s Latest Security Update Fixes 9.8 CVSS RCE and Deserialization Flaws SAP Security Patches CVE-2026-27685 SAP Security Update CVE-2026-0488 CVE-2024-47578 - CVE-2025-0070 and CVE-2025-0066
  • Vulnerability Report

Critical Alert: SAP’s Latest Security Update Fixes 9.8 CVSS RCE and Deserialization Flaws

Do Son March 10, 2026 0

SAP's latest security update addresses 15 flaws, including critical RCE (CVE-2019-17571) and deserialization (CVE-2026-27685) vulnerabilities. Patch now.

Exploiting the Crisis: Chinese APTs Weaponize Middle East Tensions to Target Qatar with PlugX NATS-as-C2 Sysdig CVE-2026-33017 Langflow RCE Microsoft Phone Link Hijack CloudZ Pheno Plugin Insider Threat BlackCat (ALPHV) OFAC Sanctions DPRK IT Workers Transparent Tribe APT36 React2Shell, EtherRAT SideWinder Espionage, Netlify Phishing DDNS Abuse, C2 Infrastructure Hacking Health Club
  • Cyber Security
  • Malware

Exploiting the Crisis: Chinese APTs Weaponize Middle East Tensions to Target Qatar with PlugX

Do Son March 10, 2026 0

Chinese APTs like Camaro Dragon are targeting Qatar with PlugX malware and Cobalt Strike, weaponizing Middle East tensions for cyberespionage.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-59104CVSS 9.3
    UgCS server before 6.2 contains an authentication bypass in the HCI protocol login handler (LoginHandler) exposed on TCP...
    📅 Updated: Nov 6, 2026
  • CVE-2026-54143CVSS 9.8
    OpenHuman is an open-source agent harness available as a desktop application and Rust library. Before version 0.57.13, an...
    📅 Updated: Nov 6, 2026
  • CVE-2026-54141CVSS 9.0
    OpenHuman is an open-source agent harness available as a desktop application and Rust library. Before 0.57.13, a remote...
    📅 Updated: Nov 6, 2026
  • CVE-2026-77596CVSS 9.6
    Kubeflow Pipelines enables users to build and deploy portable, scalable machine learning workflows. Prior to 2.18.0, the multi-user...
    📅 Updated: Nov 6, 2026
  • CVE-2026-102940CVSS 9.6
    OpenEMR is a free and open source electronic health records and medical practice management application. Prior to 8.4.0,...
    📅 Updated: Nov 6, 2026
  • CVE-2026-123279CVSS 9.0
    In JetBrains Datalore before 2026.4 code execution was possible in a notebook's computation by view-only collaborators
    📅 Updated: Nov 6, 2026
  • CVE-2026-123294CVSS 9.6
    In JetBrains Hub before 2026.2.52556 privilege escalation was possible by changing email authentication details during the verification flow
    📅 Updated: Nov 6, 2026
  • CVE-2026-123831CVSS 9.6
    In JetBrains CLion before 2026.2, 2026.1.4 code execution was possible in Safe Mode via Meson project settings
    📅 Updated: Nov 6, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.