Skip to content
November 7, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
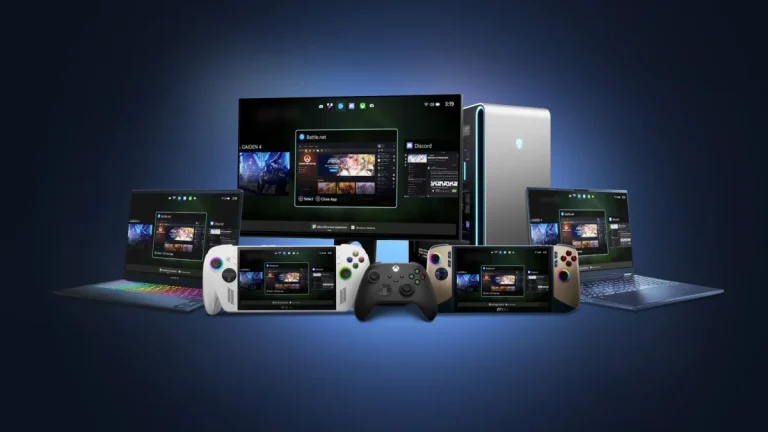
The “Helix” Horizon: Microsoft Transforms Windows 11 Into a Console With “Xbox Mode” Xbox Project Helix Xbox Mode Windows 11
  • Windows

The “Helix” Horizon: Microsoft Transforms Windows 11 Into a Console With “Xbox Mode”

Do Son March 13, 2026 0

Microsoft’s new "Xbox Mode" brings a full-screen, controller-first console experience to all Windows 11 PCs this April. Say goodbye to shader stutter in 2026.

Double Zero-Day Threat: Emergency Chrome Update Patches Actively Exploited Skia and V8 Flaws Chrome security update exploit in the wild Chrome Zero-Day CVE-2026-3909 Chrome Zero-Day PoC CVE-2026-2441 Chrome Zero-Day CVE-2026-2441 Chrome Zero-Day, Active Exploitation CVE-2025-10585 Chrome vulnerability, zero-day exploit CVE-2025-6558 Chrome Zero-Day, V8 Vulnerability Chrome Zero-Day, Security Update
  • Vulnerability Report

Double Zero-Day Threat: Emergency Chrome Update Patches Actively Exploited Skia and V8 Flaws

Do Son March 12, 2026 0

Google releases an emergency Chrome update to patch two actively exploited zero-day vulnerabilities (CVE-2026-3909 & CVE-2026-3910). Update immediately.
The $32 Billion Fortress: Google Completes Historic Wiz Acquisition to Solve the “AI-Native” Risk Google Wiz acquisition 2026
  • Technology

The $32 Billion Fortress: Google Completes Historic Wiz Acquisition to Solve the “AI-Native” Risk

Do Son March 12, 2026 0

Google has finalized its $32B acquisition of Wiz, the largest in its history. Discover how this "code-to-cloud" platform secures AI in a multi-cloud world.

The Silicon Schism: Google Deploys 3 Million AI Agents to the Pentagon as Anthropic Faces Exile AI Overviews opt out Google Gemini Pentagon contract Penske Media, AI Overviews
  • Technology

The Silicon Schism: Google Deploys 3 Million AI Agents to the Pentagon as Anthropic Faces Exile

Do Son March 12, 2026 0

Google has deployed Gemini AI agents to 3 million Pentagon staff following a fallout with Anthropic. Discover the ethics shift and the new "GenAI.mil" portal.
Beyond the Formula: ChatGPT’s New “Dynamic Visuals” Turn Equations Into Interactive Sandboxes ChatGPT Dynamic Visual Explanations
  • Technology

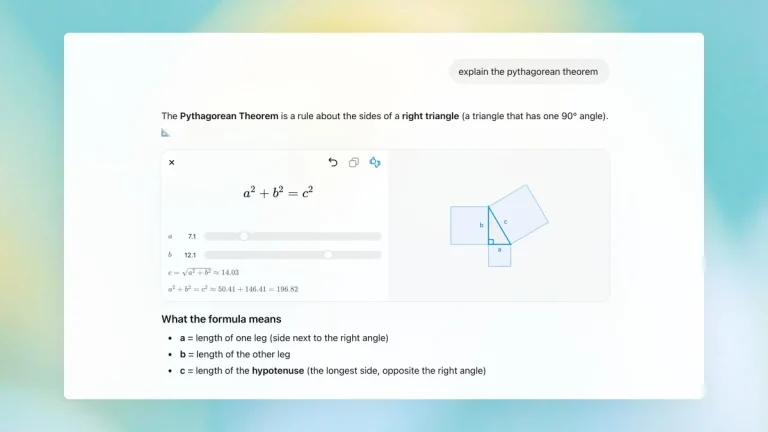
Beyond the Formula: ChatGPT’s New “Dynamic Visuals” Turn Equations Into Interactive Sandboxes

Do Son March 12, 2026 0

ChatGPT’s new "Dynamic Visual Explanations" let you manipulate variables in real-time diagrams for 70+ math and science concepts. No more static formulas.

Agentic War: Amazon Secures Landmark Injunction to Block Perplexity’s AI Shopping Bot Motorola Smart Feed redirect Anthropic Amazon 5GW partnership Amazon Perplexity lawsuit AWS-LC Vulnerabilities Cryptographic Bypass AWS Middle East drone strikes Amazon layoffs 2026, Amazon AI restructuring Amazon Kindle DRM Policy, Publisher Control EPUB AWS Nova Forge AI Model Customization AWS Trainium3 EC2 Trn3 UltraServer Route 53 Accelerated Recovery AWS DNS Resilience AI Browser War, Amazon Comet Amazon layoffs, cost reduction AWS outage, DynamoDB DNS AWS outage, cloud dependency AWS VPN Client, Root Privilege Escalation WSA shutdown, Amazon Appstore Amazon Wondery, Podcast Restructuring Amazon Q2 2025 Generative AI AWS Client VPN, Privilege Escalation Amazon AI, Wearable AI
  • Technology

Agentic War: Amazon Secures Landmark Injunction to Block Perplexity’s AI Shopping Bot

Do Son March 12, 2026 0

A San Francisco judge has blocked Perplexity’s Comet AI from buying on Amazon. Learn how this 2026 ruling defines the legal boundaries of agentic AI commerce.
One Vector to Rule Them All: How Gemini Embedding 2 Unifies Text, Audio, and Video Gemini Embedding 2
  • Technology

One Vector to Rule Them All: How Gemini Embedding 2 Unifies Text, Audio, and Video

Do Son March 12, 2026 0

Google DeepMind’s Gemini Embedding 2 is here. Map text, images, 120s of video, and native audio into one vector space to revolutionize multimodal RAG and search.
The Mutable Tag Trap: Critical 9.4 CVSS Attack on Xygeni GitHub Action Exposes CI/CD Pipelines Xygeni Tag Poisoning CVE-2026-31976
  • Malware
  • Vulnerability Report

The Mutable Tag Trap: Critical 9.4 CVSS Attack on Xygeni GitHub Action Exposes CI/CD Pipelines

Do Son March 12, 2026 0

A critical 9.4 CVSS tag poisoning attack (CVE-2026-31976) hit the xygeni-action GitHub Action, injecting a C2 backdoor into CI/CD pipelines. Update now.
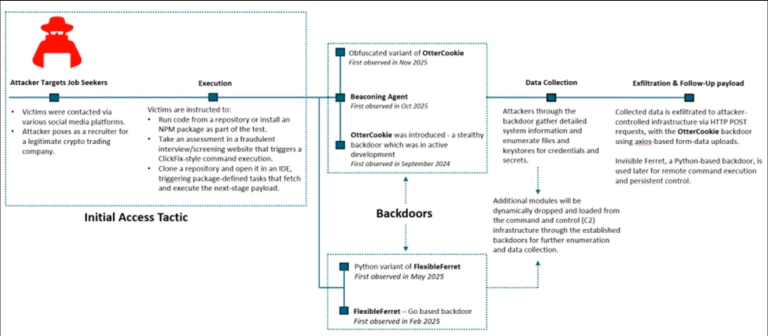
The Fake Job Trap: Microsoft Exposes the ‘Contagious Interview’ Campaign Targeting Developers Contagious Interview Invisible Ferret
  • Cybercriminals

The Fake Job Trap: Microsoft Exposes the ‘Contagious Interview’ Campaign Targeting Developers

Do Son March 12, 2026 0

Microsoft exposes the "Contagious Interview" campaign. Fake recruiters trick developers into installing Invisible Ferret malware during coding tests.
CISA Mandates Urgent Patch for Maximum 10.0 CVSS n8n RCE Flaw n8n RCE Vulnerability CVE-2025-68613 CISA KEV WinRAR Zero-Day, Cloud Files UAF OpenPLC ScadaBR, CVE-2021-26829 CISA KEV, Gladinet LFI RCE XWiki RCE, VMware EoP CISA KEV CISA, Known Exploited Vulnerabilities CVE-2020-2883 CISA, Trend Micro
  • Vulnerability Report

CISA Mandates Urgent Patch for Maximum 10.0 CVSS n8n RCE Flaw

Do Son March 12, 2026 0

CISA warns of a critical 10.0 CVSS RCE flaw (CVE-2025-68613) in n8n workflow automation. Update to version 1.122.0 immediately to prevent server takeover.

High-Privilege Havoc: Splunk Patches RCE Flaw Lurking in File Previews Splunk Enterprise vulnerabilities, CVSS 9.8 flaw, CVE-2026-20253, CVE-2026-20251, CVE-2026-20258 Splunk Enterprise Vulnerabilities CVE-2026-20240 Splunk RCE CVE-2026-20204 Splunk RCE Vulnerability CVE-2026-20163 Splunk Enterprise Vulnerabilities CVE-2026-20140 Splunk Permission Flaw, Local Privilege Escalation Splunk Vulnerabilities CVE-2024-53247 - Splunk Secure Gateway App CVE-2025-20229 & CVE-2025-20231
  • Vulnerability Report

High-Privilege Havoc: Splunk Patches RCE Flaw Lurking in File Previews

Do Son March 12, 2026 0

Splunk warns of a high-severity RCE flaw (CVE-2026-20163) in its REST API. Attackers with edit_cmd rights can execute arbitrary commands. Patch immediately.
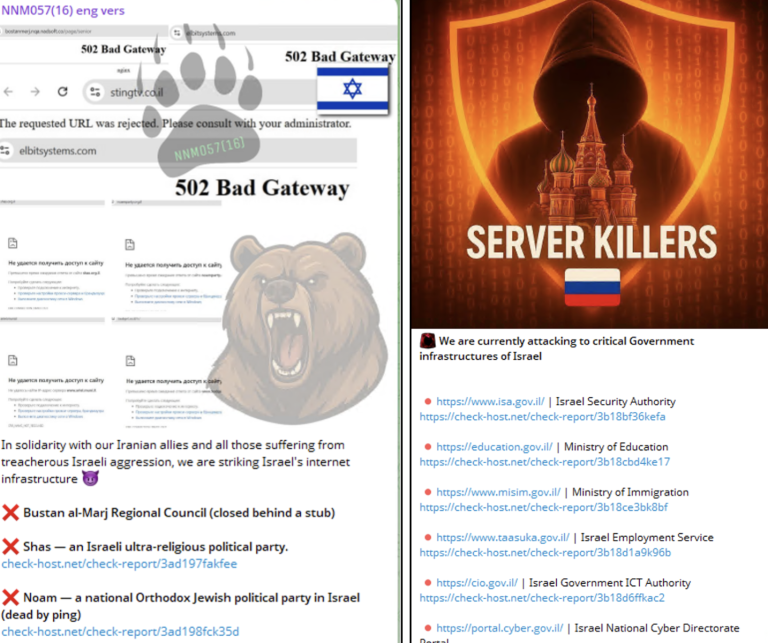
Cyber Escalation in the Middle East: Disruption, Deception, and the Quest for Data State-Sponsored Espionage
  • Cyber Security
  • Vulnerability Report

Cyber Escalation in the Middle East: Disruption, Deception, and the Quest for Data

Do Son March 12, 2026 0

Rapid7 reveals a surge in state-directed cyber espionage and noisy hacktivism. Learn how actors like MuddyWater exploit critical CVEs to breach networks.
Root Access via CLI: Cisco Patches Critical IOS XR Privilege Escalation Flaws Cisco IOS XR Vulnerability CVE-2026-20040
  • Vulnerability Report

Root Access via CLI: Cisco Patches Critical IOS XR Privilege Escalation Flaws

Do Son March 12, 2026 0

Cisco patches critical privilege escalation flaws (CVE-2026-20040, CVE-2026-20046) in IOS XR software that allow local attackers to gain full root access.
Iran-Aligned TA453 Weaponizes ‘Operation Epic Fury’ for Cyber Espionage Operation Epic Fury TA453 Phishing
  • Cyber Security

Iran-Aligned TA453 Weaponizes ‘Operation Epic Fury’ for Cyber Espionage

Do Son March 12, 2026 0

Proofpoint reveals Iran-aligned TA453 is exploiting Operation Epic Fury to launch targeted credential phishing campaigns against U.S. think tanks.
The Dark Side of Telegram: How Cybercriminals Weaponize Bot APIs for Stealthy Data Exfiltration Telegram Bot API Data Exfiltration
  • Cybercriminals

The Dark Side of Telegram: How Cybercriminals Weaponize Bot APIs for Stealthy Data Exfiltration

Do Son March 12, 2026 0

A new Cofense report reveals how hackers abuse legitimate Telegram Bot APIs to create stealthy Command and Control (C2) centers for data exfiltration.

Chrome 146 Arrives with 29 Security Fixes: Critical WebML Flaw Discovered Chrome 146 Security CVE-2026-3913
  • Vulnerability Report

Chrome 146 Arrives with 29 Security Fixes: Critical WebML Flaw Discovered

Do Son March 12, 2026 0

Google releases Chrome 146, fixing 29 vulnerabilities including a critical heap buffer overflow in WebML (CVE-2026-3913). Update your browser immediately.

Code Red: GitLab’s Latest Security Update Patches High-Severity XSS and API DoS Vulnerabilities GitLab Security Update Account Impersonation GitLab Security Update CVE-2026-1090 GitLab vulnerability GitLab vulnerability, GitLab patches
  • Vulnerability Report

Code Red: GitLab’s Latest Security Update Patches High-Severity XSS and API DoS Vulnerabilities

Do Son March 12, 2026 0

GitLab issues urgent security updates (18.9.2, 18.8.6, 18.7.6) fixing critical XSS (CVE-2026-1090) and DoS flaws. Patch self-managed instances today.

Operation False Siren: The Weaponization of Israel’s Red Alert App for Geo-Fenced Espionage Goldoon Botnet Operation False Siren Red Alert Spyware
  • Cybercriminals

Operation False Siren: The Weaponization of Israel’s Red Alert App for Geo-Fenced Espionage

Do Son March 12, 2026 0

Discover how Operation False Siren weaponizes Israel's Red Alert app via smishing, deploying advanced Android spyware for geo-fenced mobile espionage.
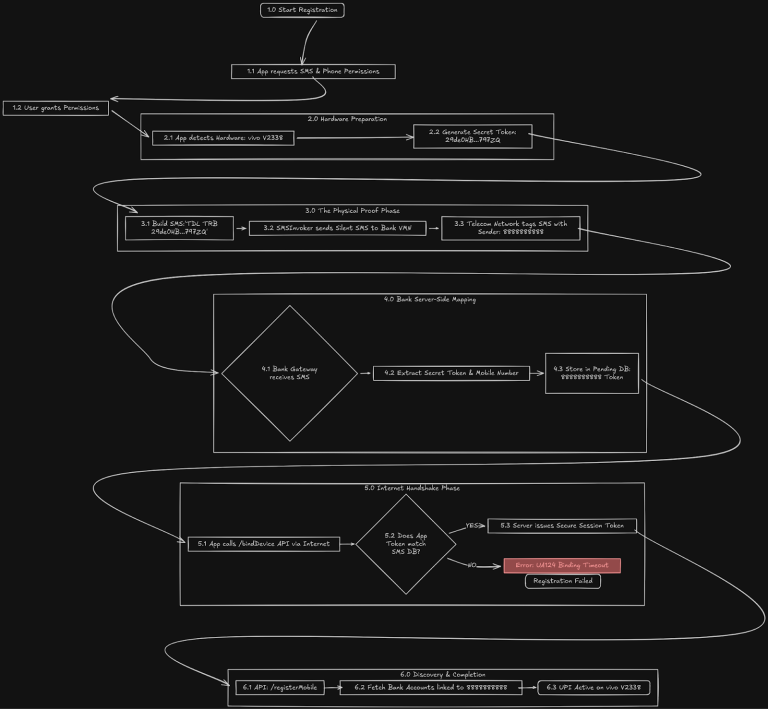
Gaslighting Android: How the ‘Digital Lutera’ Attack Uses LSPosed to Bypass UPI SIM-Binding UPI SIM-Binding Bypass LSPosed Framework
  • Malware

Gaslighting Android: How the ‘Digital Lutera’ Attack Uses LSPosed to Bypass UPI SIM-Binding

Do Son March 12, 2026 0

CloudSEK reveals how attackers use LSPosed and the "Digital Lutera" module to bypass Android UPI SIM-binding, gaslighting payment apps for remote fraud.

The Sleeper in Your Toolbar: How a “Featured” Chrome Extension Turned Into a Full-Scale Infostealer ShotBird extension malware
  • Malware

The Sleeper in Your Toolbar: How a “Featured” Chrome Extension Turned Into a Full-Scale Infostealer

Do Son March 12, 2026 0

Once a "Featured" tool, the ShotBird extension now delivers malware via "vibecoded" scripts and fake updates. Remove it now to protect your passwords and data.
How CTEM Allows Security Teams to Uncover What Attackers Already See Salesforce vulnerability CVE-2025-9844 Salt Typhoon cyberattack
  • Technique

How CTEM Allows Security Teams to Uncover What Attackers Already See

Do Son March 11, 2026 0
Most security teams operate from the inside out. They rely on logs and alerts to see what’s...
Read More Read more about How CTEM Allows Security Teams to Uncover What Attackers Already See
Critical 9.8 CVSS Bypass Unearthed in HPE Aruba AOS-CX Switches CVE-2024-42509 & CVE-2024-47460 HPE Aruba Fabric Composer CVE-2026-23592 Aruba AOS-CX CVE-2026-23813
  • Vulnerability Report

Critical 9.8 CVSS Bypass Unearthed in HPE Aruba AOS-CX Switches

Do Son March 11, 2026 0

HPE Aruba patches a critical 9.8 CVSS bypass in AOS-CX switches that allows unauthenticated password resets. Upgrade to 10.17.1001+ to secure your network now.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-59104CVSS 9.3
    UgCS server before 6.2 contains an authentication bypass in the HCI protocol login handler (LoginHandler) exposed on TCP...
    📅 Updated: Nov 6, 2026
  • CVE-2026-54143CVSS 9.8
    OpenHuman is an open-source agent harness available as a desktop application and Rust library. Before version 0.57.13, an...
    📅 Updated: Nov 6, 2026
  • CVE-2026-54141CVSS 9.0
    OpenHuman is an open-source agent harness available as a desktop application and Rust library. Before 0.57.13, a remote...
    📅 Updated: Nov 6, 2026
  • CVE-2026-77596CVSS 9.6
    Kubeflow Pipelines enables users to build and deploy portable, scalable machine learning workflows. Prior to 2.18.0, the multi-user...
    📅 Updated: Nov 6, 2026
  • CVE-2026-102940CVSS 9.6
    OpenEMR is a free and open source electronic health records and medical practice management application. Prior to 8.4.0,...
    📅 Updated: Nov 6, 2026
  • CVE-2026-123279CVSS 9.0
    In JetBrains Datalore before 2026.4 code execution was possible in a notebook's computation by view-only collaborators
    📅 Updated: Nov 6, 2026
  • CVE-2026-123294CVSS 9.6
    In JetBrains Hub before 2026.2.52556 privilege escalation was possible by changing email authentication details during the verification flow
    📅 Updated: Nov 6, 2026
  • CVE-2026-123831CVSS 9.6
    In JetBrains CLion before 2026.2, 2026.1.4 code execution was possible in Safe Mode via Meson project settings
    📅 Updated: Nov 6, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.