Skip to content
November 6, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
Cracking the Cloud’s Crypto: Unauthenticated Bypass Flaws Found in Amazon’s AWS-LC Library Motorola Smart Feed redirect Anthropic Amazon 5GW partnership Amazon Perplexity lawsuit AWS-LC Vulnerabilities Cryptographic Bypass AWS Middle East drone strikes Amazon layoffs 2026, Amazon AI restructuring Amazon Kindle DRM Policy, Publisher Control EPUB AWS Nova Forge AI Model Customization AWS Trainium3 EC2 Trn3 UltraServer Route 53 Accelerated Recovery AWS DNS Resilience AI Browser War, Amazon Comet Amazon layoffs, cost reduction AWS outage, DynamoDB DNS AWS outage, cloud dependency AWS VPN Client, Root Privilege Escalation WSA shutdown, Amazon Appstore Amazon Wondery, Podcast Restructuring Amazon Q2 2025 Generative AI AWS Client VPN, Privilege Escalation Amazon AI, Wearable AI
  • Vulnerability Report

Cracking the Cloud’s Crypto: Unauthenticated Bypass Flaws Found in Amazon’s AWS-LC Library

Do Son March 6, 2026 0

Researchers discovered three major flaws in Amazon’s AWS-LC cryptographic library, allowing hackers to bypass digital signature validation. Update now.

Signed Malware Masquerading as Workplace Apps Deploys Persistent Backdoors EV Certificate Phishing RMM Backdoors
  • Cybercriminals

Signed Malware Masquerading as Workplace Apps Deploys Persistent Backdoors

Do Son March 6, 2026 0

Microsoft Defender exposes a new phishing campaign using EV certificates and fake Teams invites to silently deploy RMM backdoors on corporate networks.

Unmasking OCRFix: The New Russian Botnet Hiding its C2 Infrastructure in the Blockchain OCRFix Botnet EtherHiding CrowdStrike supply chain attack Ivanti CSA Vulnerabilities
  • Malware

Unmasking OCRFix: The New Russian Botnet Hiding its C2 Infrastructure in the Blockchain

Do Son March 6, 2026 0

Cybersecurity researchers uncover OCRFix, a Russian-linked botnet using EtherHiding and fake CAPTCHAs to mask its C2 servers in blockchain smart contracts.

Malicious PHP Packages Found Hidden in Laravel Ecosystem fast16 Malware Cyber Sabotage IronWind malware Stealc
  • Malware

Malicious PHP Packages Found Hidden in Laravel Ecosystem

Do Son March 6, 2026 0

Socket researchers uncover a Packagist supply chain attack where fake Laravel utility packages secretly install a persistent Remote Access Trojan (RAT).

Which Tool Is Free And Secure to Merge PDFs Online? Screenshot_20260305_220705_Docs
  • Technique

Which Tool Is Free And Secure to Merge PDFs Online?

Do Son March 5, 2026 0
If you’ve ever had to merge pdf files securely and without losing your mind, you know it...
Read More Read more about Which Tool Is Free And Secure to Merge PDFs Online?
Nvidia’s “Overclocking” Rescue: The 595.76 Hotfix Arrives to Cure GPU Voltage and Cooling Woes NVIDIA acquisition rumors NVIDIA AI Security AI Framework Vulnerabilities Nvidia 595.76 Hotfix NVIDIA Megatron Bridge vulnerability GPU vs ASIC AI battle NVIDIA Driver Vulnerability CVE-2025-33217 NVIDIA biggest TSMC customer 2026, NVIDIA vs Apple TSMC revenue share NVIDIA CUDA Toolkit CVE-2025-33228 Groq NVIDIA licensing deal, Jonathan Ross acquihire 2025 NeMo Code Injection, AI Framework RCE NVIDIA App Privilege Escalation, CVE-2025-23358 NVIDIA Security Update, DLS Vulnerability CVE-2025-23316 NVIDIA NVDebug, vulnerabilities NVIDIA Driver Vulnerabilities, vGPU Security Nvidia Jetson, UEFI Vulnerabilities CVE-2024-0130 - CVE-2024-0136 CVE-2024-0148 NVIDIA Driver Support, Windows 10 EOL
  • Technology

Nvidia’s “Overclocking” Rescue: The 595.76 Hotfix Arrives to Cure GPU Voltage and Cooling Woes

Do Son March 5, 2026 0

Nvidia releases the 595.76 Hotfix to resolve a critical voltage cap preventing GPU overclocking and fix Resident Evil: Requiem visual bugs. Download now!

Weaponized in the Wild: Public PoC Exploit Disclosed for Critical 10.0 Cisco SD-WAN Flaw Cisco SD-WAN Vulnerability CVE-2026-20127 CVE-2024-20481 - Daggerfly group
  • Vulnerability Report

Weaponized in the Wild: Public PoC Exploit Disclosed for Critical 10.0 Cisco SD-WAN Flaw

Do Son March 5, 2026 0

A critical 10.0 CVSS flaw (CVE-2026-20127) in Cisco Catalyst SD-WAN is actively exploited in the wild. A public PoC is now available. Patch immediately!
Integer Overflow Flaw in Apache ActiveMQ Exposes MQTT Brokers to DoS ActiveMQ security flaws Jolokia web console exploit ActiveMQ RCE Jolokia Spring Vulnerability ActiveMQ MQTT Vulnerability CVE-2025-66168 Apache Artemis Vulnerability CVE-2026-27446
  • Vulnerability Report

Integer Overflow Flaw in Apache ActiveMQ Exposes MQTT Brokers to DoS

Do Son March 5, 2026 0

An integer overflow flaw (CVE-2025-66168) in Apache ActiveMQ's MQTT module allows authenticated attackers to crash brokers. Update your systems immediately.

The Digital Gavel Falls: Global Strike Dismantles LeakBase Cybercrime Forum LeakBase shutdown
  • Cybercriminals

The Digital Gavel Falls: Global Strike Dismantles LeakBase Cybercrime Forum

Do Son March 5, 2026 0

Law enforcement from 14 countries just seized LeakBase.ws. With 142k accounts and 215k messages exposed, the DOJ sends a clear message: No hacker is anonymous.

Google Slashes Play Store Fees and Welcomes Fortnite Back in Landmark Epic Settlement Low carbon cloud computing Smartphone clusters, Green technology, Data centers, Google research Google Agentic AI search G Suite legacy free commercial reclassification 2026 Agent Payments Protocol AP2 Back-Button Hijacking Google Search AI headlines Google Play Store fee reduction Google Antigravity account recovery Google Advanced Air-Cooling Alphabet $185 billion CapEx 2026 Google Aluminum OS 2026 ai-disclosure HTML attribute, Chrome AI content transparency 2026 Google monopoly appeal 2026, Search data sharing stay Change @gmail.com address, Gmail email alias feature 2025 Google Play Store external download fees, Epic vs Google 2026 billing Google Dark Web Report Retirement, Data Breach Monitoring Google Antitrust One-Year Limit Default Search Contract Term Google AI Headlines Discover Headline Distortion Aluminium OS Android ChromeOS Merge Google Accelerator Impact $31.2 Billion Funding Google Texas Investment AI Data Center Expansion Google Play payments, external billing Gmail HIBP leak Privacy Sandbox Termination, Third-Party Cookies Google Strategic Market Status, CMA Antitrust ICEBlock Removal, DOJ Pressure Google Logo, AI Branding
  • Android

Google Slashes Play Store Fees and Welcomes Fortnite Back in Landmark Epic Settlement

Do Son March 5, 2026 0

Google settles with EPIC! Commissions drop to 20%, Fortnite returns, and a new $800M partnership emerges. See how the Android ecosystem is changing in 2026.

The Race to M153: Why Google Chrome is Doubling Its Update Speed to a 14-Day Cadence Chrome 14-day update cycle Chromium JPEG-XL Image Format Debate Chromium DoS, document.title Browser Muting, iframe Media Supporters of Chromium-based Browsers
  • Technology

The Race to M153: Why Google Chrome is Doubling Its Update Speed to a 14-Day Cadence

Do Son March 5, 2026 0

Google Chrome shifts to a 14-day update cycle starting with M153 in Sept 2026. Discover how this biweekly rhythm impacts security, features, and developers.

The “GitHub Killer”? OpenAI Secretly Building Its Own AI-Native Code Repository to Rival Microsoft OpenAI token price reduction OpenAI Deployment Company DeployCo OpenAI IPO strategy OpenAI Privacy Filter 1.5B OpenAI $122 billion funding OpenAI GitHub alternative OpenAI military agreement 2026 OpenAI Stargate project collapse NVIDIA OpenAI investment stall ChatGPT Go $8 subscription, OpenAI GPT-5.2 Instant ads OpenAI Torch acquisition, Unified Medical Memory OpenAI Head of Preparedness 2025, Sam Altman AI safety lawsuits ChatGPT Advertising Speculation OpenAI Ad Code Denial OpenAI AI Confession Hallucination Mitigation ChatGPT Quality Focus OpenAI Gemini Red Alert ChatGPT Login, AI ecosystem OpenAI Mental Health, AI Well-Being Council ChatGPT Instant Checkout, Agentic Commerce OpenAI cloud computing OpenAI, startup incubator OpenAI chips, NVIDIA competition AI competition, antitrust lawsuit GPT-5, OpenAI Livestream OpenAI Open-Weight, AI Models OpenAI Infrastructure, AI Data Centers ChatGPT Business, Office Productivity OpenAI Open-Weight Model, WindSurf Acquisition OpenAI AI Browser, ChatGPT Integration Mattel AI, OpenAI Partnership OpenAI o3, Price Cut OpenAI's Next-Gen AI: O3-Pro's Enhanced Reasoning PowerOpenAI profit OpenAI Bid OpenAI Social Network ChatGPT Social OpenAI Non-profit OpenAI UAE ChatGPT Plus free
  • Technology

The “GitHub Killer”? OpenAI Secretly Building Its Own AI-Native Code Repository to Rival Microsoft

Do Son March 5, 2026 0

Frustrated by GitHub outages, OpenAI is reportedly building its own "agent-first" code-hosting platform. Is this the end of the Microsoft-OpenAI partnership?

The Price of Deception: X Imposes 90-Day Payout Ban on AI-Generated War “Slop” Elon Musk SEC settlement X bootloader verification X Creator Revenue Sharing suspension X Platform, AI Training X open-source algorithm 2026, Elon Musk ad transparency
  • Technology

The Price of Deception: X Imposes 90-Day Payout Ban on AI-Generated War “Slop”

Do Son March 5, 2026 0

X strikes back at engagement farmers! New 2026 rules impose a 90-day monetization ban for posting undisclosed AI-generated war videos. Is your payout at risk?

OpenAI’s Stolen Valor Purge: The Massive Crackdown on ChatGPT Plus Military Verification Scams OpenAI confidential IPO filing OpenAI code signing certificate rotation AI private equity joint ventures OpenAI Axios Supply Chain Attack OpenAI Promptfoo acquisition OpenAI military resignation ChatGPT Plus military fraud OpenAI smart speaker Jony Ive OpenAI Frontier platform ChatGPT AI age prediction 2026, OpenAI Persona age verification Sarah Friar OpenAI infrastructure, AI Scaling Law revenue OpenAI Gumdrop AI pen, Jony Ive OpenAI hardware 2027 OpenAI New CRO, Denise Dresser Monetization Strategy OpenAI Competitive Pressure Gemini 3 Overtake OpenAI Infrastructure, AI Closed Loop Economy
  • Technology

OpenAI’s Stolen Valor Purge: The Massive Crackdown on ChatGPT Plus Military Verification Scams

Do Son March 5, 2026 0

OpenAI is purging accounts that used forged military IDs to score free ChatGPT Plus. See how the new SheerID audits are ending the "Stolen Valor" era.

A $1.2 Billion Speed Test: Why Accenture Just Bet the Future of AI on Ookla Accenture Ookla acquisition global broadband speed
  • Technology

A $1.2 Billion Speed Test: Why Accenture Just Bet the Future of AI on Ookla

Do Son March 5, 2026 0

Accenture acquires Ookla for $1.2 billion at MWC 2026, turning Speedtest and Downdetector into a strategic data foundation for the global AI infrastructure race.

Global Coalition Dismantles Tycoon 2FA’s Phishing Empire Tycoon 2FA AiTM Phishing
  • Cybercriminals

Global Coalition Dismantles Tycoon 2FA’s Phishing Empire

Do Son March 5, 2026 0

Microsoft and Europol lead a global coalition to dismantle Tycoon 2FA, a massive AiTM phishing platform that bypassed MFA for over 500,000 organizations.

Under Attack: Cisco Urges Immediate Action as Hackers Actively Exploit SD-WAN Manager Flaws Knowledge Deliver RCE vulnerability FortiClient EMS Vulnerability CVE-2026-35616 Cisco SD-WAN Vulnerability CVE-2026-20122 PCPcat, Next.js RCE Salesloft breach, Salesforce CRM WIREFIRE web shell
  • Vulnerability Report

Under Attack: Cisco Urges Immediate Action as Hackers Actively Exploit SD-WAN Manager Flaws

Do Son March 5, 2026 0

Cisco warns that two vulnerabilities (CVE-2026-20122 and CVE-2026-20128) in its Catalyst SD-WAN Manager are being actively exploited. Update immediately.
Root Access for All: Critical Auth Bypass Hits Cisco Firewall Management Center Cisco Secure FMC CVE-2026-20079 Cisco RCE, Firewall Vulnerability Cisco Nexus, vulnerability CVE-2024-20412 - Cisco data breach
  • Vulnerability Report

Root Access for All: Critical Auth Bypass Hits Cisco Firewall Management Center

Do Son March 5, 2026 0

A critical 10.0 CVSS zero-click flaw (CVE-2026-20079) in Cisco Secure FMC gives unauthenticated attackers root access. Patch your systems immediately.
Critical 10.0 CVSS Flaw in pac4j-jwt Lets Hackers Forge Admin Tokens pac4j-jwt Vulnerability CVE-2026-29000
  • Vulnerability Report

Critical 10.0 CVSS Flaw in pac4j-jwt Lets Hackers Forge Admin Tokens

Do Son March 5, 2026 0

A critical 10.0 CVSS flaw (CVE-2026-29000) in the pac4j-jwt library allows attackers to forge JWTs and bypass authentication. Patch immediately.

Update Chrome Now: Google Patches 3 Critical Flaws and 7 High-Risk Vulnerabilities Chrome Security Update Use After Free Chrome Security Update Critical Vulnerabilities Chrome Security Update CVE-2026-3062 Chrome Security Update V8 Engine Vulnerability Chrome Security Update CVE-2026-1862 CVE-2026-0628 Chrome 143 Update Chrome Safe Browsing UAF, CVE-2025-11756 Chrome Memory Flaws, CVE-2025-11460 Google Chrome, vulnerability CVE-2025-10200, CVE-2025-10201 Big Sleep CVE-2025-9478 Chrome Update, Security Vulnerabilities
  • Vulnerability Report

Update Chrome Now: Google Patches 3 Critical Flaws and 7 High-Risk Vulnerabilities

Do Son March 5, 2026 0

Google releases an urgent security update for Chrome, patching 10 flaws including 3 critical memory corruption vulnerabilities. Update to version 145 now.
Critical 10.0 CVSS Flaw in Cisco Secure FMC Hands Hackers Root Access to Enterprise Firewalls Cisco ISE Root Escalation * Read-Only Admin Exploit Cisco Secure FMC Vulnerability CVE-2026-20131 Cisco Meeting Management Vulnerability CVE-2026-20098 Cisco vulnerability, RCE flaw CVE-2025-20265 Cisco Meraki, VPN Vulnerability Cisco Nexus Dashboard - CVE-2024-20424 CVE-2025-20115 Cisco Vulnerability CVE-2018-0171 Privilege Escalation Cisco Unified Intelligence Center
  • Vulnerability Report

Critical 10.0 CVSS Flaw in Cisco Secure FMC Hands Hackers Root Access to Enterprise Firewalls

Do Son March 5, 2026 0

A critical 10.0 CVSS unauthenticated RCE flaw (CVE-2026-20131) in Cisco Secure FMC allows hackers root access via insecure Java deserialization. Patch now.
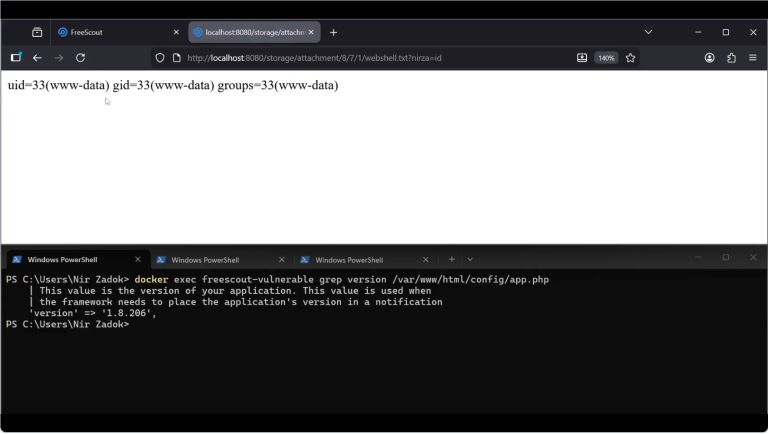
CVSS 10.0 Unauthenticated Remote Code Execution in FreeScout (Public Proof-of-Concept Disclosed) FreeScout RCE CVE-2026-28289
  • Vulnerability Report

CVSS 10.0 Unauthenticated Remote Code Execution in FreeScout (Public Proof-of-Concept Disclosed)

Do Son March 5, 2026 0

A critical 10.0 CVSS unauthenticated remote code execution flaw (CVE-2026-28289) in FreeScout allows full server takeover via an invisible character exploit.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
  • CVE-2023-54413CVSS 6.1
    The WPML plugin for WordPress is vulnerable to Reflected Cross-Site Scripting via the wp_lang parameter in versions up...
    Watchtower Verified📅 Updated: Nov 4, 2026
  • CVE-2024-27834CVSS 5.5
    The issue was addressed with improved checks. This issue is fixed in Safari 17.5, iOS 16.7.8 and iPadOS...
    CISA KEV📅 Added to KEV: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-86345CVSS 9.0
    A flaw was found in 389-ds-base. The server does not discard plaintext bytes already buffered from a client...
    📅 Updated: Nov 6, 2026
  • CVE-2026-48752CVSS 9.9
    Incus is a system container and virtual machine manager. Prior to version 7.2.0, a specially crafted image or...
    📅 Updated: Nov 6, 2026
  • CVE-2026-48751CVSS 9.9
    Incus is a system container and virtual machine manager. Prior to version 7.2.0, instance snapshots ignore the `restricted.containers.lowlevel=block`...
    📅 Updated: Nov 6, 2026
  • CVE-2026-48750CVSS 9.9
    Incus is a system container and virtual machine manager. Prior to version 7.2.0, the `record-output` parameter of the...
    📅 Updated: Nov 6, 2026
  • CVE-2026-48749CVSS 9.9
    Incus is a system container and virtual machine manager. Prior to version 7.2.0, a specially crafted image can...
    📅 Updated: Nov 6, 2026
  • CVE-2026-48755CVSS 9.9
    Incus is a system container and virtual machine manager. Prior to version 7.1.0, improper validation of user-provided backup...
    📅 Updated: Nov 6, 2026
  • CVE-2026-48769CVSS 9.9
    Incus is a system container and virtual machine manager. Prior to version 7.2.0, an arbitrary file write exists...
    📅 Updated: Nov 6, 2026
  • CVE-2026-63017CVSS 9.4
    Incorrect authorization in PowerSYSTEM Center allows a low-privileged, authenticated user to access resources normally limited to administrators.
    📅 Updated: Nov 6, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.