
 Do Son
LockBit 5.0 launches with a unified codebase targeting Windows, Linux, and ESXi. Acronis reveals identical encryption and ties to SmokeLoader.

OysterLoader malware uses custom LZMA & steganography to evade tools. Linked to Rhysida ransomware, it hides in fake IT installers.
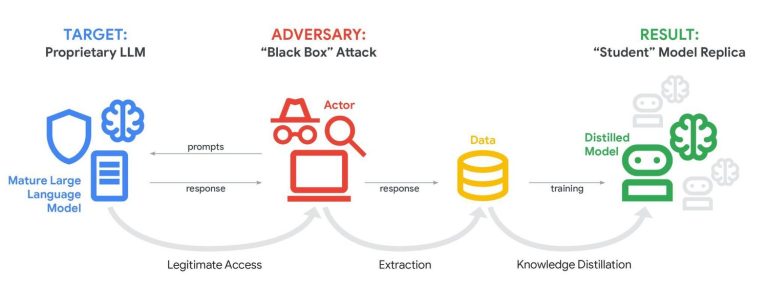
Google Threat Intelligence reports a surge in "model extraction" attacks. Private entities are cloning AI models & stealing API keys. Stay alert.

Critical FileZen flaw CVE-2026-25108 is under active attack. Antivirus feature allows command injection. Update to V5.0.11 immediately to secure data.

CISA warns of critical ZLAN5143D flaws CVE-2026-25084 & CVE-2026-24789. Attackers can bypass login & reset passwords. Isolate devices now.
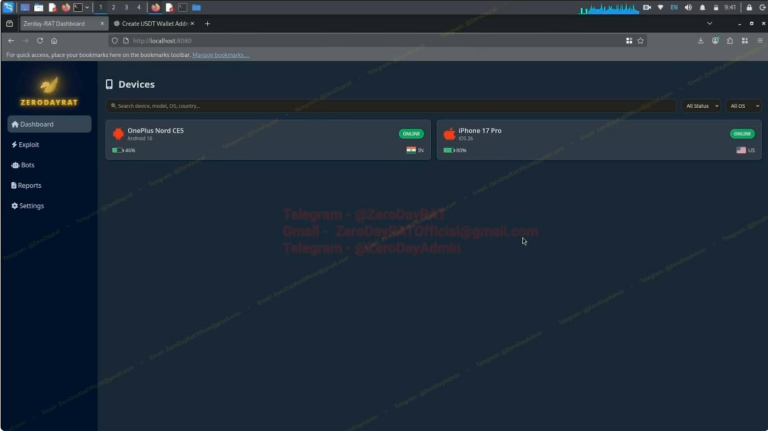
ZeroDayRAT mobile spyware is sold on Telegram. It offers full remote control of Android & iOS devices, including camera streaming & crypto theft.

HAProxy patches high-severity QUIC flaws CVE-2026-26080 & 26081. Remote attackers can crash servers via malformed packets. Update to v3.0.16 now.
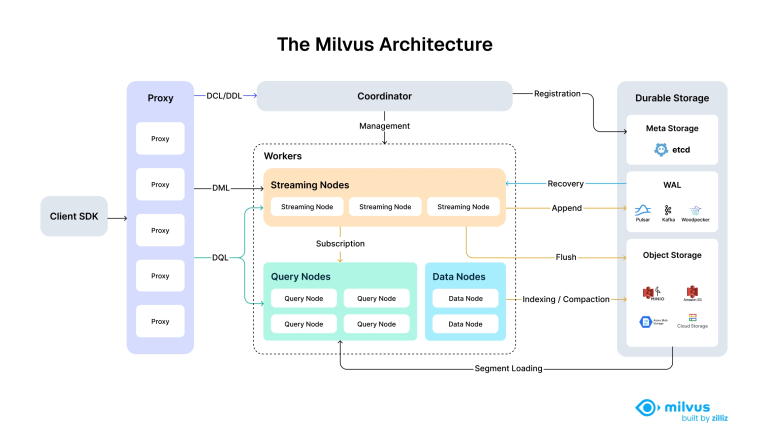
Critical Milvus flaw (CVSS 9.8) exposes port 9091. Unauthenticated attackers can steal secrets & delete data. Update to v2.5.27 or v2.6.10 immediately.

While all strategies are interconnected, sales enablement and data-driven decision-making are among the most critical. Teams that combine strong enablement with actionable insights consistently outperform competitors.

Lotus Blossom hijacked Notepad++ updates to target admins. The supply chain attack deployed Chrysalis backdoor. Update to v8.9.1 immediately.
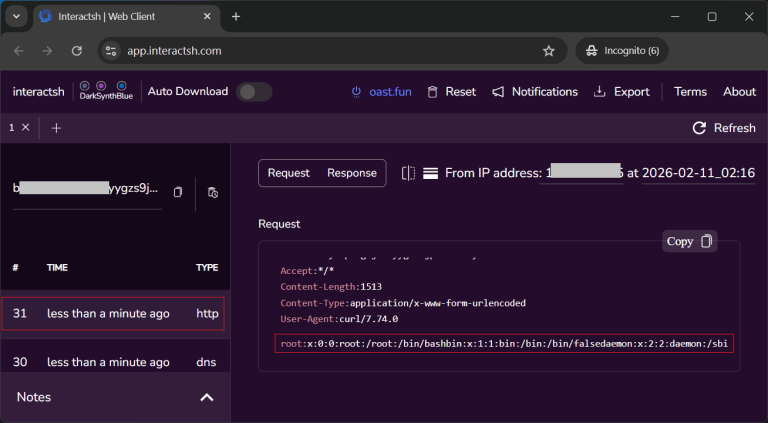
Arctic Wolf warns of CVE-2026-1731, a critical BeyondTrust flaw exploited in the wild. Attackers use it to deploy backdoors. Patch self-hosted instances now.

Google patches critical zero-day CVE-2026-2441. Attackers are exploiting this CSS use-after-free flaw in the wild. Update to Chrome 145 immediately.

Malicious Outlook add-in "AgreeTo" steals 4,000+ credentials. Attackers hijacked the abandoned tool in the official store. Uninstall immediately.

Zimbra 10.1.16 patches critical XSS, XXE, and LDAP injection flaws. Update immediately to secure your email collaboration suite and restore PDF previews.

Storm-2603 exploits SmarterMail vulnerability CVE-2026-23760 to deploy Warlock ransomware. Upgrade to Build 9511 immediately to prevent system compromise.

Lazarus Group targets crypto developers with fake job offers in new "Graphalgo" campaign. Malicious npm packages deliver multi-stage malware. Stay alert.

LummaStealer is back, evading takedowns with "ClickFix" tactics. Bitdefender reveals how fake CAPTCHAs trick users into running malware. Stay alert.
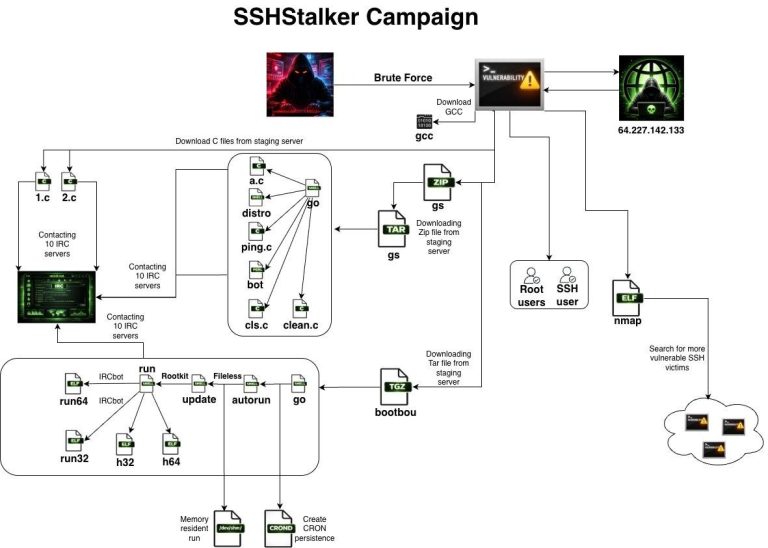
New SSHStalker botnet uses vintage IRC tactics & automated SSH brute-forcing to compromise Linux servers. Flare research reveals a "zombie army" in the making.
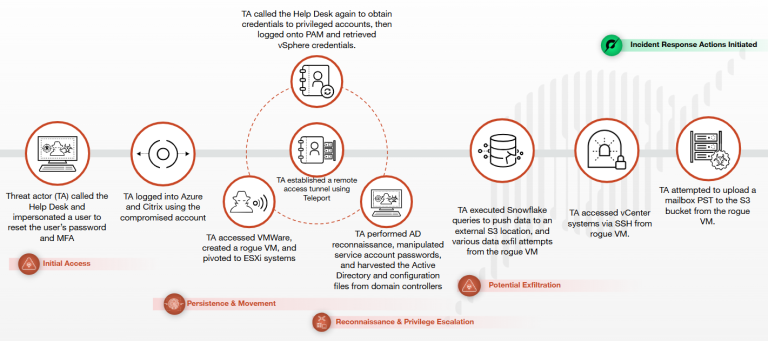
Unit 42 reveals Muddled Libra (Scattered Spider) uses rogue VMs in vSphere to persist. Learn how they bypass defenses without malware. Read more.

New Telegram phishing campaign abuses the "This is me" feature for account takeover. CYFIRMA reveals a global framework evading detection. Stay alert.

Siri’s long-awaited AI overhaul is delayed again. Discover why Apple is postponing the "Gemini-powered" assistant until iOS 26.5 or later.

Google’s 2026 "Agent Commerce" shift uses the Universal Commerce Protocol to let AI agents buy products for you instantly. The search-to-sale gap is closing.