Skip to content
November 6, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
Cybersecurity Excellence Awards Reveal Nomination Shift from AI Hype to Governance Execution Cybersecurity_Insiders_Press_Release_FEB_2026_1771270319lAAqrrrXI9
  • Press Release

Cybersecurity Excellence Awards Reveal Nomination Shift from AI Hype to Governance Execution

cybernewswire February 17, 2026 0
Washington DC, USA, 17th February 2026, CyberNewswire
Read More Read more about Cybersecurity Excellence Awards Reveal Nomination Shift from AI Hype to Governance Execution
Apache NiFi Flaw (CVE-2026-25903) Lets Users Bypass Restrictions Apache NiFi RCE CVE-2026-39816 Apache NiFi Vulnerability CVE-2026-25903 Apache NiFi Deserialization, GetAsanaObject Vulnerability CVE-2024-52067 - CVE-2024-56512 CVE-2025-27017
  • Vulnerability Report

Apache NiFi Flaw (CVE-2026-25903) Lets Users Bypass Restrictions

Do Son February 17, 2026 0

Apache NiFi flaw CVE-2026-25903 allows unauthorized users to modify restricted components. Update to version 2.8.0 immediately to secure data pipelines.

The Great Refurbishment: Why iOS 27 is the “Vernal Cleansing” Your iPhone Battery Needs FCC Chinese lab ban iPhone NATO certification iPhone 18 Pro Deep Red iOS 27 Snow Leopard update 2026 smartphone memory shortage, IDC mobile market forecast iPhone Satellite Natural Usage iPhone 17 Speaker Issue, USB-C Static iPhone 17 Pro, MagSafe Scratches iPhone 17 Pro, professional filmmaking
  • Technology

The Great Refurbishment: Why iOS 27 is the “Vernal Cleansing” Your iPhone Battery Needs

Do Son February 17, 2026 0

iOS 27 ditched flashy features for a "Snow Leopard" style cleanup. Discover how Apple is purging 20 years of legacy code to save your iPhone's battery life.

The Rise of the Digital Concierge: OpenAI Hires OpenClaw Visionary to Turn ChatGPT into an Autonomous Agent ChatGPT Lockdown Mode OpenAI OpenClaw acquisition OpenAI Prism GPT-5.2 LaTeX, scientific research AI workspace OpenAI, Mixpanel Breach ChatGPT Data Preservation, NYT Lawsuit ChatGPT Apps SDK, super app OpenAI Jony Ive, AI Hardware Delay Musk Apple lawsuit, App Store antitrust UK AI Partnership, OpenAI Collaboration Jony Ive OpenAI, DoD Contract OpenAI Lawsuit, ChatGPT Privacy North Korea ChatGPT - GPT-4.5 model OpenAI Models, AI Advancements OpenAI pricing, Flex API
  • Technology

The Rise of the Digital Concierge: OpenAI Hires OpenClaw Visionary to Turn ChatGPT into an Autonomous Agent

Do Son February 17, 2026 0

OpenAI hires OpenClaw creator Peter Steinberger to lead its "Personal Agent" revolution, aiming to turn ChatGPT into a proactive, task-executing concierge.

Hiding in Plain Sight: APT28’s “Operation MacroMaze” Hits European Govs GemStuffer RubyGems Campaign RubyGems Data Exfiltration TanStack npm Compromise Supply Chain Attack DNS Hijacking APT28 (Fancy Bear) OpenVSX Supply Chain Attack Checkmarx Plugin Breach Stryker Cyberattack CISA Alert Trans-Regional Cyber Conflict Operation Epic Fury Cyber Operation MacroMaze APT28 Cyber Espionage Notepad++ Supply Chain Attack Lotus Blossom Group Defense Industrial Base Threats GTIG Report APT28 Operation Neusploit CVE-2026-21509 Bookworm Malware
  • Cyber Security

Hiding in Plain Sight: APT28’s “Operation MacroMaze” Hits European Govs

Do Son February 17, 2026 0

APT28's "Operation MacroMaze" targets Europe using Spanish gov decoys. The campaign uses "low-tech" macros & Webhook.site to evade detection.
The AI Baseline: Apple’s “Special Experience” to Launch Budget MacBooks and M5 Powerhouses Apple Experience March 4 Apple Spring Event 2026
  • Technology

The AI Baseline: Apple’s “Special Experience” to Launch Budget MacBooks and M5 Powerhouses

Do Son February 17, 2026 0

Apple’s March 4 "Experience" debuts M5 Pro/Max chips and a colorful $699 MacBook. Say goodbye to "AI orphans" as Apple Intelligence goes global.
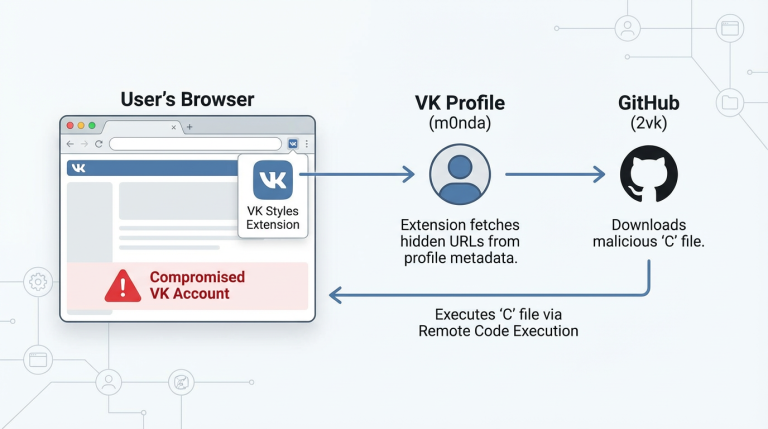
The “Styles” Trap: 500,000 VK Accounts Hijacked by Chrome Extensions VK Malicious Extensions VK Styles Campaign
  • Malware

The “Styles” Trap: 500,000 VK Accounts Hijacked by Chrome Extensions

Do Son February 17, 2026 0

500k VK accounts hijacked by "VK Styles" extensions. Malware forces subscriptions and bypasses CSRF tokens. Remove the extension immediately.
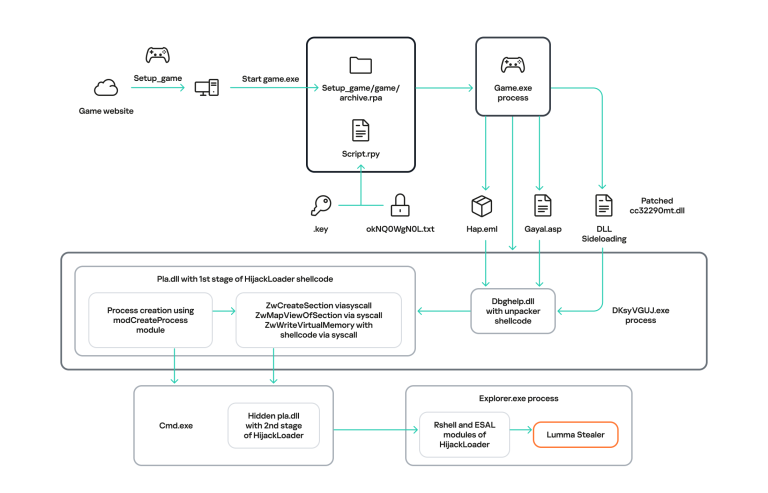
Game Over: “RenEngine” Malware Hides in Pirated Visual Novels RenEngine Malware Pirated Games Security
  • Malware

Game Over: “RenEngine” Malware Hides in Pirated Visual Novels

Do Son February 17, 2026 0

Kaspersky warns: Pirated visual novels are spreading RenEngine malware. Attackers use fake downloads to install ACR Stealer. Protect your data now.
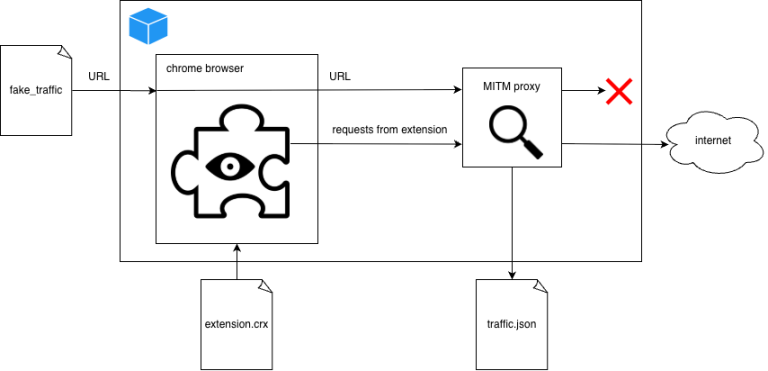
The 1% Breach: 287 Chrome Extensions Caught Spying on 37M Users Malicious Chrome Extensions
  • Data Leak

The 1% Breach: 287 Chrome Extensions Caught Spying on 37M Users

Do Son February 17, 2026 0

Q Continuum finds 287 Chrome extensions spying on 37M users. "Super PiP" & others exfiltrate history via Google Analytics. Check your browser now.
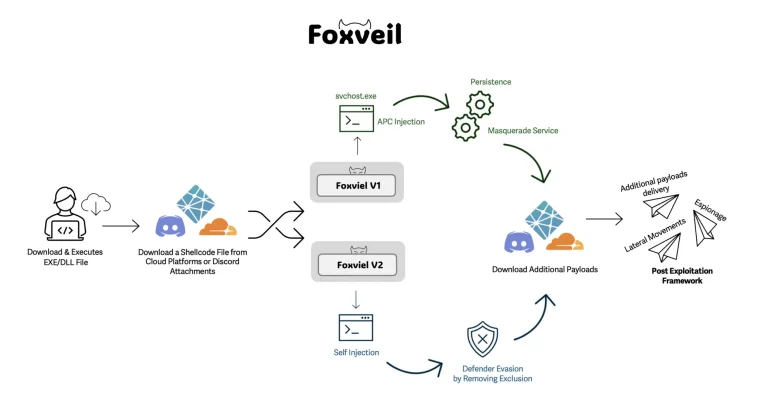
Foxveil: New Malware Loader Hides in Plain Sight Using Cloudflare and Discord Foxveil Malware
  • Malware

Foxveil: New Malware Loader Hides in Plain Sight Using Cloudflare and Discord

Do Son February 17, 2026 0

Cato CTRL discovers Foxveil, a new malware loader abusing Cloudflare, Netlify & Discord to bypass defenses. Active since Aug 2025. Learn the signs.
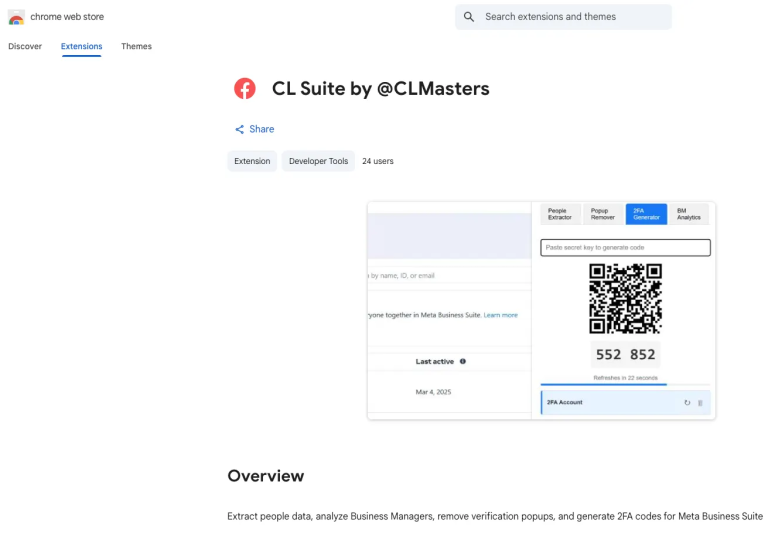
“CL Suite” Deception: Malicious Chrome Extension Steals 2FA Secrets and Meta Business Data CL Suite Malicious Extension Meta Business Suite Security
  • Malware

“CL Suite” Deception: Malicious Chrome Extension Steals 2FA Secrets and Meta Business Data

Do Son February 17, 2026 0

"CL Suite" Chrome extension steals Meta Business 2FA seeds & data. Attackers bypass security even after uninstall. Reset 2FA immediately.

“Natural Selection” at Work: How North Korean IT Workers Use AI to Infiltrate Companies North Korean Laptop Farm DPRK Insider Threat North Korea WMD Cyber Funding, Australia Sanctions Insider threat, North Korean hackers Kimsuky, cyber-espionage NPM Malware, North Korea Cyber-espionage North Korea, Remote IT Job Scam Laptop Farm - DriverEasy - Kimsuky Watering Hole Attack
  • Cybercriminals

“Natural Selection” at Work: How North Korean IT Workers Use AI to Infiltrate Companies

Do Son February 17, 2026 0

Okta exposes North Korean IT workers using AI photos & stolen LinkedIn profiles to land remote jobs. Learn how "JJ" bypassed checks.

The Navigation War: Why Tesla is Ghosting Apple CarPlay Amidst a Sales Slump Apple HomePad delay Tesla CarPlay integration 2026 Apple CarPlay AI integration 2026 Apple 2026 product roadmap rumors, foldable iPhone release date Apple Vision Pro sales slump, Vision Pro production cut Russia FaceTime Ban Network Blockade Apple Apple 2026 Roadmap, iPhone Foldable, Apple Intelligence Apple Maps ads, iOS monetization Apple, Digital Markets Act FCC Leak, iPhone 16e Schematics iPhone Fold Apple Made in India Apple US Investment, Indian Tariffs Apple Leadership, Tim Cook Tenure Siri Redesign, Apple AI Apple App Store Apple EU, Digital Markets Act CVE-2022-32898 Third-Party iOS Apps Apple Antitrust, DOJ Lawsuit
  • Technology

The Navigation War: Why Tesla is Ghosting Apple CarPlay Amidst a Sales Slump

Do Son February 16, 2026 0

Elon Musk’s fortress holds firm. Despite slumping sales, Tesla resists Apple CarPlay due to navigation conflicts and iOS 26 adoption hurdles.

Colorful, Metallic, and Powered by iPhone: Apple’s Bold $500 Gamble to Reclaim the Classroom Budget MacBook aluminum Apple MacBook, A18 Pro Chip MacBook Pro OLED
  • Technology

Colorful, Metallic, and Powered by iPhone: Apple’s Bold $500 Gamble to Reclaim the Classroom

Do Son February 16, 2026 0
According to insights shared by Bloomberg’s Mark Gurman in his latest “Power On” dispatch, the rumored budget-oriented...
Read More Read more about Colorful, Metallic, and Powered by iPhone: Apple’s Bold $500 Gamble to Reclaim the Classroom
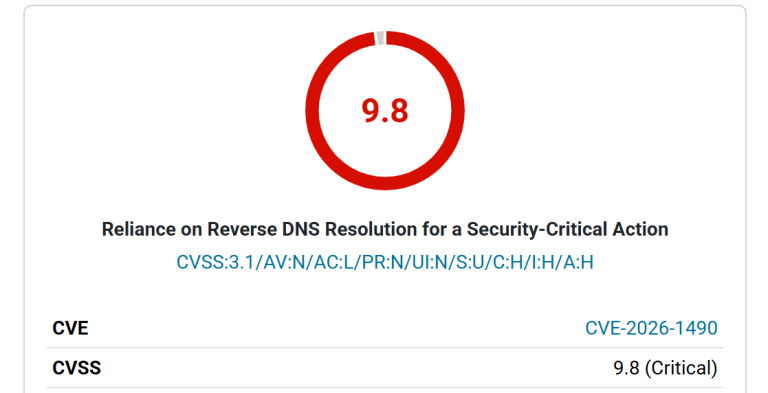
200k Sites Exposed: Critical CleanTalk Flaw (CVSS 9.8) Allows RCE CleanTalk Vulnerability CVE-2026-1490
  • Vulnerability Report

200k Sites Exposed: Critical CleanTalk Flaw (CVSS 9.8) Allows RCE

Do Son February 16, 2026 0

CleanTalk flaw CVE-2026-1490 (CVSS 9.8) exposes 200k sites to RCE via DNS spoofing. Attackers bypass auth to install plugins. Update to v6.72 now.
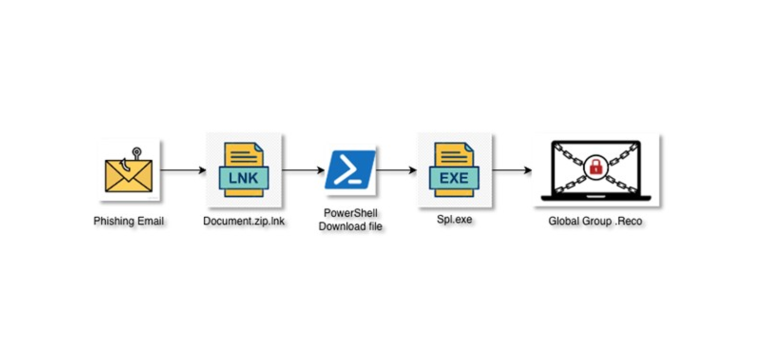
Don’t Click That Shortcut: Phorpiex Botnet Hides in “Your Document” Emails Phorpiex Botnet LNK Phishing
  • Malware

Don’t Click That Shortcut: Phorpiex Botnet Hides in “Your Document” Emails

Do Son February 16, 2026 0

Phorpiex botnet returns in "Your Document" phishing campaign. Attackers use malicious .LNK files and hidden extensions to trick users.

Industrial Sabotage Risk: Critical Airleader Flaw (CVSS 9.8) Exposed shell-quote command injection AI-Driven Vulnerabilities Q1 2026 Cyber Threats vm2 Sandbox Escape Node.js RCE upKeeper Privilege Escalation CVE-2026-2449 Pharos Controls Vulnerability Root Access Exploit Cybersecurity Vulnerability Roundup CVSS 10.0 Flaws Shadow Archives CVE-2026-0866 MS-Agent Prompt Injection CVE-2026-2256 basic-ftp Path Traversal CVE-2026-27699 telnetd Root Vulnerability CVE-1999-0073 Regression USR-W610 Vulnerabilities End-of-Life IoT Security IceWarp Security Update IceWarp Vulnerabilities Airleader Master Vulnerability CVE-2026-1358 ZLAN5143D Vulnerability CISA ICS Advisory Acronis Cyber Protect Vulnerability CVE-2025-30411 WAGO 852 Vulnerability OT Network Security SandboxJS Vulnerability Sandbox Escape (CVSS 10.0) Kubernetes Local Path Provisioner CVE-2025-62878 CISA Unresponsive Vendors Avation & RISS Vulnerabilities KiloView Vulnerability CVE-2026-1453 OpenClaw RCE vulnerability Johnson Controls Vulnerability CVE-2025-26385 SandboxJS Vulnerability CVE-2026-23830 ibaPDA Vulnerability CVE-2025-14988 Protobuf Vulnerability CVE-2026-0994 AVEVA Process Optimization Vulnerability CVE-2025-61937 ConnectWise PSA Vulnerability CVE-2026-0695 Aruba VIA Vulnerability CVE-2025-37186 aiohttp v3.13.3, Denial of Service (DoS) SmarterMail RCE, CVE-2025-52691 Airoha RACE, Headphone Jacking HPE OneView RCE CVE-2025-37164 FreePBX Auth Bypass, PBX Takeover ScreenConnect Config Flaw, Untrusted Extensions Ruby SAML Auth Bypass, XML Parser Differential Devolutions SQL Injection, Password Manager Flaw Vivotek Unauthenticated RCE, EOL IP Camera Flaw Lynx+ Critical Flaw, Unauthenticated Reset Firebox Default Credentials, CVE-2025-59396 Veeder-Root RCE, Critical ATG Flaw ArcGIS Server SQLi Watchdoc RCE, CVE-2025-58384 Delta DIALink Daikin Security Gateway, authentication bypass Frostbyte10, industrial controller security SunPower, vulnerability Ubiquiti UniFi Connect, EV Station Vulnerabilities Adobe Experience Manager, RCE Vulnerability UniFi Access, Command Injection LDAPNightmare - CVE-2025-1316
  • Vulnerability Report

Industrial Sabotage Risk: Critical Airleader Flaw (CVSS 9.8) Exposed

Do Son February 16, 2026 0

CISA warns of critical Airleader Master vulnerability CVE-2026-1358. Unauthenticated attackers can upload files and gain RCE. Update to 6.386 now.
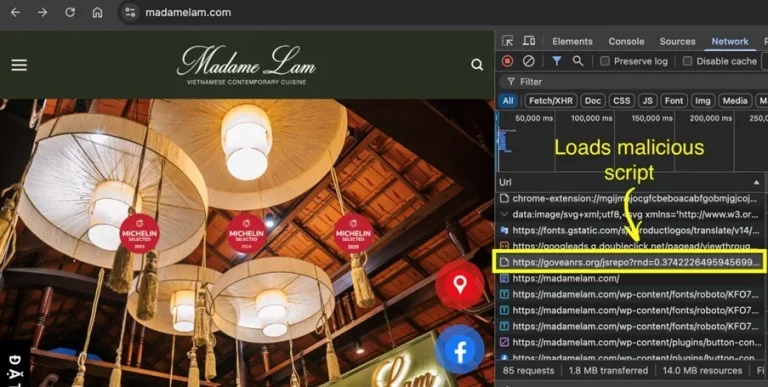
The “Windows + R” Trap: ClickFix Scam Tricks Users into Installing StealC Malware StealC Malware ClickFix Campaign
  • Malware

The “Windows + R” Trap: ClickFix Scam Tricks Users into Installing StealC Malware

Do Son February 16, 2026 0

LevelBlue warns of StealC malware using "ClickFix" fake CAPTCHAs. Users are tricked into running fileless malware via PowerShell. Stay alert.
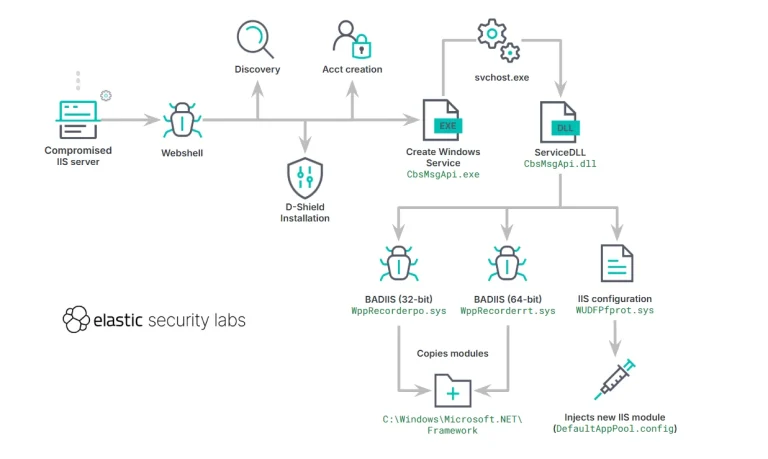
The Silent Hijack: BADIIS Malware Turns 1,800+ Servers into Illicit Websites BADIIS Malware IIS SEO Poisoning
  • Malware

The Silent Hijack: BADIIS Malware Turns 1,800+ Servers into Illicit Websites

Do Son February 16, 2026 0

Elastic Security Labs uncovers BADIIS malware compromising 1,800+ IIS servers. Attackers use SEO poisoning to redirect users to illicit gambling sites.
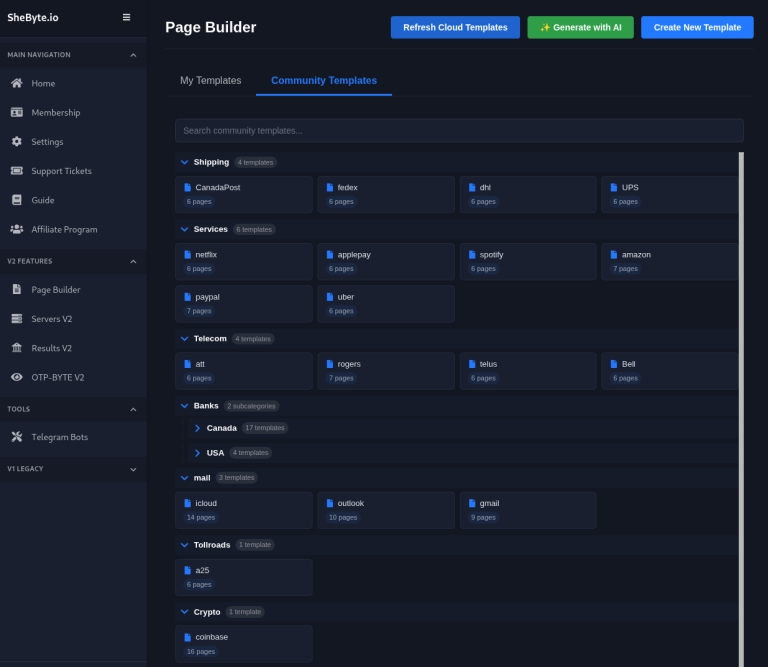
“Carding” as a Service: How Stolen Credit Cards Became a Structured Economy Carding-as-a-Service Underground Credit Card Market
  • Cybercriminals

“Carding” as a Service: How Stolen Credit Cards Became a Structured Economy

Do Son February 16, 2026 0

Rapid7 reveals how "Carding-as-a-Service" mimics legitimate e-commerce. Fraud markets now offer refunds & "Fullz" data. Learn about the new threat.
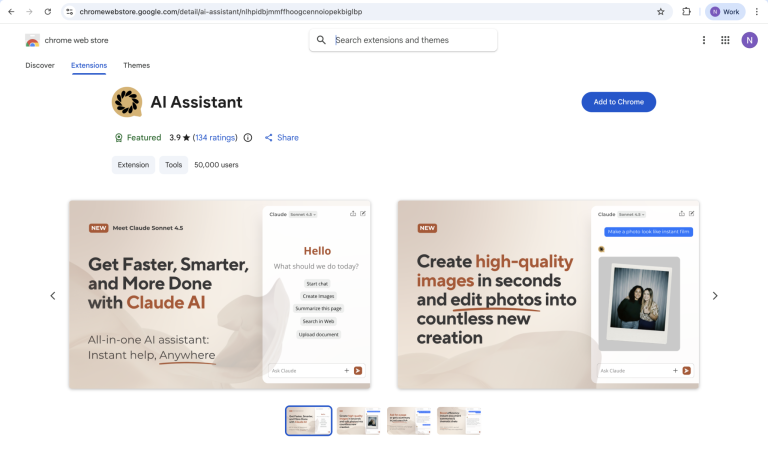
Fake AI, Real Spies: 260,000 Users Hit by Malicious Browser Extensions Malicious AI Extensions Browser Surveillance
  • Malware

Fake AI, Real Spies: 260,000 Users Hit by Malicious Browser Extensions

Do Son February 16, 2026 0

LayerX exposes 30+ malicious AI extensions spying on 260,000 users. These "privileged proxies" steal Gmail data & page content. Uninstall now.

“Matryoshka” Malware: New macOS Attack Hides Inside “Russian Dolls” of Obfuscation OSX/Amos Stealer Electron ASAR Trojan MioLab Malware macOS Security MacSync Stealer macOS Malware ambar-src npm Malware Supply Chain Typosquatting Matryoshka Mac Malware ClickFix Crypto Scam Infostealer Evolution macOS Malware Predator Spyware Intellexa Anti-Analysis XCSSET macOS Malware, Xcode Supply Chain
  • Malware

“Matryoshka” Malware: New macOS Attack Hides Inside “Russian Dolls” of Obfuscation

Do Son February 16, 2026 0

New "Matryoshka" Mac malware uses "ClickFix" scams to steal crypto. Intego warns of fake error fixes patching Ledger & Trezor apps. Stay alert.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
  • CVE-2023-54413CVSS 6.1
    The WPML plugin for WordPress is vulnerable to Reflected Cross-Site Scripting via the wp_lang parameter in versions up...
    Watchtower Verified📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-80668CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: netfilter: nf_conntrack_expect: use conntrack GC to reap expectations...
    📅 Updated: Nov 6, 2026
  • CVE-2026-120844CVSS 9.8
    Incorrect Privilege Assignment vulnerability in miniOrange OAuth Single Sign On – SSO (OAuth Client) miniorange-login-with-eve-online-google-facebook allows Privilege Escalation.This...
    📅 Updated: Nov 6, 2026
  • CVE-2026-114630CVSS 9.1
    The ELEX WordPress HelpDesk & Customer Ticketing System plugin for WordPress is vulnerable to arbitrary file deletion due...
    📅 Updated: Nov 6, 2026
  • CVE-2026-71495CVSS 10.0
    Wanderer is a self-hosted trail database for saving and sharing adventures. Prior to 0.20.0, when PUBLIC_PRIVATE_INSTANCE is not...
    📅 Updated: Nov 6, 2026
  • CVE-2026-116769CVSS 9.3
    CVE-2026-116769 is an authentication bypass vulnerability in Secure Access servers starting with version 13.0 and prior to 14.61....
    📅 Updated: Nov 6, 2026
  • CVE-2026-97718CVSS 9.4
    CVE-2026-97718 Is a cross-site request forgery vulnerability in version 14.60 of the Secure Access server.  Because of a...
    📅 Updated: Nov 6, 2026
  • CVE-2024-5535CVSS 9.1
    Issue summary: Calling the OpenSSL API function SSL_select_next_proto with an empty supported client protocols buffer may cause a...
    📅 Updated: Nov 6, 2026
  • CVE-2026-64618CVSS 9.8
    Improper Neutralization of Special Elements used in an SQL Command ("SQL Injection") vulnerability exists in Apache Fineract (through...
    📅 Updated: Nov 6, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.