 Do Son
Cybercriminals are using fake DocuSign emails and the JWrapper framework to stealthily deploy SimpleHelp remote access tools. Learn how to spot the threat.

Critical Pterodactyl API flaw (CVE-2026-26016) allows cross-node authorization bypass. Attackers can destroy game servers. Update to version 1.12.1 now.

Node.js DoS flaw CVE-2026-26278 in fast-xml-parser freezes event loops via XML entity expansion. 46M weekly downloads affected. Update to version 5.3.6.

Apache Camel patches critical flaws in Keycloak (CVE-2026-23552) and LevelDB (CVE-2026-25747) components that allow auth bypass and RCE. Update to 4.18.0.
Jenkins patches a high-severity stored XSS flaw (CVE-2026-27099) and an info disclosure bug. Update to version 2.551 or LTS 2.541.2 to secure pipelines.

 cybernewswire
Frankfurt am Main, Germany, 19th February 2026, CyberNewswire

Google releases an urgent Chrome update to patch high-severity flaws in PDFium (CVE-2026-2648) and the V8 engine (CVE-2026-2649). Update to 145 now.

NVIDIA warns of 7.8-rated vulnerabilities in Megatron Bridge. Learn how "educational" tutorials could let attackers hijack your AI training infrastructure.

The EU’s primary regulator has launched a massive GDPR probe into xAI's Grok. From deepfake porn to data theft, can Elon Musk’s AI survive the legal onslaught?

A 42% stock surge and the rise of "Edge Inference" have transformed the Raspberry Pi into the premier low-cost vessel for autonomous AI agents in 2026.

Google I/O 2026 kicks off May 19! Discover how Gemini 3 and Android 17 are turning your phone into a proactive AI concierge. The era of the agent is here.

CISA warns of Honeywell CCTV flaw CVE-2026-1670. Unauthenticated attackers can reset passwords & hijack feeds. Update firmware immediately.

Acronis uncovers CRESCENTHARVEST, a new spyware targeting Iranian dissidents. Attackers use protest lures & Google DLL sideloading to steal data.

North Korean hackers target IT pros with "Contagious Interview" malware. Fake job offers install trojanized MetaMask extensions to steal crypto.

Bridewell warns of Russian hackers targeting Booking.com. Phishing kits steal hotel staff creds to scam guests with "I Paid Twice" messages.
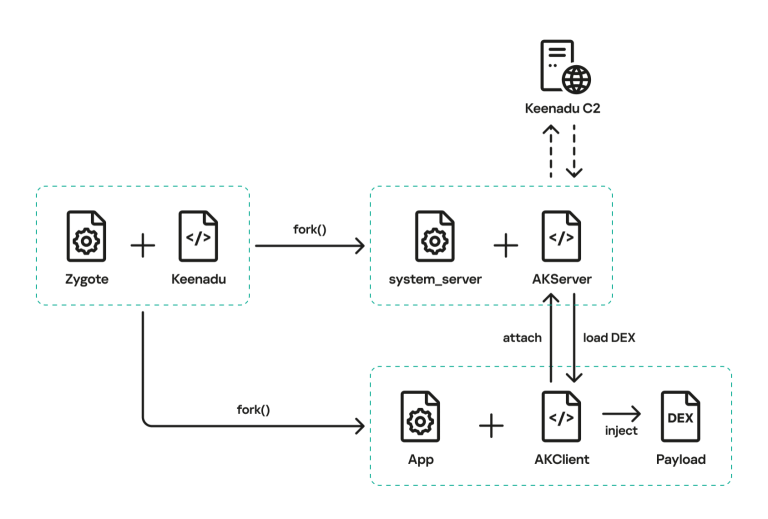
Kaspersky uncovers Keenadu, a firmware-level Android backdoor infecting the Zygote process. This pre-installed malware gives attackers full control.

Urgent: PostgreSQL patches 5 flaws, including 3 critical RCEs (CVSS 8.8). Attackers can execute code as OS user via text manipulation. Update v14-18.

Mandiant reveals UNC6201 exploiting Dell RecoverPoint zero-day CVE-2026-22769. Attackers use "Ghost NICs" & GRIMBOLT malware. Patch now.

Hackers abuse Atlassian Jira notifications to bypass spam filters. Trend Micro warns of scams targeting enterprise users via trusted alerts.

Ivanti EPMM under attack via zero-days CVE-2026-1281 & 1340. Hackers use bash scripts to plant dormant backdoors. Patch immediately.

CISA adds 4 flaws to KEV: Ancient Windows ActiveX bug (CVE-2008-0015) & new Chrome zero-day (CVE-2026-2441). Patch now to prevent exploitation.

SINGAPORE, Singapore, 17th February 2026, CyberNewswire