Skip to content
November 6, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
Streaming Fraud: “Massiv” Android Trojan Uses Fake IPTV Apps for Complete Device Takeover Massiv Android Malware IPTV Banking Trojan
  • Malware

Streaming Fraud: “Massiv” Android Trojan Uses Fake IPTV Apps for Complete Device Takeover

Do Son February 23, 2026 0

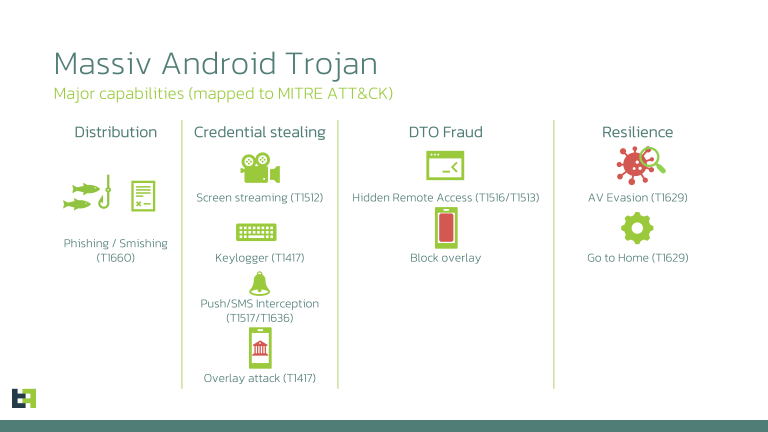
ThreatFabric exposes Massiv, a new Android banking Trojan hiding in fake IPTV apps. The malware uses accessibility permissions for full device takeover.

Maintaining the critical minimum through energy monitoring during storm disruptions CVE-2024-31070 & CVE-2024-36491
  • Technique

Maintaining the critical minimum through energy monitoring during storm disruptions

Do Son February 21, 2026 0

Technical analysis of energy monitoring and load prioritization strategies for maintaining smart home stability during grid outages.

Inside the ‘Upworksell’ Syndicate: Hacker Gets 60 Months for Funneling US Tech Jobs to North Korea Romanian hacker sentenced identity theft conviction Pig-Butchering Crackdown Operation Level Up Oleksandr Didenko North Korean IT Workers Coinbase TaskUs insider breach, Hyderabad police Coinbase arrest Scattered Spider, Cybercrime Scattered Spider group
  • Cybercriminals

Inside the ‘Upworksell’ Syndicate: Hacker Gets 60 Months for Funneling US Tech Jobs to North Korea

Do Son February 20, 2026 0

Ukrainian hacker Oleksandr Didenko receives a 60-month sentence for orchestrating a massive laptop farm scheme aiding North Korean IT operatives.

Exploited in the Wild & PoC Disclosed: Emergency Chrome Zero-Day (CVE-2026-2441) Patched Chrome security update exploit in the wild Chrome Zero-Day CVE-2026-3909 Chrome Zero-Day PoC CVE-2026-2441 Chrome Zero-Day CVE-2026-2441 Chrome Zero-Day, Active Exploitation CVE-2025-10585 Chrome vulnerability, zero-day exploit CVE-2025-6558 Chrome Zero-Day, V8 Vulnerability Chrome Zero-Day, Security Update
  • Vulnerability Report

Exploited in the Wild & PoC Disclosed: Emergency Chrome Zero-Day (CVE-2026-2441) Patched

Do Son February 20, 2026 0

Google patches Chrome zero-day CVE-2026-2441, an actively exploited memory flaw. With PoC exploit code now publicly disclosed, update to v145 immediately.

Bypassing the Bouncer: Apache Tomcat Patches SNI & Legacy Protocol Flaws Tomcat Security Update CVE-2026-24733 CVE-2023-41081 -CVE-2024-56337
  • Vulnerability Report

Bypassing the Bouncer: Apache Tomcat Patches SNI & Legacy Protocol Flaws

Do Son February 20, 2026 0

Apache Tomcat rolls out urgent updates for versions 9, 10, and 11 to fix legacy HTTP/0.9 protocol confusion and SNI certificate bypass flaws. Patch now.

The Dev Environment Trap: 128 Million Users at Risk as Top VS Code Extensions Unmask Critical Flaws VS Code extension vulnerabilities 2026
  • Vulnerability Report

The Dev Environment Trap: 128 Million Users at Risk as Top VS Code Extensions Unmask Critical Flaws

Do Son February 20, 2026 0

Critical flaws in Live Server, Code Runner, and more expose 128M+ developers to file theft and remote code execution. Is your VS Code workspace secure?

Google Unveils Gemini 3.1 Pro with 1 Million Tokens for Deep-Data Mastery Google Gemini Pentagon deal Google AI Pro 5TB storage Gemini 3.1 Pro launch
  • Technology

Google Unveils Gemini 3.1 Pro with 1 Million Tokens for Deep-Data Mastery

Do Son February 20, 2026 0

Google debuts Gemini 3.1 Pro! With a 1M token context window and native multi-modal power, it’s the new gold standard for complex analysis and big data.
Infoblox Exposes Hybrid Malvertising & “Pig Butchering” Scam Hybrid Crypto Scam Pig Butchering Malvertising
  • Cybercriminals

Infoblox Exposes Hybrid Malvertising & “Pig Butchering” Scam

Do Son February 20, 2026 0

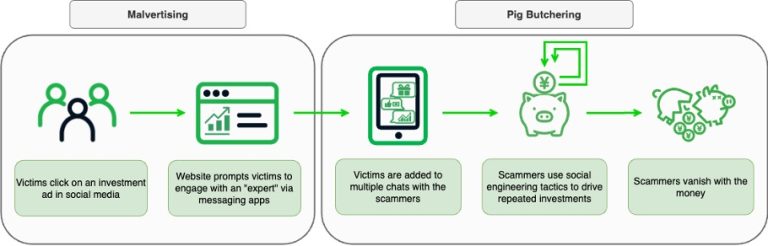
Infoblox Threat Intel exposes a highly scalable hybrid scam merging automated malvertising with "pig butchering" to drain global crypto investors' funds.

PoC Publicly Disclosed: Critical Grandstream VoIP Flaw (CVSS 9.3) Grants Stealthy Root Access Grandstream VoIP Zero-Day CVE-2026-2329 PoC
  • Vulnerability Report

PoC Publicly Disclosed: Critical Grandstream VoIP Flaw (CVSS 9.3) Grants Stealthy Root Access

Do Son February 20, 2026 0

Rapid7 publicly discloses a critical zero-day and PoC (CVE-2026-2329) for Grandstream GXP1600 VoIP phones allowing remote root access. Patch now.

Trojan Routers: Texas Sues TP-Link Over Alleged CCP Surveillance and Supply Chain Deception TP-Link Lawsuit CCP Surveillance
  • Malware

Trojan Routers: Texas Sues TP-Link Over Alleged CCP Surveillance and Supply Chain Deception

Do Son February 20, 2026 0

Texas AG Ken Paxton sues TP-Link, alleging the Wi-Fi giant's routers act as Trojan horses for CCP surveillance. State bans TP-Link gear for employees.
How to Secure Multiple Bybit Accounts Without Triggering Suspicious Activity Flags CVE-2025-20059
  • Technique

How to Secure Multiple Bybit Accounts Without Triggering Suspicious Activity Flags

Do Son February 20, 2026 0
In the increasingly regulated world of crypto derivatives, managing multiple exchange accounts has become a common practice....
Read More Read more about How to Secure Multiple Bybit Accounts Without Triggering Suspicious Activity Flags
CVE-2025-65717: Critical Vulnerability in VS Code’s Live Server Extension Puts 72 Million Developers at Risk, No Patch image-19
  • Vulnerability Report

CVE-2025-65717: Critical Vulnerability in VS Code’s Live Server Extension Puts 72 Million Developers at Risk, No Patch

Do Son February 20, 2026 0

Critical VS Code Live Server flaw CVE-2025-65717 (CVSS 9.1) lets attackers steal source code and credentials via malicious links. Protect your workspace now.

1.75 Million Apps Blocked: Google’s AI-Driven War on Android Malware in 2025 Google Play Security Android 16 Tapjacking Protection
  • Android
  • Malware

1.75 Million Apps Blocked: Google’s AI-Driven War on Android Malware in 2025

Do Son February 20, 2026 0

Google's VP Vijaya Kaza reveals 1.75M bad apps blocked in 2025. Android 16 introduces one-line tapjacking protection to fight AI-powered cyber threats.

The Symphonic Chatbot: How Google’s Gemini and Lyria 3 are Turning Every Prompt into a Hit Song Chrome hidden weights.bin download Gemini Nano privacy controversy 2026 Google Antigravity account suspension Gemini Lyria 3 integration Google Gemini enterprise sales, Google Cloud AI revenue 2026 Google Gemini daily limits 2026, Gemini Thinking model quotas Google Gemini 3 Agentic Development Platform
  • Technology

The Symphonic Chatbot: How Google’s Gemini and Lyria 3 are Turning Every Prompt into a Hit Song

Do Son February 20, 2026 0

Gemini meets Lyria 3! Generate 30-second high-fidelity songs from text, photos, or video. Discover the future of AI-driven musical creation today.

The Strategic Divorce: Why NVIDIA Sold Its Arm Shares While Doubling Down on Its Architecture NVIDIA GPU Security CUDA-Q Vulnerability NVIDIA Apex Vulnerability AI Infrastructure Security NVIDIA Cumulus Linux CVE-2025-33179 NVIDIA Arm divestment NVIDIA DGX Spark, CVE-2025-33187 NVIDIA Isaac-GROOT, Code Injection Megatron-LM Vulnerability, AI Code Injection NVIDIA China NVIDIA GPUs, Hardware Kill Switches NVIDIA Megatron-LM, LLM Vulnerabilities NVIDIA Base Command Manager - CVE-2024-0138
  • Technology

The Strategic Divorce: Why NVIDIA Sold Its Arm Shares While Doubling Down on Its Architecture

Do Son February 20, 2026 0

NVIDIA has fully divested its $156M stake in Arm. Is it a rift or a calculated move as Arm prepares to build its own chips? Discover the new "Grace" strategy.

The Wristband Revolution: Meta’s Revived Smartwatch Aims to Control the Future of AR Meta Malibu 2 smartwatch Solos Technology vs Meta lawsuit, Ray-Ban Meta patent infringement
  • Technology

The Wristband Revolution: Meta’s Revived Smartwatch Aims to Control the Future of AR

Do Son February 20, 2026 0

Meta's "Malibu 2" smartwatch is back! Discover how neural sensors and EMG gestures will turn this wearable into the ultimate controller for Meta's AR ecosystem.

The Private Powerhouse: How Meta’s $135B NVIDIA Bet is Bringing Stealth AI to WhatsApp WhatsApp Confidential Computing
  • Technology

The Private Powerhouse: How Meta’s $135B NVIDIA Bet is Bringing Stealth AI to WhatsApp

Do Son February 19, 2026 0

Meta is spending $135B to bring NVIDIA’s "Confidential Computing" to WhatsApp. Get AI assistance without breaking the sanctity of end-to-end encryption.
The Designer in the Machine: How WordPress’s New AI Concierge is Killing Layout Frustration WordPress Persistent AI Assistant
  • Technology

The Designer in the Machine: How WordPress’s New AI Concierge is Killing Layout Frustration

Do Son February 19, 2026 0

WordPress.com launches a Persistent AI Assistant to handle CSS, font styling, and image editing. Turn natural language into a professional site design instantly.

Google Pixel 10a Perfects the Mid-Range with 3,000 Nits and Satellite SOS Pixel reboot loop bug, Pixel factory reset, Pixel software update issue, Pixel boot loop fix Google Pixel 10a pre-order
  • Android

Google Pixel 10a Perfects the Mid-Range with 3,000 Nits and Satellite SOS

Do Son February 19, 2026 0

Google Pixel 10a is here! For $499, get a 3,000-nit Actua display, Satellite SOS, and 7 years of updates. The mid-range "definitive" evolution has arrived.

Beyond the Lens: Samsung Unveils the Galaxy S26’s AI-Powered “Luminous Metamorphosis” Galaxy S26 AI Camera Galaxy Unpacked 2026
  • Android

Beyond the Lens: Samsung Unveils the Galaxy S26’s AI-Powered “Luminous Metamorphosis”

Do Son February 19, 2026 0

Samsung’s Galaxy S26 turns day into night with "Luminous Metamorphosis." Discover the AI-orchestrated camera workflow destined to redefine mobile photography.

Live from Your Webcam: Remcos RAT Evolves into a Real-Time Surveillance Nightmare WhatsApp Worm, Brazilian Banking Trojan LAPSUS$ Alliance, Scattered Spider Ransomware, Cybercrime RedCurl APT group Russian Cyberespionage, ApolloShadow Malware
  • Malware

Live from Your Webcam: Remcos RAT Evolves into a Real-Time Surveillance Nightmare

Do Son February 19, 2026 0

Point Wild reveals a new Remcos RAT variant abandoning local storage for real-time webcam streaming, memory evasion, and aggressive anti-forensics.

Splunk Windows Flaws Expose Servers to System Takeover Splunk Enterprise vulnerabilities, CVSS 9.8 flaw, CVE-2026-20253, CVE-2026-20251, CVE-2026-20258 Splunk Enterprise Vulnerabilities CVE-2026-20240 Splunk RCE CVE-2026-20204 Splunk RCE Vulnerability CVE-2026-20163 Splunk Enterprise Vulnerabilities CVE-2026-20140 Splunk Permission Flaw, Local Privilege Escalation Splunk Vulnerabilities CVE-2024-53247 - Splunk Secure Gateway App CVE-2025-20229 & CVE-2025-20231
  • Vulnerability Report

Splunk Windows Flaws Expose Servers to System Takeover

Do Son February 19, 2026 0

Splunk Enterprise Windows flaws (CVSS 7.7) CVE-2026-20143 & CVE-2026-20140 allow system takeover via DLL and Python search path hijacking. Patch immediately.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
  • CVE-2023-54413CVSS 6.1
    The WPML plugin for WordPress is vulnerable to Reflected Cross-Site Scripting via the wp_lang parameter in versions up...
    Watchtower Verified📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-123488CVSS 9.3
    Craft CMS 4.0.0 before 4.18.9 and 5.0.0 before 5.11.2 contains an unauthenticated SQL injection vulnerability in the element...
    📅 Updated: Nov 6, 2026
  • CVE-2026-93754CVSS 9.8
    The payever – WooCommerce Gateway plugin for WordPress is vulnerable to arbitrary file upload leading to remote code...
    📅 Updated: Nov 6, 2026
  • CVE-2026-59105CVSS 9.3
    Jumis (formerly Tildes Jumis) creates and uses a Microsoft SQL Server login named ##Tilde_JumisAdmin## whose password is derived...
    📅 Updated: Nov 6, 2026
  • CVE-2026-118636CVSS 9.8
    **UNSUPPORTED WHEN ASSIGNED**  JavaNativeMessageDecoder in the MINA 3.0 codec module calls ObjectInputStream.readObject() on frame bytes with no class...
    📅 Updated: Nov 6, 2026
  • CVE-2026-19256CVSS 9.8
    The All In One Login WordPress plugin before 2.5.0 does not adequately restrict the number of attempts that...
    📅 Updated: Nov 6, 2026
  • CVE-2026-115230CVSS 9.8
    The WHIZZ WordPress plugin through 1.1.8 does not validate the password-reset key before updating a user's password, relying...
    📅 Updated: Nov 6, 2026
  • CVE-2026-110955CVSS 9.8
    The Wurdey WordPress plugin through 1.0.0 does not verify a request signature before logging a user in, allowing...
    📅 Updated: Nov 6, 2026
  • CVE-2026-113584CVSS 9.8
    The placester WordPress plugin through 1.4.3 does not perform any capability, nonce or ownership check on an AJAX...
    📅 Updated: Nov 6, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.